CVE-2022-34302
Demonstrates CVE-2022-34302, a Secure Boot bypass via the New Horizon Datasys signed bootloader whose built-in custom PE/COFF loader executes…

Demonstrates CVE-2022-34302, a Secure Boot bypass via the New Horizon Datasys signed bootloader whose built-in custom PE/COFF loader executes…

OS Command Injection Vulnerability via Cache Clearing Scheduler in Reolink Desktop Application

Read-only PowerShell security auditor for Windows endpoints and servers: checks Defender configuration, patch status, credentials, persistence,…

.NET post-exploitation toolkit for Active Directory reconnaissance and exploitation

ExtensionHijack

SQLWinds - SQL Server Security Assessment & Post-Exploitation Toolkit

Toolbox containing research notes & PoC code for weaponizing .NET's DLR

Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.

BrowserBackdoor is an Electron Application with a JavaScript WebSocket Backdoor and a Ruby Command-Line Listener

PowerUpSQL: A PowerShell Toolkit for Attacking SQL Server

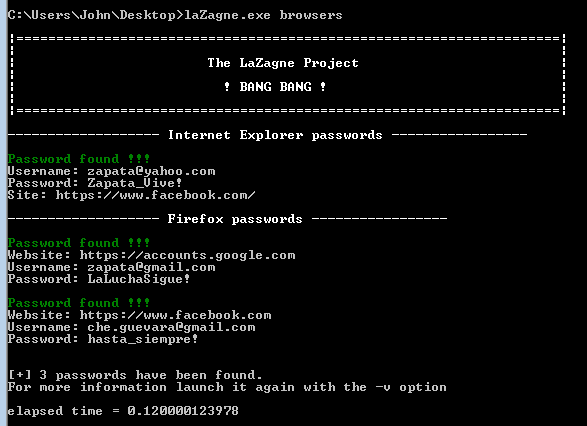
Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…

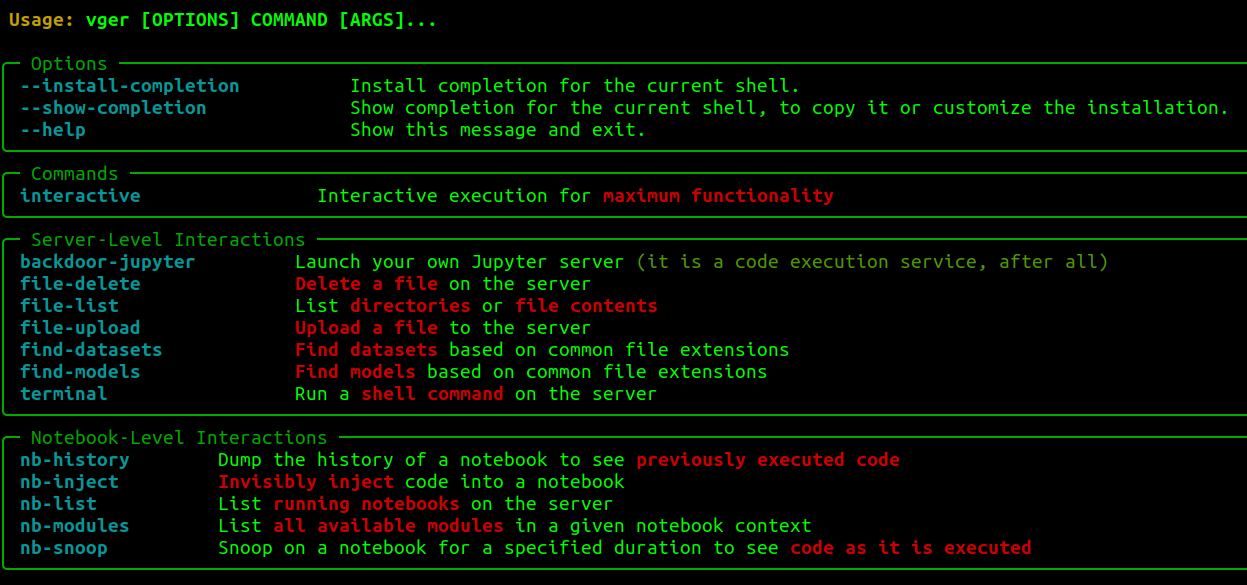
An interactive CLI application for interacting with authenticated Jupyter instances.

Cromos is a tool for downloading legitimate extensions of the Chrome Web Store and inject codes in the background of the application.

SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.

SharpGPOAbuse is a .NET application written in C# that can be used to take advantage of a user's edit rights on a Group Policy Object (GPO) in order…

CobaltStrike BOF to spawn Beacons using DLL Application Directory Hijacking