

BEAR-C2
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
adversarial-attackcommand-and-controldata-exfiltration+8
679
s3n4t0r-0x0/bear-c2The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 cenobyte-vincit/xspawn
Spawns macOS programs through launchd's private XPC interface without execing them, making EDR record launchd as parent. Supports one-shot,…
 securest8/npm-incident-response
Scanner for the keyv/cacheable supply-chain attack: detects compromised npm packages, verifies payload hashes, and finds persistence implants in repo…
 gtworek/psbits
Simple (relatively) things allowing you to dig a bit deeper than usual.
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 xforcered/scmkit
Source Code Management Attack Toolkit
 nvisosecurity/cobaltwhispers
CobaltWhispers is an aggressor script that utilizes a collection of Beacon Object Files (BOF) for Cobalt Strike to perform process injection,…
 med0x2e/gadgettojscript
A tool for generating .NET serialized gadgets that can trigger .NET assembly load/execution when deserialized using BinaryFormatter from JS/VBS/VBA…
 knight0x07/poc-malware-ttps
PoC-Malware-TTPs
 saadahla/pspersist
Dropping a powershell script at %HOMEPATH%\Documents\WindowsPowershell\ , that contains the implant's path , and whenever powershell process is…
 d00mfist/mystikal
macOS Initial Access Payload Generator
 cybrly/badsuccessor
Exploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…
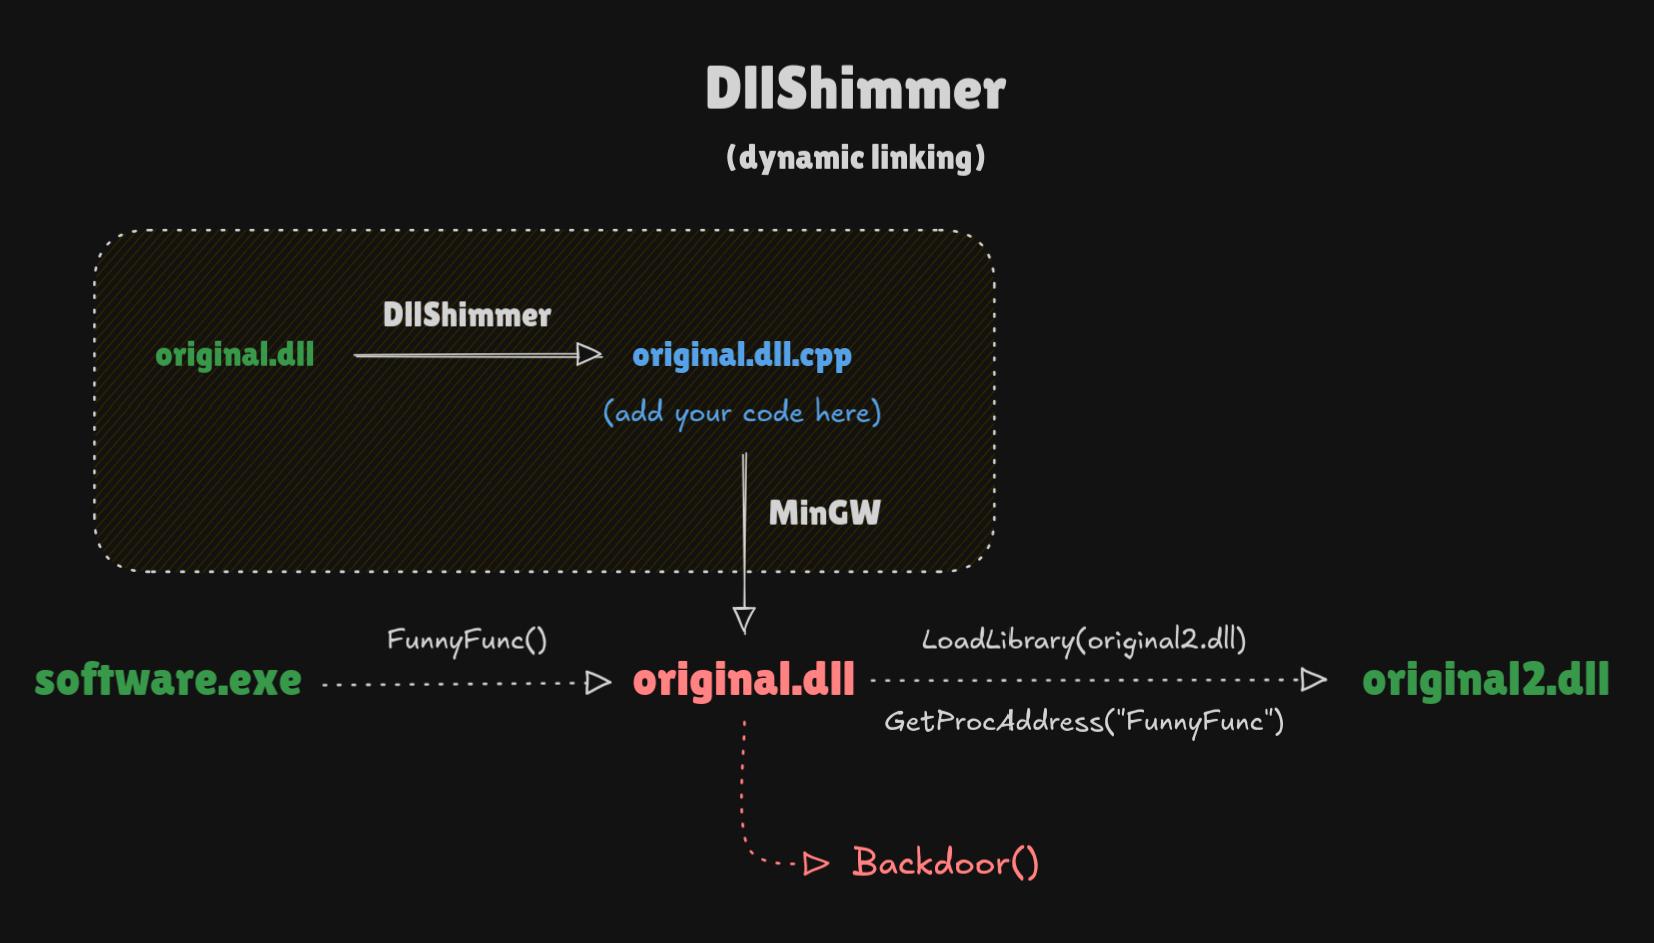 print3m/dllshimmer
Weaponize DLL hijacking easily. Backdoor any function in any DLL.
 trustedsec/tap
The TrustedSec Attack Platform is a reliable method for droppers on an infrastructure in order to ensure established connections to an organization.
 al1ex/powershell-c2
Powershell-C2
 integration-it/active-directory-exploitation-cheat-sheet
A cheat sheet that contains common enumeration and attack methods for Windows Active Directory.
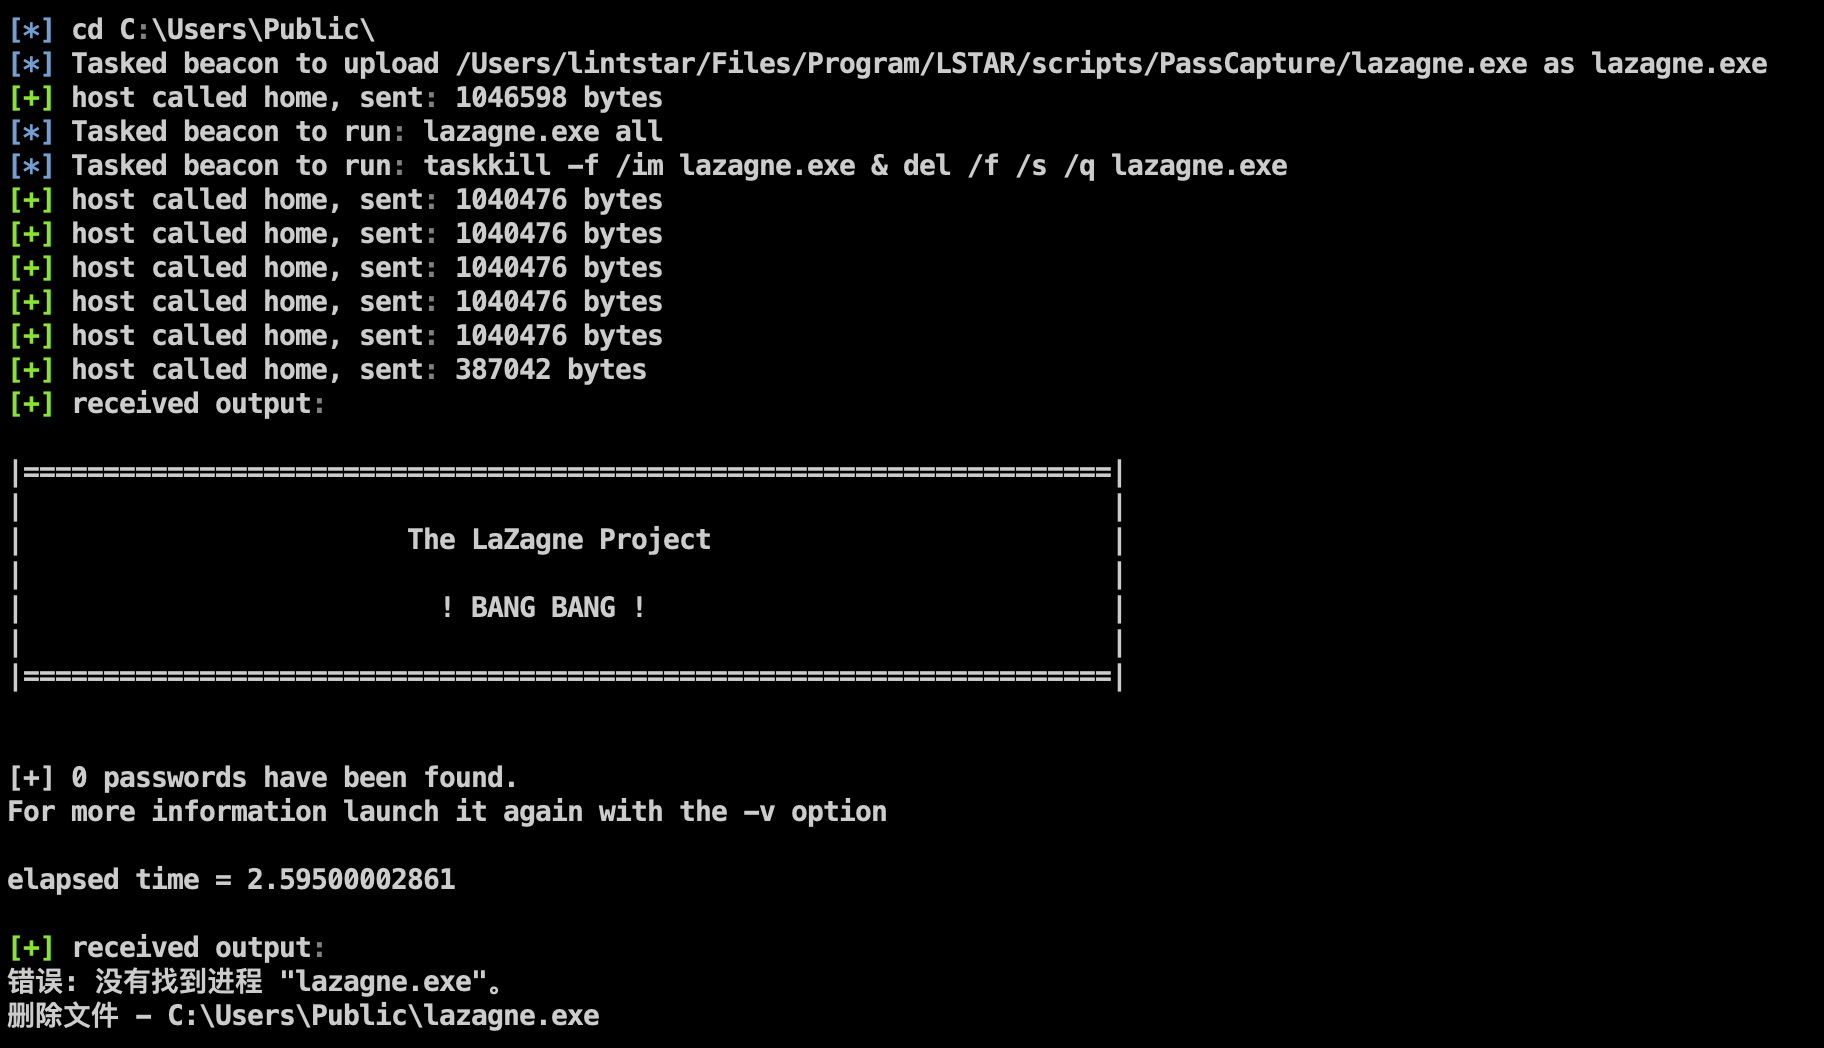 lintstar/lstar
LSTAR - CobaltStrike 综合后渗透插件
 enigma0x3/powershell-c2
PowerShell-based command and control framework using website-hosted payloads for persistent remote access and post-exploitation on Windows systems.