
MrRAT
 user696/mrrat
:mouse: This is a cross-platform Python 2.x Remote Access Trojan (RAT)
command-and-controlencryption-decryption-toolspayload-development+3
149 years ago
user696/mrrat:mouse: This is a cross-platform Python 2.x Remote Access Trojan (RAT)
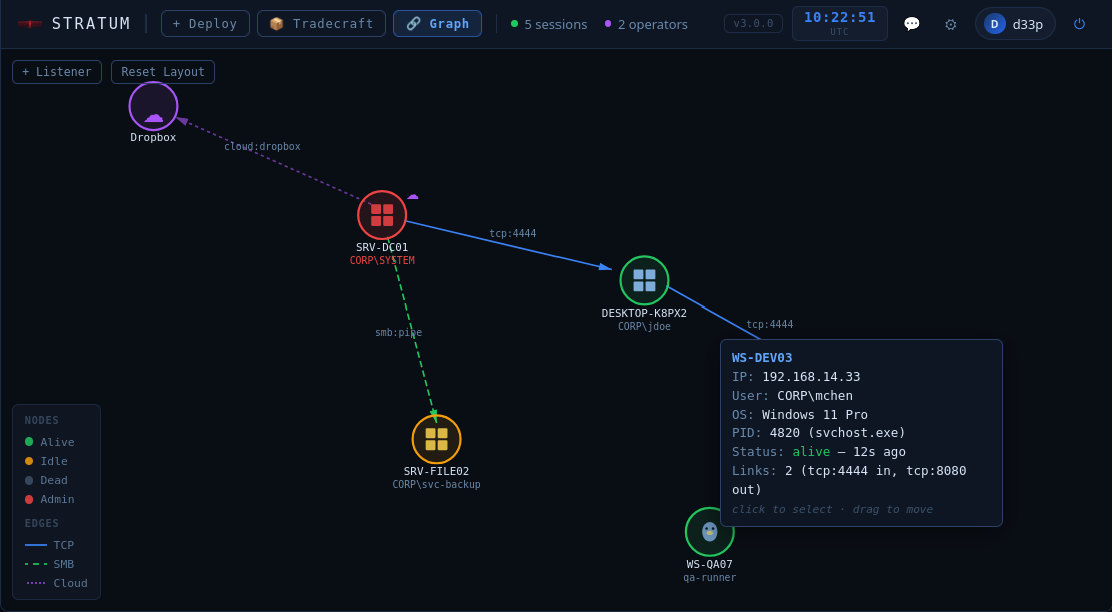 lame-projects/stratum-c2
Cloud dead-drop C2 framework — RSA-4096 + AES-256-GCM, 5 cloud providers, Rust-only agents, P2P mesh, persistence engine, credential harvesting
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 alessandroz/lazagne
Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…
 qwqdanchun/dcrat
A simple remote tool in C#.
 med0x2e/sigflip
SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.
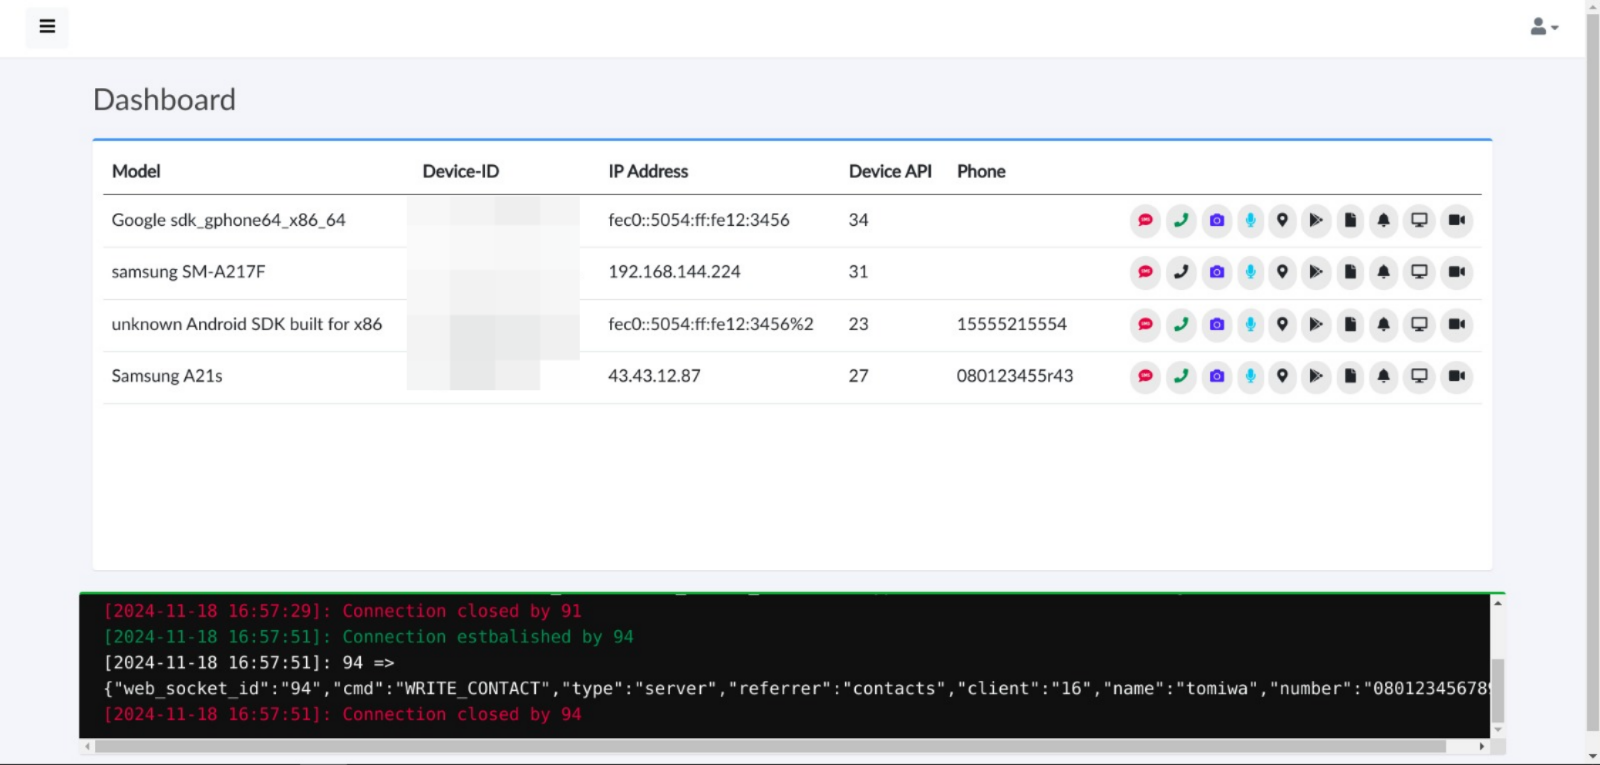 tomiwa-ot/moukthar
Android remote administration tool
 voidsecsoftwares/voidsyscall
Cross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.
 s3cur3th1ssh1t/nimsyscallpacker
Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…
 pushpenderindia/thorse
THorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.
 x3r0day/fud-c2-framework
A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
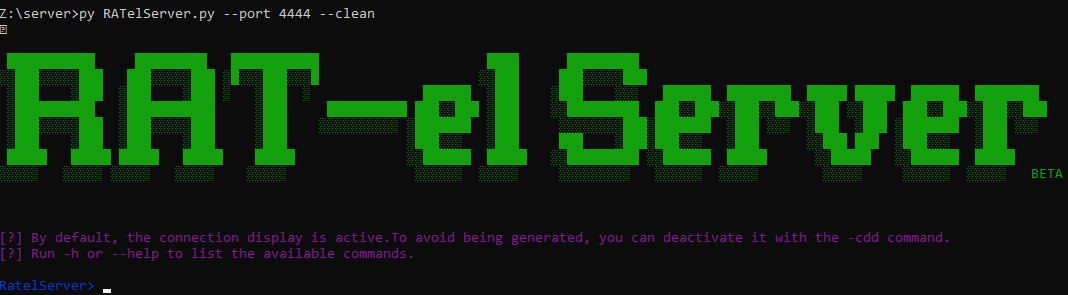 frenchcisco/ratel
RAT-el is an open source penetration test tool that allows you to take control of a windows machine. It works on the client-server model, the server…
 adaptix-framework/adaptixc2
AdaptixC2 is a highly modular advanced redteam toolkit

 sp00kyskelet0n/discordrat
Discord Remote Administration Tool fully written in Python3
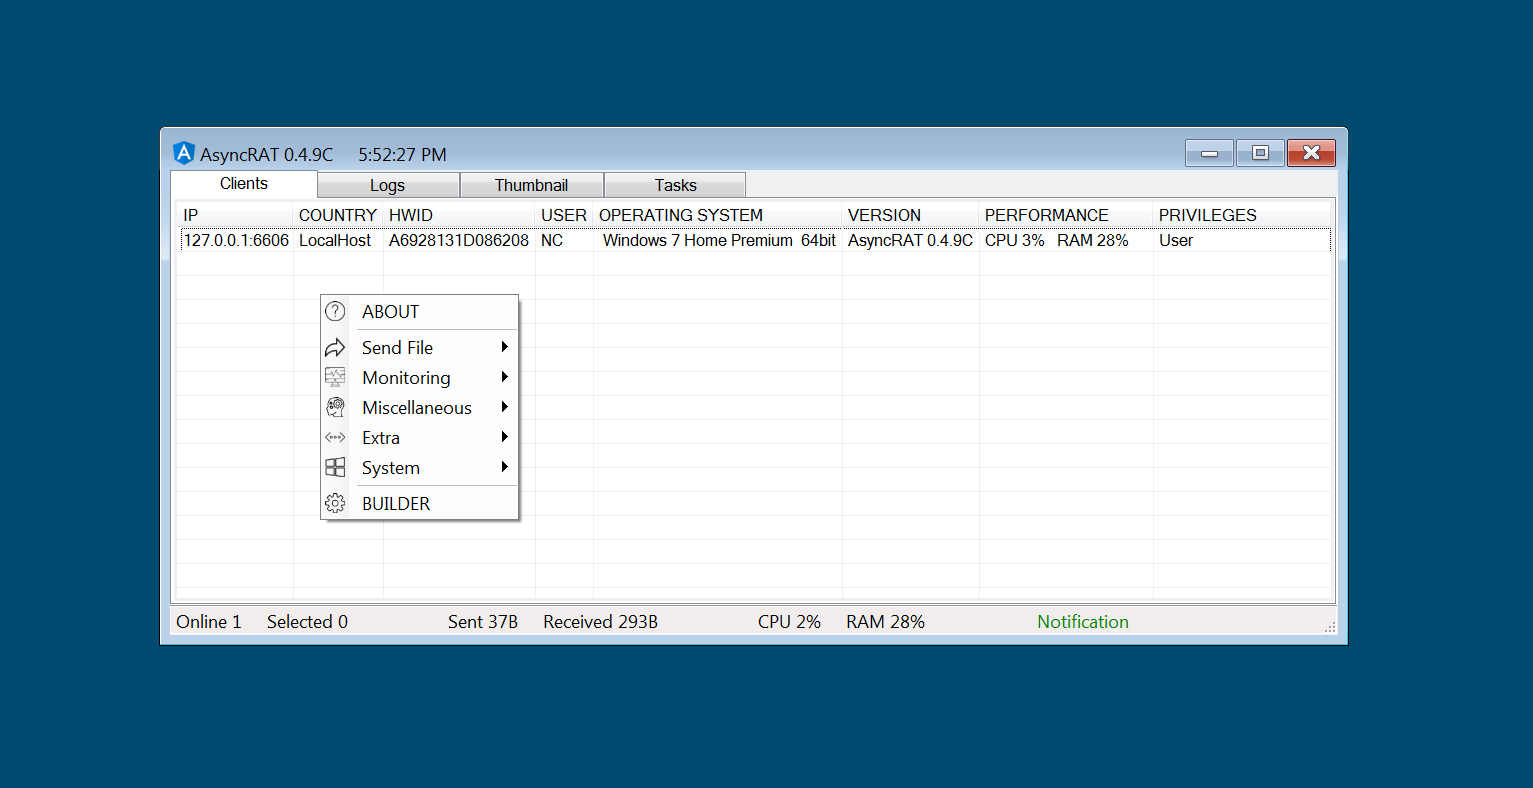 nyan-x-cat/asyncrat-c-sharp
Open-Source Remote Administration Tool For Windows C# (RAT)
 dragon56yt/revshell
A comprehensive educational repository demonstrating the evolution of a Windows reverse shell implant, from a simple proof‑of‑concept (v1.0) to a…
 marten4n6/evilosx
An evil RAT (Remote Administration Tool) for macOS / OS X.