Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
27 results
TitanHide preview

TitanHide

GitHubmrexodia/titanhide

Windows kernel driver that hooks Nt* SSDT functions to hide debuggers and processes from anti-debug checks, with an x64dbg plugin for stealth…
anti-botbinary-analysisdebuggers+4
2.9k
3 months ago
Vegile preview

Vegile

GitHubscreetsec/vegile

This tool will setting up your backdoor/rootkits when backdoor already setup it will be hidden your spesisifc process,unlimited your session in…

exploit-frameworkslateral-movementpayload-generation+4
7547 years ago
emp3r0r preview

emp3r0r

GitHubjm33-m0/emp3r0r

Linux post-exploitation C2 framework with gossip mesh networking, memory-only operations, modular payloads, and OPSEC-focused transport for red team…
anti-botcommand-and-controlids-ips-evasion+10
1.8k2 days ago
Silverseal preview

Silverseal

GitHubidov31/silverseal

Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
binary-exploitationexploitationmalware-analysis+4
17322 days ago
FakeMBR preview

FakeMBR

GitHubmalwaretech/fakembr

TDL4 style rootkit to spoof read/write requests to master boot record
binary-analysisexploitationmalware-analysis+2
13611 years ago
azazel preview

azazel

GitHubchokepoint/azazel

Azazel is a userland rootkit based off of the original LD_PRELOAD technique from Jynx rootkit. It is more robust and has additional features, and…
educationpersistence-mechanismspost-exploitation+2
8116 years ago
hidden preview

hidden

GitHubjkornev/hidden

Windows driver with usermode interface which can hide processes, file-system and registry objects, protect processes and etc
anti-botdefensive-toolsids-ips-evasion+3
2.1k4 years ago
rootkit preview

rootkit

GitHubnurupo/rootkit

Linux kernel module that grants root privileges, hides processes/files, and protects itself from unloading, designed for educational purposes on…

persistence-mechanismspost-exploitationprivilege-escalation
8312 years ago
r77-rootkit preview

r77-rootkit

GitHubbytecode77/r77-rootkit

Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.
command-and-controldefensive-toolsids-ips-evasion+6
2.2k3 months ago
Diamorphine preview

Diamorphine

GitHubm0nad/diamorphine

LKM rootkit for Linux Kernels 2.6.x-6.x (x86/x86_64 and ARM/64)
malware-analysispersistence-mechanismsprivilege-escalation+1
2.5k0 days ago
Umbra preview

Umbra

GitHubh3xduck/umbra

A LKM rootkit targeting 4.x and 5.x kernel versions which opens a backdoor that can spawn a reverse shell to a remote host, launch malware and more.
command-and-controleducationencryption-decryption-tools+6
1385 years ago
TripleCross preview

TripleCross

GitHubh3xduck/triplecross

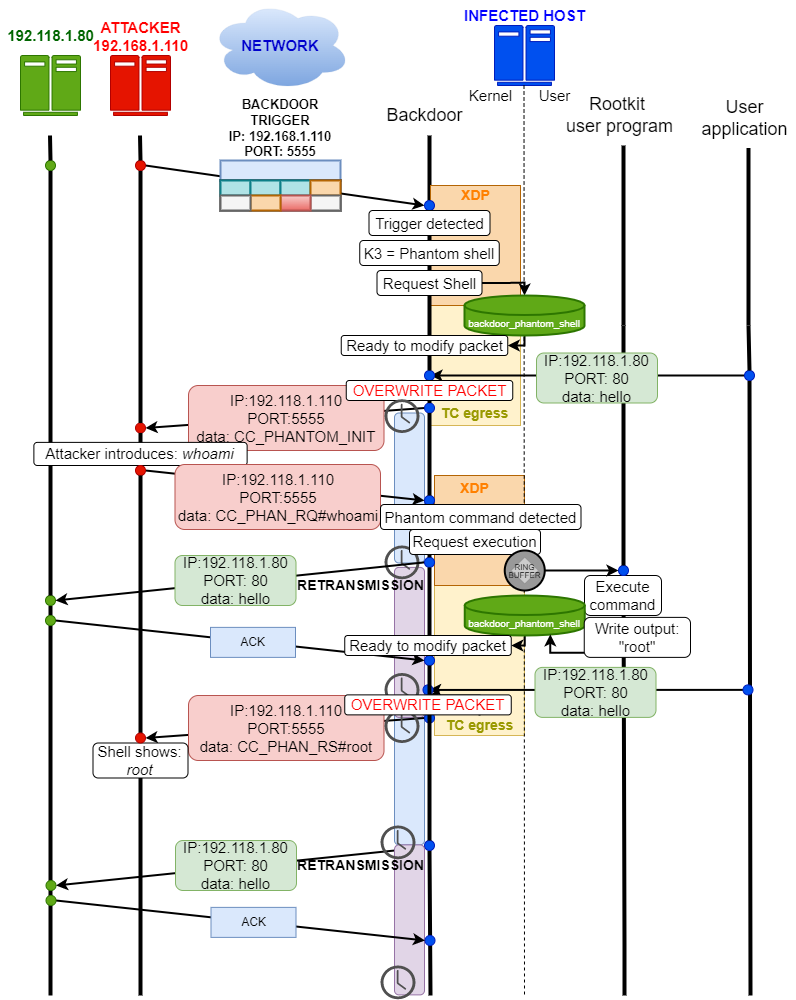
A Linux eBPF rootkit with a backdoor, C2, library injection, execution hijacking, persistence and stealth capabilities.
command-and-controleducationpersistence-mechanisms+1
2.0k3 years ago
VectorKernel preview

VectorKernel

GitHubdaem0nc0re/vectorkernel

PoCs for Kernelmode rootkit techniques research.
educationexploitationmalware-analysis+3
4457 months ago
project-rvbbit preview

project-rvbbit

GitHubbuter-chkalova/project-rvbbit

Educational Linux kernel rootkit PoC exploring DKOM, syscall hooking, stealth, observability and defensive detection
defensive-toolseducationmalware-analysis+3
341 month ago
blackpill preview
Archived

blackpill

GitHubshard77/blackpill

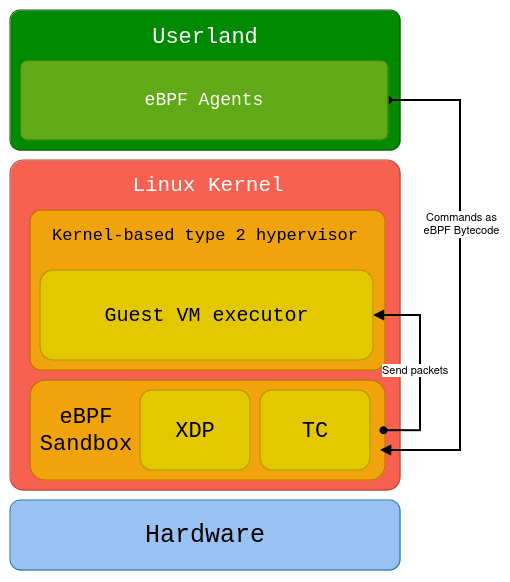
A Linux kernel rootkit in Rust using a custom made type-2 hypervisor, eBPF XDP and TC programs
binary-exploitationcommand-and-controlids-ips-evasion+7
3418 months ago
Codeine preview

Codeine

GitHubdiego-tella/codeine

Linux LKM Rootkit

command-and-controlpersistence-mechanismspost-exploitation+3
131 year ago
Cronos-Rootkit preview
Archived

Cronos-Rootkit

GitHubxaff-xaff/cronos-rootkit

Cronos is Windows 10/11 x64 ring 0 rootkit. Cronos is able to hide processes, protect and elevate them with token manipulation.
ids-ips-evasionpersistence-mechanismspost-exploitation+2
9474 years ago
talkingBen preview

talkingBen

GitHubm4rm0k/talkingben

UEFI rootkit under development focusing on privilege escalation, C2 integration, and anti-EDR/AV evasion for real-world malware deployment.

command-and-controlexploitationmalware-analysis+4
11 year ago
Previous12Next