
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
23 results
AddUser-SAMR preview

AddUser-SAMR

GitHubricardojoserf/adduser-samr

Create local administrators in Windows using the SAMR API. In C#, Crystal, Python, Rust, Golang, Nim and Deno (Javascript)
authenticationidentity-access-managementlateral-movement+5
97
26 days ago
pupy preview

pupy

GitHubalessandroz/pupy

Pupy is an opensource, multi-platform (Windows, Linux, OSX, Android), multi function RAT (Remote Administration Tool) mainly written in python. It…
command-and-controldata-exfiltrationlateral-movement+7
918 years ago
RightHand-Persistence preview

RightHand-Persistence

GitHubi014n/righthand-persistence

COM Windows Persistence Technique
educationexploitationpersistence-mechanisms+2
895 months ago
CasperStager preview

CasperStager

GitHubustayready/casperstager

PoC for persisting .NET payloads in Windows Notification Facility (WNF) state names using low-level Windows Kernel API calls.
exploitationpayload-developmentpersistence-mechanisms+2
1527 years ago
CS-Remote-OPs-BOF preview

CS-Remote-OPs-BOF

GitHubtrustedsec/cs-remote-ops-bof

Remote operations commands implemented using Beacon Object Files
authenticationencryption-decryption-toolslateral-movement+6
1.2k1 day ago
ToRat preview
Archived

ToRat

GitHubluantak/torat

ToRat is a Remote Administation tool written in Go using Tor as a transport mechanism and RPC for communication
command-and-controleducationpayload-generation+6
1.0k3 years ago
patchy preview

patchy

GitHubrek7/patchy

Automated Persistence and Lateral Movement using GCP Patch Management
cloud-securityexploitationlateral-movement+3
164 years ago
Powershell-RAT preview

Powershell-RAT

GitHubviralmaniar/powershell-rat

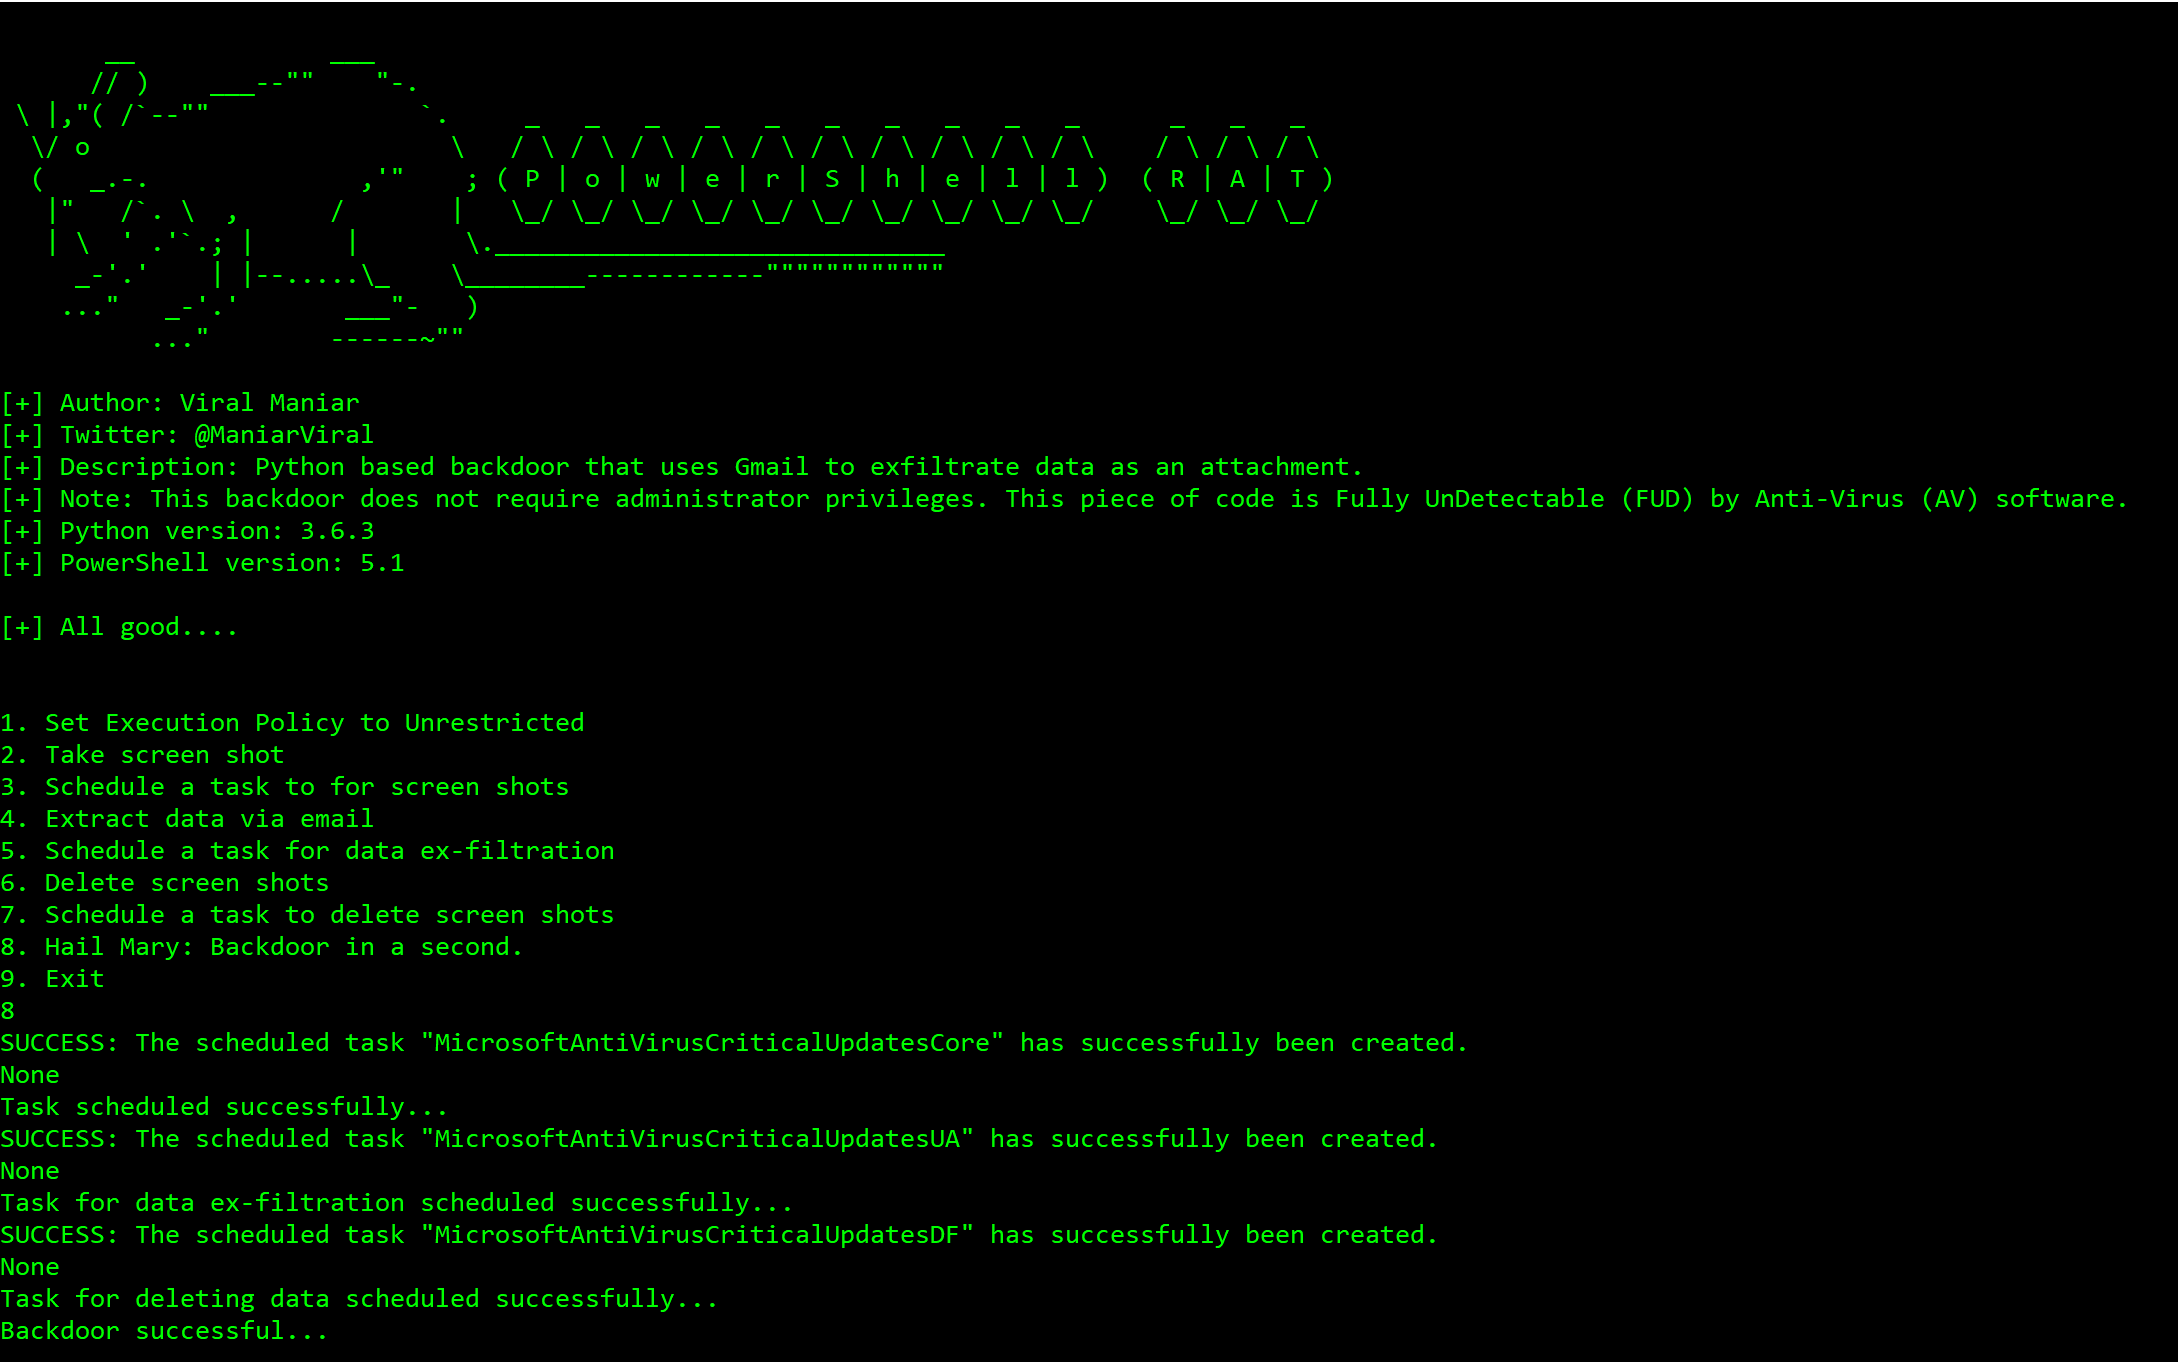
Python based backdoor that uses Gmail to exfiltrate data through attachment. This RAT will help during red team engagements to backdoor any Windows…
data-exfiltrationeducationpayload-generation+4
1.2k7 years ago
Fsociety-CVE-2024-0670-CheckMK-LPE preview

Fsociety-CVE-2024-0670-CheckMK-LPE

GitHubnikopmpm/fsociety-cve-2024-0670-checkmk-lpe

🔍 Exploit CVE-2024-0670 in CheckMK agents for local privilege escalation using a robust C++ tool designed for security professionals.
exploitationpenetration-testingpersistence-mechanisms+4
2 days ago
shepard preview

shepard

GitHubd3adzo/shepard

In progress persistent download/upload/execution tool using Windows BITS.
command-and-controldata-exfiltrationpersistence-mechanisms+3
415 years ago
GraphSpy preview

GraphSpy

GitHubredbyte1337/graphspy

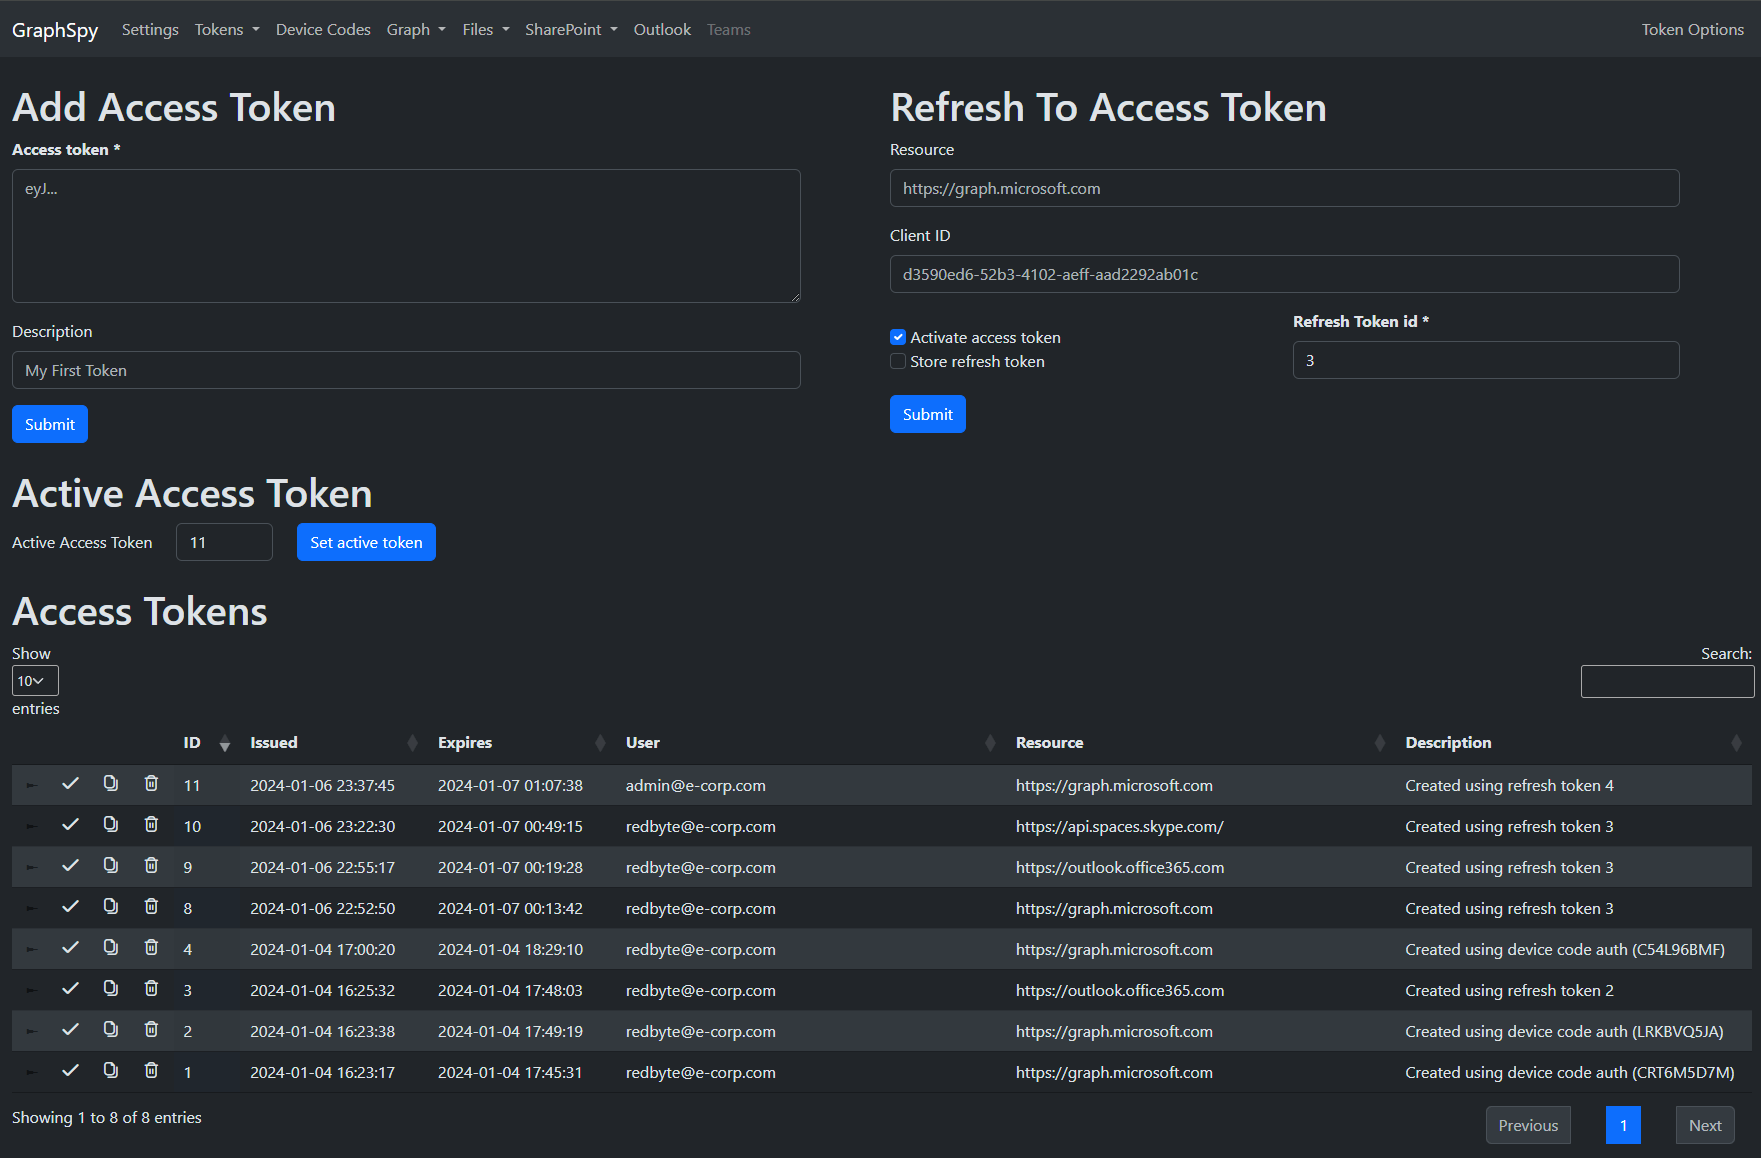
Initial Access and Post-Exploitation Tool for Entra ID and M365 with a browser-based GUI
authenticationcloud-securitydata-exfiltration+6
1.4k1 month ago
DogWalk-rce-poc preview

DogWalk-rce-poc

GitHubariary/dogwalk-rce-poc

🐾Dogwalk PoC (using diagcab file to obtain RCE on windows)

exploitationpayload-generationpenetration-testing+1
764 years ago
IIS-Backdoor preview

IIS-Backdoor

GitHubnu11secur1ty/iis-backdoor

Stealthy IIS backdoor using hidden ISAPI filter for persistent remote access, data exfiltration, and on-the-fly exploit injection via custom HTTP…
command-and-controlexploitationids-ips-evasion+4
346 years ago
XeytanWin32-RAT preview

XeytanWin32-RAT

GitHubmelardev/xeytanwin32-rat

WORK IN PROGRESS. RAT written in C++ using Win32 API
command-and-controldata-exfiltrationexploitation+8
207 years ago
DropSpawn_BOF preview

DropSpawn_BOF

GitHuboctoberfest7/dropspawn_bof

CobaltStrike BOF to spawn Beacons using DLL Application Directory Hijacking
binary-exploitationexploitationpayload-development+4
2853 years ago
w11_shadow_copies preview

w11_shadow_copies

GitHubricardojoserf/w11_shadow_copies

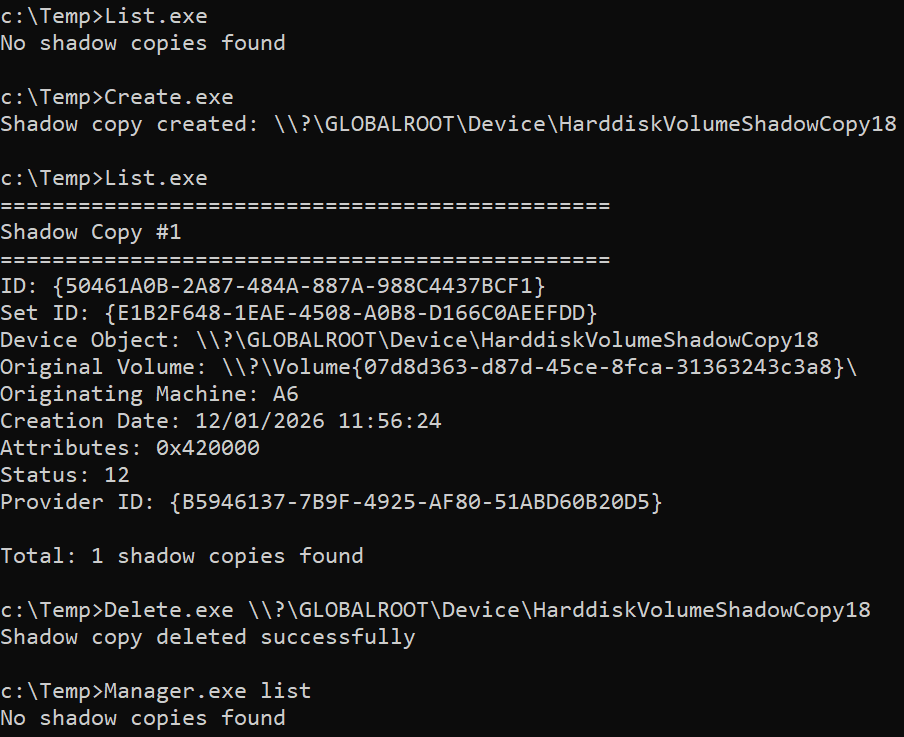
Manage Shadows Copies via the VSS API using C#, C++, Crystal or Python. Working on Windows 11
data-exfiltrationexploitationlateral-movement+5
878 months ago
macos_sandbox preview

macos_sandbox

GitHubyo-yo-yo-jbo/macos_sandbox

Blog post exploring macOS App Sandbox, entitlements via codesign, and sandbox escape techniques using launchd, LaunchAgents, and quarantine…

educationexploitationpersistence-mechanisms+3
332 months ago
Driver-hide-file preview

Driver-hide-file

GitHubgmh5225/driver-hide-file

choose and hide windows files/path from kernel space using this driver

defensive-toolspersistence-mechanisms
3 years ago
Previous12Next