
CVE-2026-78006-POC
 deadexpl0it/cve-2026-78006-poc
POC for CVE-2026-78006 The Events Calendar <= 6.17.4 - Unauthenticated PHP Object Injection to Remote Code Execution
defensive-toolsexploitationpayload-development+7
deadexpl0it/cve-2026-78006-pocPOC for CVE-2026-78006 The Events Calendar <= 6.17.4 - Unauthenticated PHP Object Injection to Remote Code Execution
 screetsec/vegile
This tool will setting up your backdoor/rootkits when backdoor already setup it will be hidden your spesisifc process,unlimited your session in…
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 sailay1996/cdpsvclpe
Windows Local Privilege Escalation via CdpSvc service (Writeable SYSTEM path Dll Hijacking)
 saumyajeetdas/godgenesis
A Python3 based C2 server to make life of red teamer a bit easier. The payload is capable to bypass all the known antiviruses and endpoints.
 trevohack/dynastypersist
Linux persistence toolkit with 11 modules for SSH key backdoors, cronjobs, systemd services, LKM rootkits, and LD_PRELOAD privilege escalation.…
 lyravoid/folkpatch
Root access to the kernel can be achieved simply by patching the Boot partition for reflashing. This solution is based on a non-parallel extended…
 frenchcisco/ratel
RAT-el is an open source penetration test tool that allows you to take control of a windows machine. It works on the client-server model, the server…
 bmax121/apatch
The patching of Android kernel and Android system
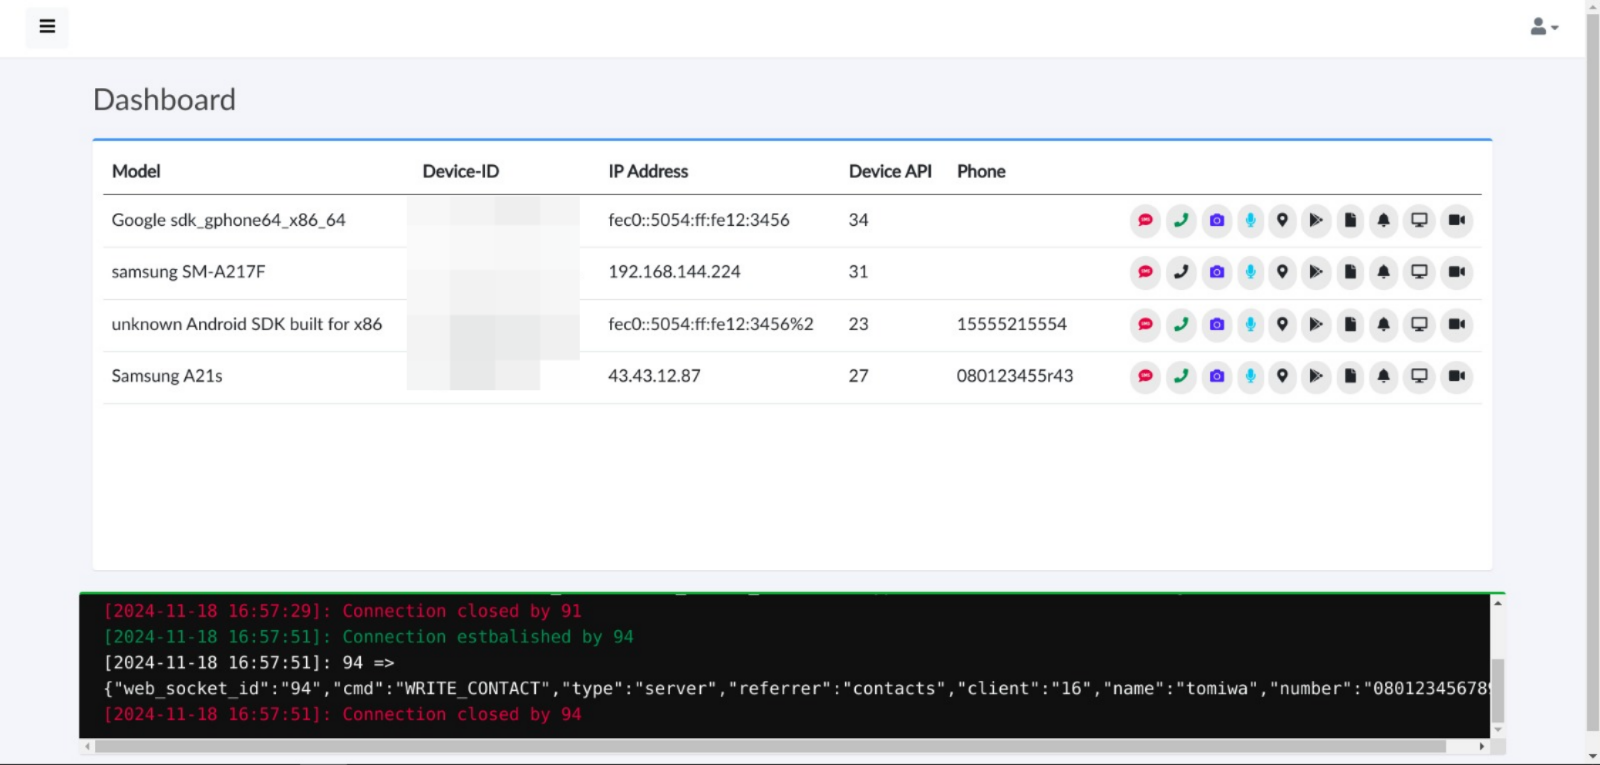 tomiwa-ot/moukthar
Android remote administration tool
 h4wkst3r/adokit
Modular attack toolkit exploiting Azure DevOps REST API for reconnaissance, privilege escalation, and persistence using stolen cookies or PATs.
 pinarsadioglu/cve-2023-23192
CVE-2023-23192
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 cdk-team/cdk
📦 Make security testing of K8s, Docker, and Containerd easier.
 4nuxd/react2shell
R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…
 jgoyd/glass-cage-ios18-cve-2025-24085-cve-2025-24201
Glass Cage is a zero-click PNG-based RCE chain in iOS 18.2.1, bypassing LockDown mode protection by exploiting ImageIO (CVE-2025-43300), then…
 snothin/ghostlock-s26
GhostLock (CVE-2026-43499) for the Galaxy S26