
Archived
PyRIT
 azure/pyrit
The Python Risk Identification Tool for generative AI (PyRIT) is an open source framework built to empower security professionals and engineers to…
adversarial-attackai-securityeducation+2
117
 a7vinx/swarm
A modular distributed penetration testing tool.
 optiv/freeze
Freeze is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls, and alternative execution methods
 qubasa/msf-remote-console
A remote msfconsole written in Python 2.7 to connect to the msfrcpd server of metasploit. This tool gives you the ability to load modules permanently…
 fox-it/ldapfragger
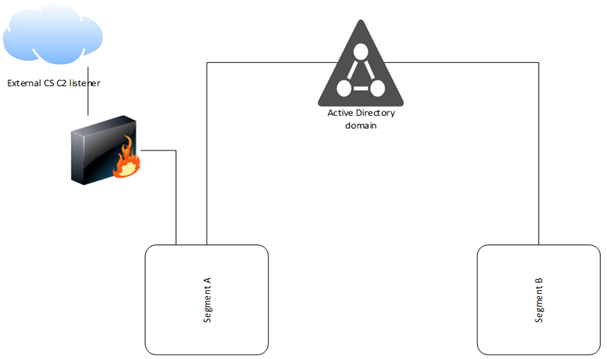
C2 tool routing Cobalt Strike beacon data over LDAP user attributes for stealthy command-and-control in segmented networks.

 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
 z4nzu/hackingtool
All-in-one penetration testing toolkit aggregating 185+ tools across 20 categories including information gathering, web & wireless attacks, phishing,…
 henkru/cs-token-vault
In-memory token vault BOF for Cobalt Strike
 horizon3ai/h3-cli
CLI tool for the Horizon3.ai API
 trustedsec/tap
The TrustedSec Attack Platform is a reliable method for droppers on an infrastructure in order to ensure established connections to an organization.
 mythicagents/thanatos
Mythic C2 agent targeting Linux and Windows hosts written in Rust
 enkomio/alanframework
A C2 post-exploitation framework
 gushmazuko/metasploit_in_termux
Install and run Metasploit Framework 6 on Android via Termux with automated setup, payload generation (msfvenom), and full msfconsole access for…
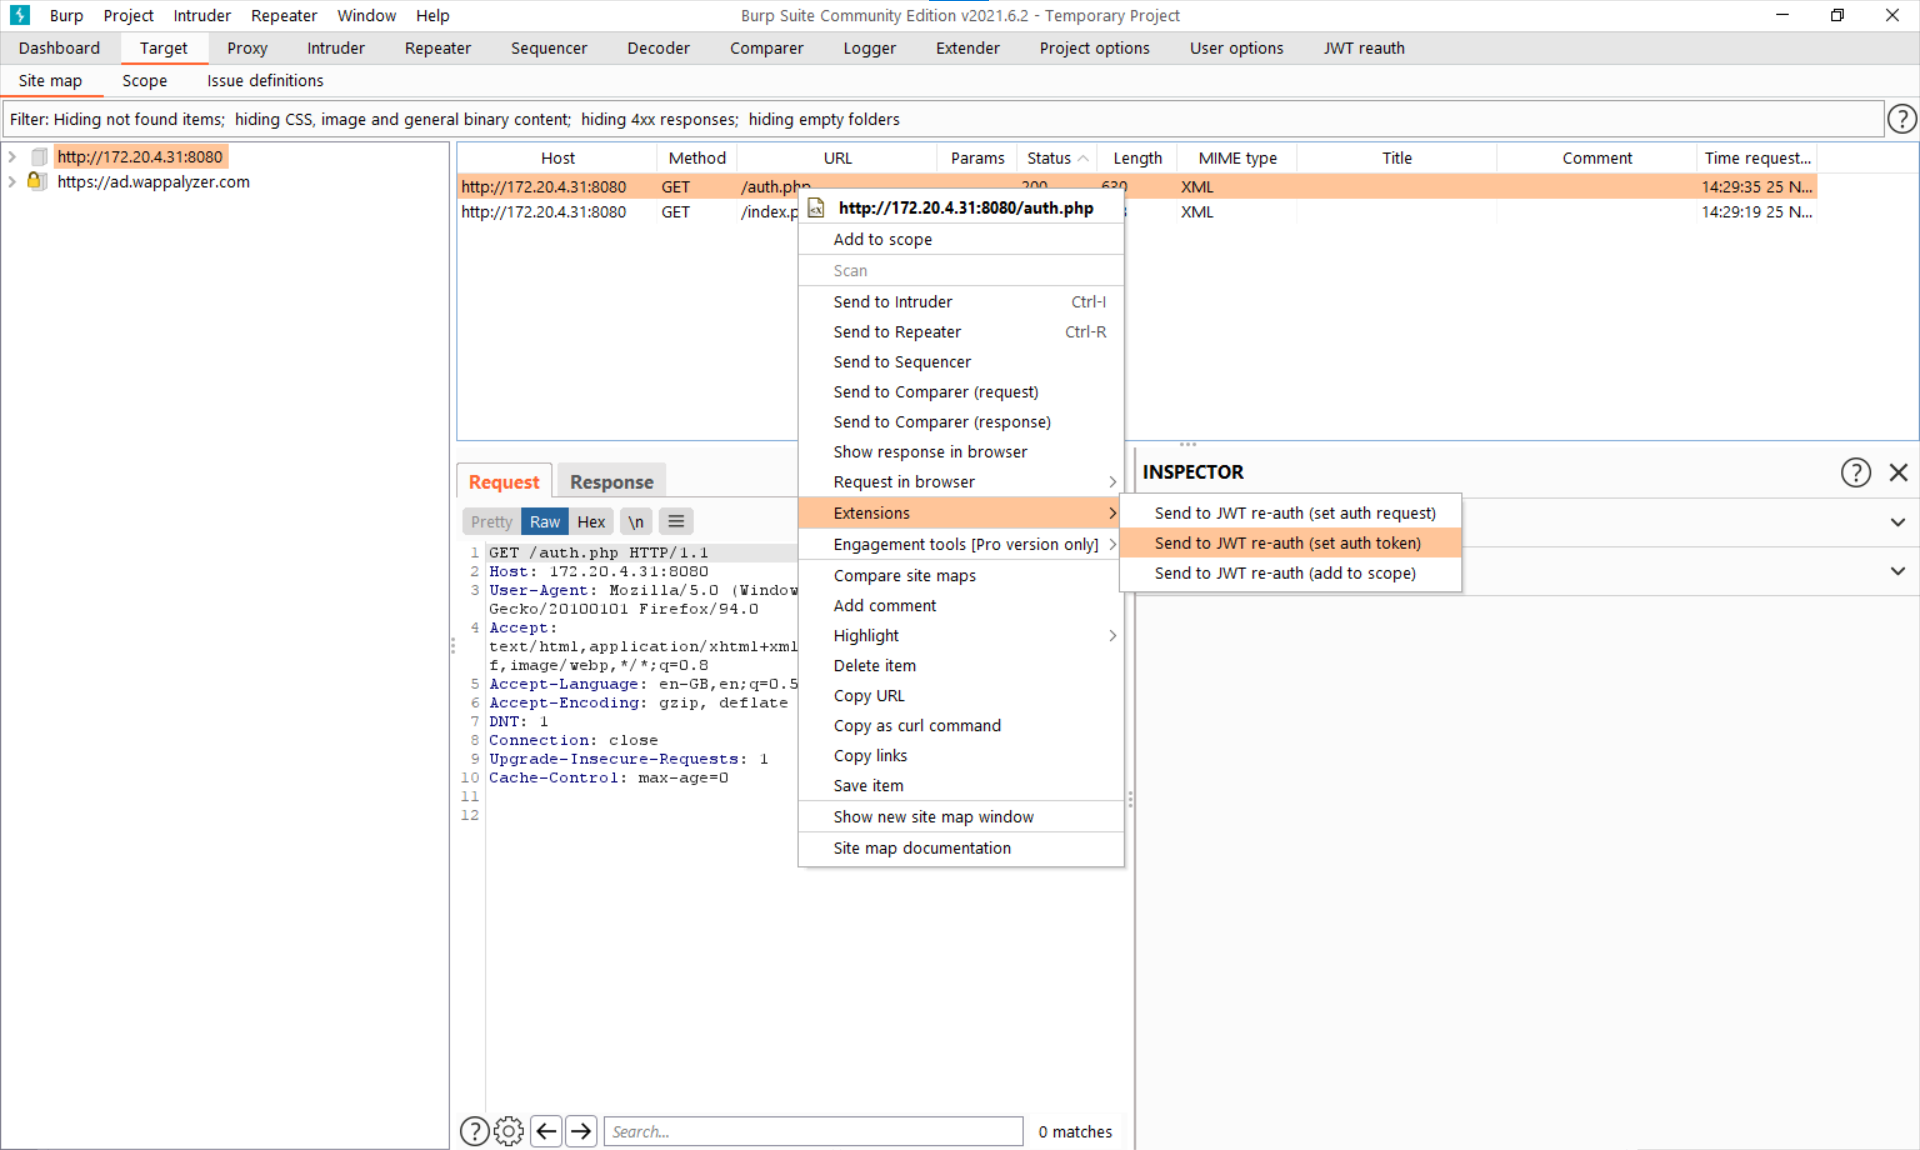 nccgroup/jwt-reauth
Caches JWT authentication tokens from an auth URL and attaches them as headers to in-scope requests in Burp Suite for automated session handling.
 n1nj4sec/pupy
Pupy is an opensource, cross-platform (Windows, Linux, OSX, Android) C2 and post-exploitation framework written in python and C
 nccgroup/autopwn
Specify targets and run sets of tools against them
 aflplusplus/libafl
Advanced Fuzzing Library - Slot your Fuzzer together in Rust! Scales across cores and machines. For Windows, Android, MacOS, Linux, no_std, ...