

LibAFL
 aflplusplus/libafl
Advanced Fuzzing Library - Slot your Fuzzer together in Rust! Scales across cores and machines. For Windows, Android, MacOS, Linux, no_std, ...
binary-analysisdynamic-analysis-sandboxingeducation+5
2.6k
aflplusplus/libaflAdvanced Fuzzing Library - Slot your Fuzzer together in Rust! Scales across cores and machines. For Windows, Android, MacOS, Linux, no_std, ...
 0xsteph/pentest-ai-agents
Turn Claude Code into your offensive security research assistant. Specialized AI subagents for authorized penetration testing plan engagements,…
 ascit31/dark-moon
Autonomous AI pentesting engine, continuous offensive security across web, cloud, AD & Kubernetes. Agentic reasoning + real exploit execution deliver…
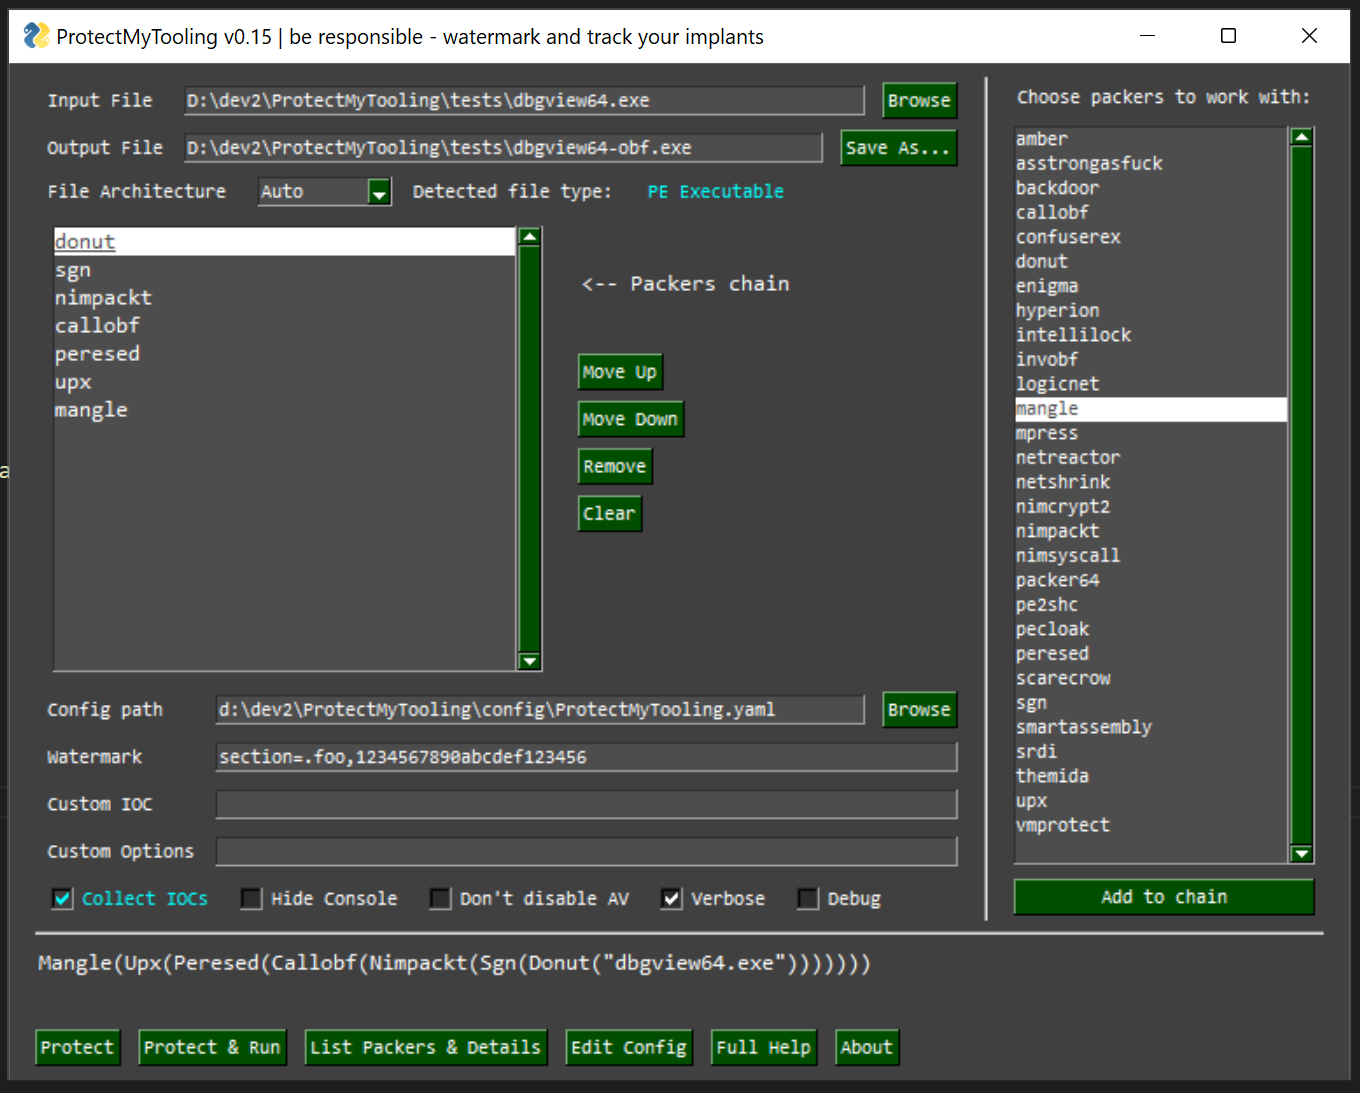 mgeeky/protectmytooling
Multi-Packer wrapper letting us daisy-chain various packers, obfuscators and other Red Team oriented weaponry. Featured with artifacts watermarking,…
 skiller9090/lucifer
A Powerful Penetration Tool For Automating Penetration Tasks Such As Local Privilege Escalation, Enumeration, Exfiltration and More... Use Or Build…
 thirdbyte/ssj
Your everyday Linux distribution gone Super Saiyan.
 ilk-toolkit/ilk-toolkit
A ToolKit that automatically installs & configures all the Tools needed to turn your Daily Driver Linux Distro into a Pentesting Machine
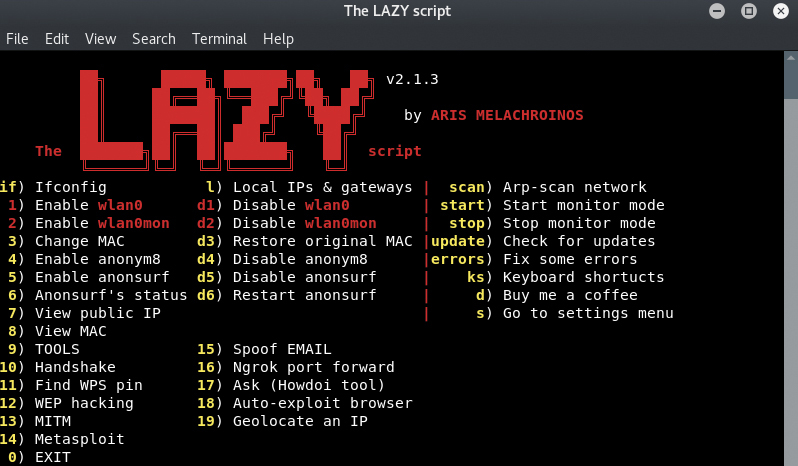 arismelachroinos/lscript
The LAZY script will make your life easier, and of course faster.
 qubasa/msf-remote-console
A remote msfconsole written in Python 2.7 to connect to the msfrcpd server of metasploit. This tool gives you the ability to load modules permanently…
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
 samugit83/redamon
An AI-powered agentic red team framework that automates offensive security operations, from reconnaissance to exploitation to post-exploitation, with…
 securecodebox/securecodebox
Kubernetes-native security scanning orchestrator that automates continuous vulnerability detection by integrating multiple open-source scanners into…
 r00ts3c/ddos-rootsec
Explore RootSec's DDOS Archive, featuring top-tier scanners, powerful botnets (Mirai & QBot) and other variants, high-impact exploits, advanced…
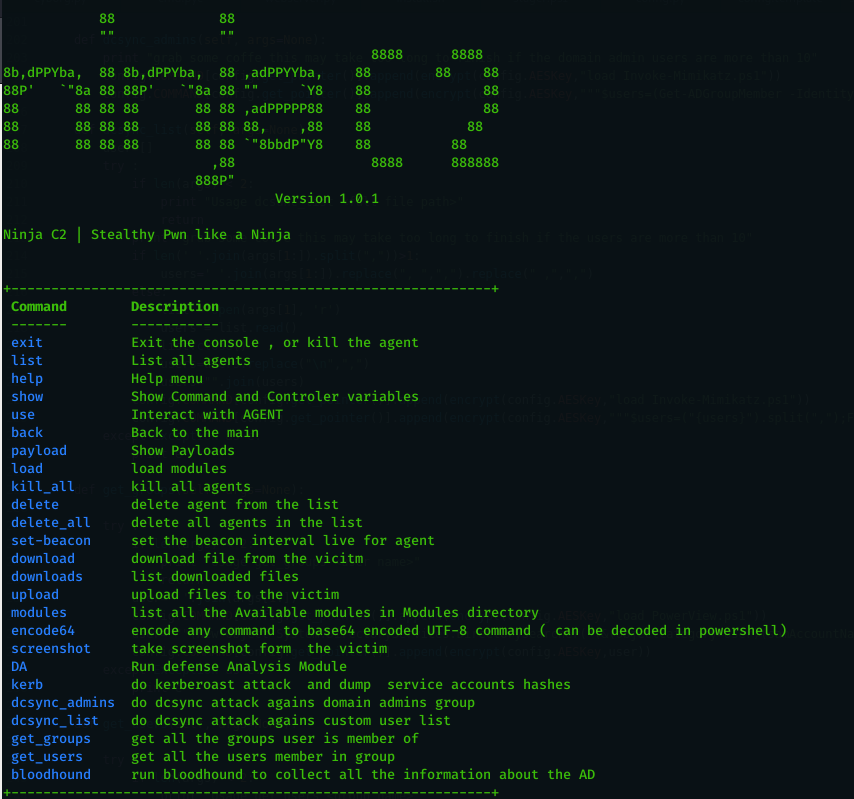 ahmedkhlief/ninja
Open source C2 server created for stealth red team operations
 s0ld13rr/pentestcode
Autonomous AI penetration testing agent that orchestrates multi-agent recon, exploitation, post-exploitation, and reporting with persistent…
 enkomio/alanframework
A C2 post-exploitation framework

 trustedsec/specula
Modular command-and-control framework abusing Microsoft Outlook's Home Page feature for stealthy persistence, remote access, and post-exploitation.