
cervantes
Open-source collaborative platform for pentesters and red teams to manage projects, clients, vulnerabilities, and generate OWASP-compliant reports…

Open-source collaborative platform for pentesters and red teams to manage projects, clients, vulnerabilities, and generate OWASP-compliant reports…

Autonomous white-hat security auditor for AI-driven code review, bug bounty research, exploit construction, and execution-grounded verification.

Turn Claude Code into your offensive security research assistant. Specialized AI subagents for authorized penetration testing plan engagements,…

The AWS exploitation framework, designed for testing the security of Amazon Web Services environments.

:cloud: :zap: Granular, Actionable Adversary Emulation for the Cloud

PowerUpSQL: A PowerShell Toolkit for Attacking SQL Server

Jackhammer - One Security vulnerability assessment/management tool to solve all the security team problems.

A canvas for red team infrastructure and cyber ranges. Compose a topology, export runnable Terraform and Ansible, and deploy it yourself. Your cloud…

Competition Infrastructure Management

Serverless C2 transport plugin for AdaptixC2 v1.2 using AWS Lambda + DynamoDB as the relay infrastructure.

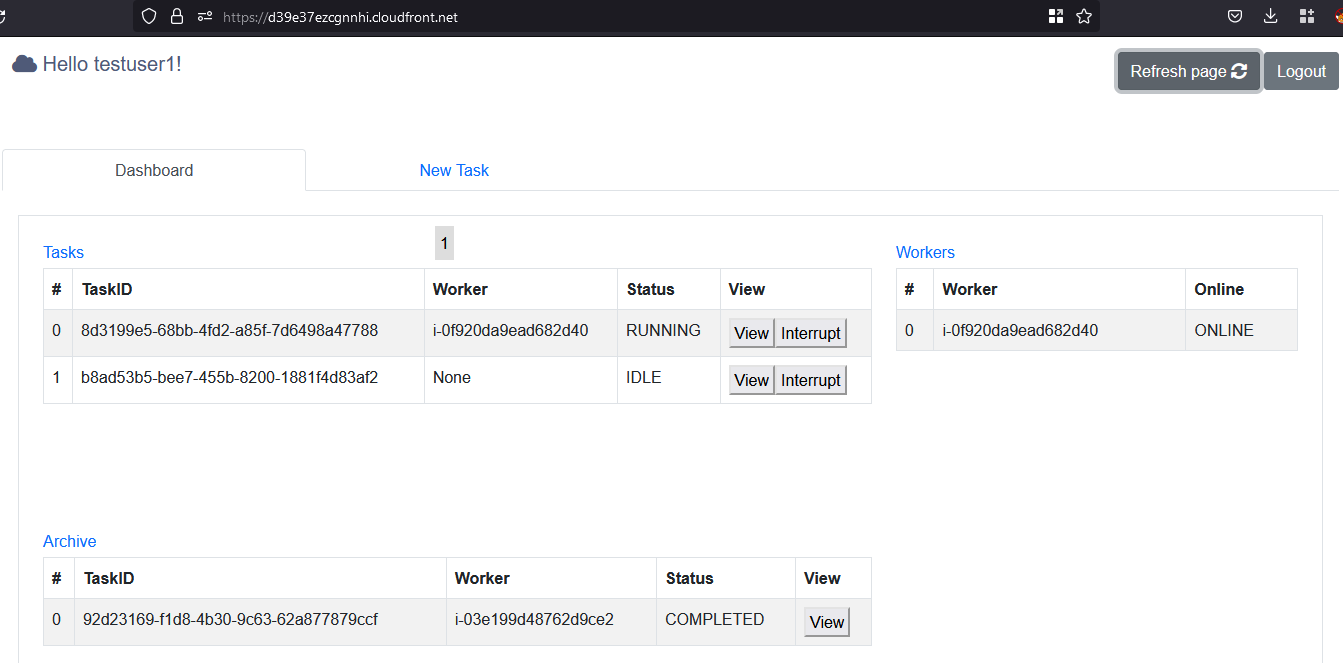
Serverless AWS solution for distributing recon and vulnerability scanning workloads. Submit tasks via web UI; EC2 workers execute custom Python…

Terraform-deployed red team operator lab on AWS: Mythic, Sliver, and Adaptix C2 behind a production-style Apache redirector, with Kali/Windows hosts…