
ethibench
 jd0965199-oss/ethibench
Evaluation framework for AI penetration testing agents that measures validated vulnerability discovery using LLM-based semantic matching, bipartite…
ai-securityeducationmachine-learning+4
jd0965199-oss/ethibenchEvaluation framework for AI penetration testing agents that measures validated vulnerability discovery using LLM-based semantic matching, bipartite…
 0xmetr0/metasploit-ldapnightmare
SafeBreaches CVE-2024-49113 POC(LdapNightmare) Integrated into Metasploit
 n1nj4sec/pupy
Pupy is an opensource, cross-platform (Windows, Linux, OSX, Android) C2 and post-exploitation framework written in python and C
 secdevops-cuse/cyberrange
The Open-Source AWS Cyber Range
 ascit31/dark-moon
Autonomous AI pentesting engine, continuous offensive security across web, cloud, AD & Kubernetes. Agentic reasoning + real exploit execution deliver…
 archstrike/archstrike
An Arch Linux repository for security professionals and enthusiasts. Done the Arch Way and optimized for i686, x86_64, ARMv6, ARMv7 and ARMv8.
 facebookincubator/ttpforge
The TTPForge is a Cybersecurity Framework for developing, automating, and executing attacker Tactics, Techniques, and Procedures (TTPs).
 rajanagori/nightingale
Nightingale Docker for Pentesters is a comprehensive Dockerized environment tailored for penetration testing and vulnerability assessment. It comes…
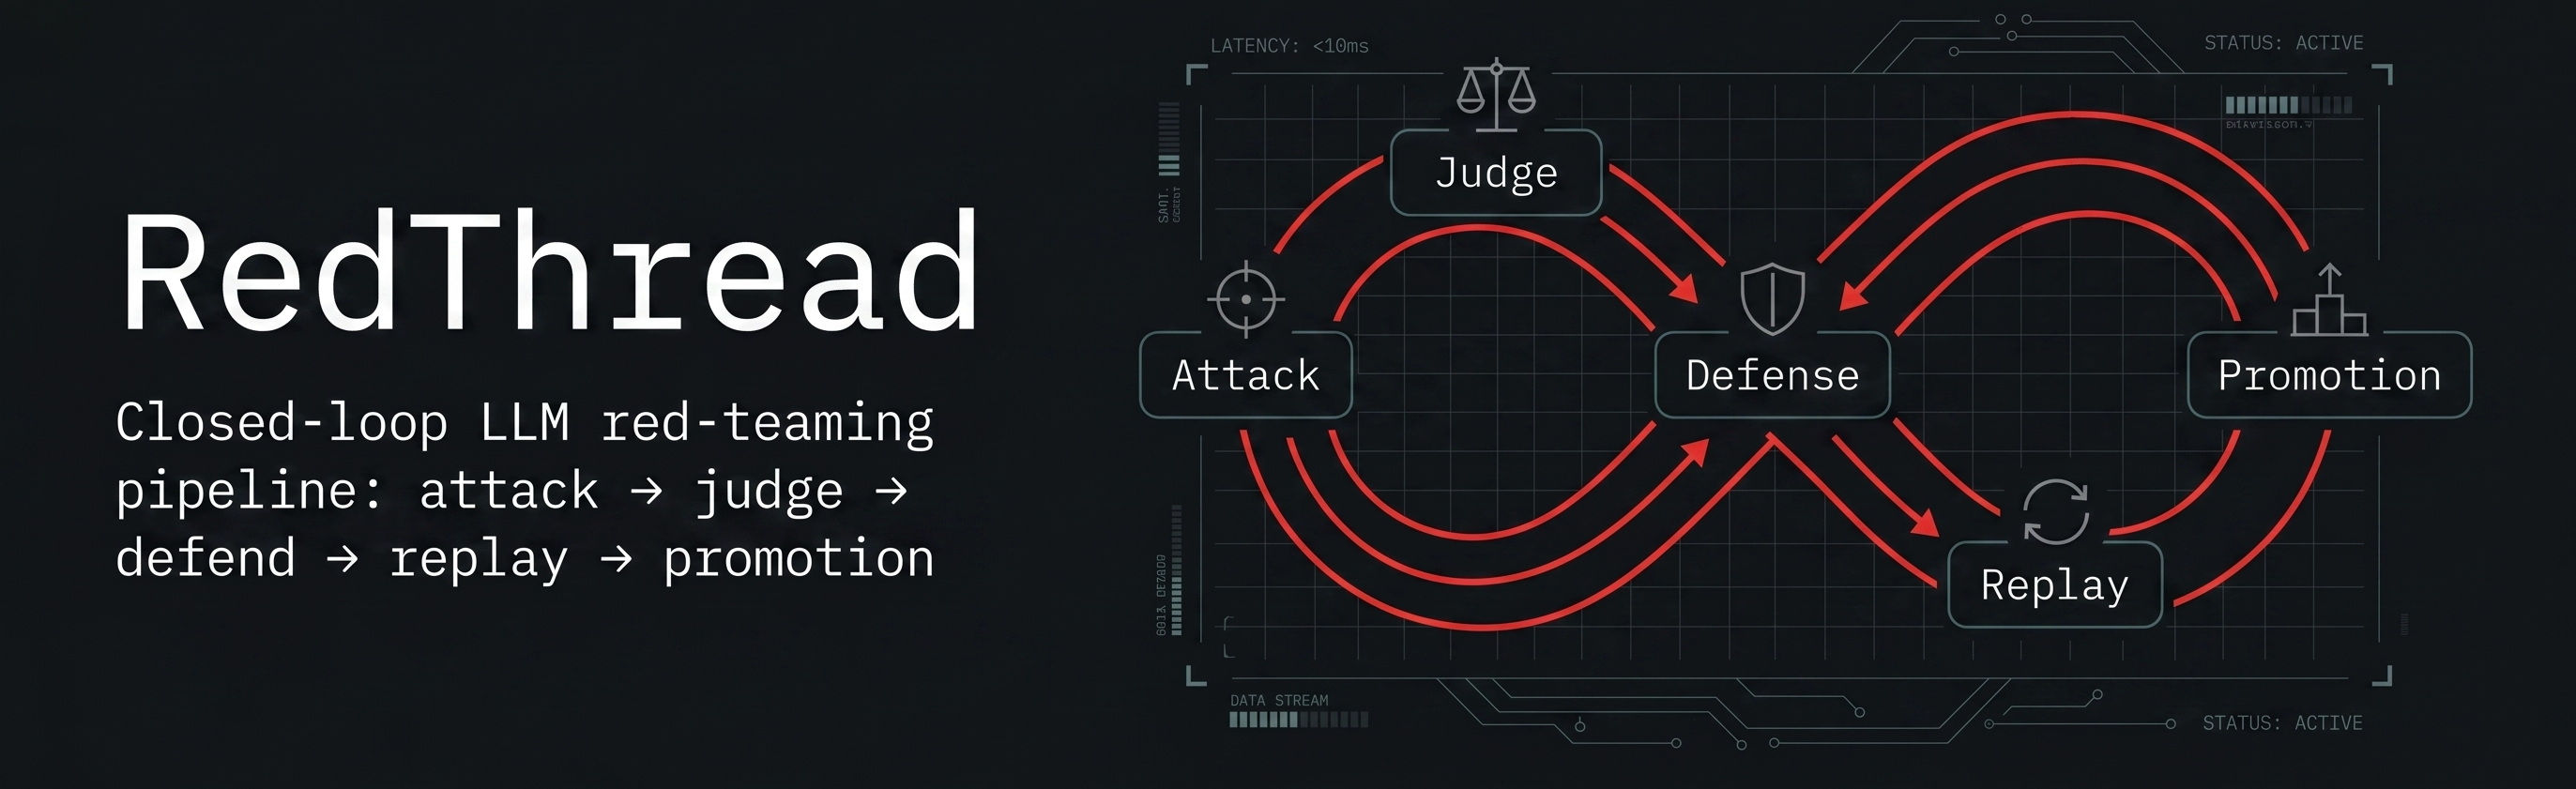 matheusht/redthread
An autonomous red-teaming engine for LLMs. RedThread manages the full security lifecycle: generating adversarial attacks, executing precision…
 owasp/redteamtoolkit
The WASM Based Security Toolkit for the Web First Paradigm
 4nuxd/react2shell
R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 havocframework/havoc
The Havoc Framework
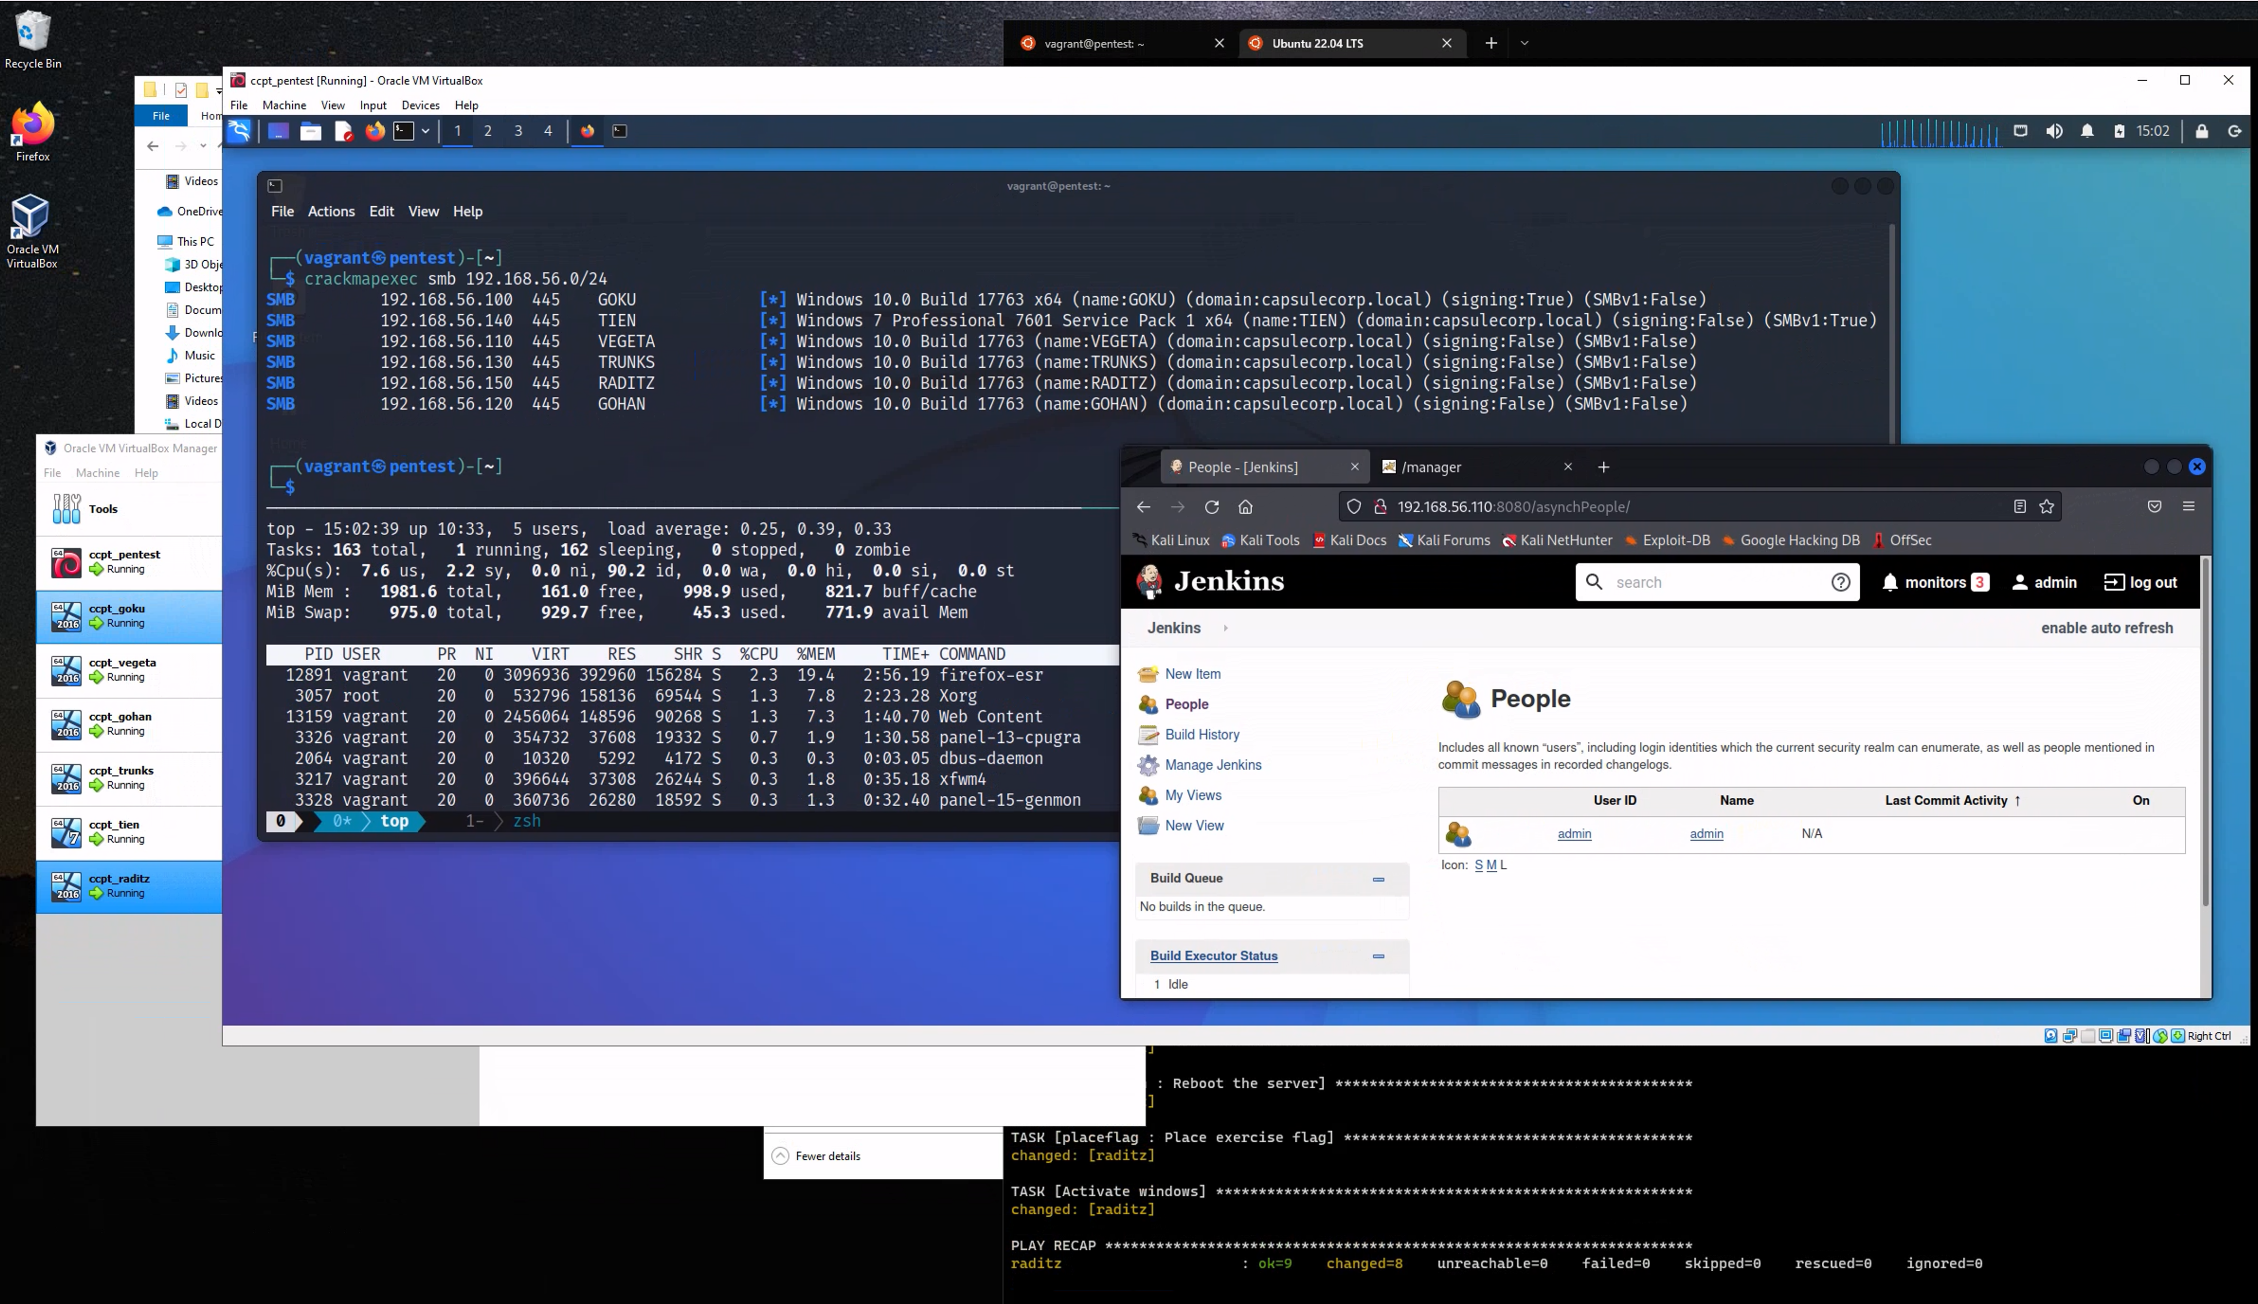 r3dy/capsulecorp-pentest
Vagrant VirtualBox environment for conducting an internal network penetration test
 seanheelan/anamnesis-release
Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…
