

dropengine
 s0lst1c3/dropengine
DropEngine provides a malleable framework for creating shellcode runners, allowing operators to choose from a selection of components and combine…
defensive-toolsexploit-frameworkspayload-development+5
214
s0lst1c3/dropengineDropEngine provides a malleable framework for creating shellcode runners, allowing operators to choose from a selection of components and combine…
 safebuffer/metateta
Automated network protocol scanner and exploiter leveraging Metasploit modules for rapid penetration testing across large networks, supporting SMB,…
 n1ckdunn/exploitivator
Automate Metasploit scanning and exploitation
 absllk/hexestra
AI-native penetration testing IDE where operators and an AI agent share browser, terminals, traffic capture, shells, asset graph, tasks, and evidence…
 mr-rizwan-syed/chomtesh
CHOMTE.SH is a powerful shell script designed to automate reconnaissance tasks during penetration testing. It utilizes various Go-based tools to…
 zcutlip/bowcaster
Python-based exploit development framework with payloads, encoders, and connect-back servers, focused on MIPS CPU architecture but designed for…
 cobbr/c2bridge
C2Bridges allow developers to create new custom communication protocols and quickly utilize them within Covenant.
 secureworks/whiskeysamlandfriends
Python-based framework for generating Golden SAML tokens, Kerberos tickets, and Azure Access Tokens to exploit federated identity systems and…
 01rabbit/pakuri
Semi-automated penetration testing framework with TUI, integrating Nmap, OpenVAS, Metasploit, and Faraday for streamlined information gathering,…
 threatexpress/threatbox
Ansible-based attack platform for deploying and managing a standardized Linux penetration testing environment with automated tool installation,…
 kalilinux/nethunter/build-scripts/kali-nethunter-installer
Builds flashable installer ZIPs that deploy a mobile penetration-testing environment on Android, including kernel boot patching, rootfs integration,…
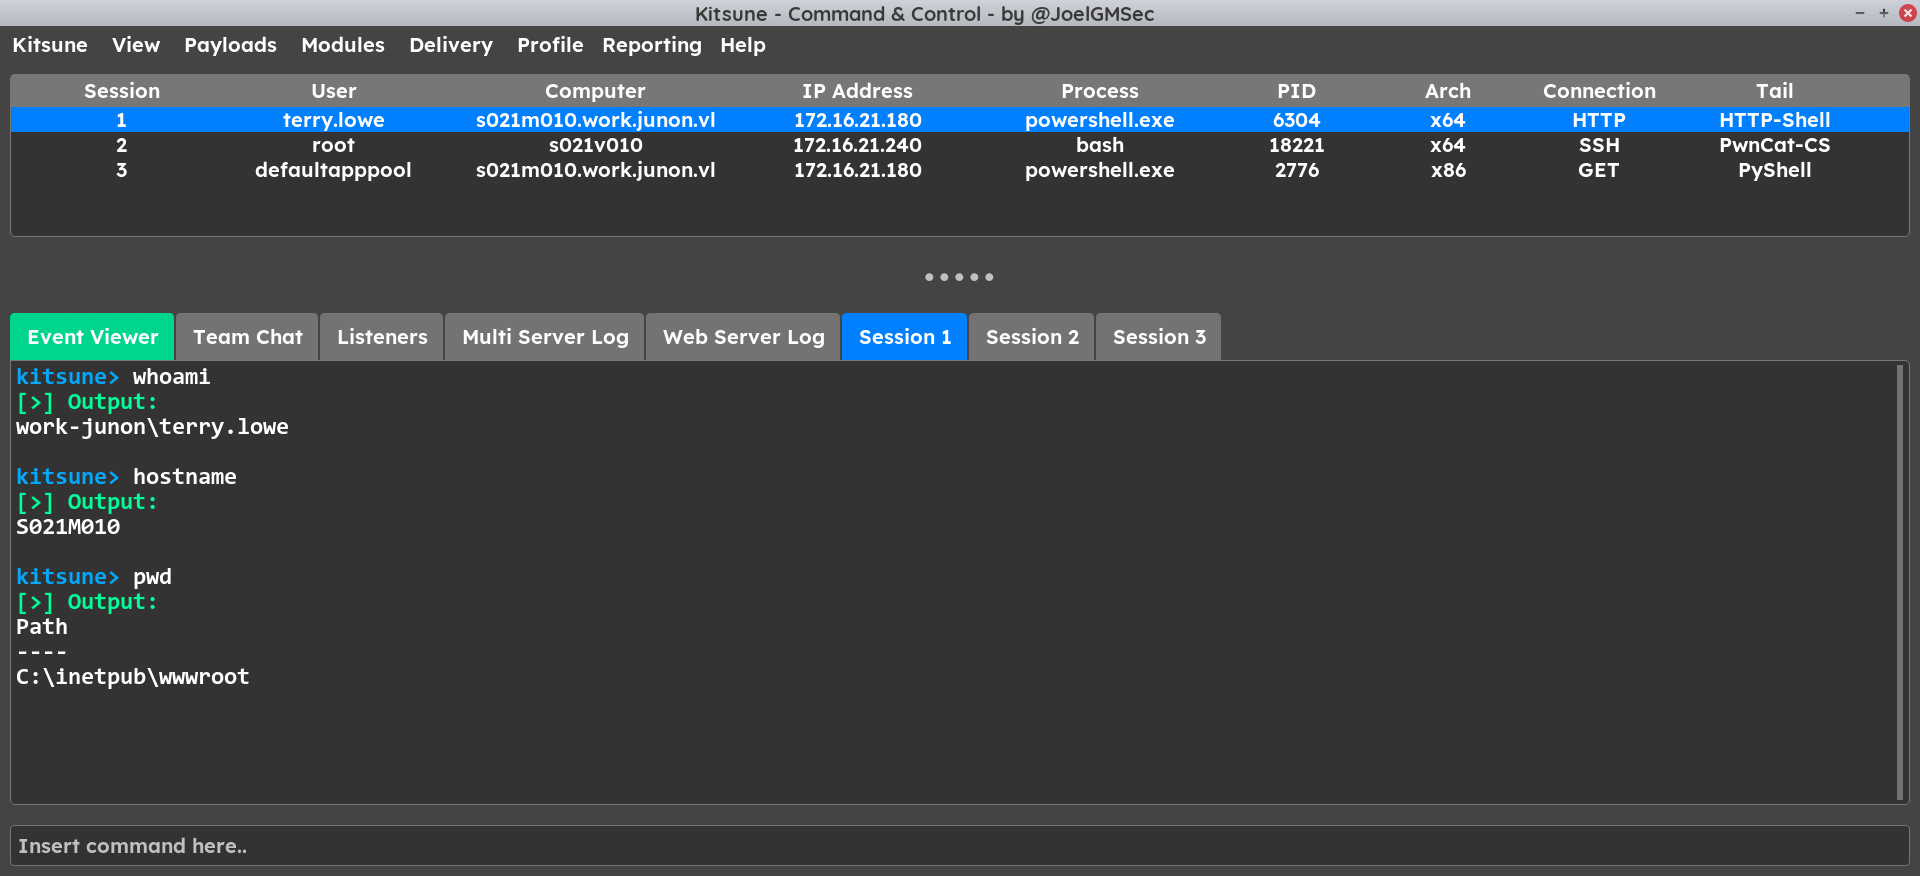 joelgmsec/kitsune
Polymorphic C2 framework with graphical interface, automatic reconnection, payload generation, and integrated hacking tools for red team operations…
 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
 ikotler/hackersh
A free and open source command-line shell and scripting language designed especially for security testing
 kuwaitist/astral_projection
Cobalt Strike UDRL that performs advanced module stomping using VEH to intercept calls, unmap modules during sleep, and remap fresh modules to evade…
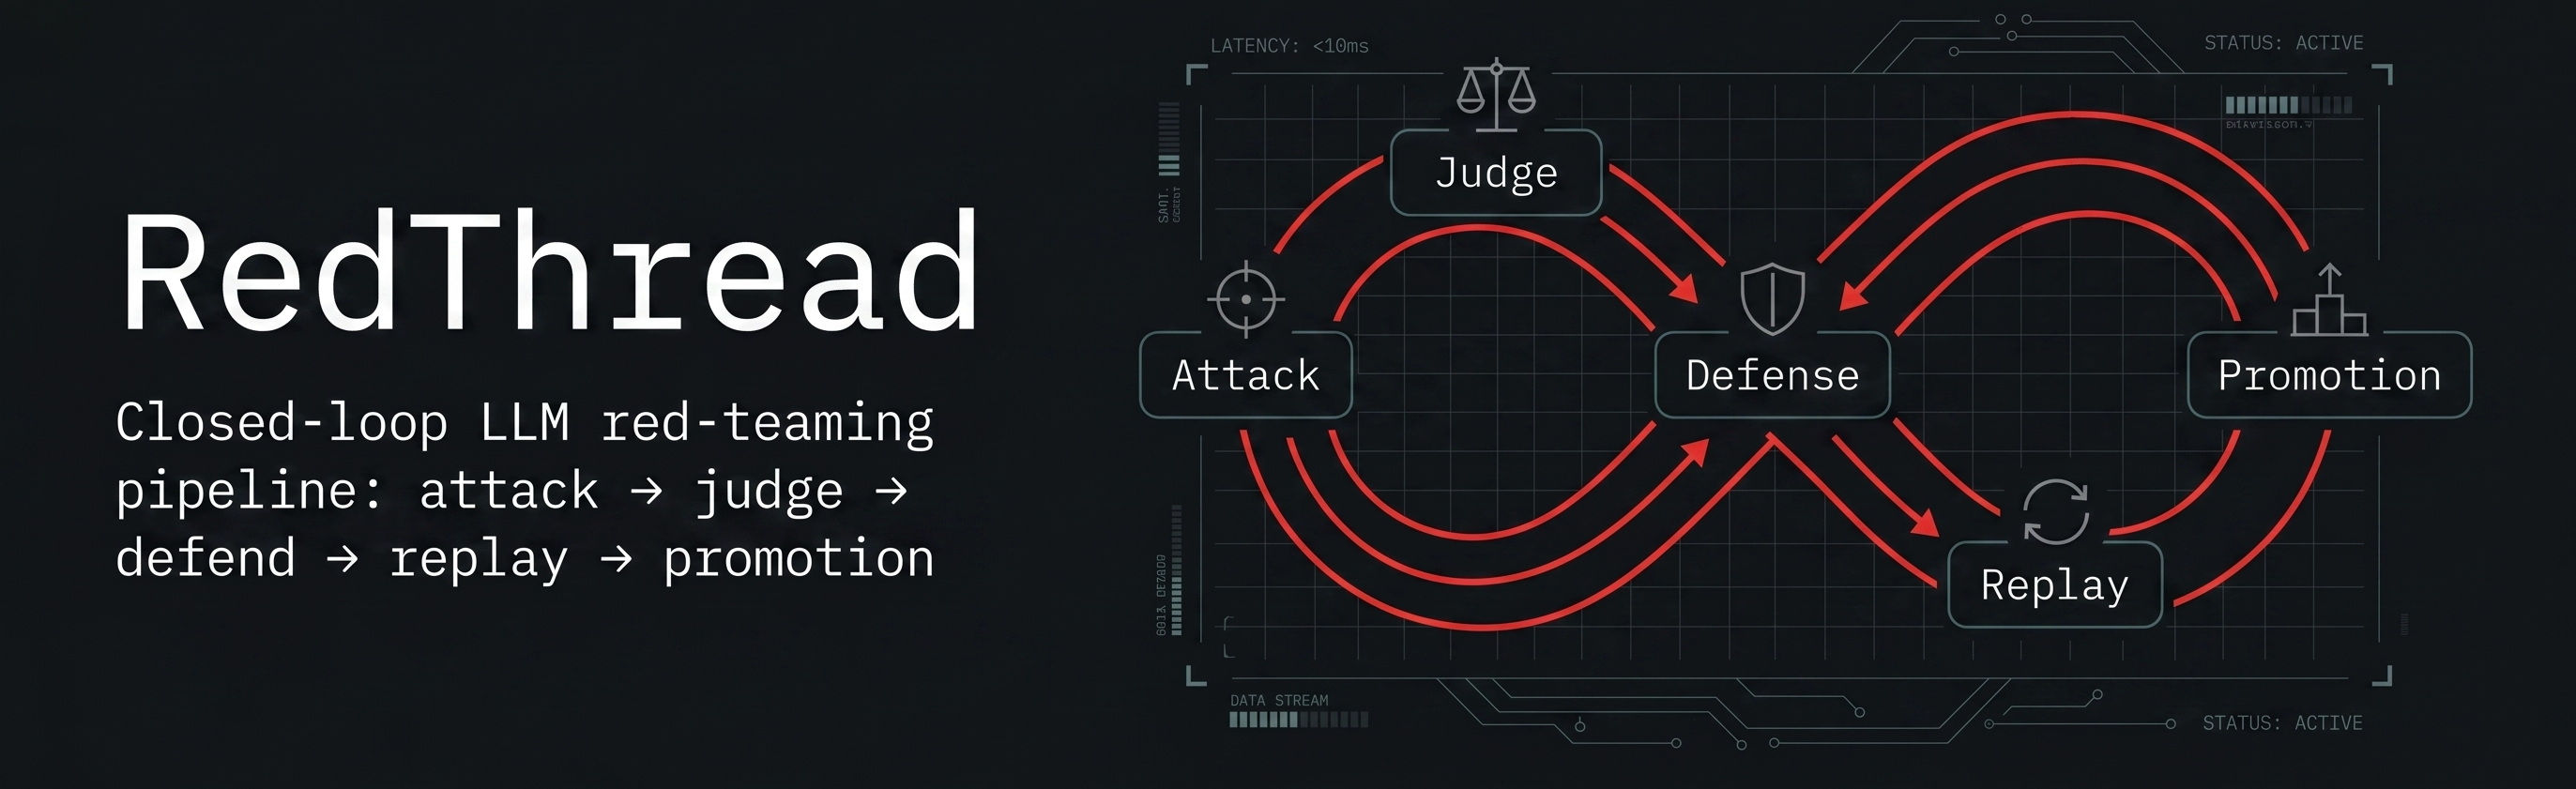 matheusht/redthread
An autonomous red-teaming engine for LLMs. RedThread manages the full security lifecycle: generating adversarial attacks, executing precision…
 redherd-project/redherd-framework
RedHerd is a collaborative and serverless framework for orchestrating a geographically distributed group of assets.
 professionallyevil/c4
Cyberdelia, a Collection of Command and Control frameworks