Apache-2.4.49-2.4.50-Traversal-Remote-Code-Execution-Exploit

This Metasploit module exploits an unauthenticated remote code execution vulnerability which exists in Apache version 2.4.49 (CVE-2021-41773). If…

This Metasploit module exploits an unauthenticated remote code execution vulnerability which exists in Apache version 2.4.49 (CVE-2021-41773). If…

Python-Based Pentesting CLI Tool

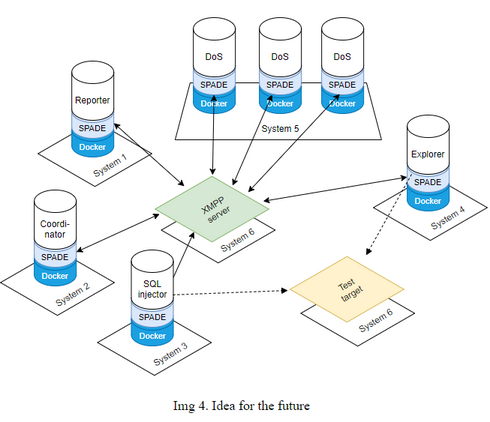
Multi-Agent System for Automated Penetration Testing (MASAPT)

Windows service agent for CALDERA adversary emulation platform. Installed on target computers to communicate with the CALDERA server, enabling…

SigPloit: Telecom Signaling Exploitation Framework - SS7, GTP, Diameter & SIP

Collection of Aggressor scripts for Cobalt Strike 3.0+ pulled from multiple sources

CLI tool for the Horizon3.ai API

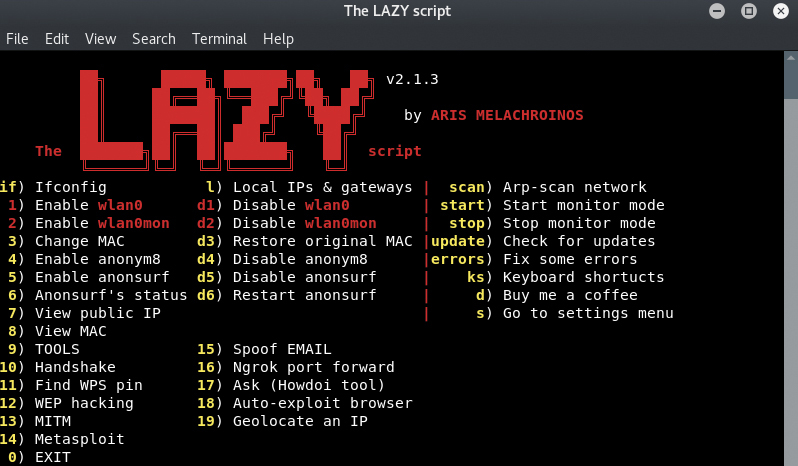
The LAZY script will make your life easier, and of course faster.

The Python Risk Identification Tool for generative AI (PyRIT) is an open source framework built to empower security professionals and engineers to…

HVNC for Cobalt Strike

An AI-powered threat modeling tool that leverages OpenAI's GPT models to generate threat models for a given application based on the STRIDE…

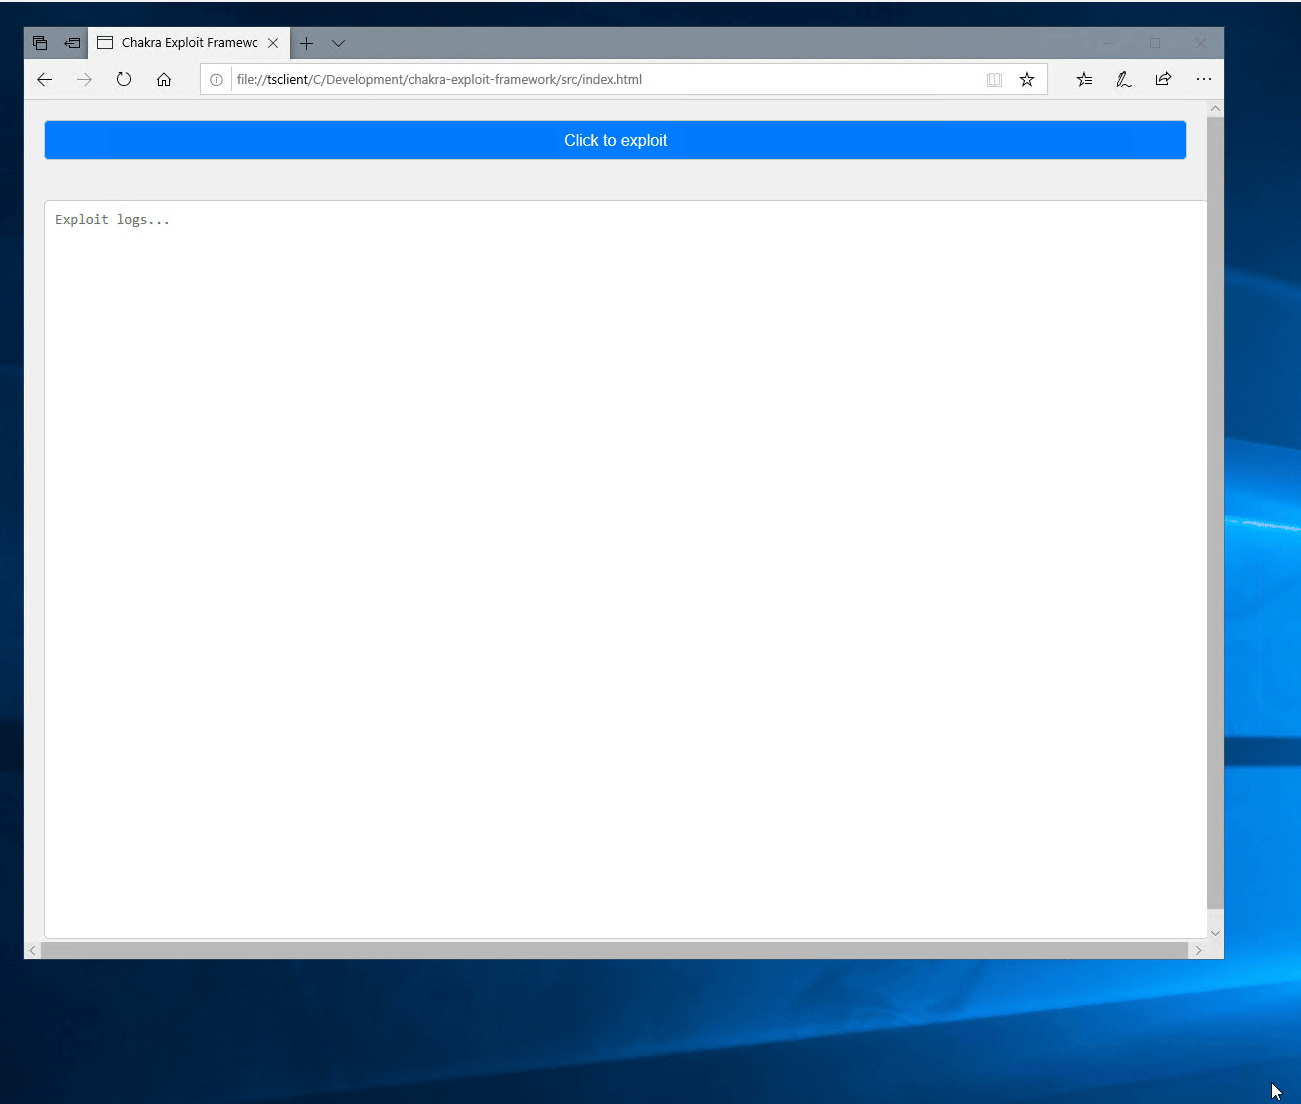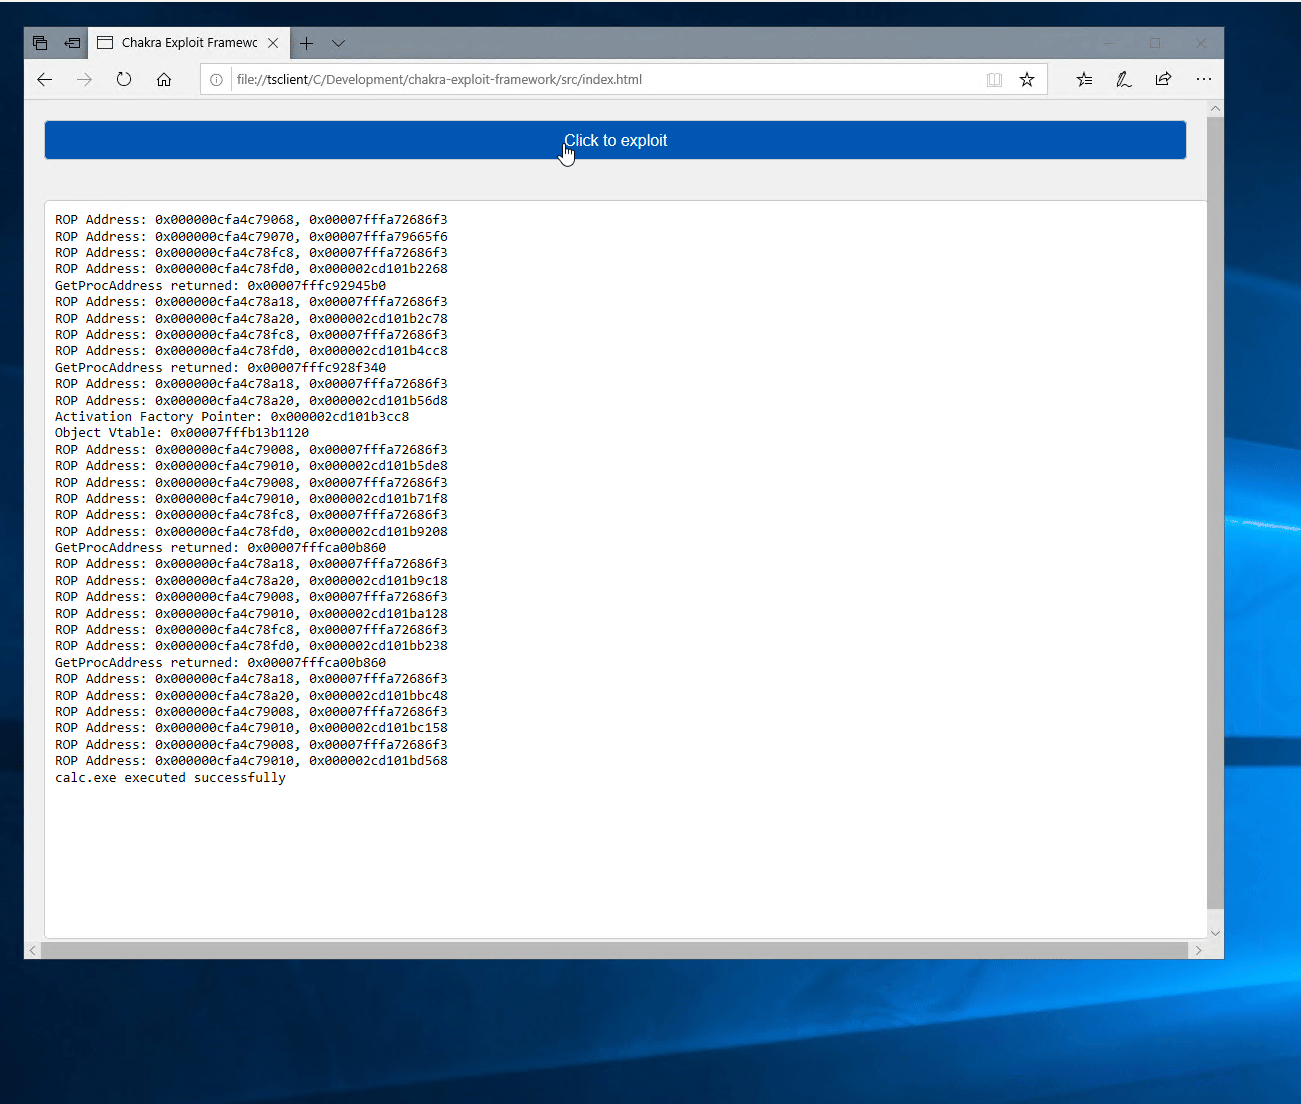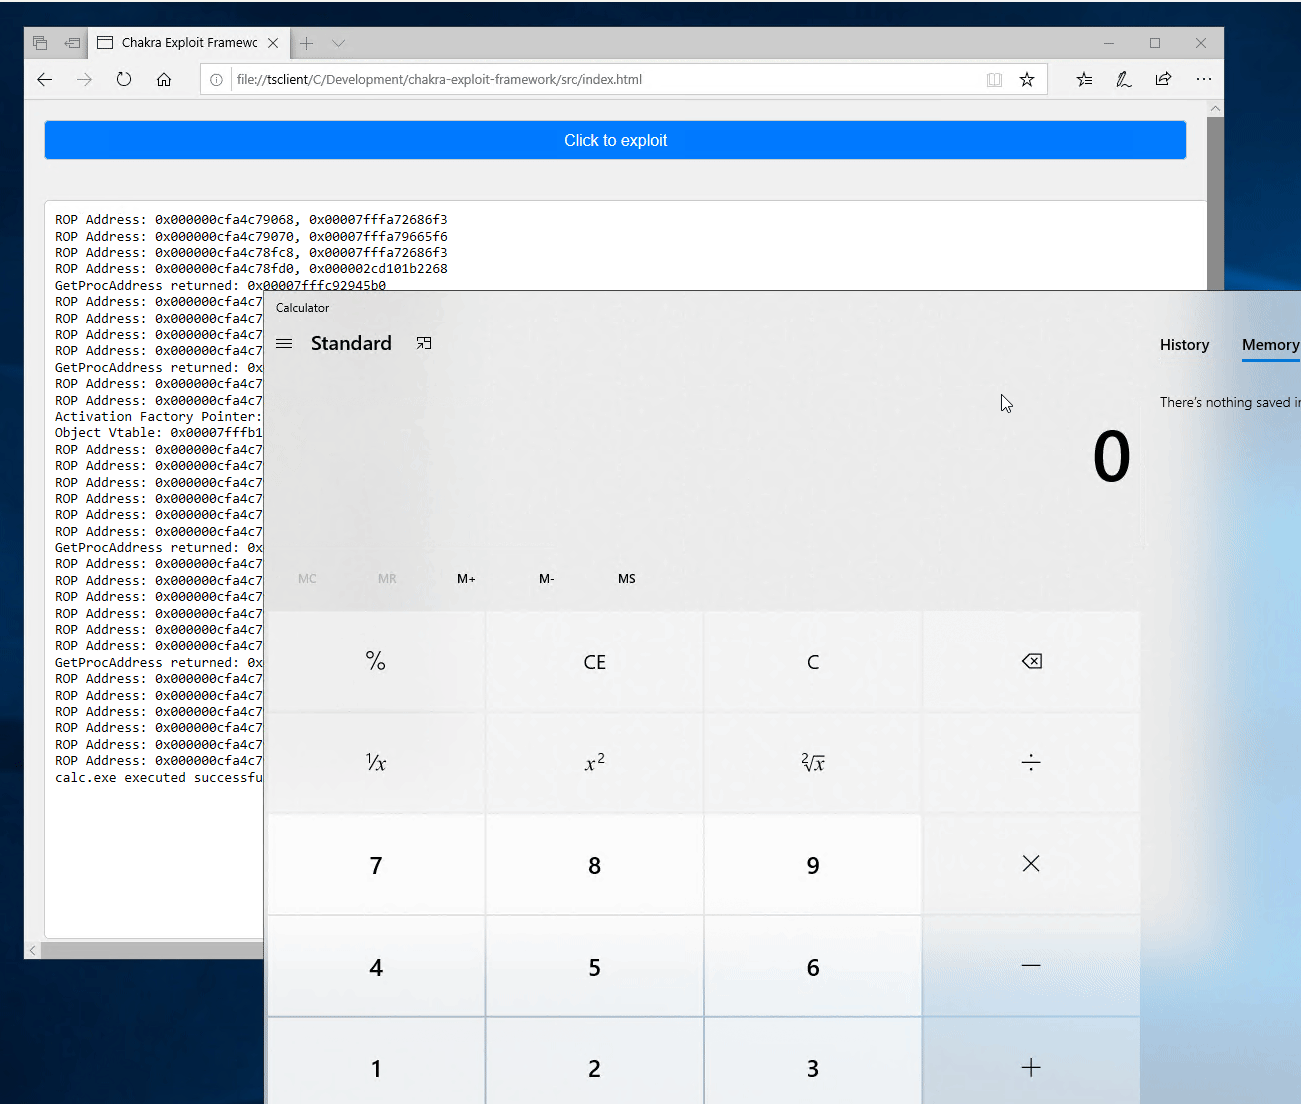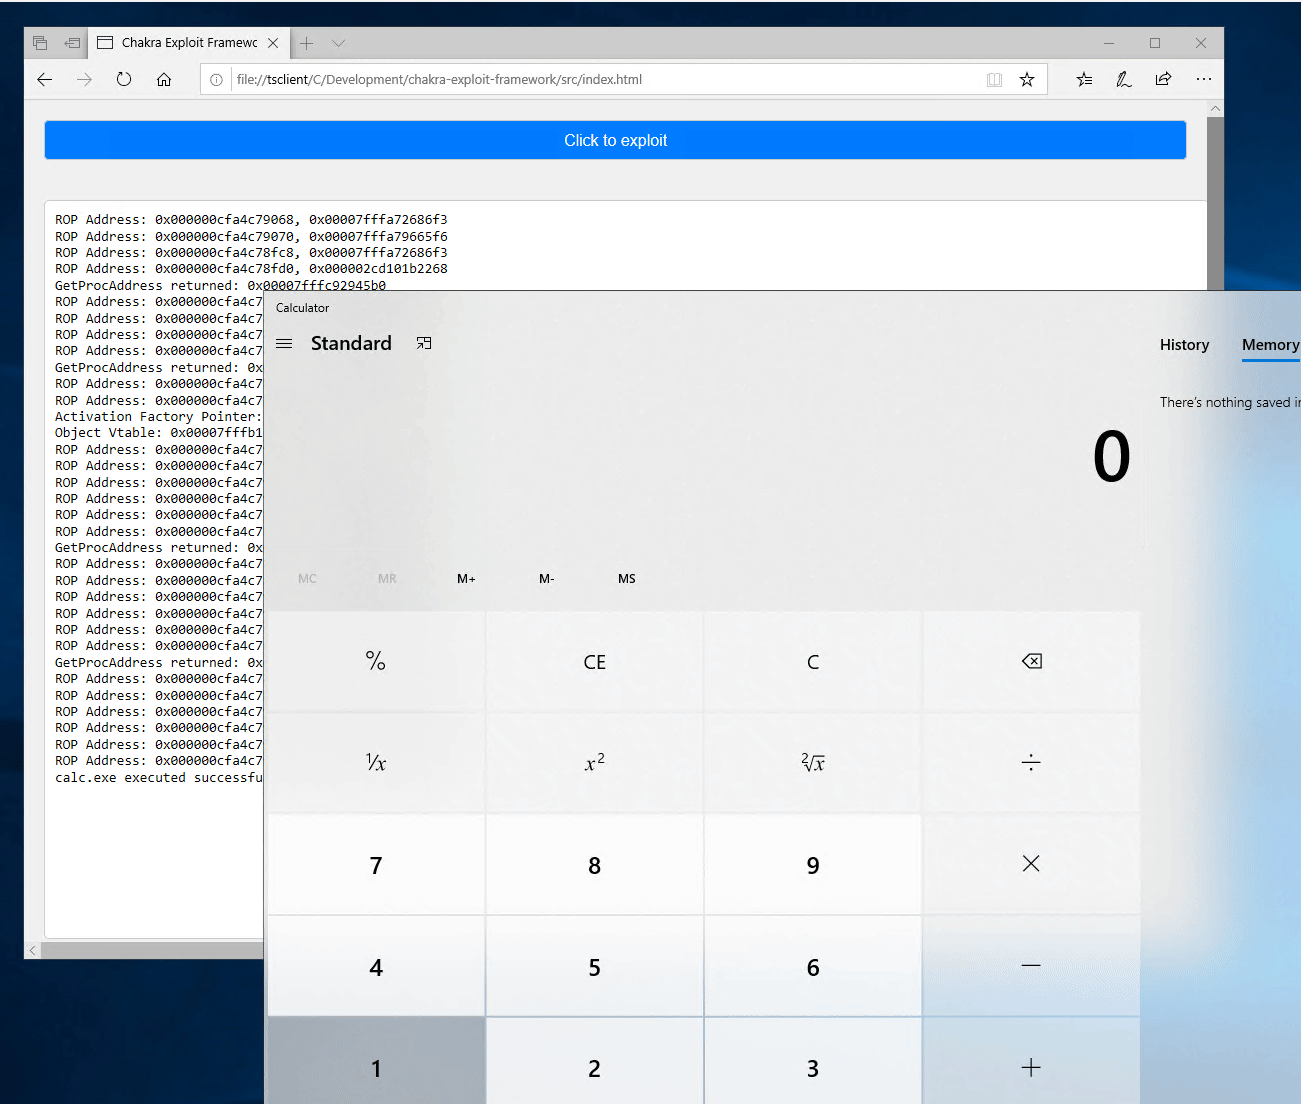
Browser exploitation framework for Chakra (Edge). Written as part of OSEE preparation. Demo bug: CVE-2019-0567

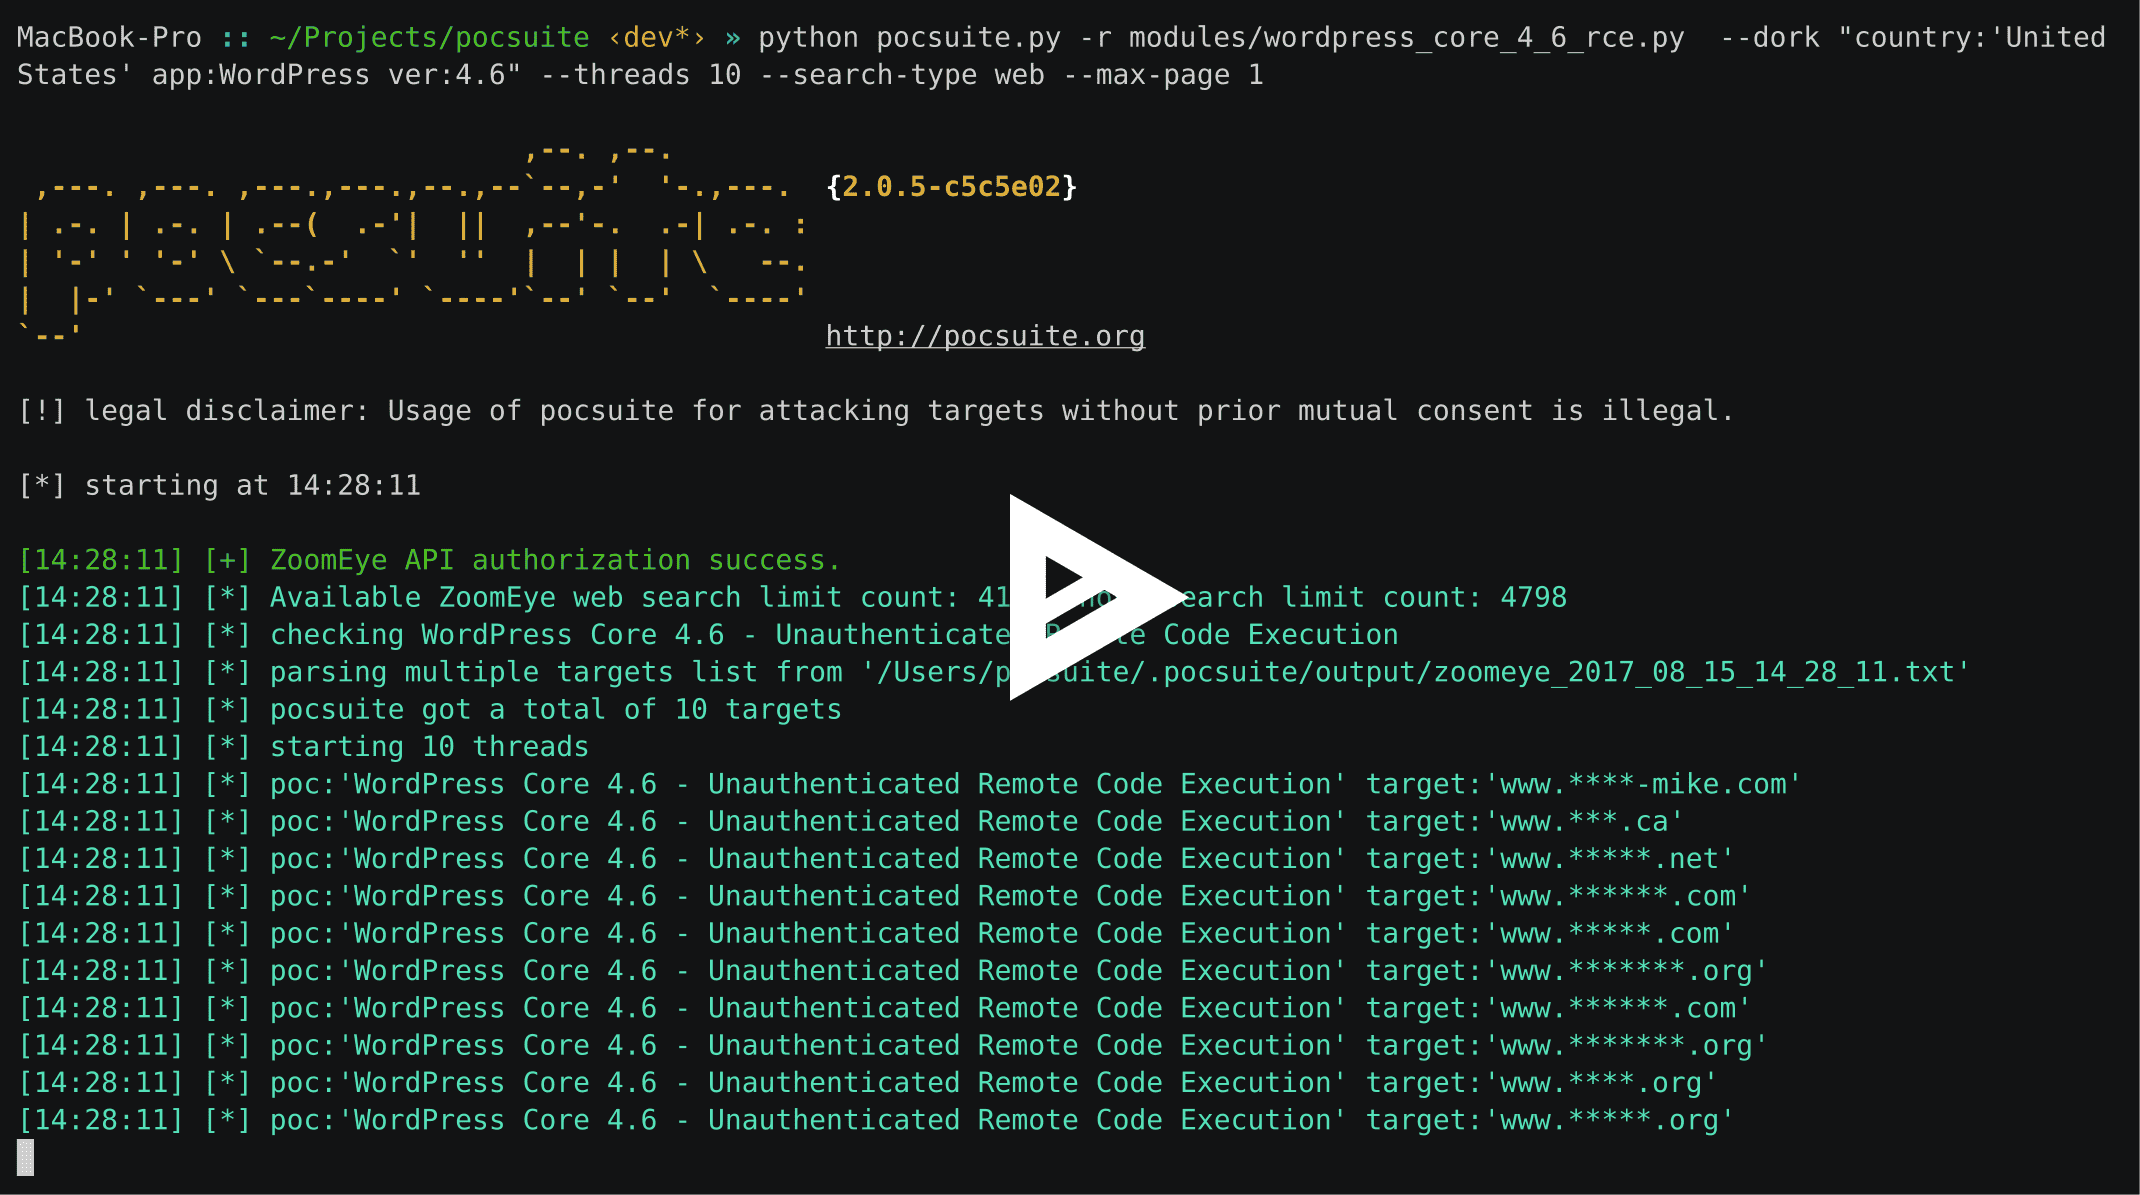
This project has stopped to maintenance, please to https://github.com/knownsec/pocsuite3 project.

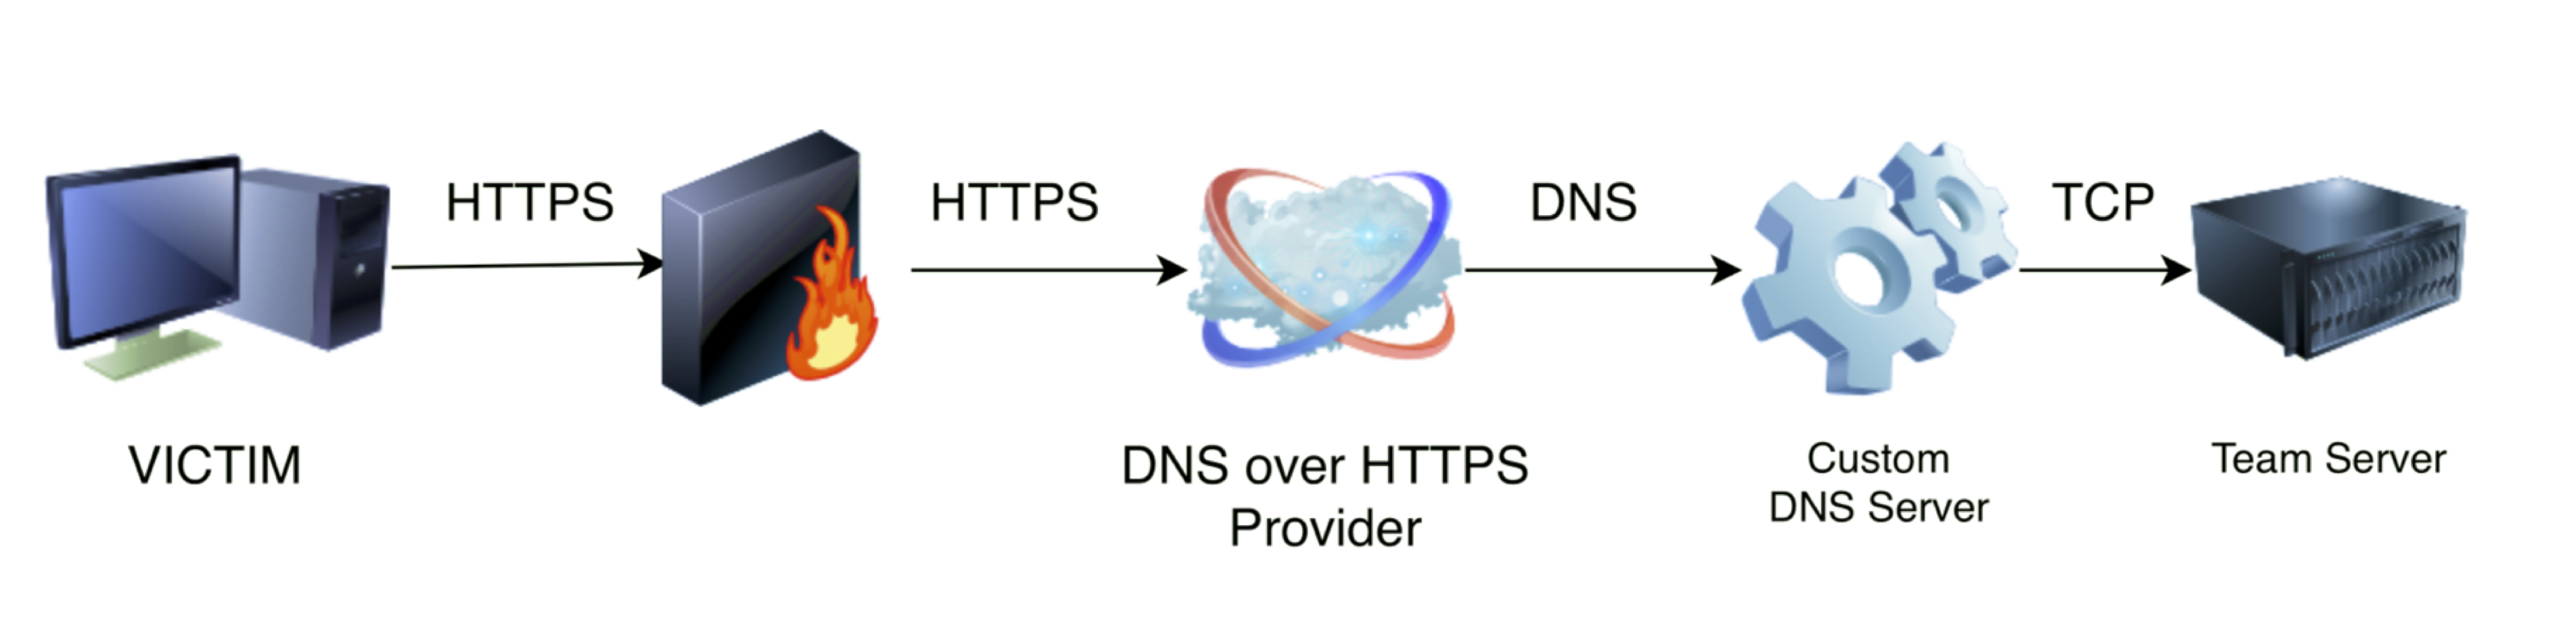
DoHC2 allows the ExternalC2 library from Ryan Hanson (https://github.com/ryhanson/ExternalC2) to be leveraged for command and control (C2) via DNS…

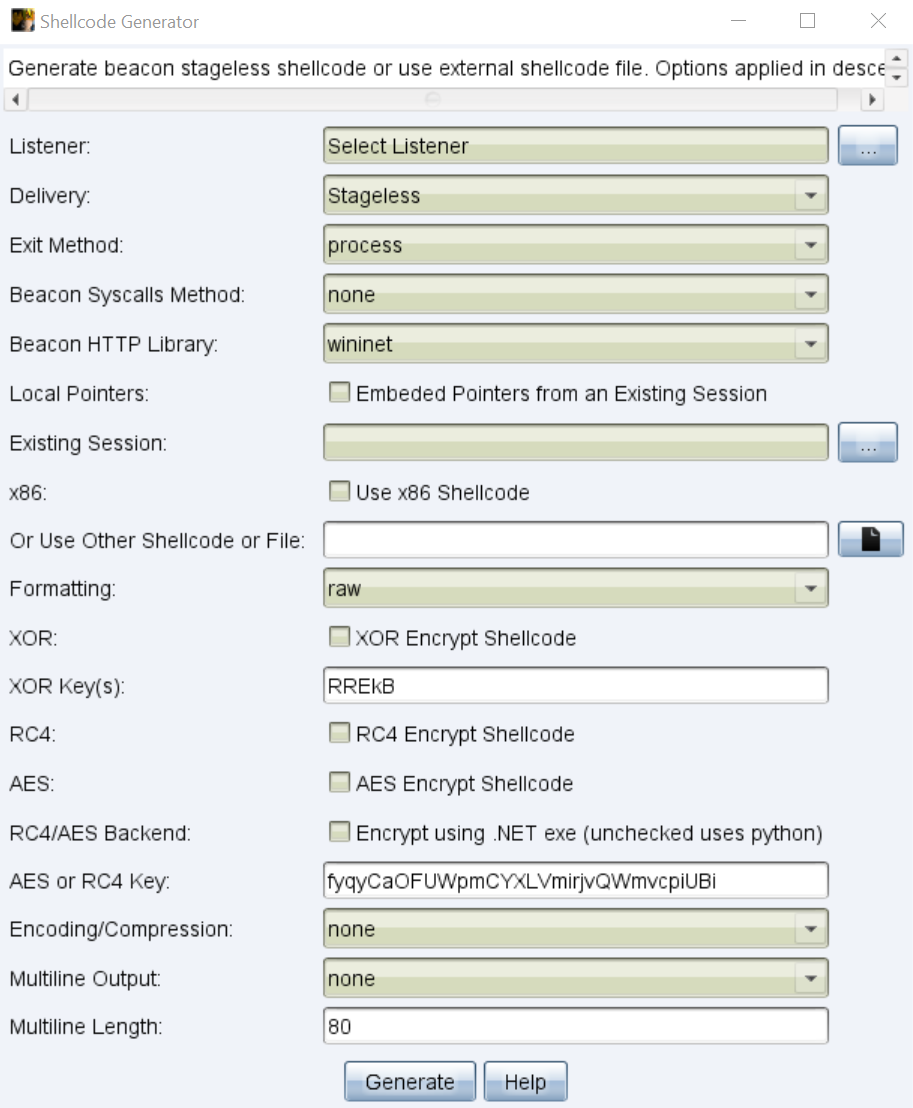
Cobalt Strike aggressor script for generating, formatting, and encrypting beacon shellcode with support for multiple exit methods, syscalls, and…

Automated Adversary Emulation Platform

An SDN penetration testing toolkit

A desktop operator console for Sliver C2, built with Wails. Provides a native, lightweight GUI interface for Sliver by directly interfacing with its…