
smokedmeat
 boostsecurityio/smokedmeat
A CI/CD Red Team Framework for demonstrating Build Pipeline security risks.
cloud-securitycommand-and-controleducation+9
394
boostsecurityio/smokedmeatA CI/CD Red Team Framework for demonstrating Build Pipeline security risks.
 gl4ssesbo1/nebula
Nebula is a cloud C2 Framework, which at the moment offers reconnaissance, enumeration, exploitation, post exploitation on AWS, but still working to…
 28zaaky/khaos-c2
KHAOS is a modern C2 framework that routes agent traffic through cloud services already trusted by enterprise networks.
 enkomio/alanframework
A C2 post-exploitation framework
 itaymigdal/nimbo-c2
Nimbo-C2 is yet another (simple and lightweight) C2 framework
 xtr4nge/fruityc2
FruityC2 is a post-exploitation (and open source) framework based on the deployment of agents on compromised machines. Agents are managed from a web…
 redsiege/persistassist
Fully modular persistence framework
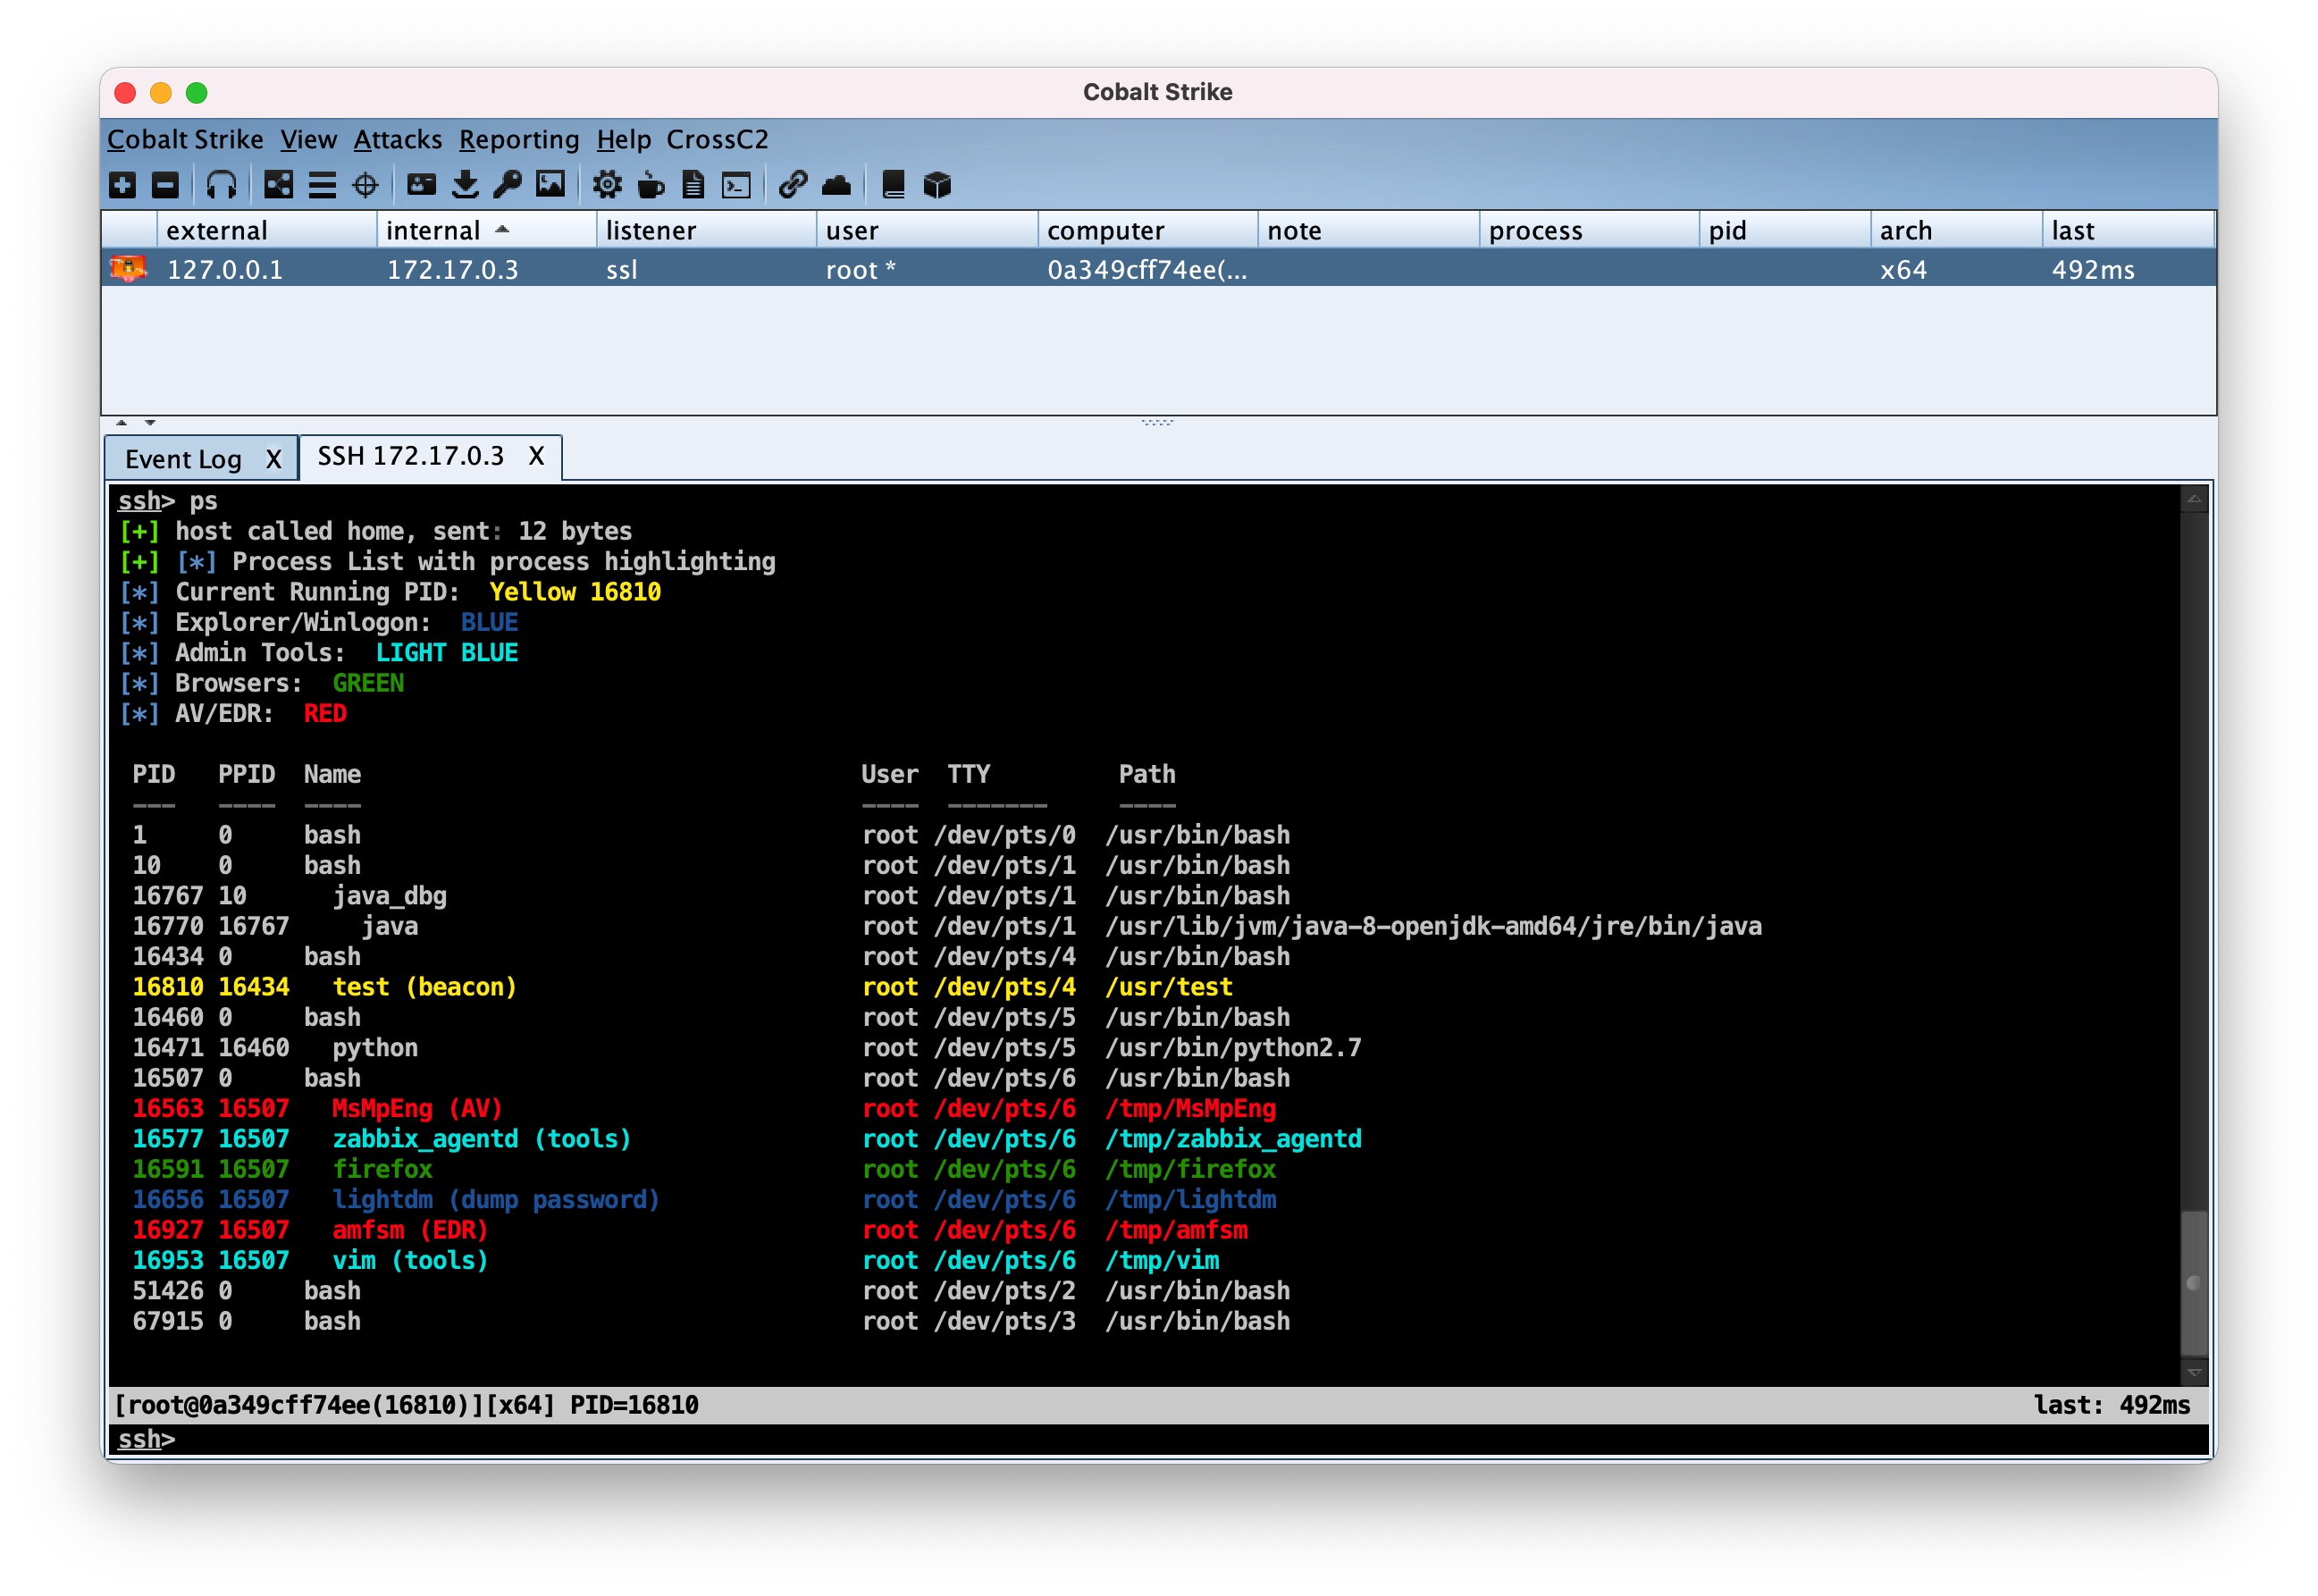 crossc2/crossc2kit
CrossC2 developed based on the Cobalt Strike framework can be used for other cross-platform system control. CrossC2Kit provides some interfaces for…
 sliverarmory/sliver-gui
Cross-platform Electron GUI for the Sliver C2 framework, providing session and beacon dashboards, payload generation, listeners, loot, and cloud…
 trustedsec/specula
Modular command-and-control framework abusing Microsoft Outlook's Home Page feature for stealthy persistence, remote access, and post-exploitation.
 darmado/atomic-red-team-c2
ARTi-C2 is a post-exploitation framework used to execute Atomic Red Team test cases with rapid payload deployment and execution capabilities via…
 acedef/synthapt
Playbook-based adversary simulation framework that compiles JSON-defined attack paths into position-independent shellcode payloads for validating…
 zerodaylab/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
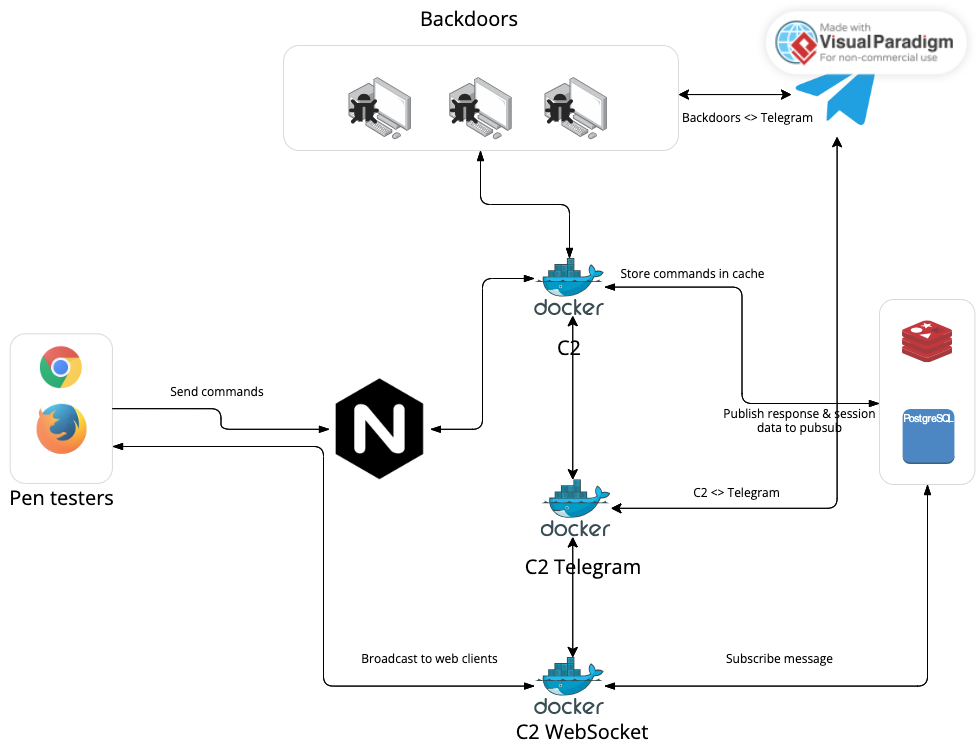 govindasamyarun/c2-cloud
The C2 Cloud is a robust web-based C2 framework, designed to simplify the life of penetration testers. It allows easy access to compromised…
 cisc0-gif/kitt-lite
Python-Based Pentesting CLI Tool
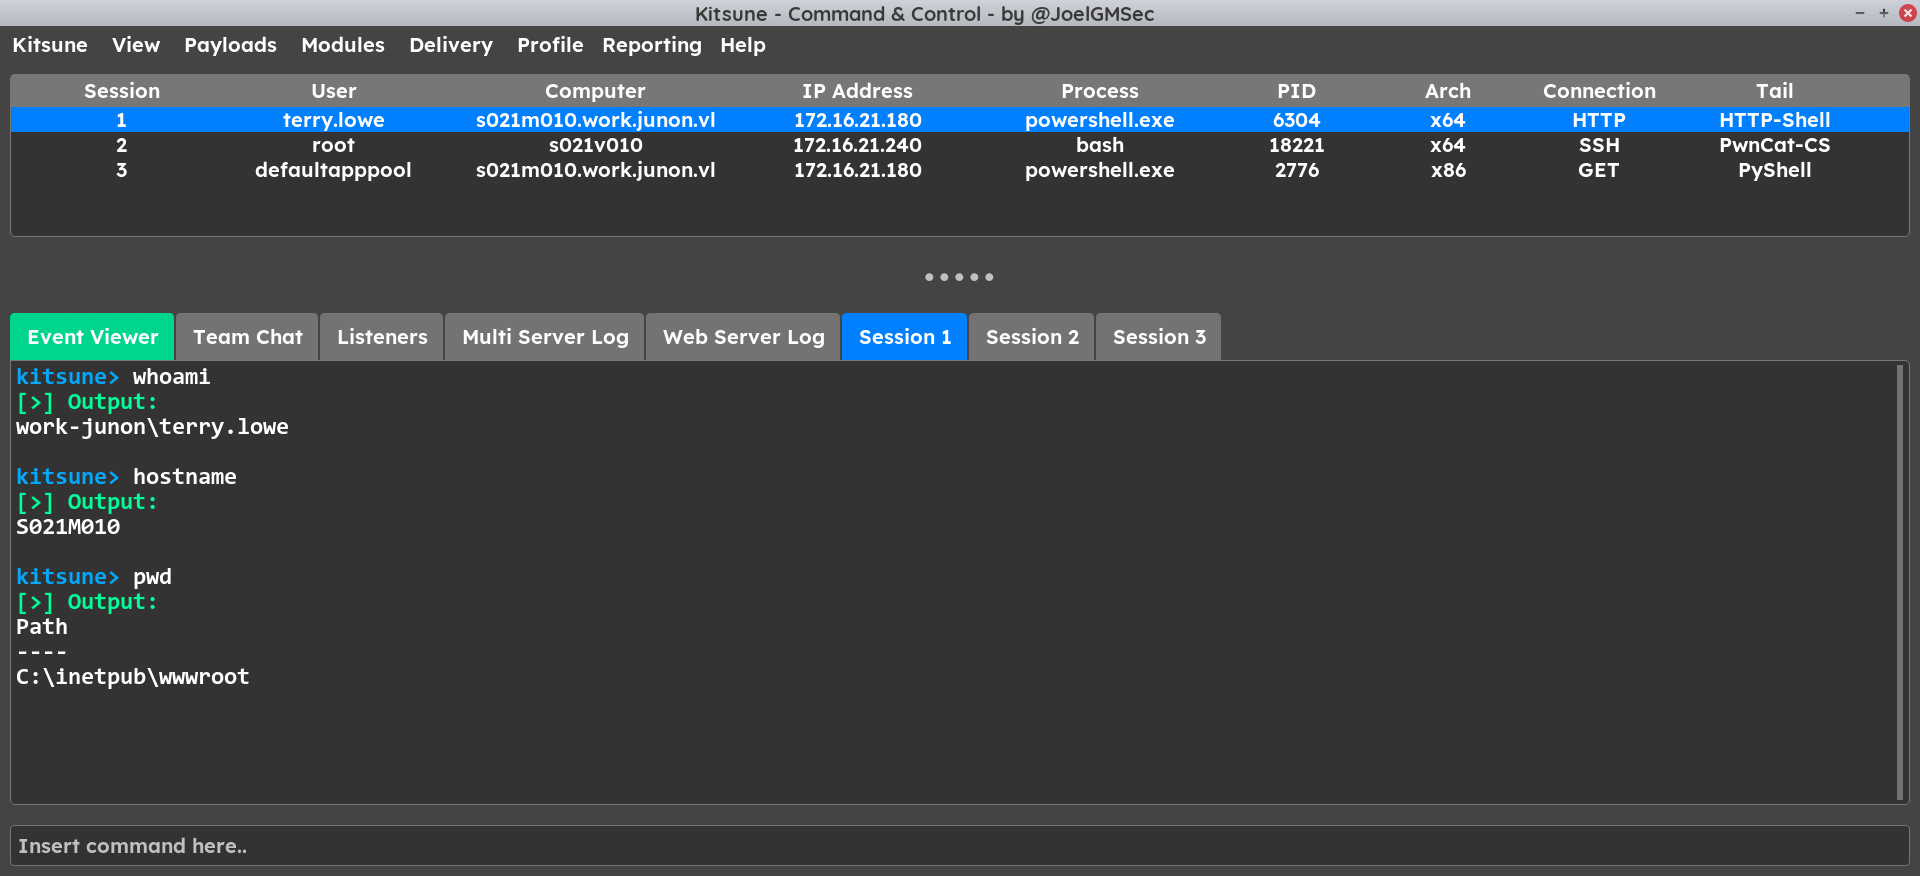 joelgmsec/kitsune
Polymorphic C2 framework with graphical interface, automatic reconnection, payload generation, and integrated hacking tools for red team operations…
 xret2pwn/picklec2
Encrypted C2 framework for post-exploitation and lateral movement, supporting PowerShell implants and custom modules for red team engagements.
 lame-projects/stratum-c2
Cloud dead-drop C2 framework — RSA-4096 + AES-256-GCM, 5 cloud providers, Rust-only agents, P2P mesh, persistence engine, credential harvesting