
redherd-framework
 redherd-project/redherd-framework
RedHerd is a collaborative and serverless framework for orchestrating a geographically distributed group of assets.
penetration-testing-frameworksred-teaming
redherd-project/redherd-frameworkRedHerd is a collaborative and serverless framework for orchestrating a geographically distributed group of assets.
 bishopfox/joro
A collaborative web exploitation framework.
 elevenpaths/siemframework
Modular Python3 attack framework for automating exploitation of SIEM platforms (Splunk, Graylog, OSSIM, QRadar, McAfee) via credential theft, payload…
 karmanya03/overthrone
All-Rust Active Directory exploitation framework: LDAP/SMB/Kerberos enumeration, attack-graph pathfinding, Kerberoasting, NTLM relay, ticket forging,…
 bitplugg/kitsune
🦊 nine-tailed pentest framework — nmap + msf + aircrack + sqlmap в одном CLI · 25 модулей · SQLite-сессия · TUI · REST API · pipx install
 g0d150ne/wp2shell
Modular WordPress pre-auth exploit framework chaining SQL injection and authentication bypass to deliver remote code execution, interactive shells,…
 black-army-security/blackarmy-framework
Modular Python-based penetration testing framework for automated security assessments, exploitation, and red team operations. Includes modules for…
 h3x0v3rl0rd/cve-2019-9053
Python exploit for CVE-2019-9053 targeting a SQL injection vulnerability in CMS Made Simple. Automates time-based blind SQLi to extract admin…
 blueisbeautiful/cve-2018-19323
An exploitation framework for CVE-2018-19323 - GIGABYTE GDrv privilege escalation vulnerability with multi-architecture support and framework…
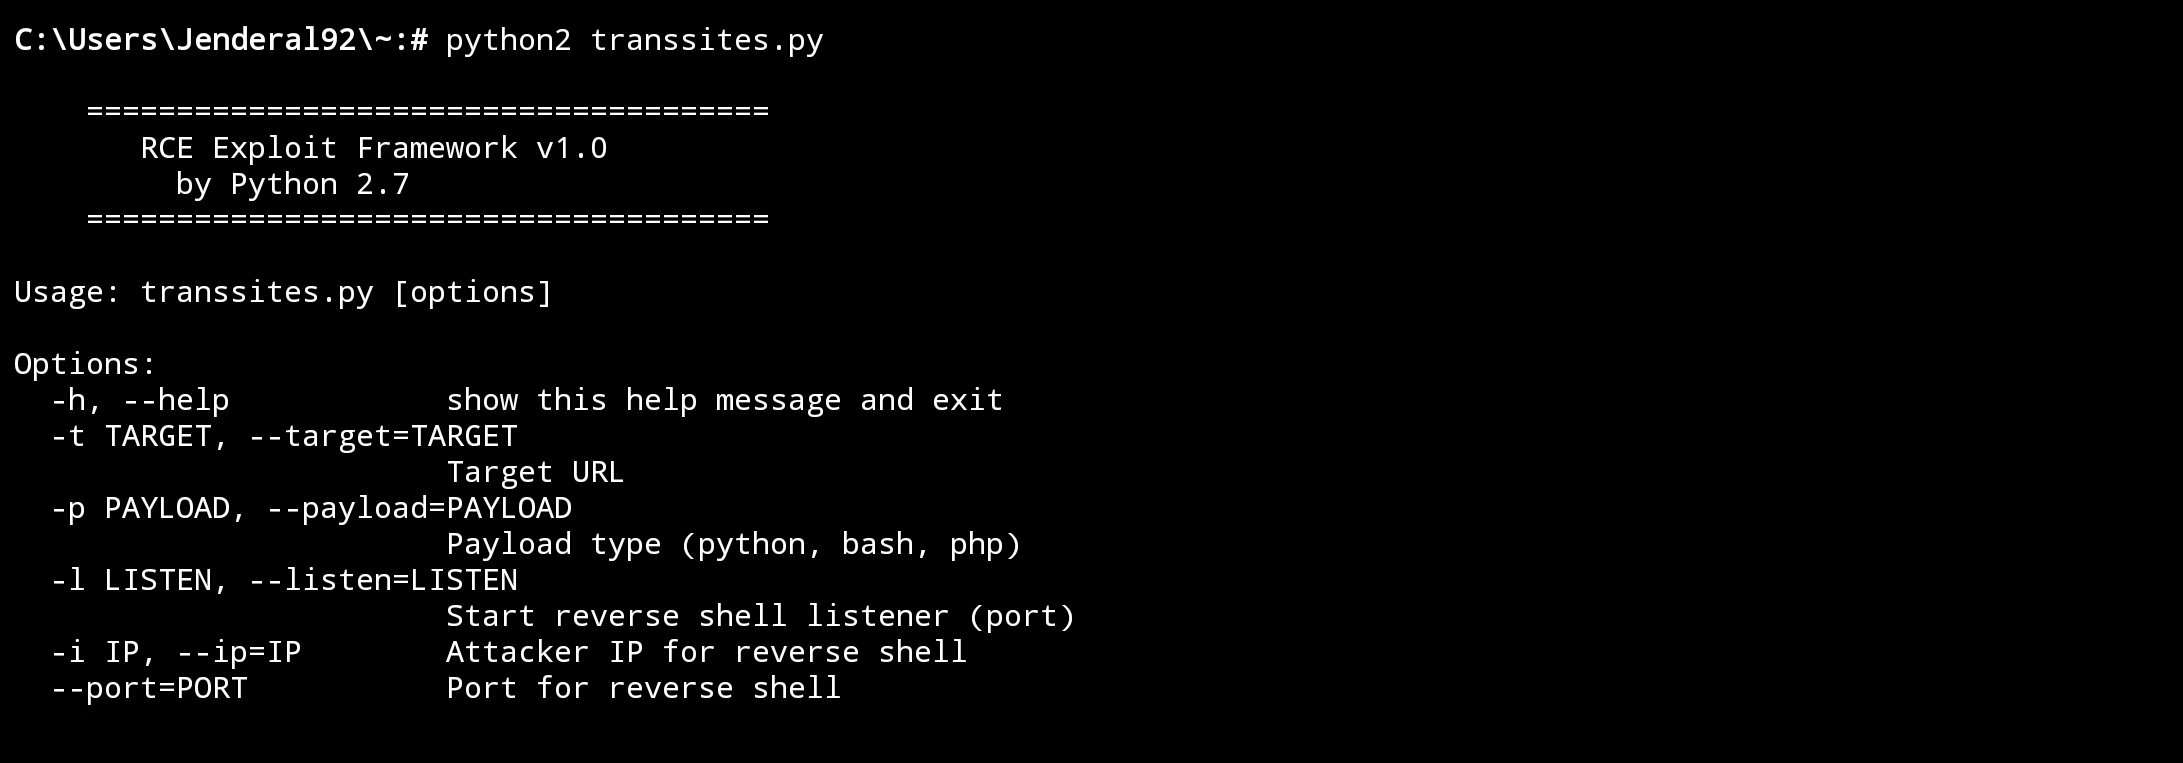 jenderal92/rce-exploit-framework
This framework is designed to assist penetration testers or developers in understanding the mechanics of remote code execution (RCE) exploitation.
 havocframework/havoc
The Havoc Framework
 spellshift/realm
Cross-platform adversary emulation framework with a Rust implant, GraphQL teamserver, and Eldritch DSL for automated, scalable red team operations…
 dark-lbp/isf
ISF(Industrial Control System Exploitation Framework),a exploitation framework based on Python
 phoenixc2/phoenixc2
Command & Control-Framework created for collaboration in python3
 trustedsec/social-engineer-toolkit
The Social-Engineer Toolkit (SET) repository from TrustedSec - All new versions of SET will be deployed here.
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
 byt3bl33d3r/silenttrinity
An asynchronous, collaborative post-exploitation agent powered by Python and .NET's DLR
 r00ts3c/ddos-rootsec
Explore RootSec's DDOS Archive, featuring top-tier scanners, powerful botnets (Mirai & QBot) and other variants, high-impact exploits, advanced…