

LibAFL
 aflplusplus/libafl
Advanced Fuzzing Library - Slot your Fuzzer together in Rust! Scales across cores and machines. For Windows, Android, MacOS, Linux, no_std, ...
binary-analysisdynamic-analysis-sandboxingeducation+5
2.6k
aflplusplus/libaflAdvanced Fuzzing Library - Slot your Fuzzer together in Rust! Scales across cores and machines. For Windows, Android, MacOS, Linux, no_std, ...
 datadog/stratus-red-team
:cloud: :zap: Granular, Actionable Adversary Emulation for the Cloud
 netspi/powerupsql
PowerUpSQL: A PowerShell Toolkit for Attacking SQL Server
 zerbea/hcxtools
A small set of tools to convert packets from capture files to hash files for use with Hashcat or John the Ripper.
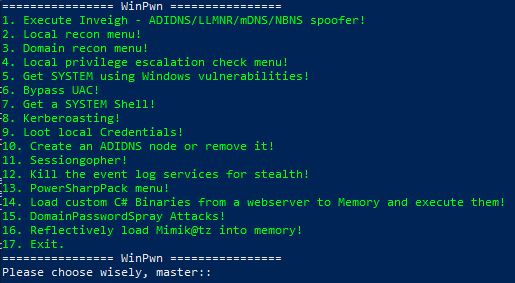 s3cur3th1ssh1t/winpwn
Automation for internal Windows Penetrationtest / AD-Security
 0xsteph/pentest-ai-agents
Turn Claude Code into your offensive security research assistant. Specialized AI subagents for authorized penetration testing plan engagements,…
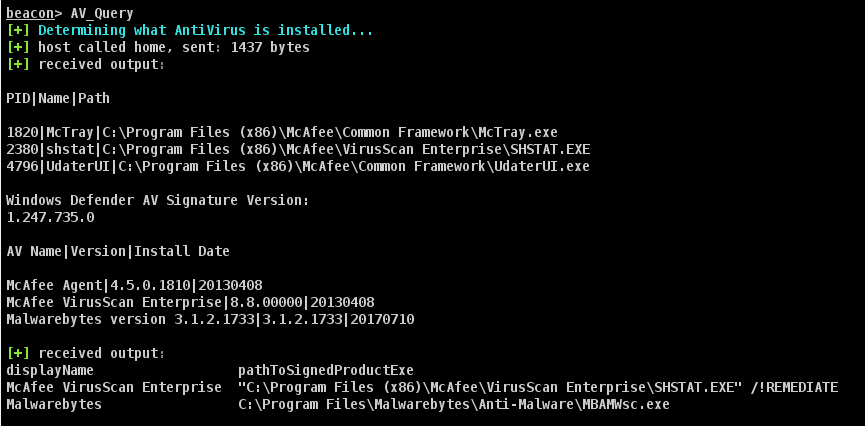 harleyqu1nn/aggressorscripts
Collection of Aggressor scripts for Cobalt Strike 3.0+ pulled from multiple sources
 dradis/dradis-ce
Dradis Framework: Collaboration and reporting for IT Security teams
 redsiege/c2concealer
Generates randomized, lint-validated C2 malleable profiles for Cobalt Strike, automating HTTP/S, DNS, SMB, and SSH beacon configuration with…
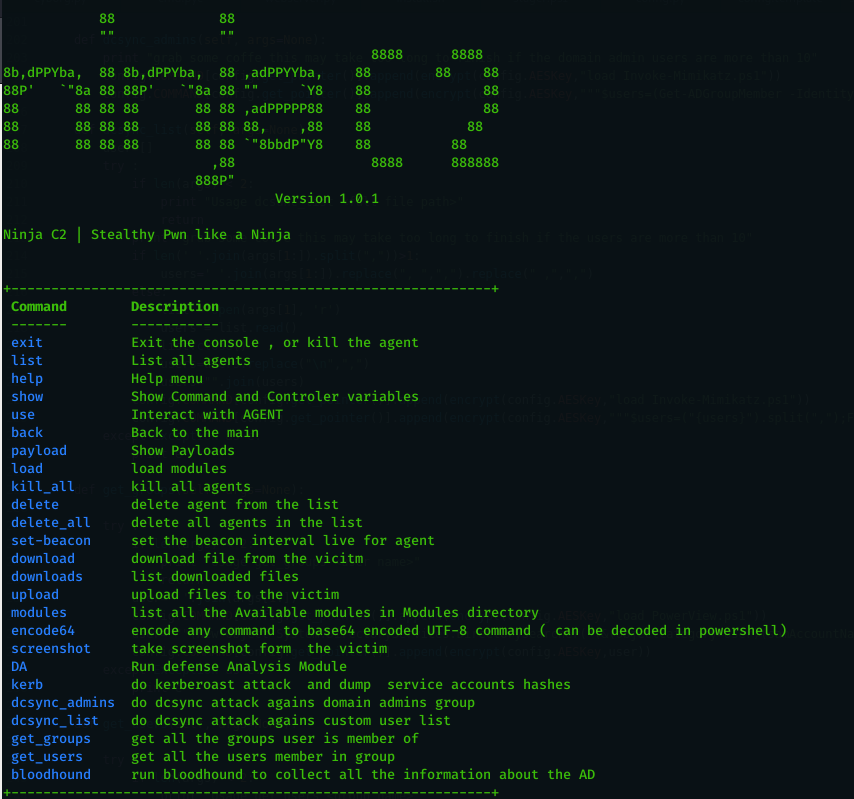 ahmedkhlief/ninja
Open source C2 server created for stealth red team operations
 gh05tcrew/metasploitmcp
MCP Server for Metasploit
 shellphish/ictf-framework
Open-source framework for hosting Attack/Defense CTF competitions with automated gamebot, script execution, VPN routing, and cloud-based…
 vulncheck-oss/go-exploit
Go-based exploit development framework with built-in phases for target verification, version scanning, exploitation, and C2. Supports multiple…
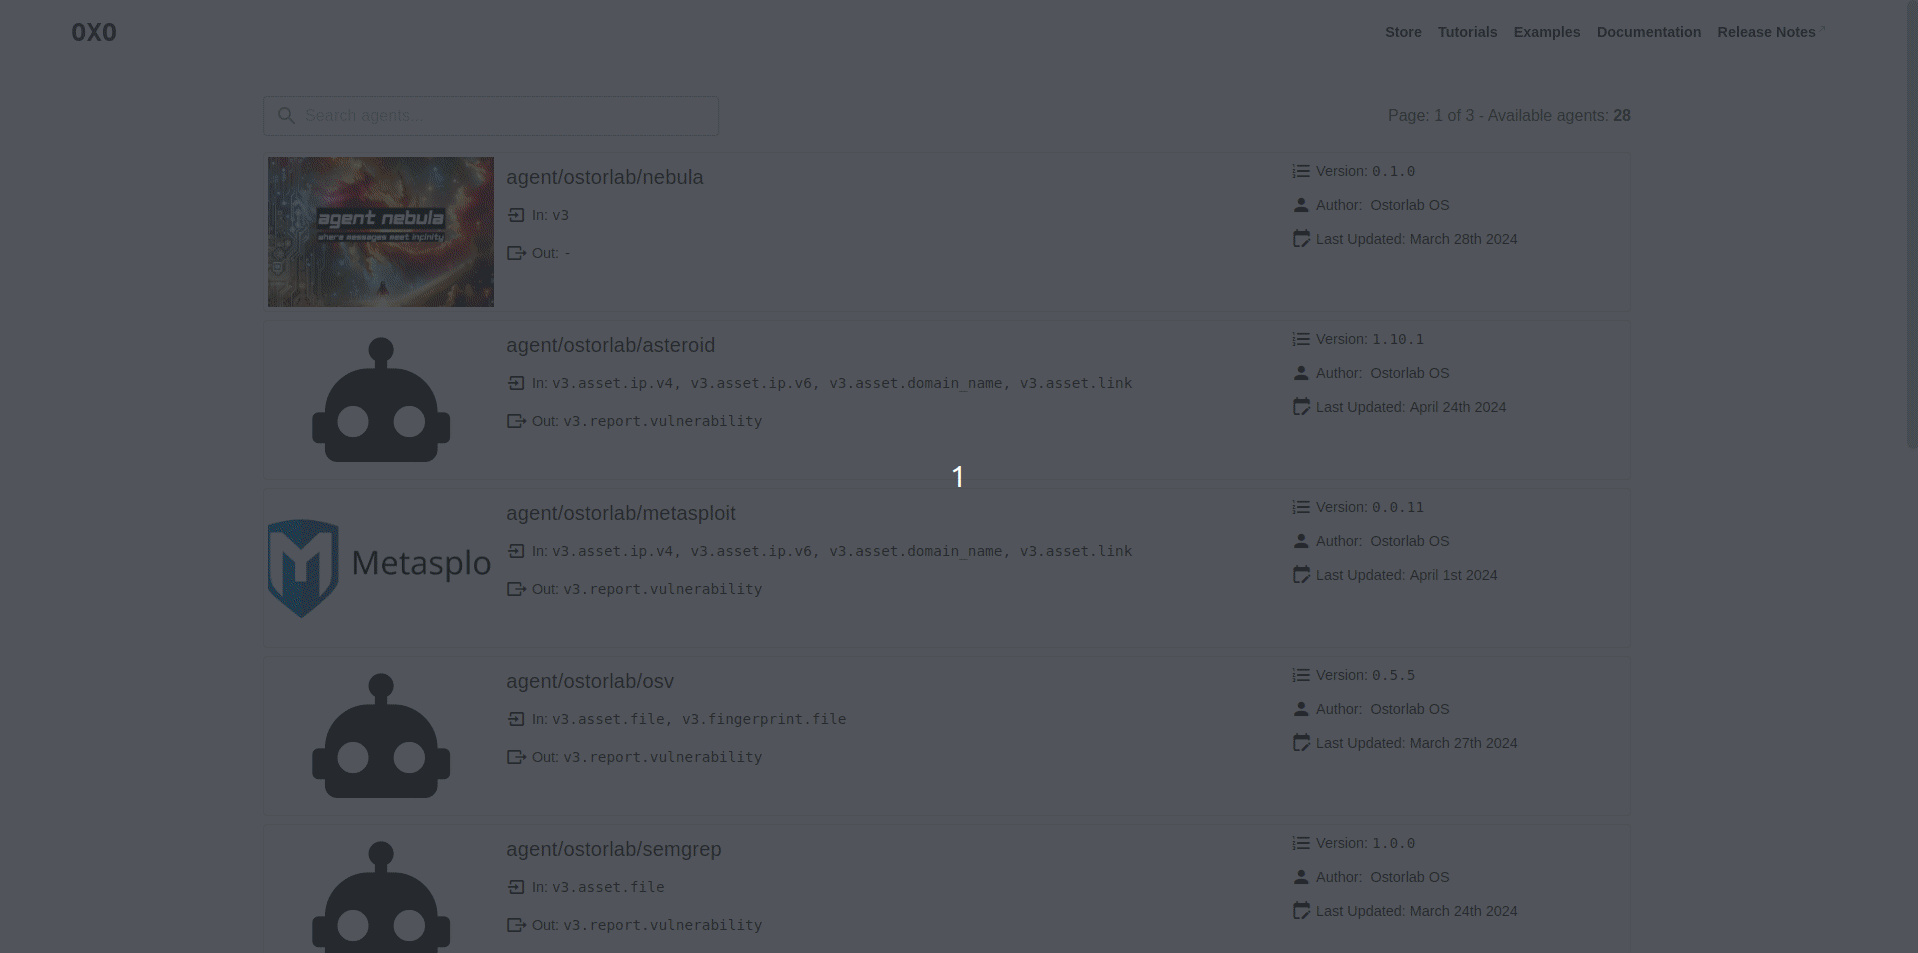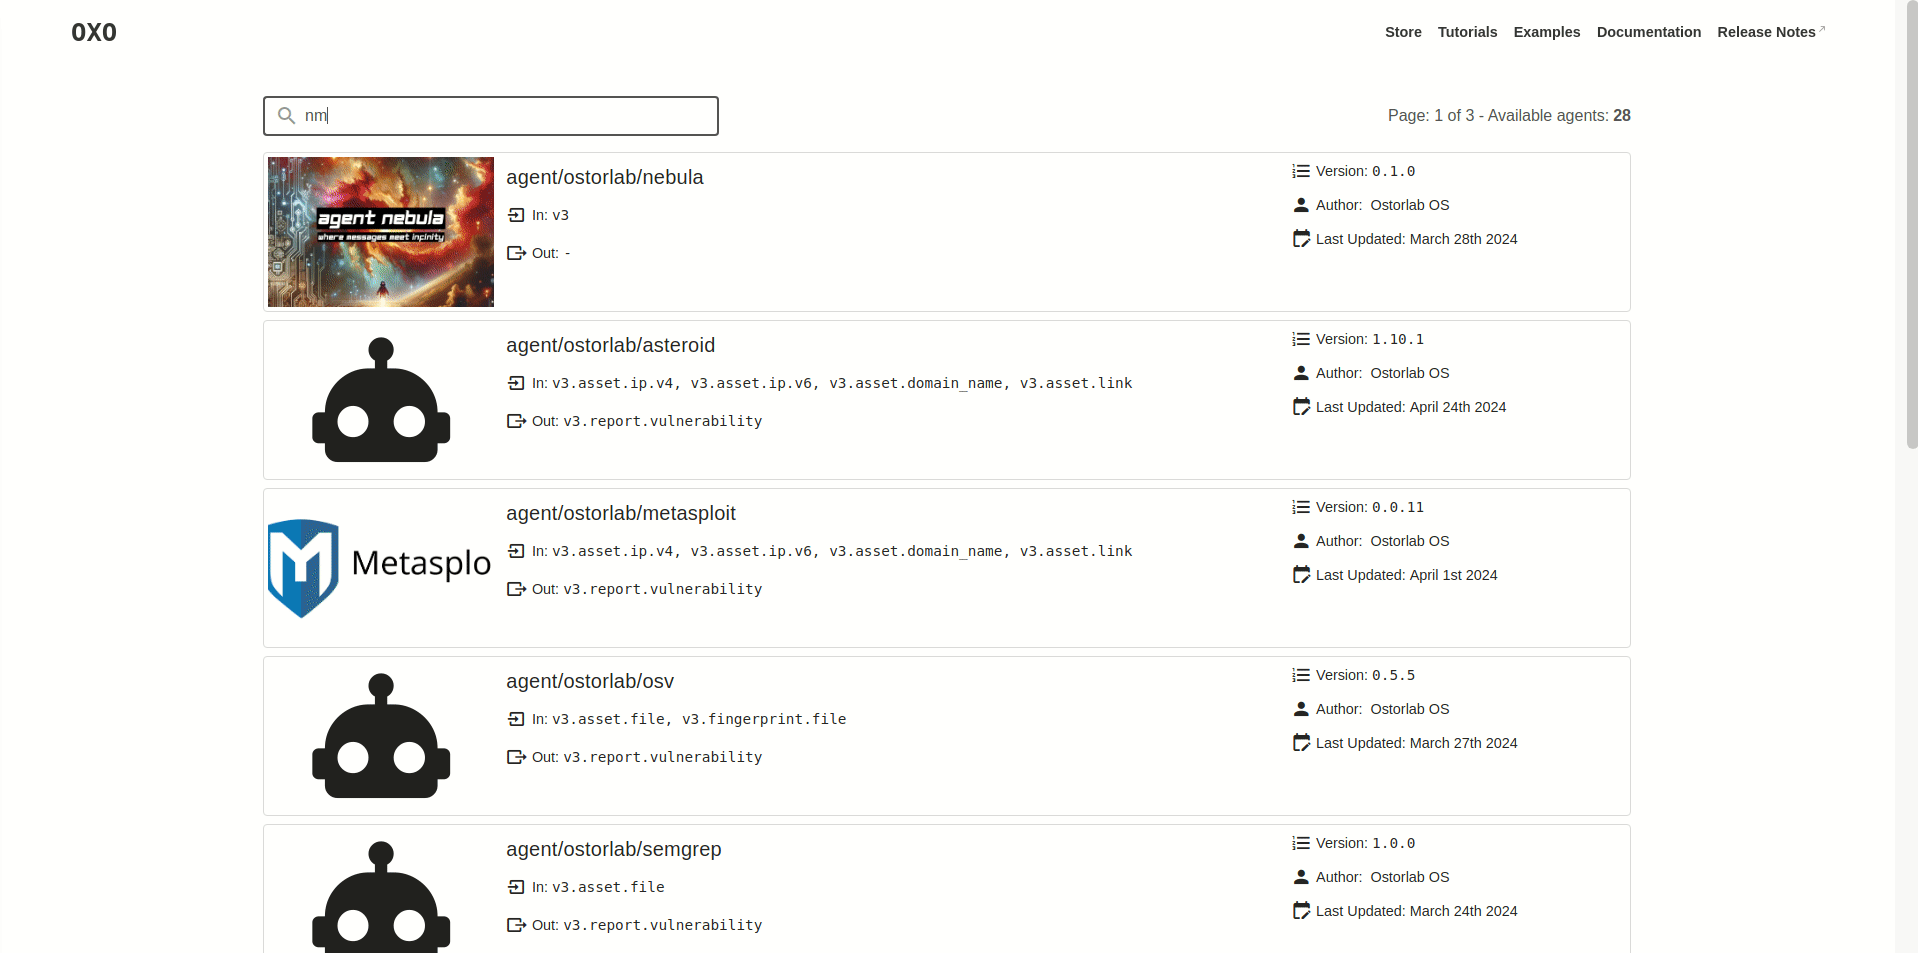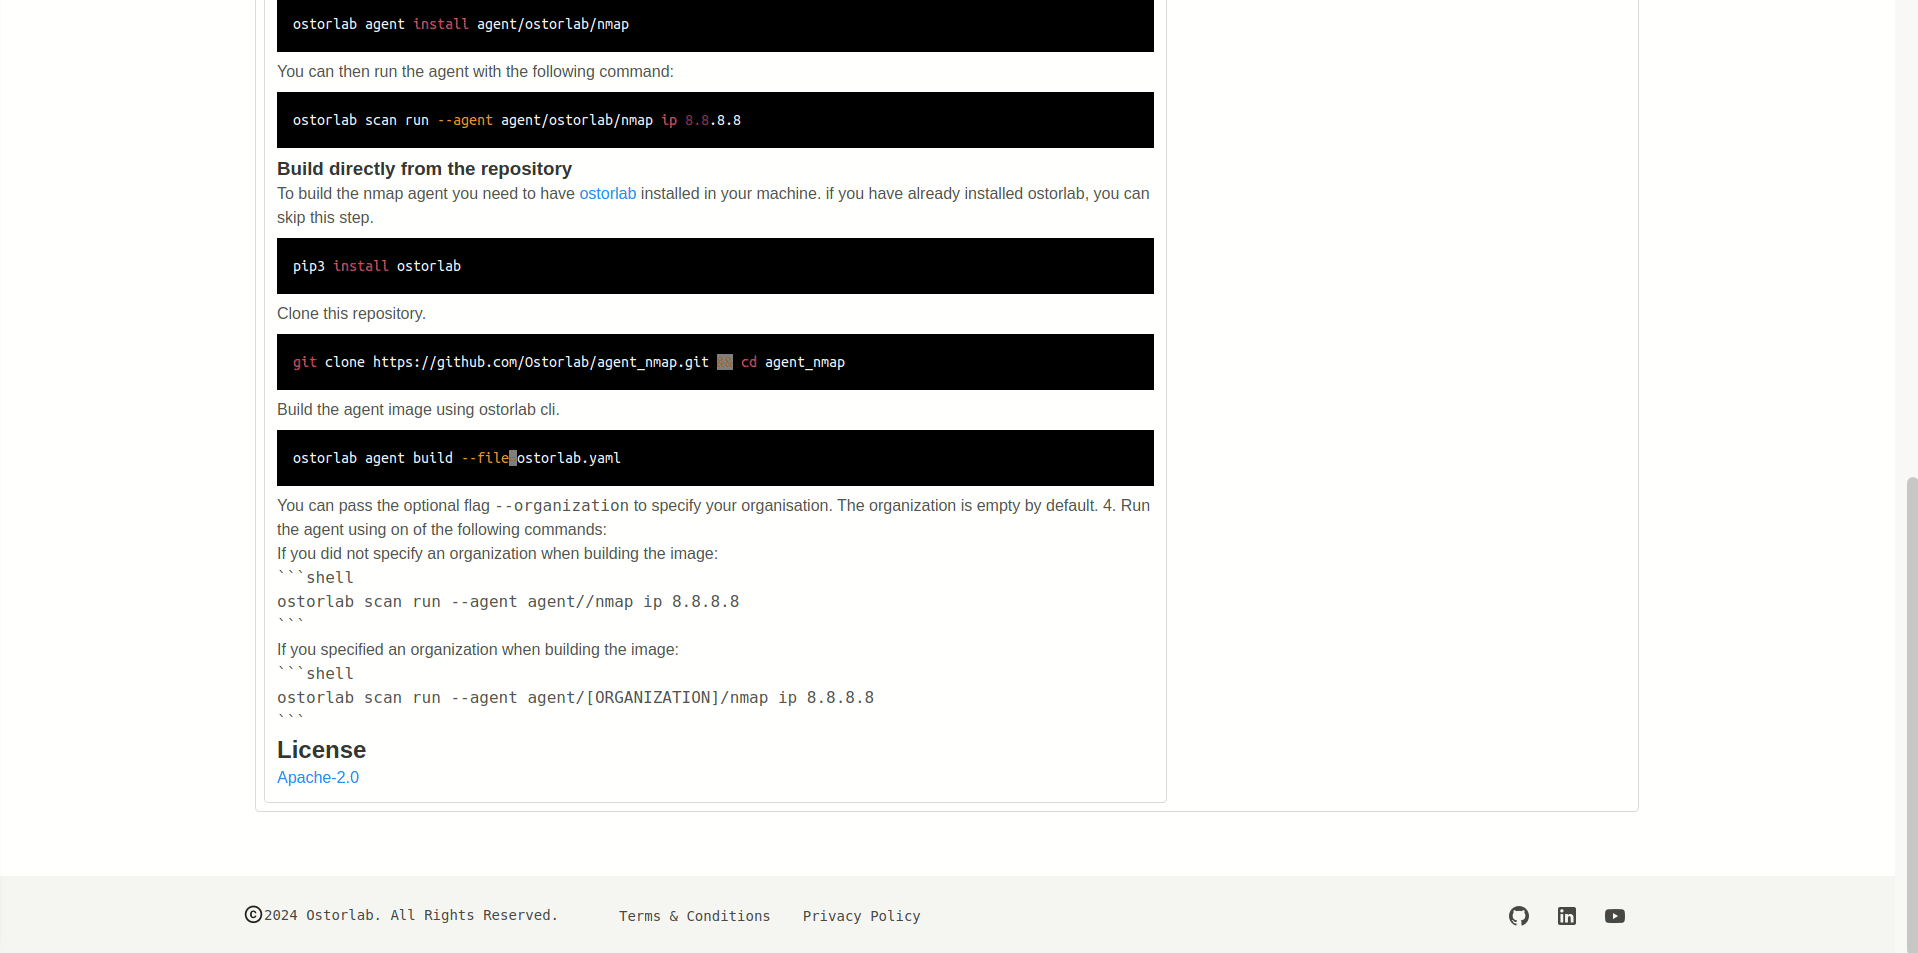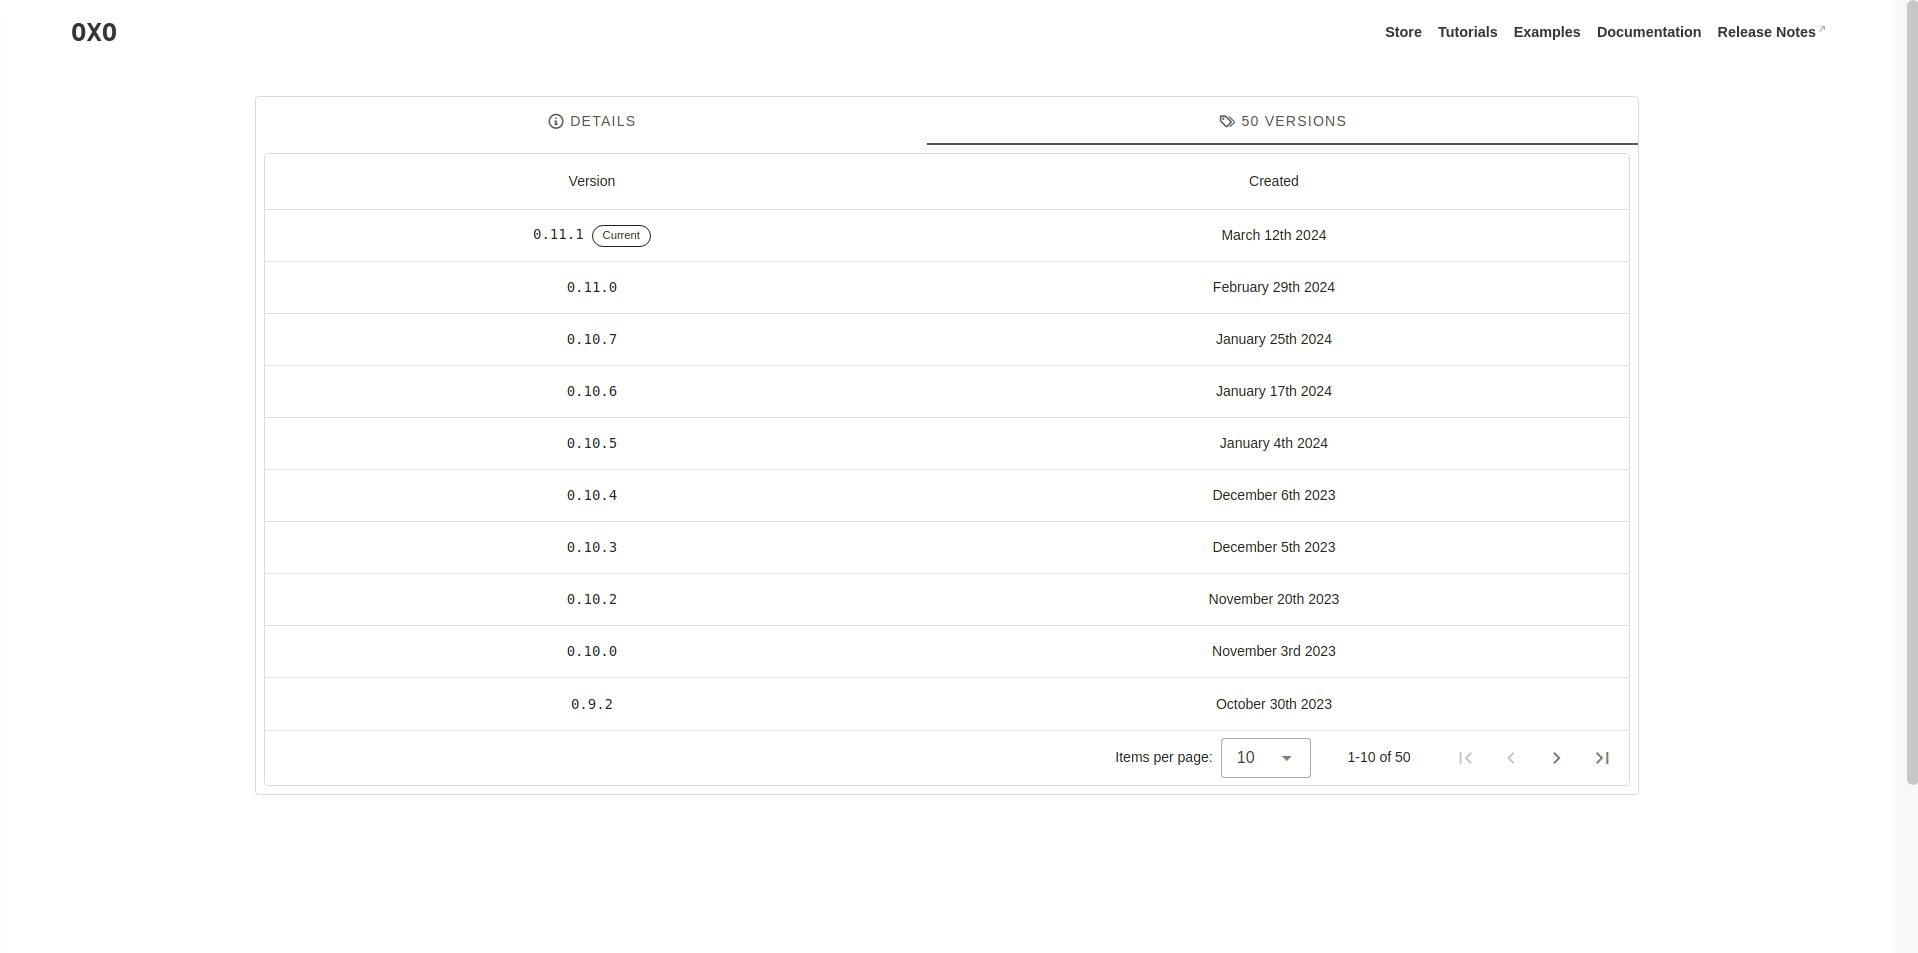 ostorlab/oxo
Modular security scanning orchestrator that combines specialized agents for vulnerability detection, reconnaissance, and fingerprinting across…
 cube0x0/sharpmapexec
Windows-native penetration testing swiss army knife for lateral movement, credential access, data exfiltration, and vulnerability scanning across…
 m4cs/babysploit
👶 BabySploit Beginner Pentesting Toolkit/Framework Written in Python 🐍
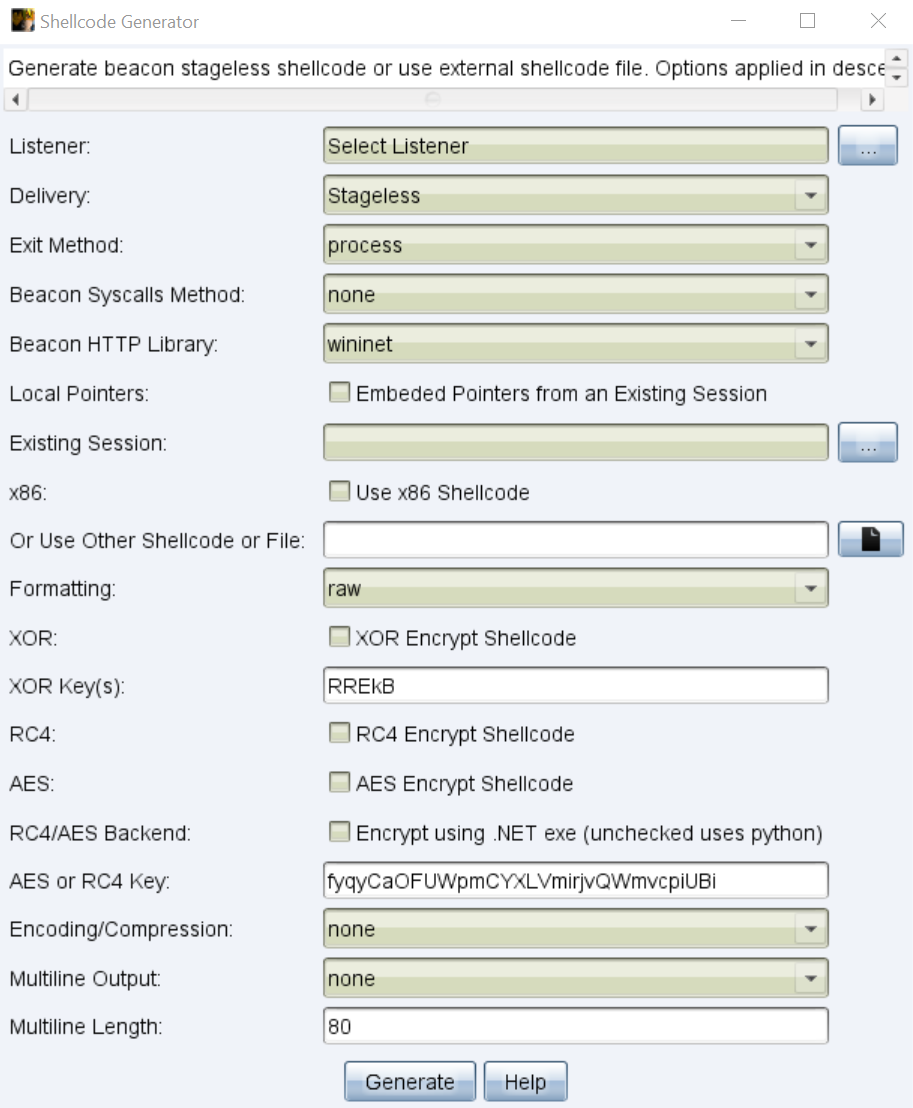 rcstep/cssg
Cobalt Strike aggressor script for generating, formatting, and encrypting beacon shellcode with support for multiple exit methods, syscalls, and…
 adshao/flounder
Autonomous white-hat security auditor for AI-driven code review, bug bounty research, exploit construction, and execution-grounded verification.