

Cusimanse
 opposum0112/cusimanse
Composable research-contract and YAML-recipe framework for agent-operated security experiments on disposable compute
ai-securitydefensive-toolsdynamic-analysis-sandboxing+9
opposum0112/cusimanseComposable research-contract and YAML-recipe framework for agent-operated security experiments on disposable compute
 mythicc2profiles/httpx
Configurable, Community driven, HTTP C2 Profile
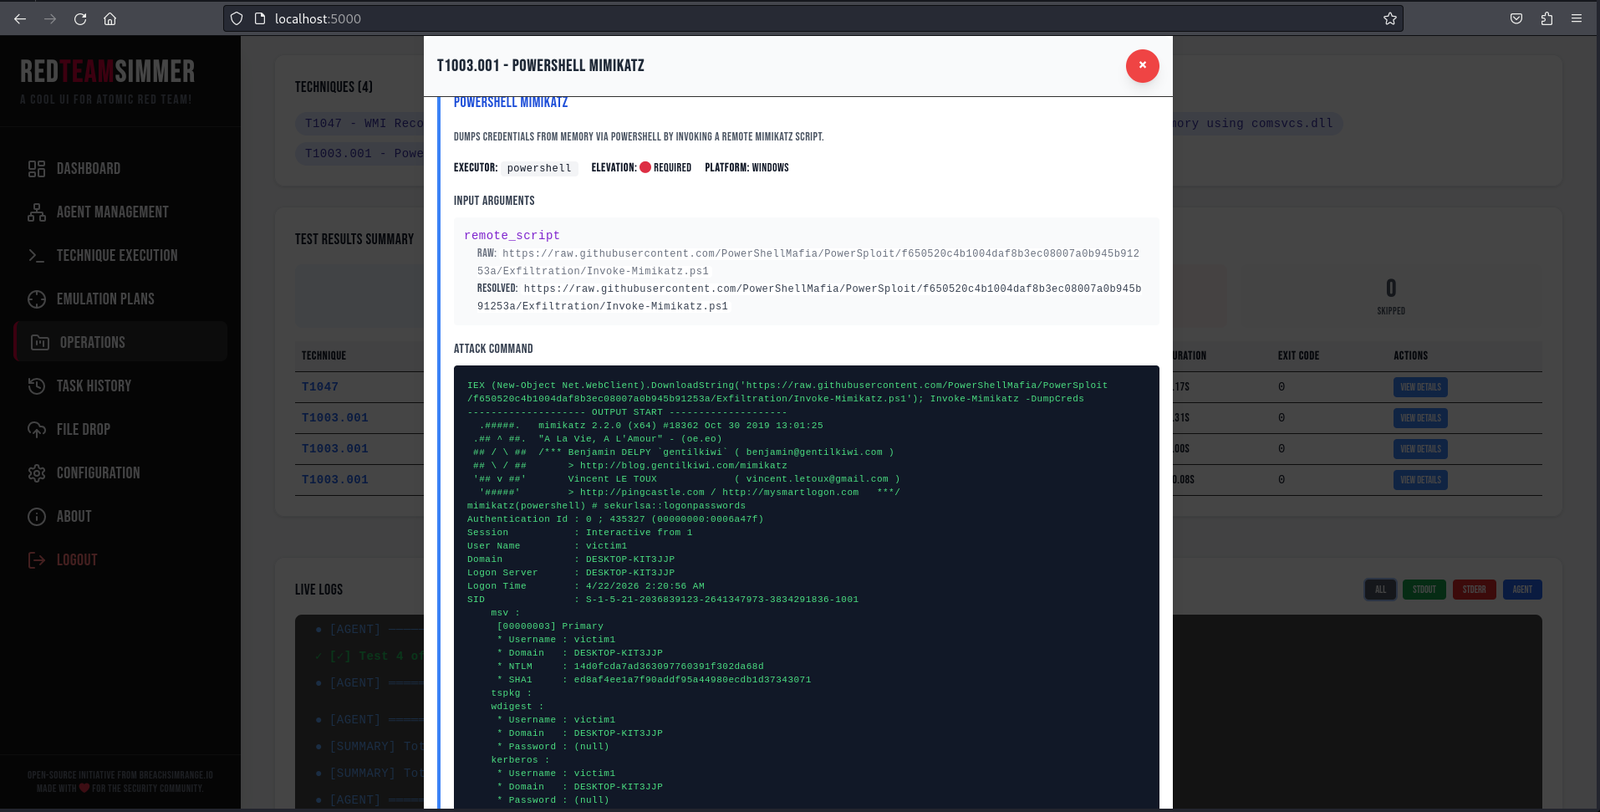 breachsimrange/redteamsimmer
Web-based adversary emulation platform that orchestrates Atomic Red Team tests across Windows endpoints via Go agents, with MITRE ATT&CK mapping, APT…
 top-celestial-company-ltd/dros-vep-lite
Open-source, 100% reproducible AI Agent Runtime Security Benchmark & Sandbox Environment (RFC-010 Draft Protocol).
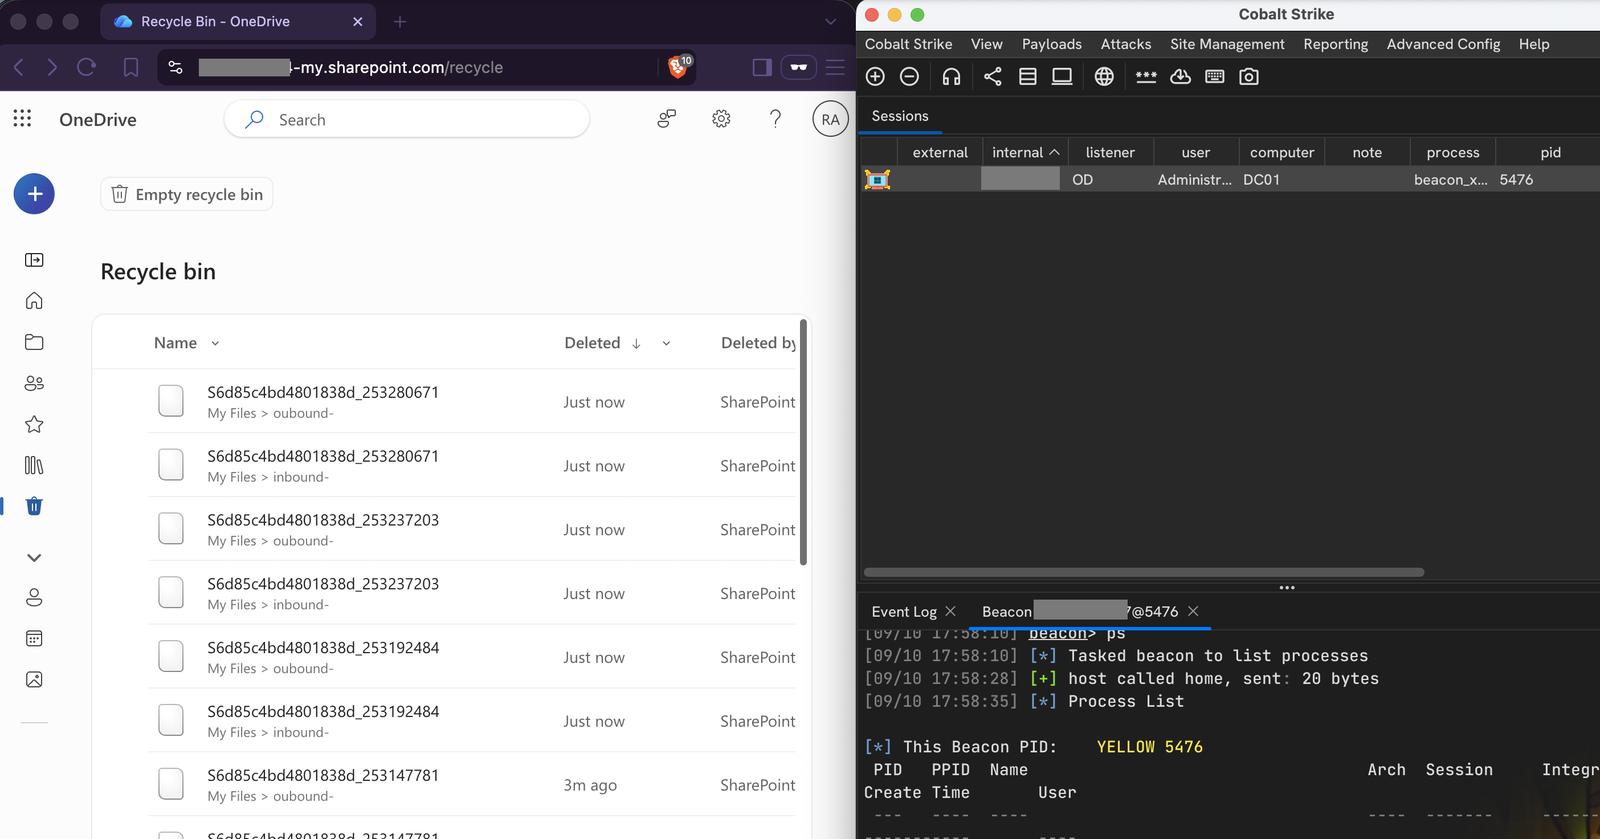 nmht3t/onedrive-udc2
OneDrive as a covert C2 transport for Cobalt Strike
 whispergate/msteams
Mythic C2 profile that tunnels agent traffic through Microsoft Teams channels using the Microsoft Graph API, with AES256 encryption, jitter, kill…
 mafifrizi/ares
Autonomous red-team engagement platform with MITRE ATT&CK module orchestration, DAG attack-path solving, OPSEC controls, encrypted credential vault,…
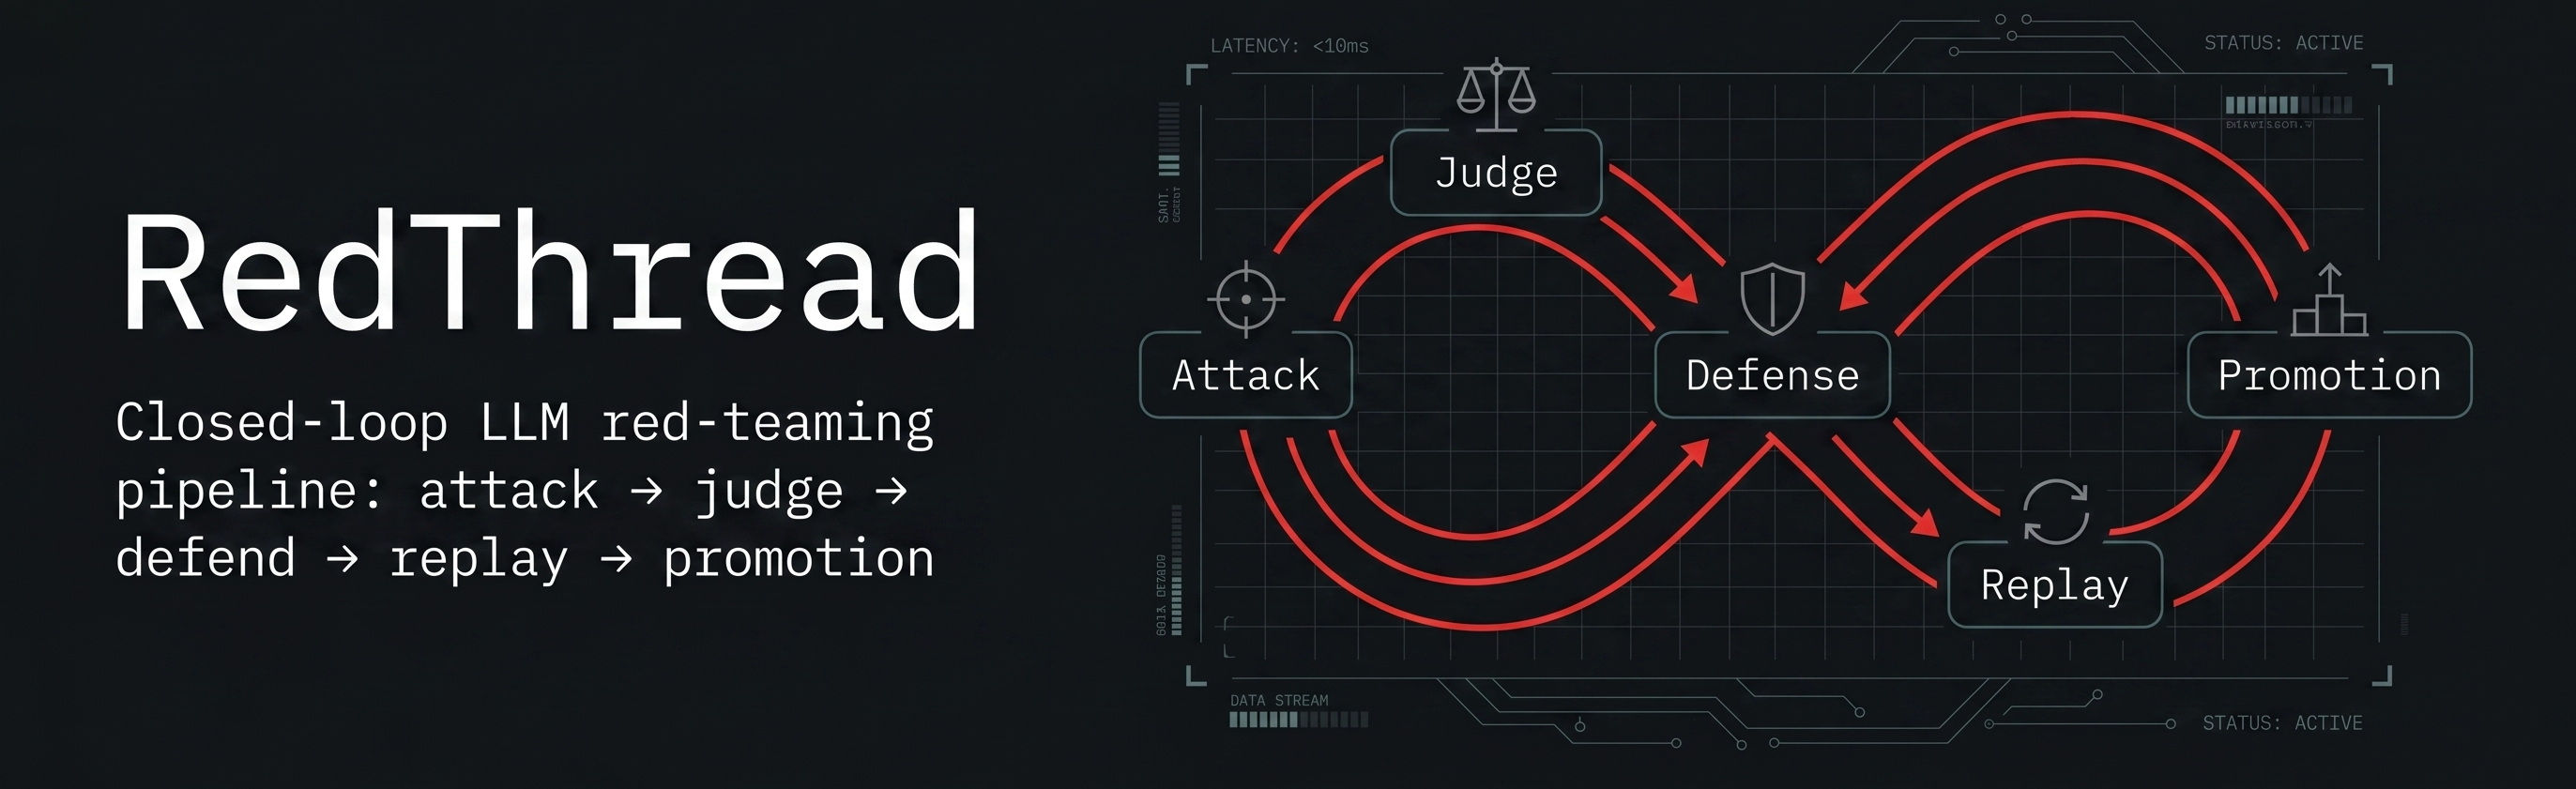 matheusht/redthread
An autonomous red-teaming engine for LLMs. RedThread manages the full security lifecycle: generating adversarial attacks, executing precision…
 galoryber/fawkes
Fawkes is a golang Mythic C2 Agent exclusively written by AI.
 crussella0129/tricorne
a Fedora remix focused on pentesting and purple hat tooling
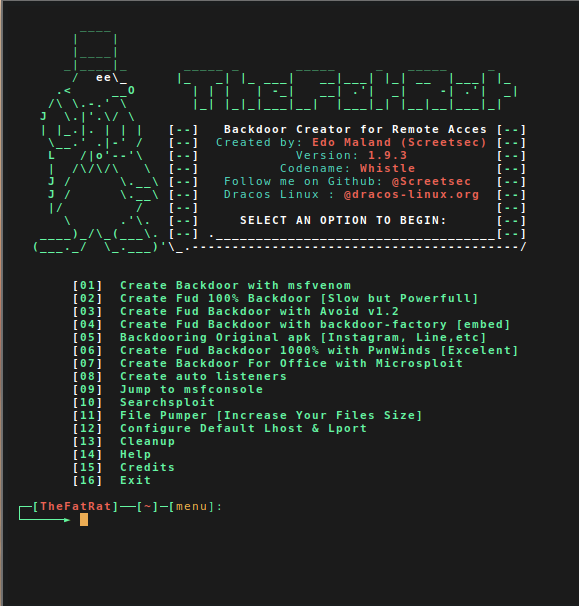 screetsec/thefatrat
Thefatrat a massive exploiting tool : Easy tool to generate backdoor and easy tool to post exploitation attack like browser attack and etc . This…
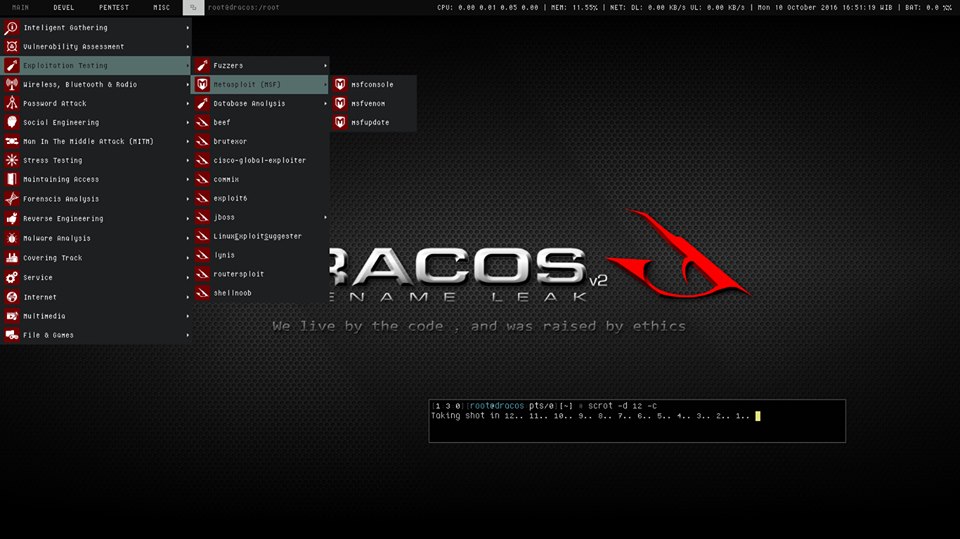 screetsec/dracos
Dracos Linux ( www.dracos-linux.org ) is the Linux operating system from Indonesian
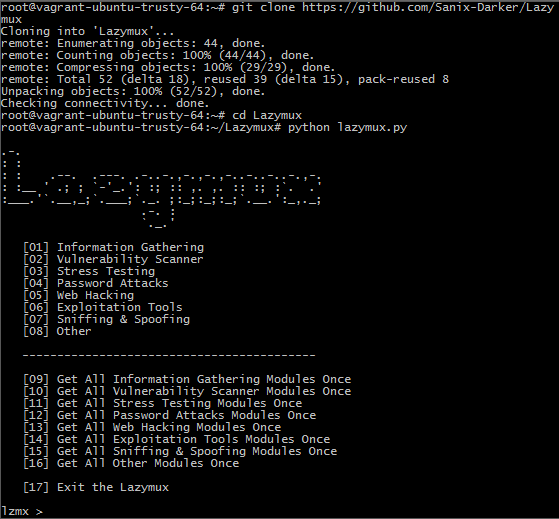 sanix-darker/lazymux
Lazymux is a huge list of Many Hacking tools and PEN-TESTING tools! NOTE: Am not Responsible of bad use of this project.
 s0lst1c3/dropengine
DropEngine provides a malleable framework for creating shellcode runners, allowing operators to choose from a selection of components and combine…