

redStack
 devzero-security/redstack
Terraform-deployed red team operator lab on AWS: Mythic, Sliver, and Adaptix C2 behind a production-style Apache redirector, with Kali/Windows hosts…
cloud-infrastructure-securitycommand-and-controleducation+8
286
devzero-security/redstackTerraform-deployed red team operator lab on AWS: Mythic, Sliver, and Adaptix C2 behind a production-style Apache redirector, with Kali/Windows hosts…
 opposum0112/cusimanse
Composable research-contract and YAML-recipe framework for agent-operated security experiments on disposable compute

 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
 mrhenrike/embedxpl-forge
Embedded Device Security Assessment Framework — 700 modules, 350 CVEs, 55 vendors, APT Group Engine. Covers routers, IP cameras, GPON ONTs, ISP CPEs,…
 kalilinux/nethunter/build-scripts/kali-nethunter-installer
Builds flashable installer ZIPs that deploy a mobile penetration-testing environment on Android, including kernel boot patching, rootfs integration,…
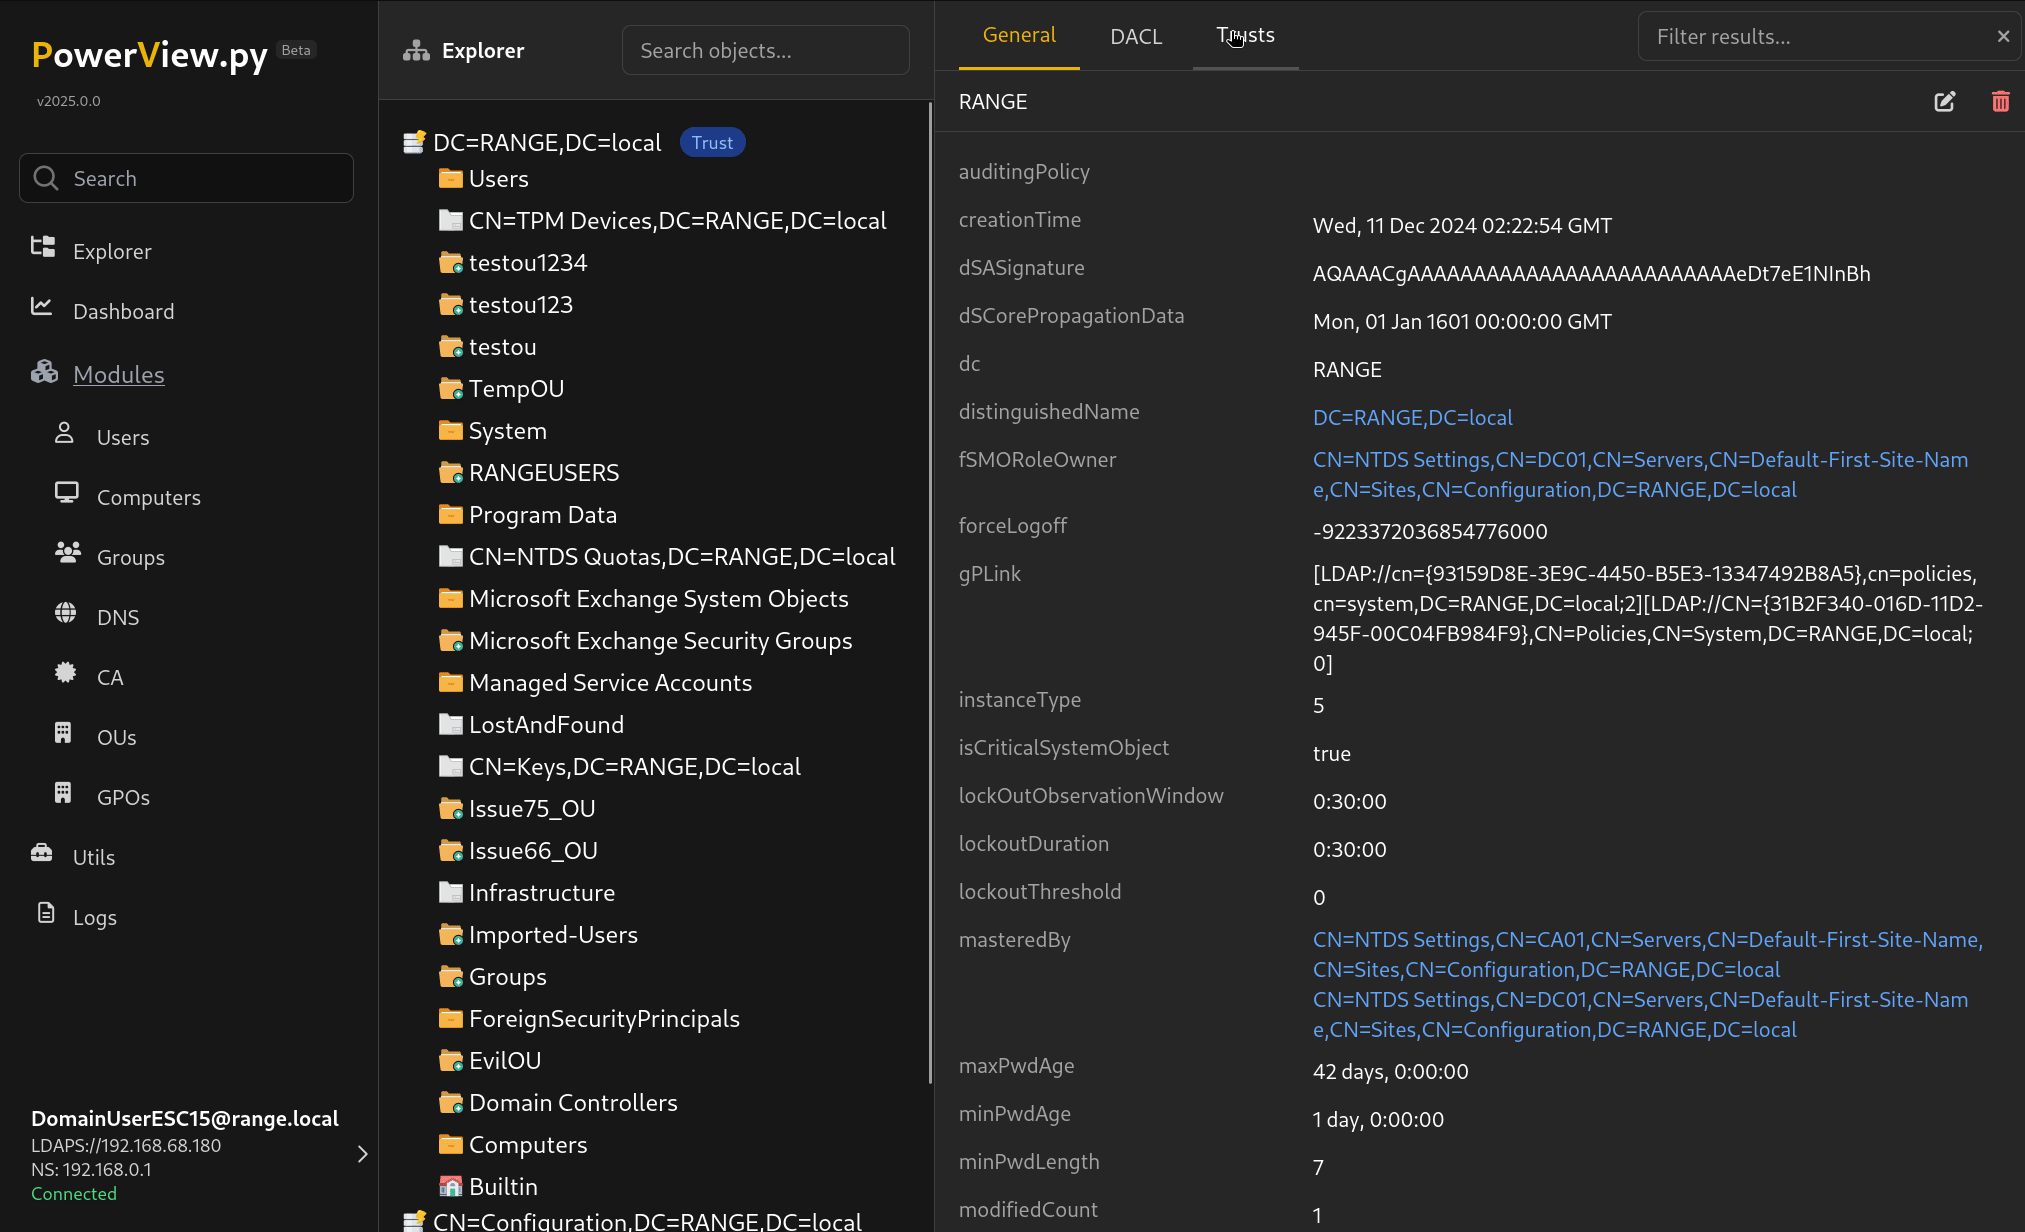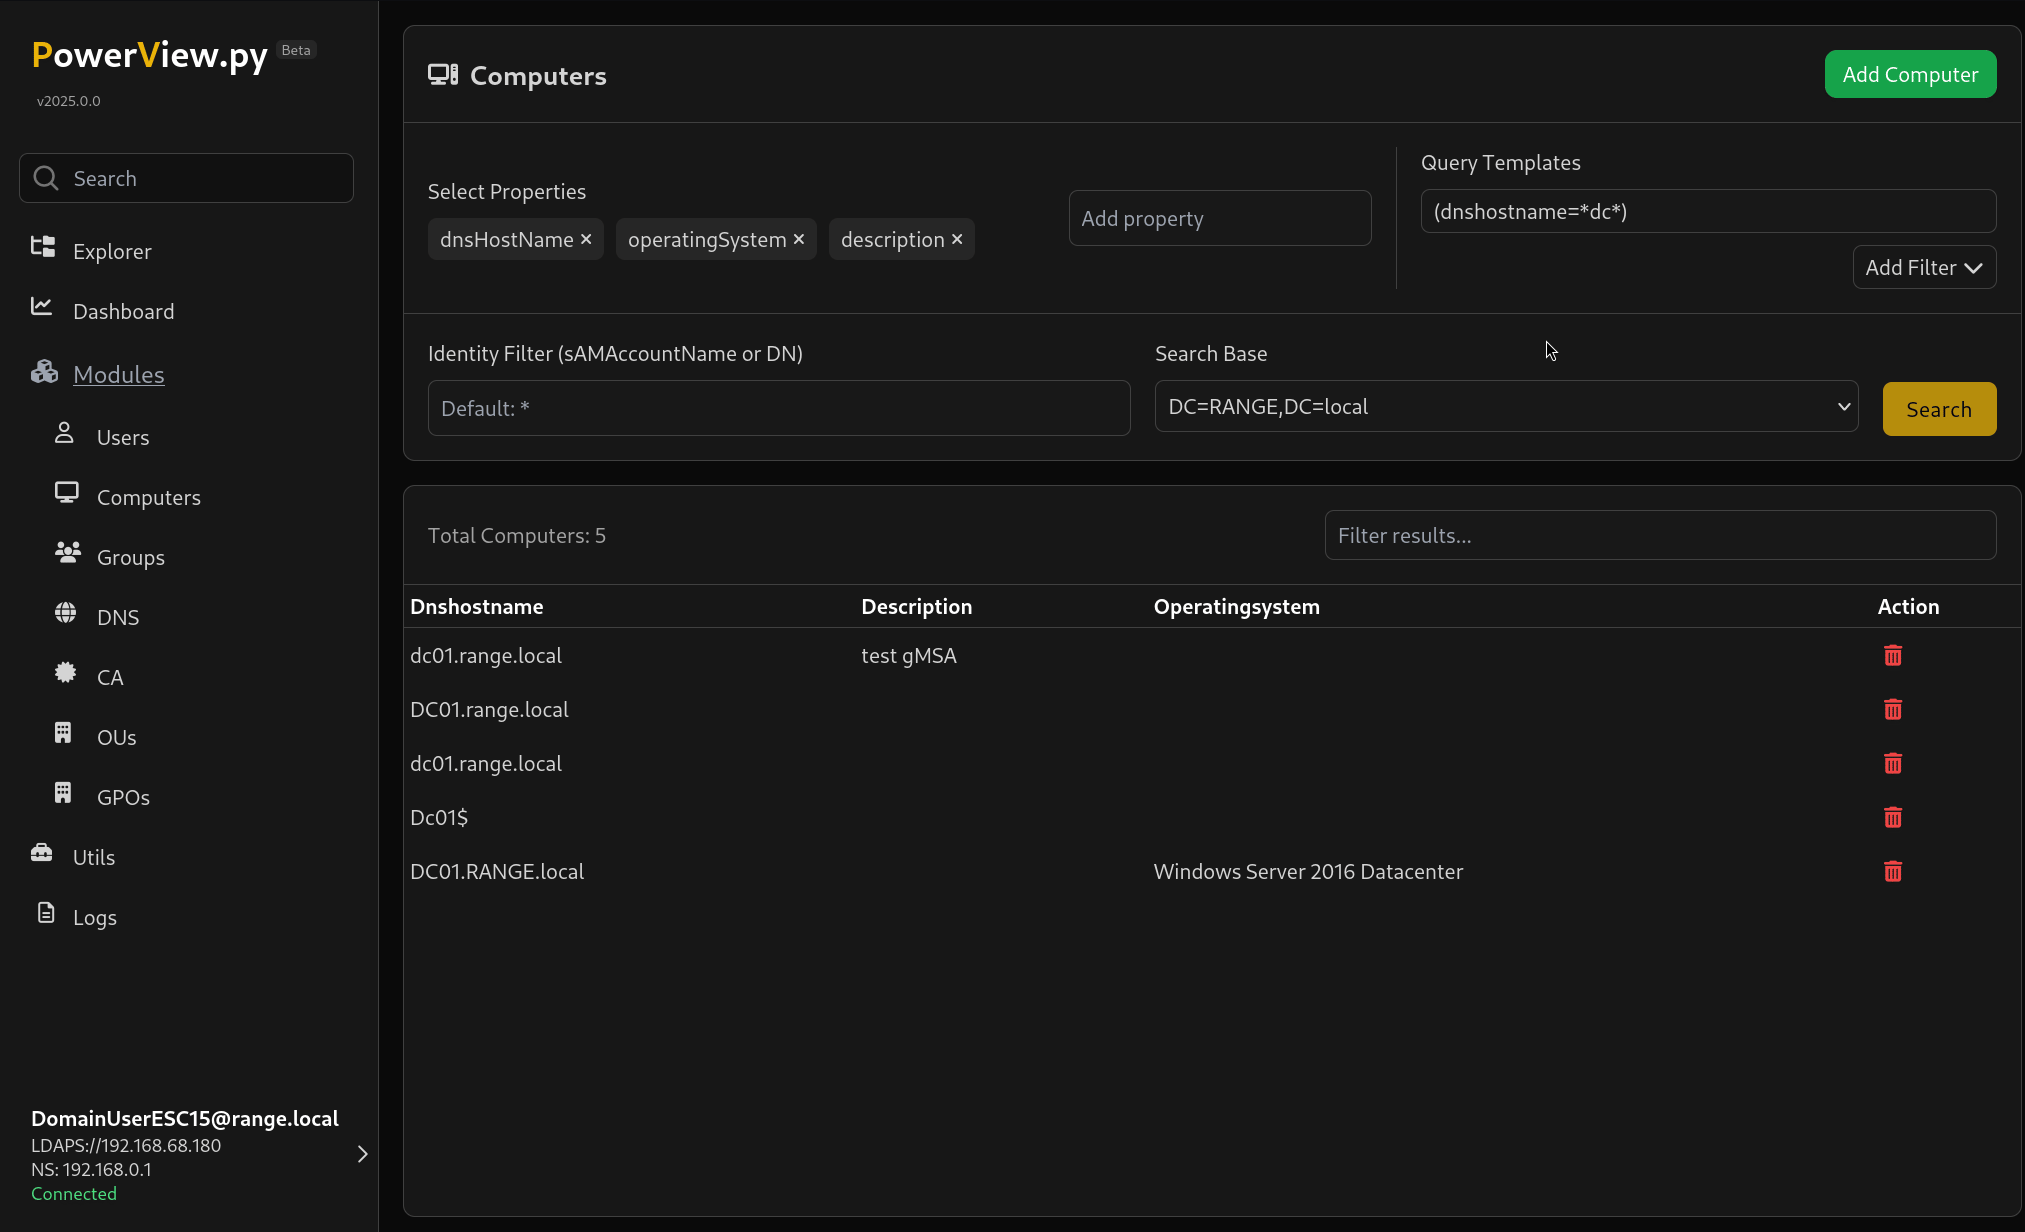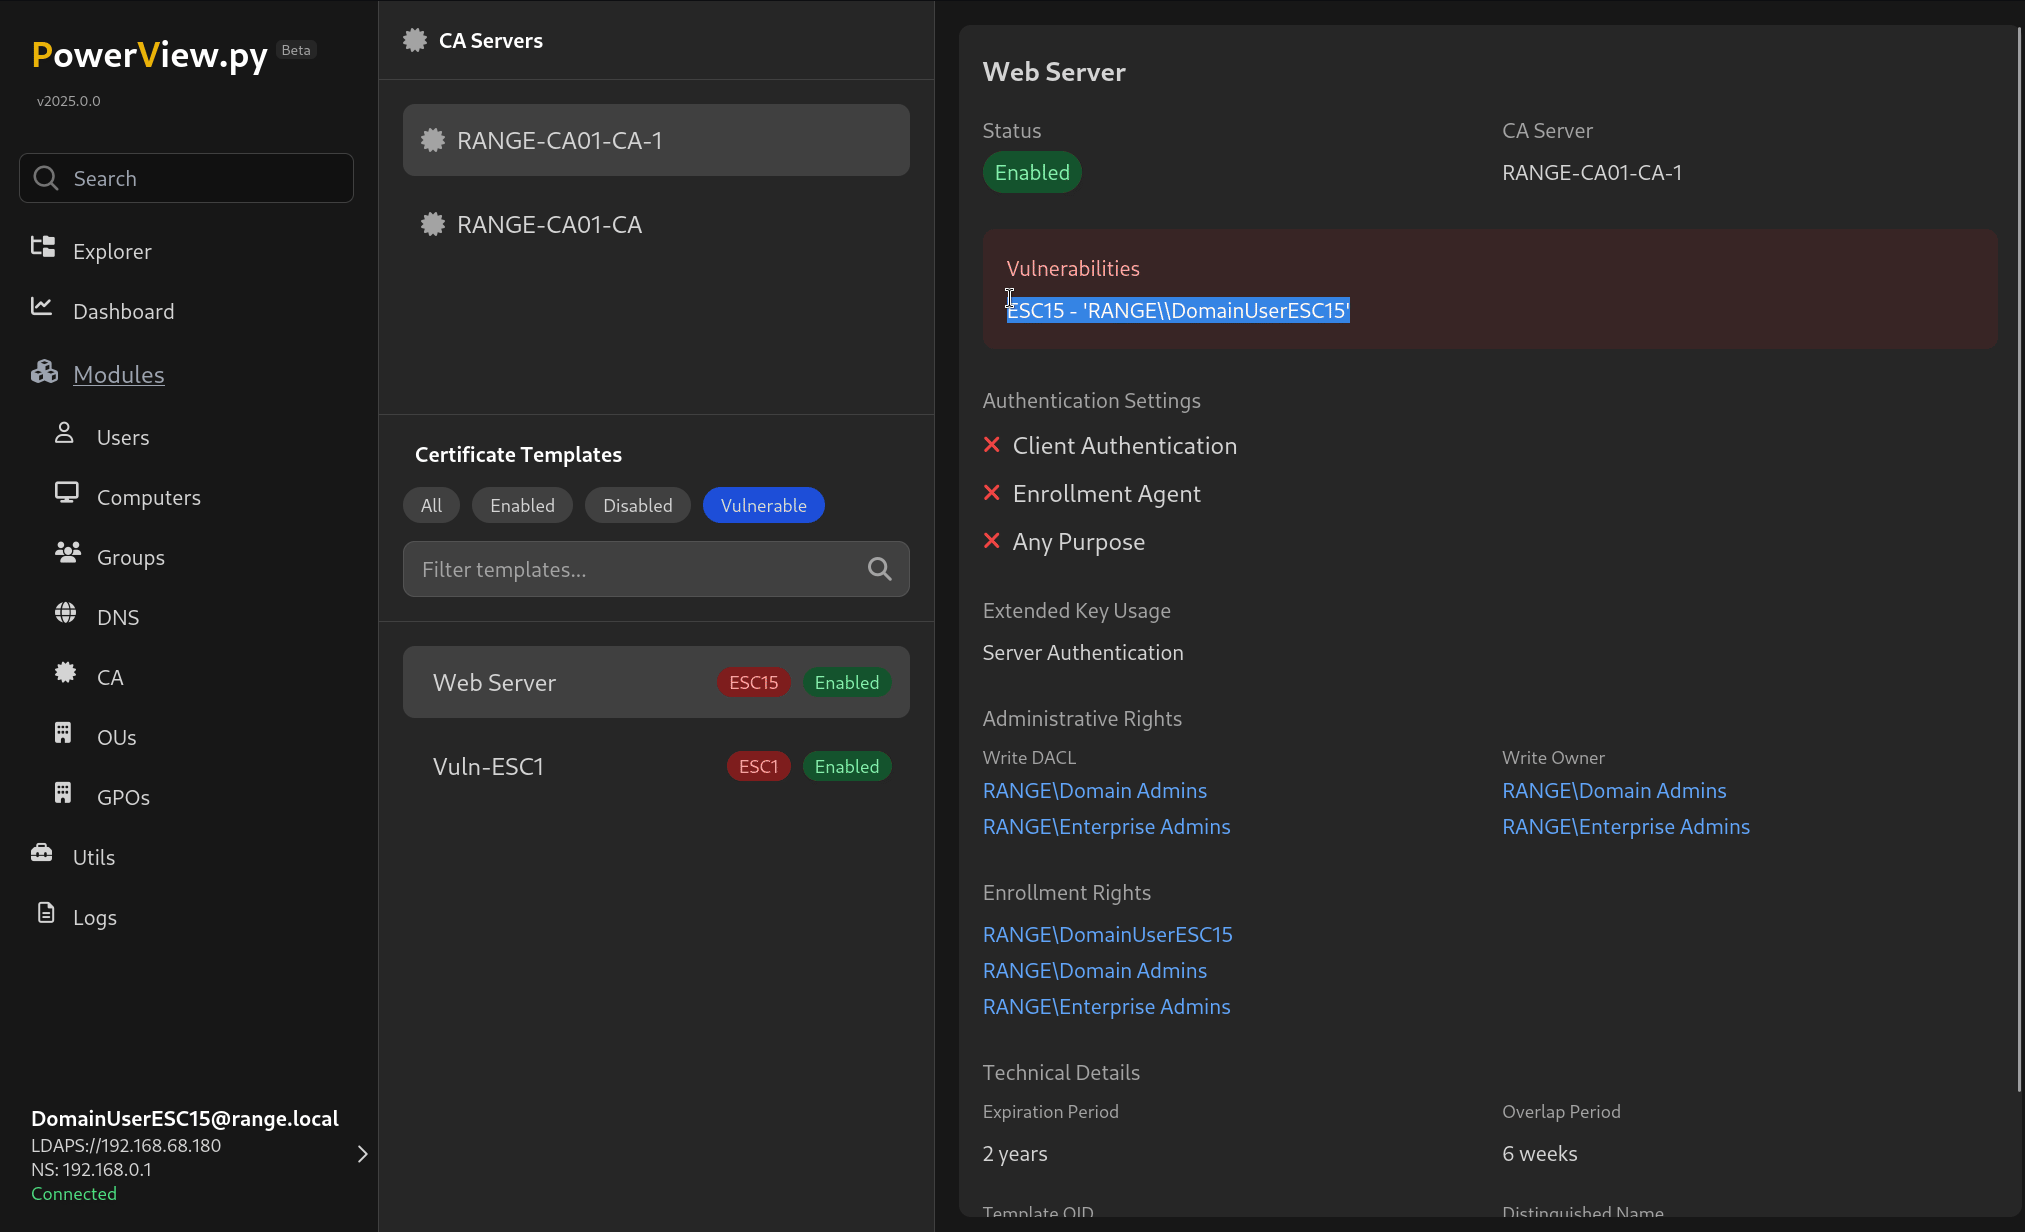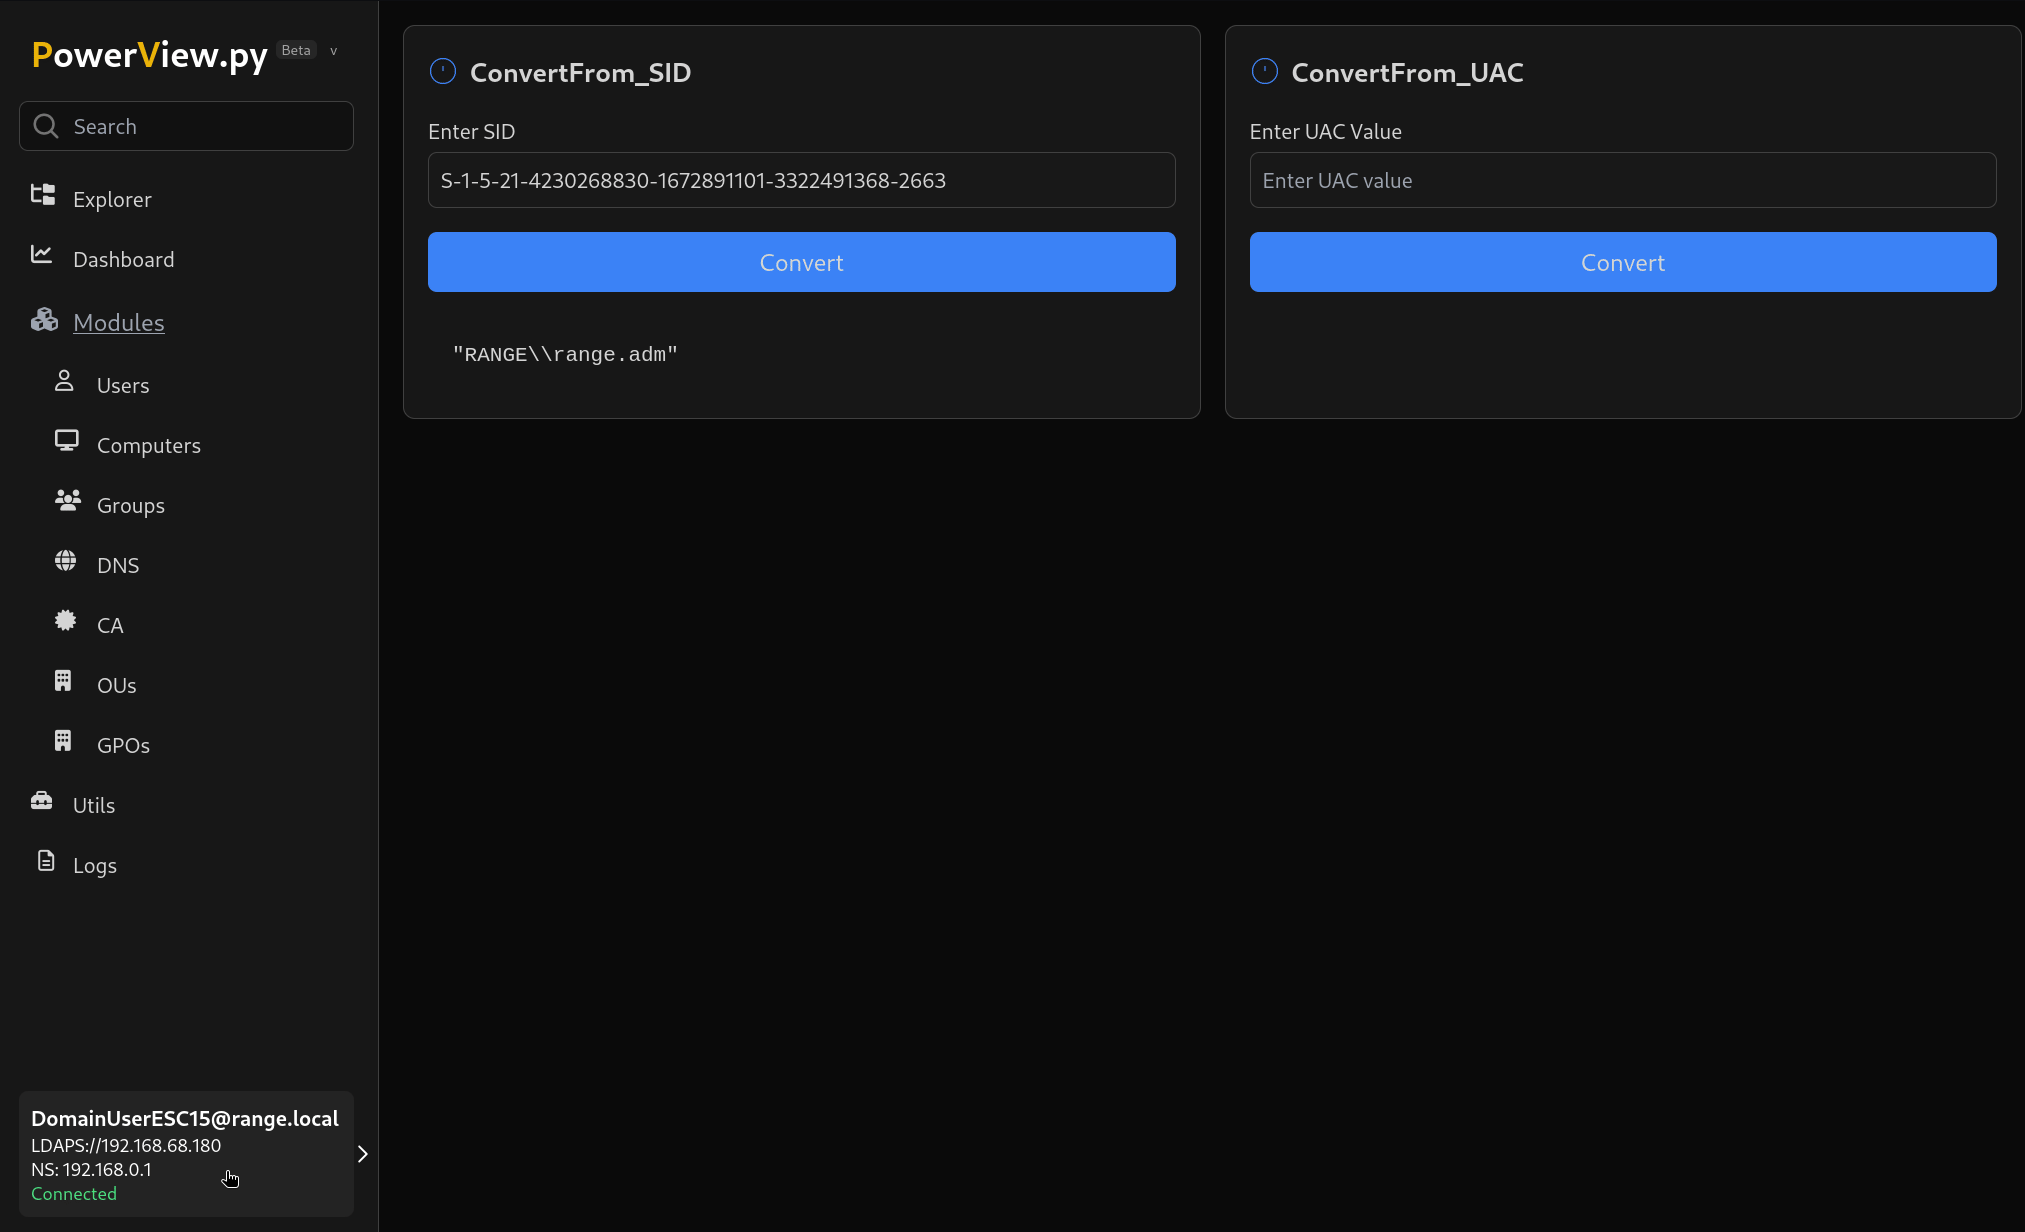 aniqfakhrul/powerview.py
Powerview on steroids
 trustedsec/specula
Modular command-and-control framework abusing Microsoft Outlook's Home Page feature for stealthy persistence, remote access, and post-exploitation.
 trustedsec/tap
The TrustedSec Attack Platform is a reliable method for droppers on an infrastructure in order to ensure established connections to an organization.
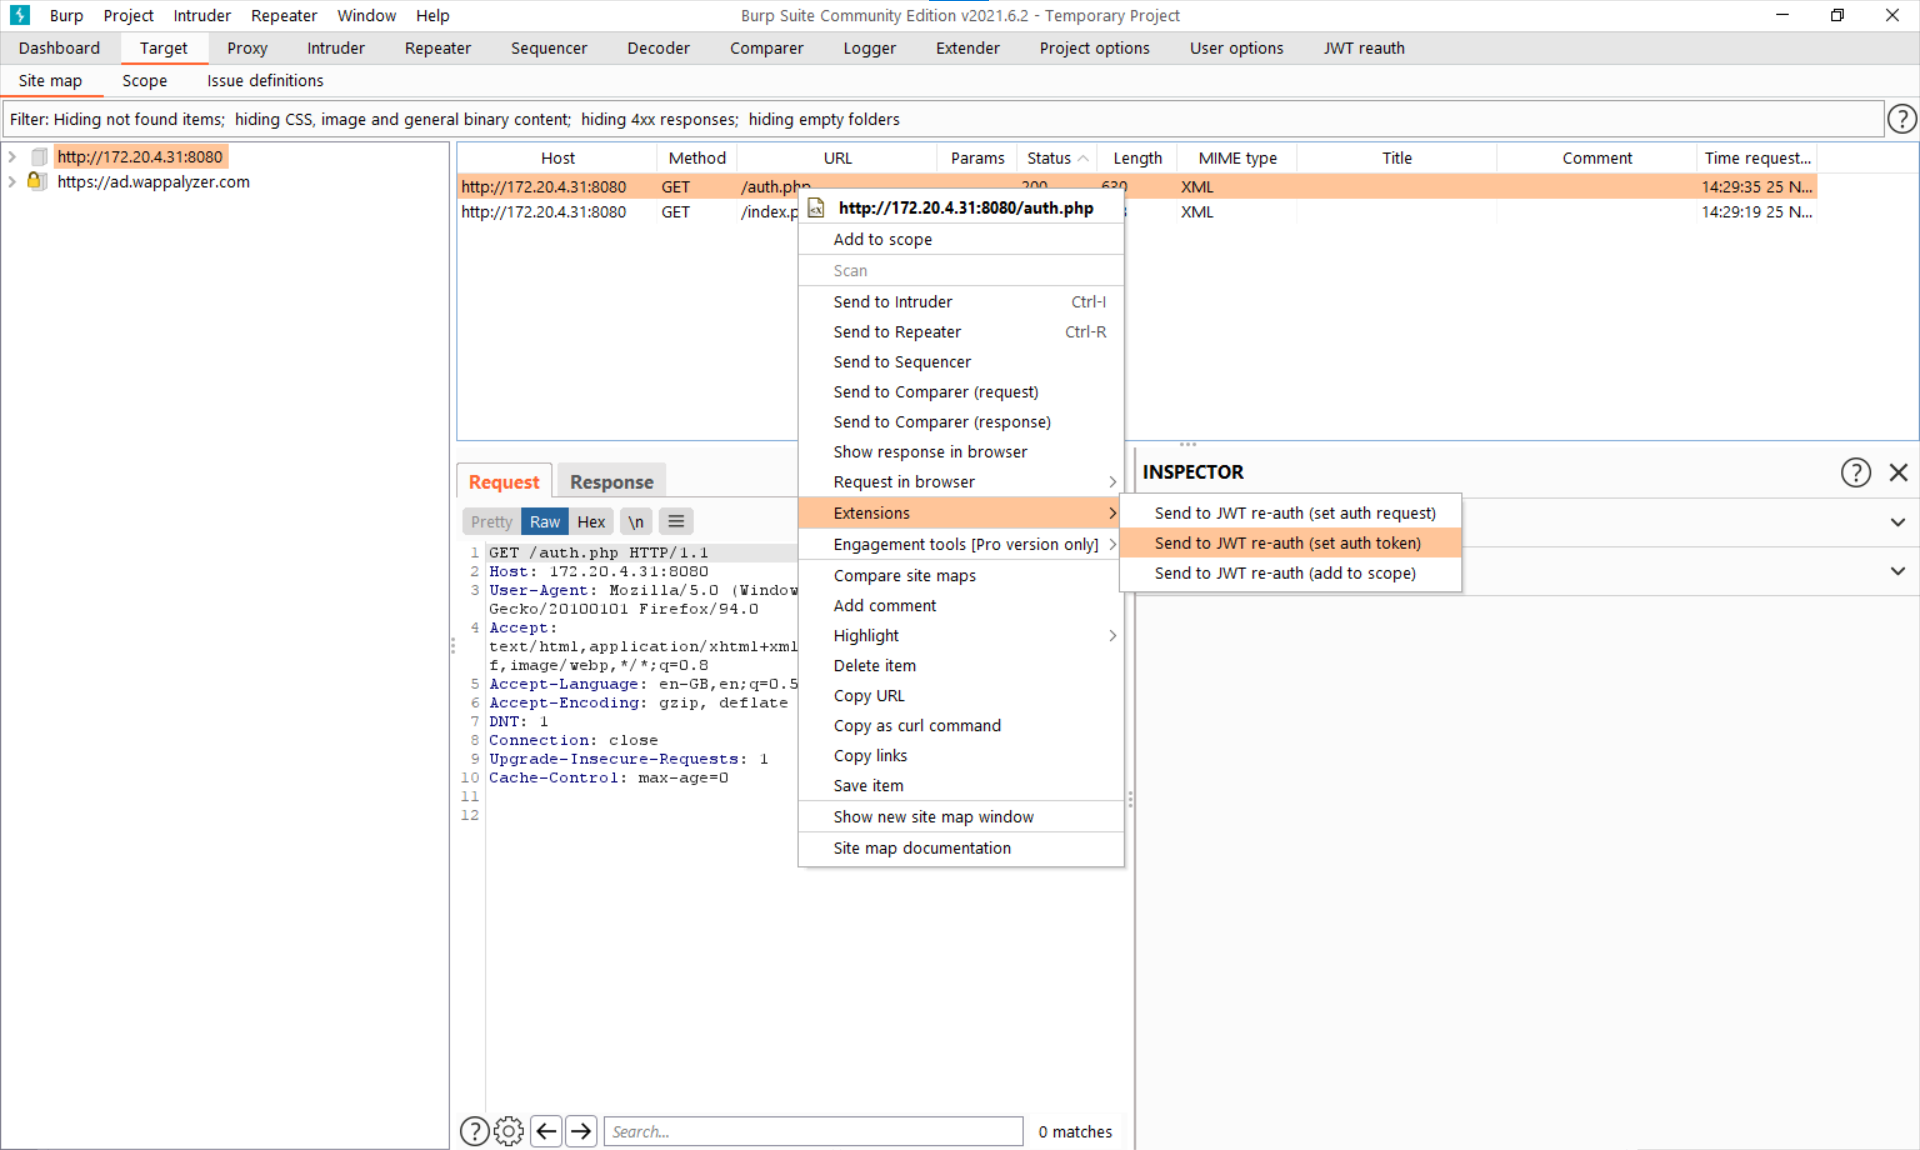 nccgroup/jwt-reauth
Caches JWT authentication tokens from an auth URL and attaches them as headers to in-scope requests in Burp Suite for automated session handling.
 jas502n/msfconsole-termux
How To Install Metasploit-Table on the Android Termux
 agampreet-singh/redroot
RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…
 mythicagents/medusa
Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…
 blacksnufkin/pwnbox-kali
Bash Script to automate the process of setting up a new Kali Linux virtual machine to look a like HTB PwnBox
 zcutlip/bowcaster
Python-based exploit development framework with payloads, encoders, and connect-back servers, focused on MIPS CPU architecture but designed for…
 qax-a-team/cobaltstrike-toolset
Aggressor Script, Kits, Malleable C2 Profiles, External C2 and so on
 und3rf10w/external_c2_framework
Python api for usage with cobalt strike's External C2 specification
 yaldobaoth/cve-2015-1578-poc-metasploit
This is a proof-of-concept Metasploit module exploit for CVE-2015-1578, a buffer overflow vulnerability in Achat 0.150 beta7 on Windows. Exploitation…
 nate0634034090/nate158g-m-w-n-l-p-d-a-o-e
### This module requires Metasploit: https://metasploit.com/download# Current source: https://github.com/rapid7/metasploit-framework##class…