

qiling
 qilingframework/qiling
A True Instrumentable Binary Emulation Framework
binary-analysisdebuggersdynamic-analysis-sandboxing+7
qilingframework/qilingA True Instrumentable Binary Emulation Framework
 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 gushmazuko/metasploit_in_termux
Install and run Metasploit Framework 6 on Android via Termux with automated setup, payload generation (msfvenom), and full msfconsole access for…
 gallopsled/pwntools
CTF framework and exploit development library
 n1nj4sec/pupy
Pupy is an opensource, cross-platform (Windows, Linux, OSX, Android) C2 and post-exploitation framework written in python and C
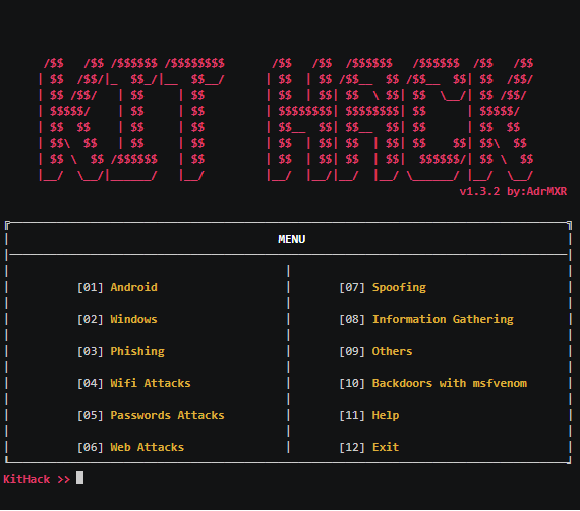 adrmxr/kithack
Hacking tools pack & backdoors generator.
 mgeeky/protectmytooling
Multi-Packer wrapper letting us daisy-chain various packers, obfuscators and other Red Team oriented weaponry. Featured with artifacts watermarking,…
 risksense-ops/cve-2016-6366
Public repository for improvements to the EXTRABACON exploit
 openrce/paimei
A reverse engineering framework written in Python.
 boku7/bokuloader
A proof-of-concept Cobalt Strike Reflective Loader which aims to recreate, integrate, and enhance Cobalt Strike's evasion features!
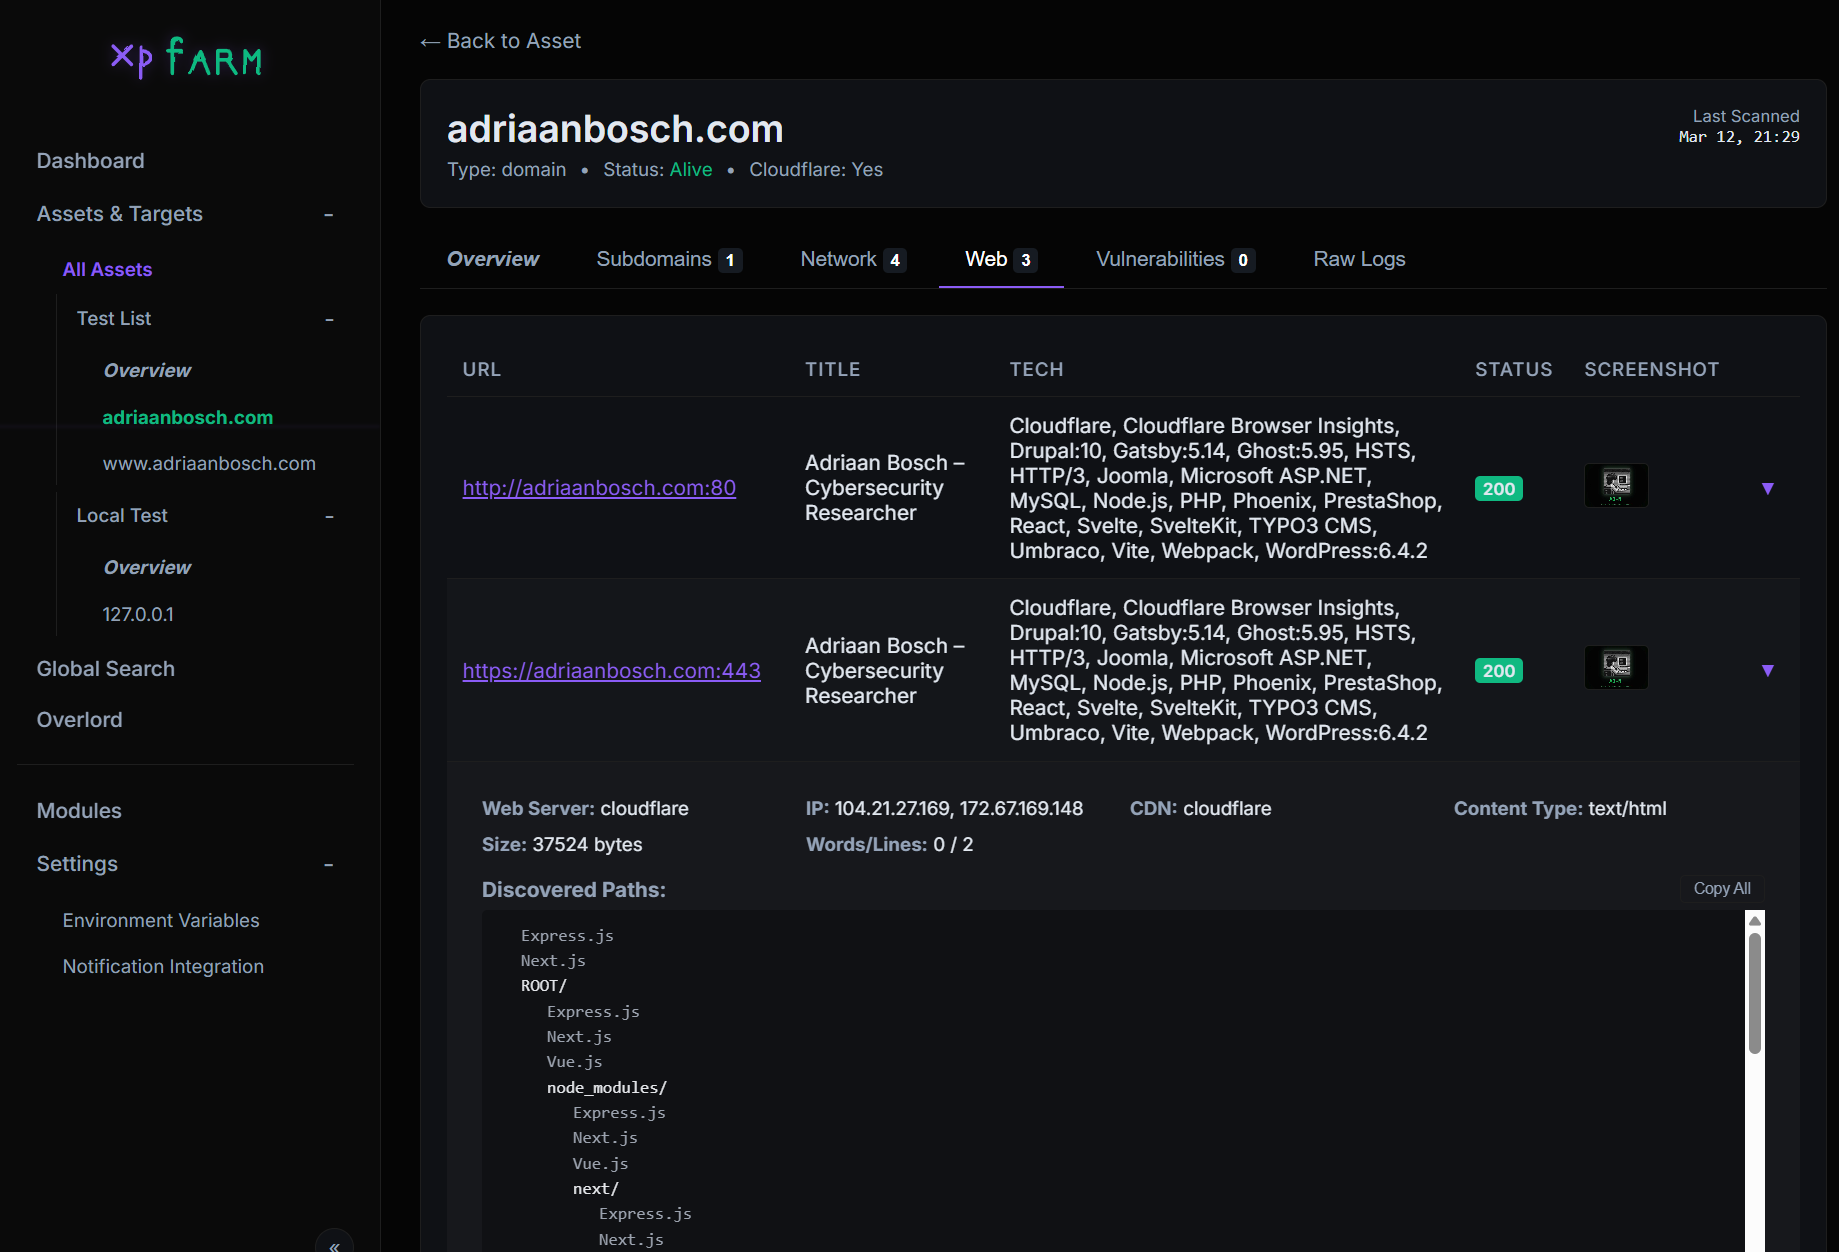 canuk40/xpfarm
Automated bug bounty & recon framework — wraps Subfinder, Naabu, Httpx, Nuclei, Nmap, CVEMap, Gowitness, Katana & more behind a unified web UI
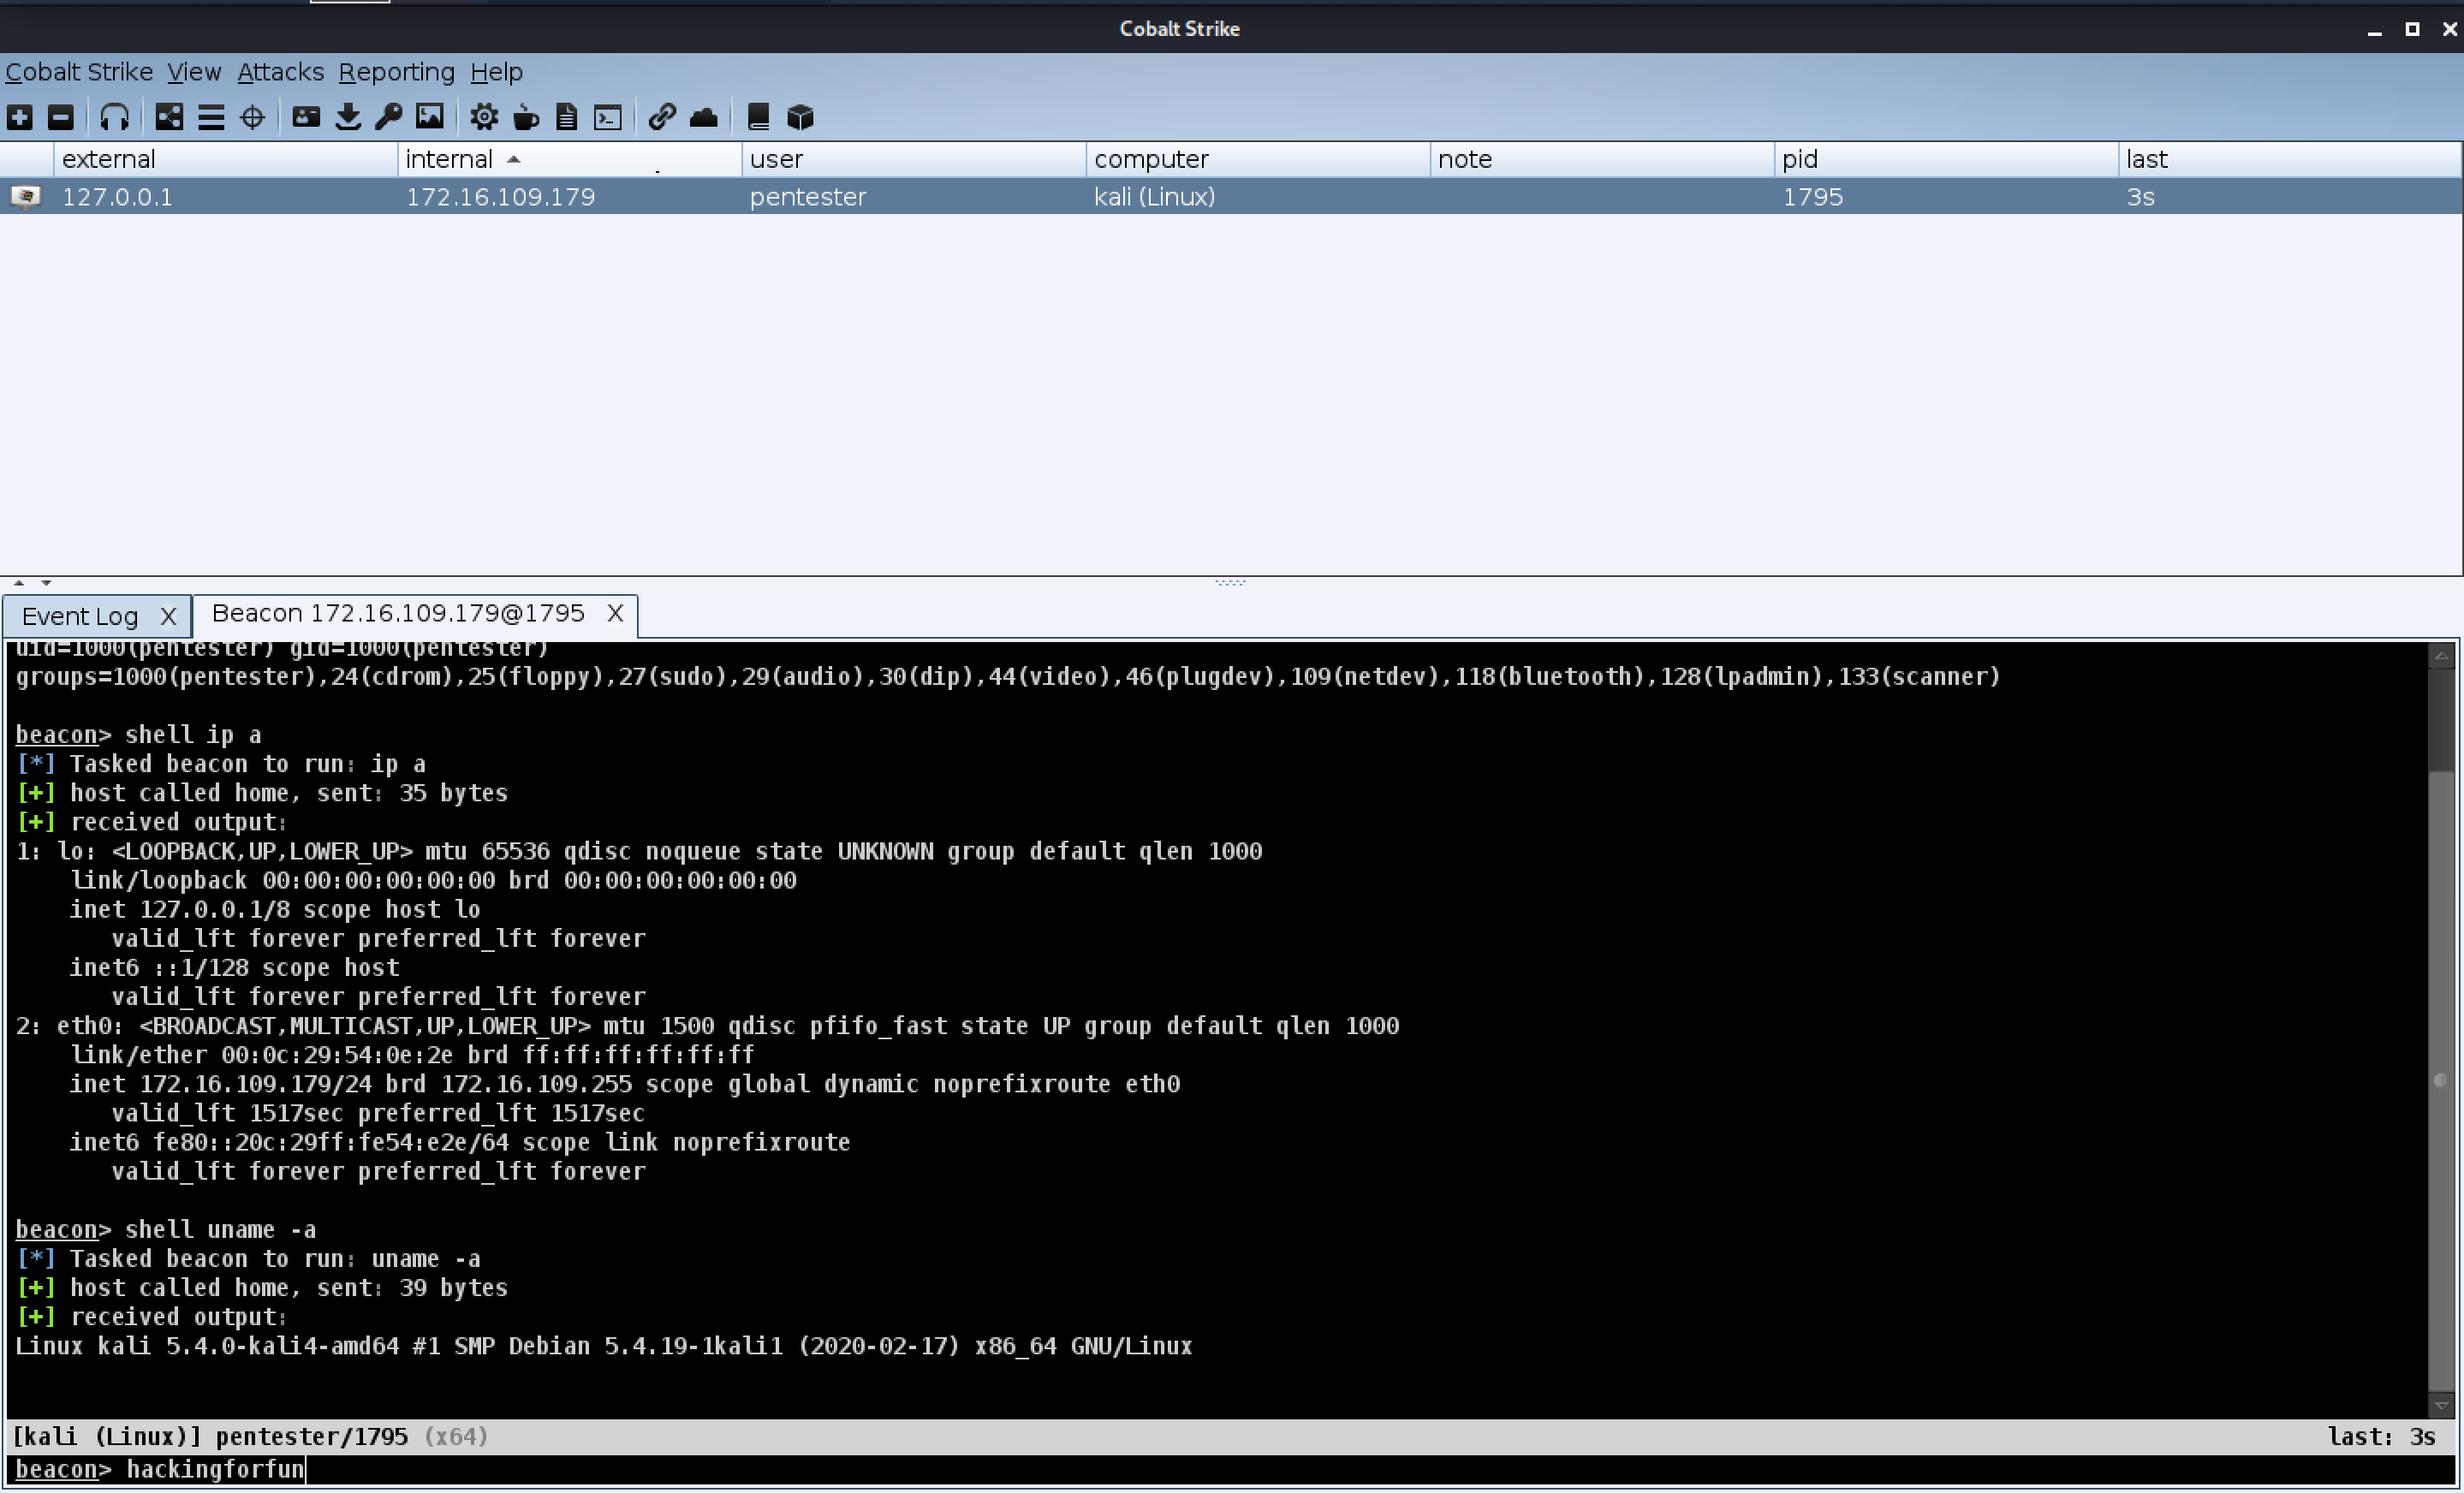 darkr4y/geacon
Practice Go programming and implement CobaltStrike's Beacon in Go