

frida-ios-hook
 noobpk/frida-ios-hook
A tool that helps you easy trace classes, functions, and modify the return values of methods on iOS platform
binary-analysisdynamic-analysis-sandboxingios-security+3
1.2k
noobpk/frida-ios-hookA tool that helps you easy trace classes, functions, and modify the return values of methods on iOS platform
 m0bilesecurity/rms-runtime-mobile-security
Runtime Mobile Security (RMS) 📱🔥 - is a powerful web interface that helps you to manipulate Android and iOS Apps at Runtime
 xcodeon1/ipa-scope
Static analysis tool for iOS applications that extracts links, API keys, subdomains, binary info, linked libraries, and strings to aid mobile…
 lautarovculic/frida-ipa-extract
Robust Frida-based tool to dump decrypted iOS apps as .ipa from a jailbroken device supports App Store, sideloaded and system.
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
 nightbringer21/fridump
Cross-platform memory dumper using Frida to extract accessible memory from iOS, Android, and Windows applications for forensic analysis and…
 prateek147/dvia-v2
Damn Vulnerable iOS App (DVIA) is an iOS application that is damn vulnerable. Its main goal is to provide a platform to mobile security…
 isecpartners/introspy-ios
Security profiling for blackbox iOS
 alonemonkey/frida-ios-dump
Extracts decrypted IPA files from jailbroken iOS devices using Frida for reverse engineering, security analysis, and mobile app pentesting.
 f4r3sx0/ios-bluetooth-ethernet-exploit
iOS Bluetooth PAN vulnerability that opens USB port 62078 and displays Ethernet icon without any adapter (€0). Apple sells a €89.95 adapter for the…
 george0papasotiriou/cve-2026-22011-ios-mdm-profile-delivery-over-http
PoC Flask server for CVE-2026-22011 that serves a malicious iOS MDM enrollment profile over HTTP, enabling man-in-the-middle interception and device…
 sterrasec/ipa-medit
Memory modification tool for re-signed ipa supports iOS apps running on iPhone and Apple Silicon Mac without jailbreaking.
 dmayer/idb
idb is a tool to simplify some common tasks for iOS pentesting and research
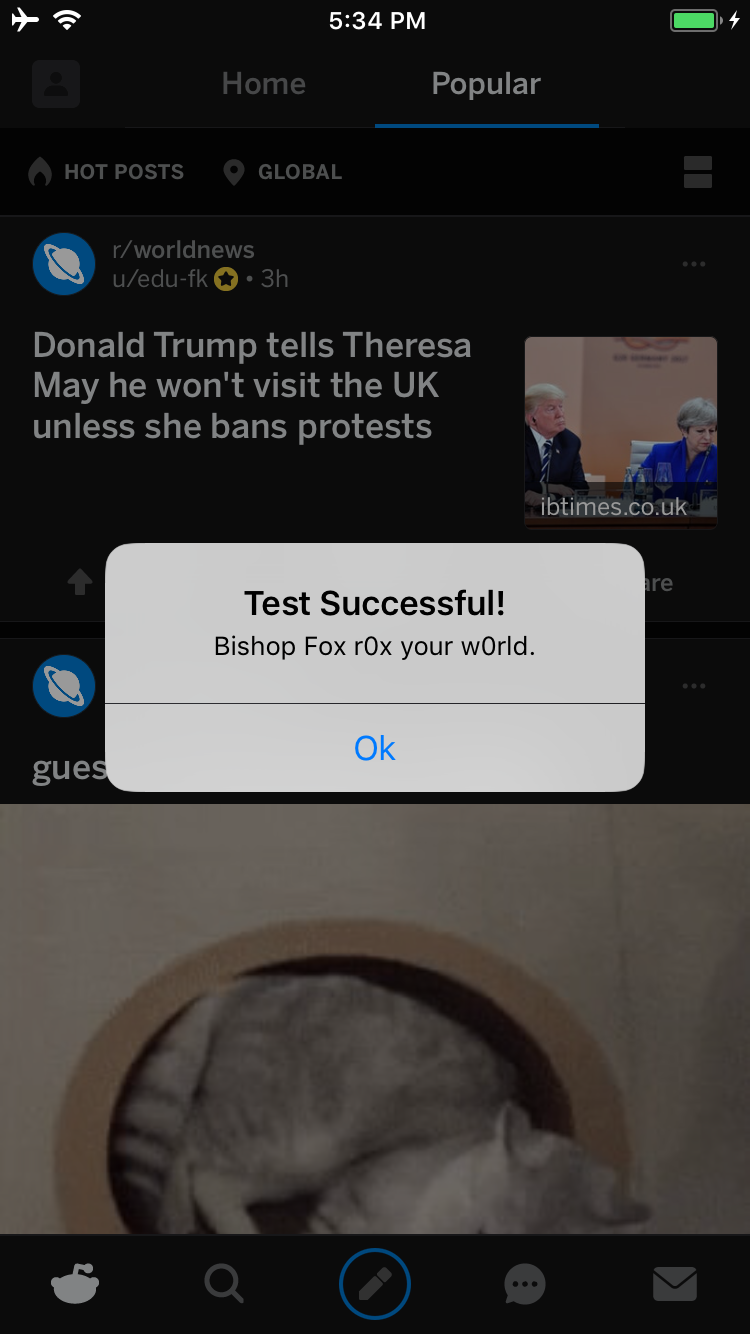 bishopfox/bfinject
Dylib injection for iOS 11.0 - 11.1.2 with LiberiOS and Electra jailbreaks
 jailbreakdotparty/dirtyzero
Simple customization toolbox, utilizing CVE-2025-24203. Supports iOS 16.0 - iOS 18.3.2.
 vighnesh91/ipaforge
Dependency-free Python CLI to unpack, inspect, edit, and rebuild iOS .ipa archives, converting plists and strings to XML while preserving Mach-O…
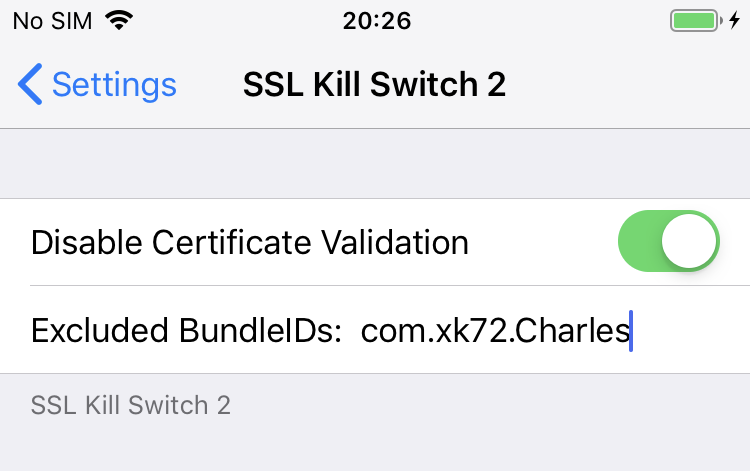 nabla-c0d3/ssl-kill-switch2
Blackbox tool to disable SSL certificate validation - including certificate pinning - within iOS and macOS applications.
 gabrielg/cve-2014-1266-poc
Proof-of-concept exploit for Apple SSL/TLS verification vulnerability (CVE-2014-1266) in iOS and OS X, demonstrating HTTPS interception via a proxy…