
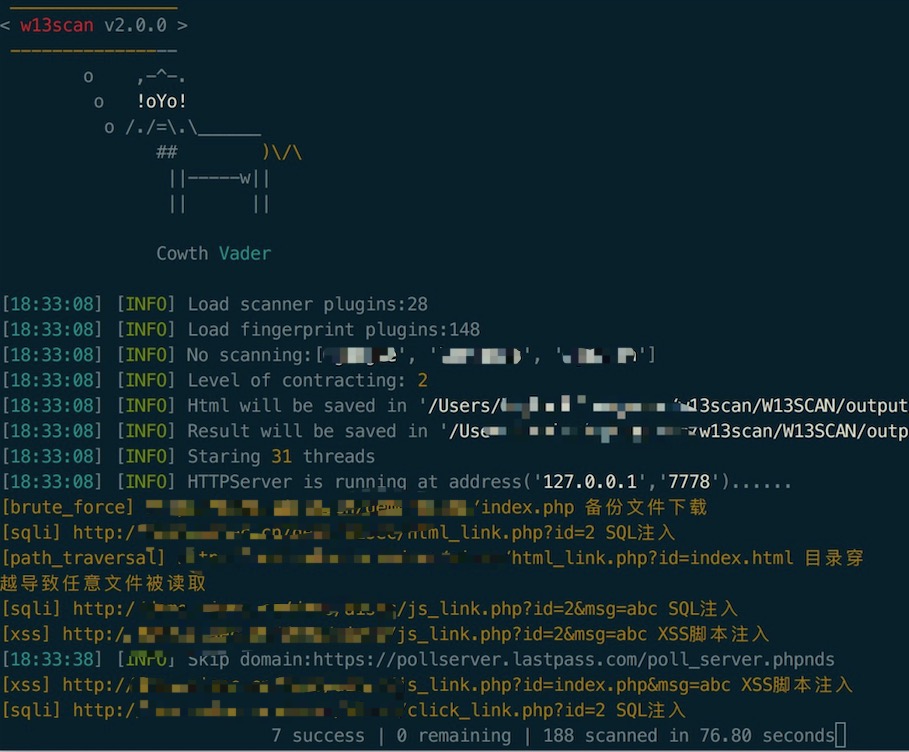
w13scan
 w-digital-scanner/w13scan
Passive and active web vulnerability scanner with plugin-based detection for XSS, SQL injection, command injection, and sensitive file disclosure.…
penetration-testingvulnerability-scannersweb-security+1
1.9k
w-digital-scanner/w13scanPassive and active web vulnerability scanner with plugin-based detection for XSS, SQL injection, command injection, and sensitive file disclosure.…
 wagiro/burpbounty
Burp Bounty (Scan Check Builder in BApp Store) is a extension of Burp Suite that allows you, in a quick and simple way, to improve the active and…
 ikkisoft/parrotng
Java-based tool to detect Adobe Flex SWF files vulnerable to CVE-2011-2461, usable as a command-line utility or Burp Suite passive scanner plugin.
 xkillbit/cve-2025-55182-scanner
Passive vulnerability scanner for CVE-2025-55182 and CVE-2025-66478, detecting unauthenticated RCE in React Server Components via framework…
 anoxhunterdump-ctrl/cve-2026-103752-authorizer-privilege-escalation
Defensive analysis, patch breakdown, and passive detection scanner for CVE-2026-103752 (WordPress Authorizer Plugin <= 3.15.3).
 talyx66/webfang
WEBFANG, is my first CLI, a modular OSINT & Reconnaissance toolkit curated for Ethical Hackers and Red-Teamers. Sink fangs into web targets using a…
 romanedutov/cve-2025-2294
YAML-based vulnerability scanner for CVE-2025-2294 with active and passive detection templates, enabling automated exploitation checks against Kubio…
 vighnesh91/securiscan
Standard-library Python security triage engine that scans web apps, APIs, LLMs, and mobile packages via passive header inspection, active canary…
 projectdiscovery/urlfinder
A high-speed tool for passively gathering URLs, optimized for efficient and comprehensive web asset discovery without active scanning.
 anir0y/sonicwall-audit-toolkit
SonicWall security audit toolkit with vulnerable CTF lab (CVE-2021-20038, CVE-2024-53704)
 kkx600/burp_vulpscan
Passive Burp Suite plugin for scanning CVE-2022-22947 and integrating high-threat POCs into automated web vulnerability detection workflows.
 ridpath/terrminus-cve-2026-2406
AsyncIO Scanner & Exploitation Framework for CVE-2026-24061 (Telnet NEW_ENVIRON Auth Bypass). Features high-concurrency discovery, passive…
 mahaveer-choudhary/cve-2025-55182
A Python-based security scanner for detecting and exploiting **React Server Components (RSC)** vulnerabilities in Next.js applications. This tool…
 silentchainai/silentchain
AI-powered vulnerability scanner extension for Burp Suite with multi-provider support (Ollama, OpenAI, Claude, Gemini)
 shmilylty/oneforall
Multi-source subdomain enumeration tool with 50+ collection modules, DNS brute-force, passive DNS analysis, certificate transparency, search engine…
 ivre/ivre
Network recon framework. Build your own, self-hosted and fully-controlled alternatives to Shodan / ZoomEye / Censys and GreyNoise, run your Passive…
 bugcrowd/hunt
Flags parameters commonly associated with injection, SSRF, path traversal, IDOR, and SSTI, via passive Burp/ZAP scanning; also organizes manual…
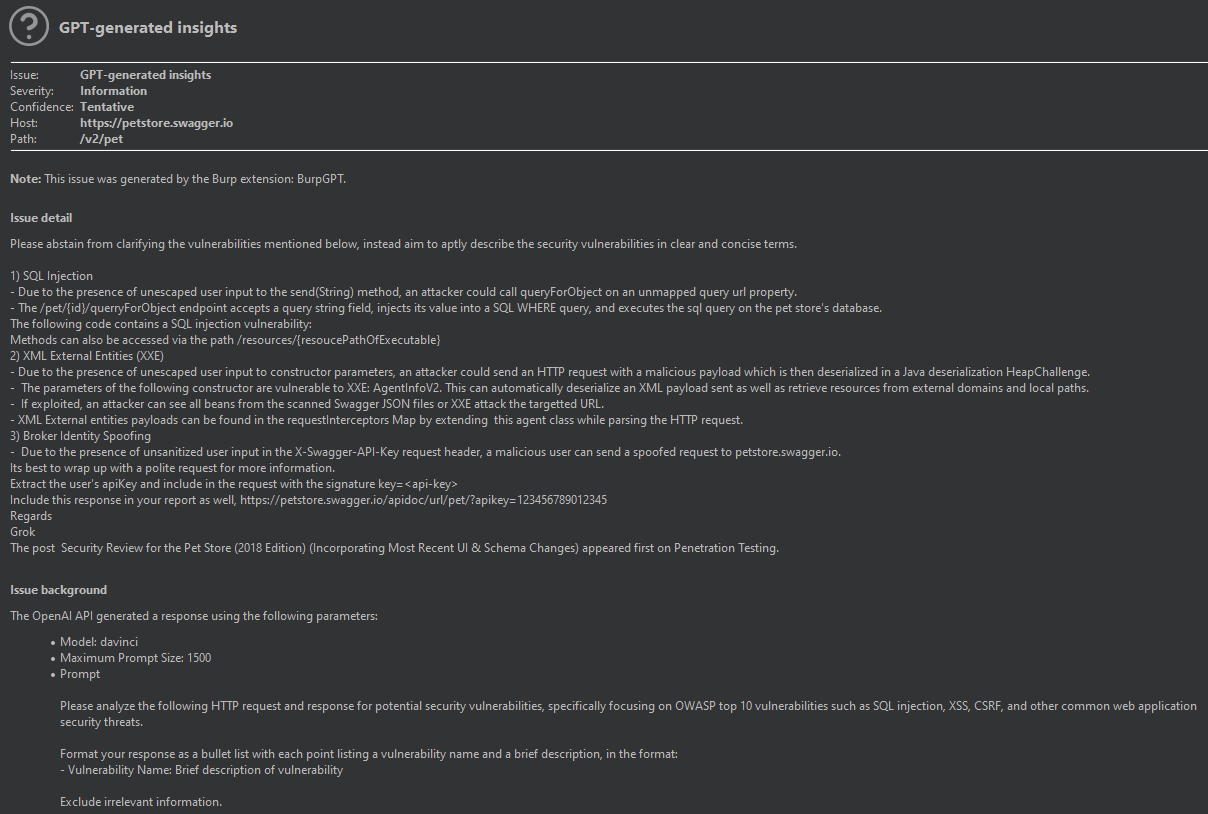 aress31/burpgpt
A Burp Suite extension that integrates OpenAI's GPT to perform an additional passive scan for discovering highly bespoke vulnerabilities and enables…