Blind-SSRF-to-Remote-Code-Execution-Shellshock-Professional-Bug-Bounty-Report

Professional bug bounty report detailing the exploitation of a Blind SSRF vulnerability leading to Shellshock (CVE-2014-6271) remote code execution,…

Professional bug bounty report detailing the exploitation of a Blind SSRF vulnerability leading to Shellshock (CVE-2014-6271) remote code execution,…

Professional JWT security testing toolkit. Analyze, crack, forge, and exploit JSON Web Tokens with 15+ vulnerability checks, 100k secret wordlist,…

Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…

Deliberately vulnerable Docker lab with a routable DNS estate and machine-readable answer keys per target, scoring scanner precision, recall and…

File Inclusion & Directory Traversal fuzzing, enumeration & exploitation tool.

DEPRECATED, please use the new repository from OWASP: https://github.com/OWASP/raider

Autonomous AI red team agent for penetration testing with 13+ specialized agents, 120+ OWASP test cases, and MITRE ATT&CK integration. Supports 15+…

Penetration tests guide based on OWASP including test cases, resources and examples.

OWASP Web Recon & Directory Discovery Platform

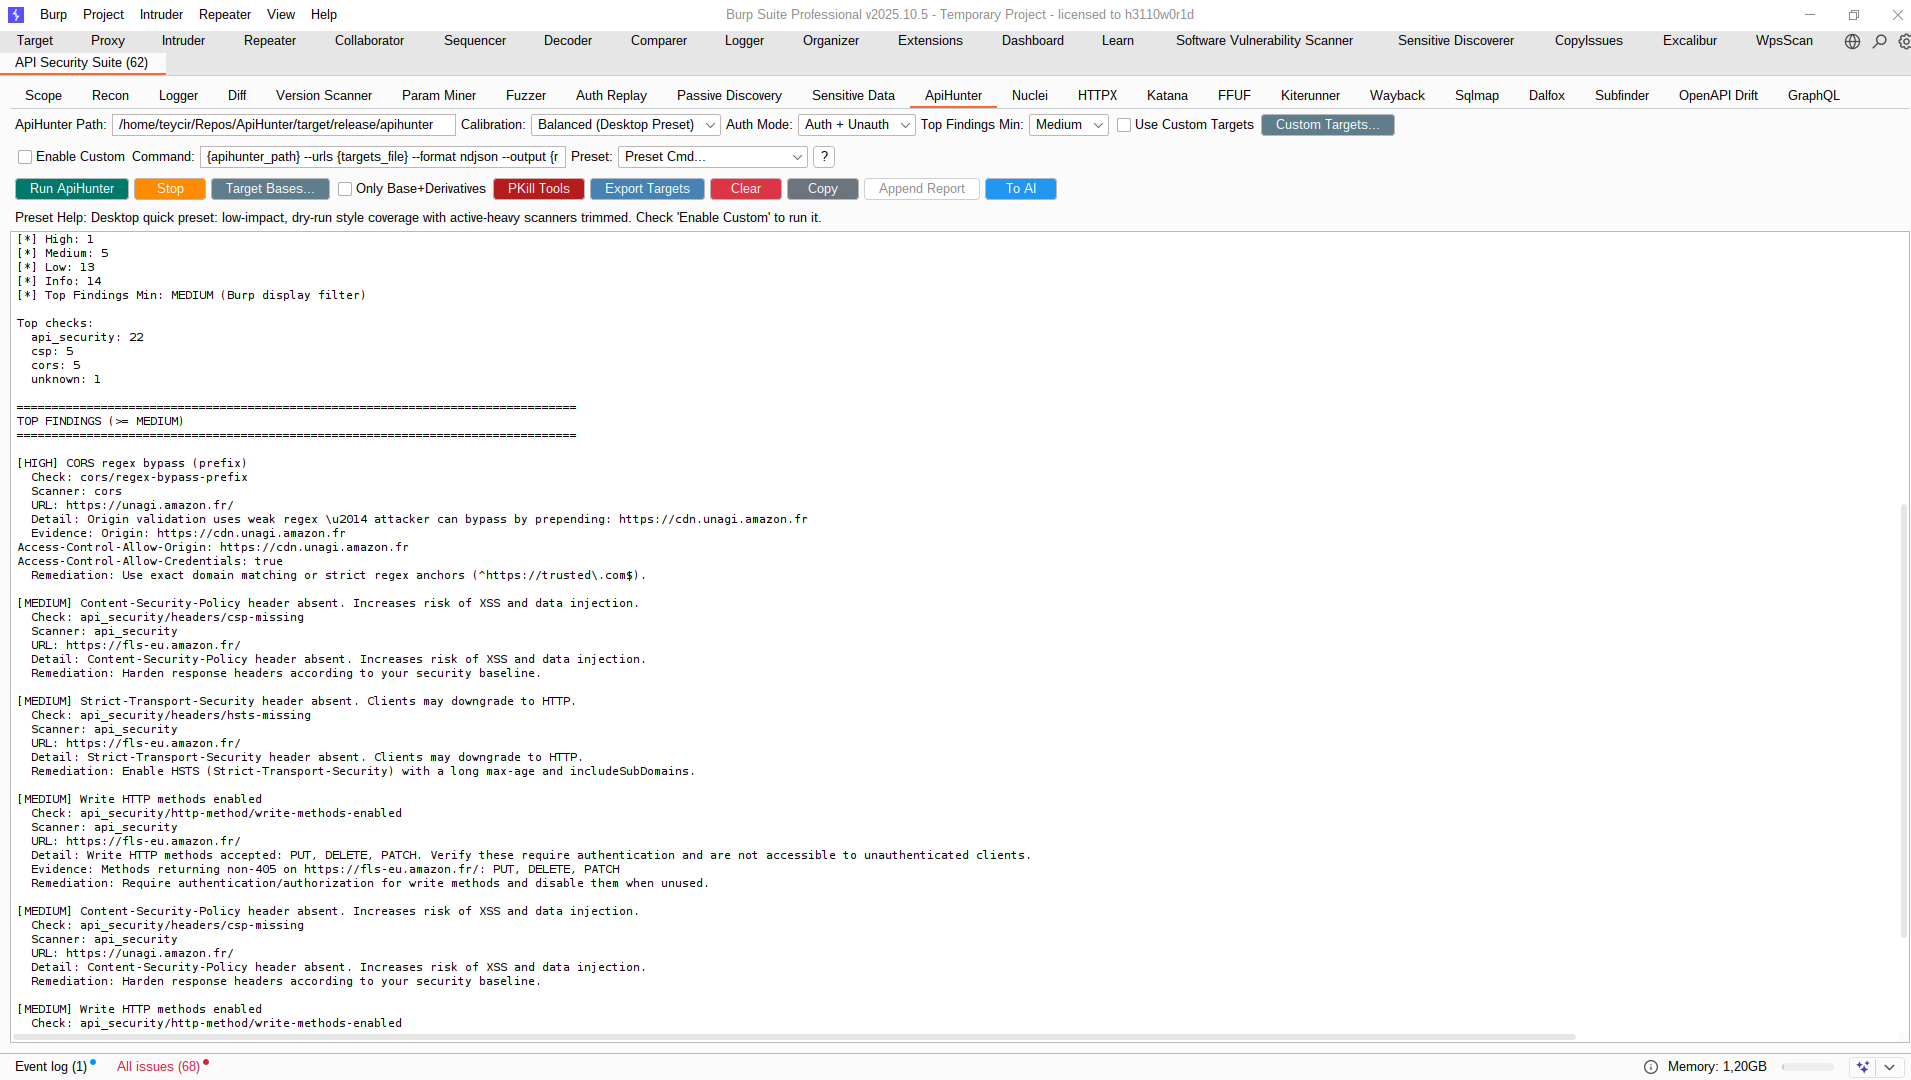
Burp Suite extension for API security testing with 15 attack types, 108+ payloads, intelligent fuzzing, BOLA/IDOR detection, AI integration, and…

OWASP Mth3l3m3nt Framework is a penetration testing aiding tool and exploitation framework. It fosters a principle of attack the web using the web as…

A OWASP Based Checklist With 80+ Test Cases

Open-source cross-modal and multimodal prompt injection test suite. 250,000+ attack payloads across text, image, document, and audio modalities.…

Hands-on capture-the-flag lab for the OWASP Kubernetes Top 10 (2025). Exploit 11 real-world cluster weaknesses, capture flags, then apply fixes and…

Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…

OWASP Web Security Testing Guide RAG system with ChromaDB, MCP for Claude Code

Automated API security testing tool that scans REST and SOAP APIs for vulnerabilities using OpenAPI/Swagger specs and WSDL files. Deploys a full …