
CVE-2025-45512
 azhariramadhan/cve-2025-45512
Proof-of-concept exploit suite for U-Boot bootloader vulnerabilities, including insecure update mechanisms, hardcoded credentials, debugging…
embedded-systems-securityexploitationfirmware-analysis+5
2
azhariramadhan/cve-2025-45512Proof-of-concept exploit suite for U-Boot bootloader vulnerabilities, including insecure update mechanisms, hardcoded credentials, debugging…
 ivanglinkin/cve-2024-36821
The public reference that contains the minimum require information for the vulnerability covered by CVE-2024-36821
 dirtyfilthy/gxv3175-remote-code-exec
Remote code execution for Grandstream GXV3175 VOIP phone.
 thorat-shubham/jxl_infotainment_cve-2025-69515
Proof-of-concept exploit for CVE-2025-69515 demonstrating static GPS spoofing on JXL 9-inch Android infotainment units via SDR-based signal…
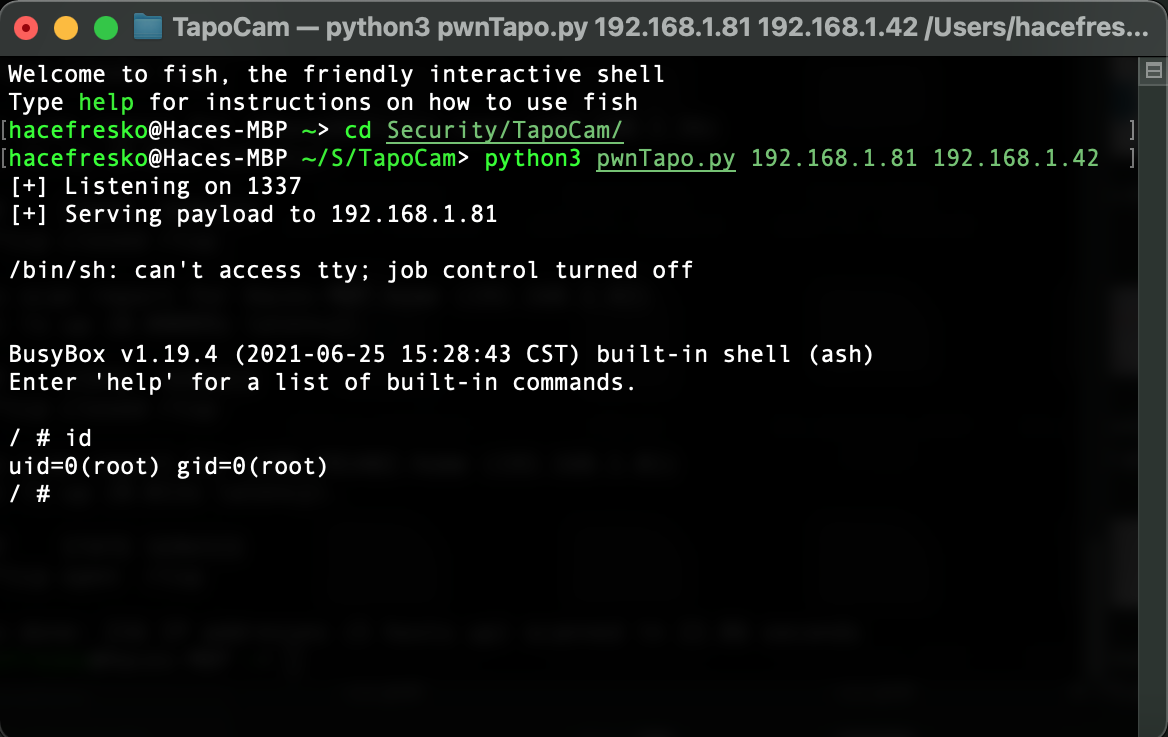 kaleth4/cve-2021-4045
Command injection exploit for TP-Link Tapo C200 camera (CVE-2021-4045) providing root shell access via UART and reverse-engineered uhttpd binary…
 mbanyamer/cve-2026-32707-px4-autopilot-tattu_can-stack-buffer-overflow-dos-
Proof-of-concept exploit for CVE-2026-32707, a stack buffer overflow in the PX4-Autopilot tattu_can driver, causing denial of service via crafted CAN…
 oliviaholly/fusee-gelee
An implementation of the Fusee Gelee exploit (CVE-2018-6242) for the Nintendo Switch, along with a custom payload.
 deepwoodssec/cve-2026-36522
Proof-of-concept exploit for CVE-2026-36522: unauthenticated NaN injection via MAVLink PARAM_SET in ArduPilot ArduPlane, causing DoS or silent…
 cipherx1802/cve-2025-69821-beat-xp-vega-smartwatch-security-assessment
A security assessment of the Beat XP VEGA Smartwatch (Firmware RB303ATV006229) focused on Bluetooth Low Energy (BLE) connectivity revealed a design…
 s-hamann/cve-2023-40289
Exploit for CVE-2023-40289, a command injection vulnerability in several Baseband Management Controllers (BMC) by with firmware by ATEN
 rizzziom/cve-2024-30167
Proof-of-concept exploit for authenticated command injection in Atlona AT-OME-RX21, allowing root-level command execution via the time configuration…
 zgsnj123/cve-2025-45467
Proof-of-concept exploit for CVE-2025-45467, demonstrating remote code execution on Unitree Go1 robotic dogs via insecure MD5-based firmware…
 whitej3rry/cve-2025-65731
Advisory for CVE-2025-65731
 fadingminibus69/advisory001
Proof-of-concept exploit for CVE-2026-52504 targeting Exein Pulsar, with detailed vulnerability description and exploitation methodology.
 yezeting/cve-2021-41730
Proof-of-concept exploit for CVE-2021-41730, demonstrating remote command execution in TENDA AC15/AC6 routers via unvalidated formSetIptv()…
 stigtsp/cve-2018-20162-digi-lr54-restricted-shell-escape
Proof-of-concept exploit for CVE-2018-20162: sandbox escape in Digi TransPort LR54 LTE router via SIGINT handling flaw, yielding root shell access.
 trinadh465/device_renesas_kernel_aosp10_r33_cve-2022-0492
Kernel source repository with modifications addressing CVE-2022-0492, providing a patched or vulnerable environment for security research and…
 kernoelpanic/cve-2015-8299
Proof-of-concept exploit for a remote buffer overflow vulnerability in KNX ETS4 management software, demonstrating ROP-based code execution via…