
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
294 results
RancidCrisco preview

RancidCrisco

GitHubfullspectrumdev/rancidcrisco

Proof-of-concept exploit for CVE-2023-20126 targeting Cisco SPA phone adapters. Uploads malicious firmware to gain a root shell on port 23000/tcp via…

embedded-systems-securityexploitationfirmware-analysis+5
24
3 years ago
Cable-modems preview

Cable-modems

GitHubebux/cable-modems

Black-box security evaluation of five ISP cable modem/router gateways, analyzing firmware images and documenting 35+ vulnerabilities including…

embedded-systems-securityexploitationfirmware-analysis+5
2510 years ago
tiandy-research preview

tiandy-research

GitHubzb3/tiandy-research

This repository contains the results of my August 2020 research of Tiandy's IPC/NVR firmware. I found two vulnerabilities that could be used to…

authenticationembedded-systems-securityexploitation+7
306 years ago
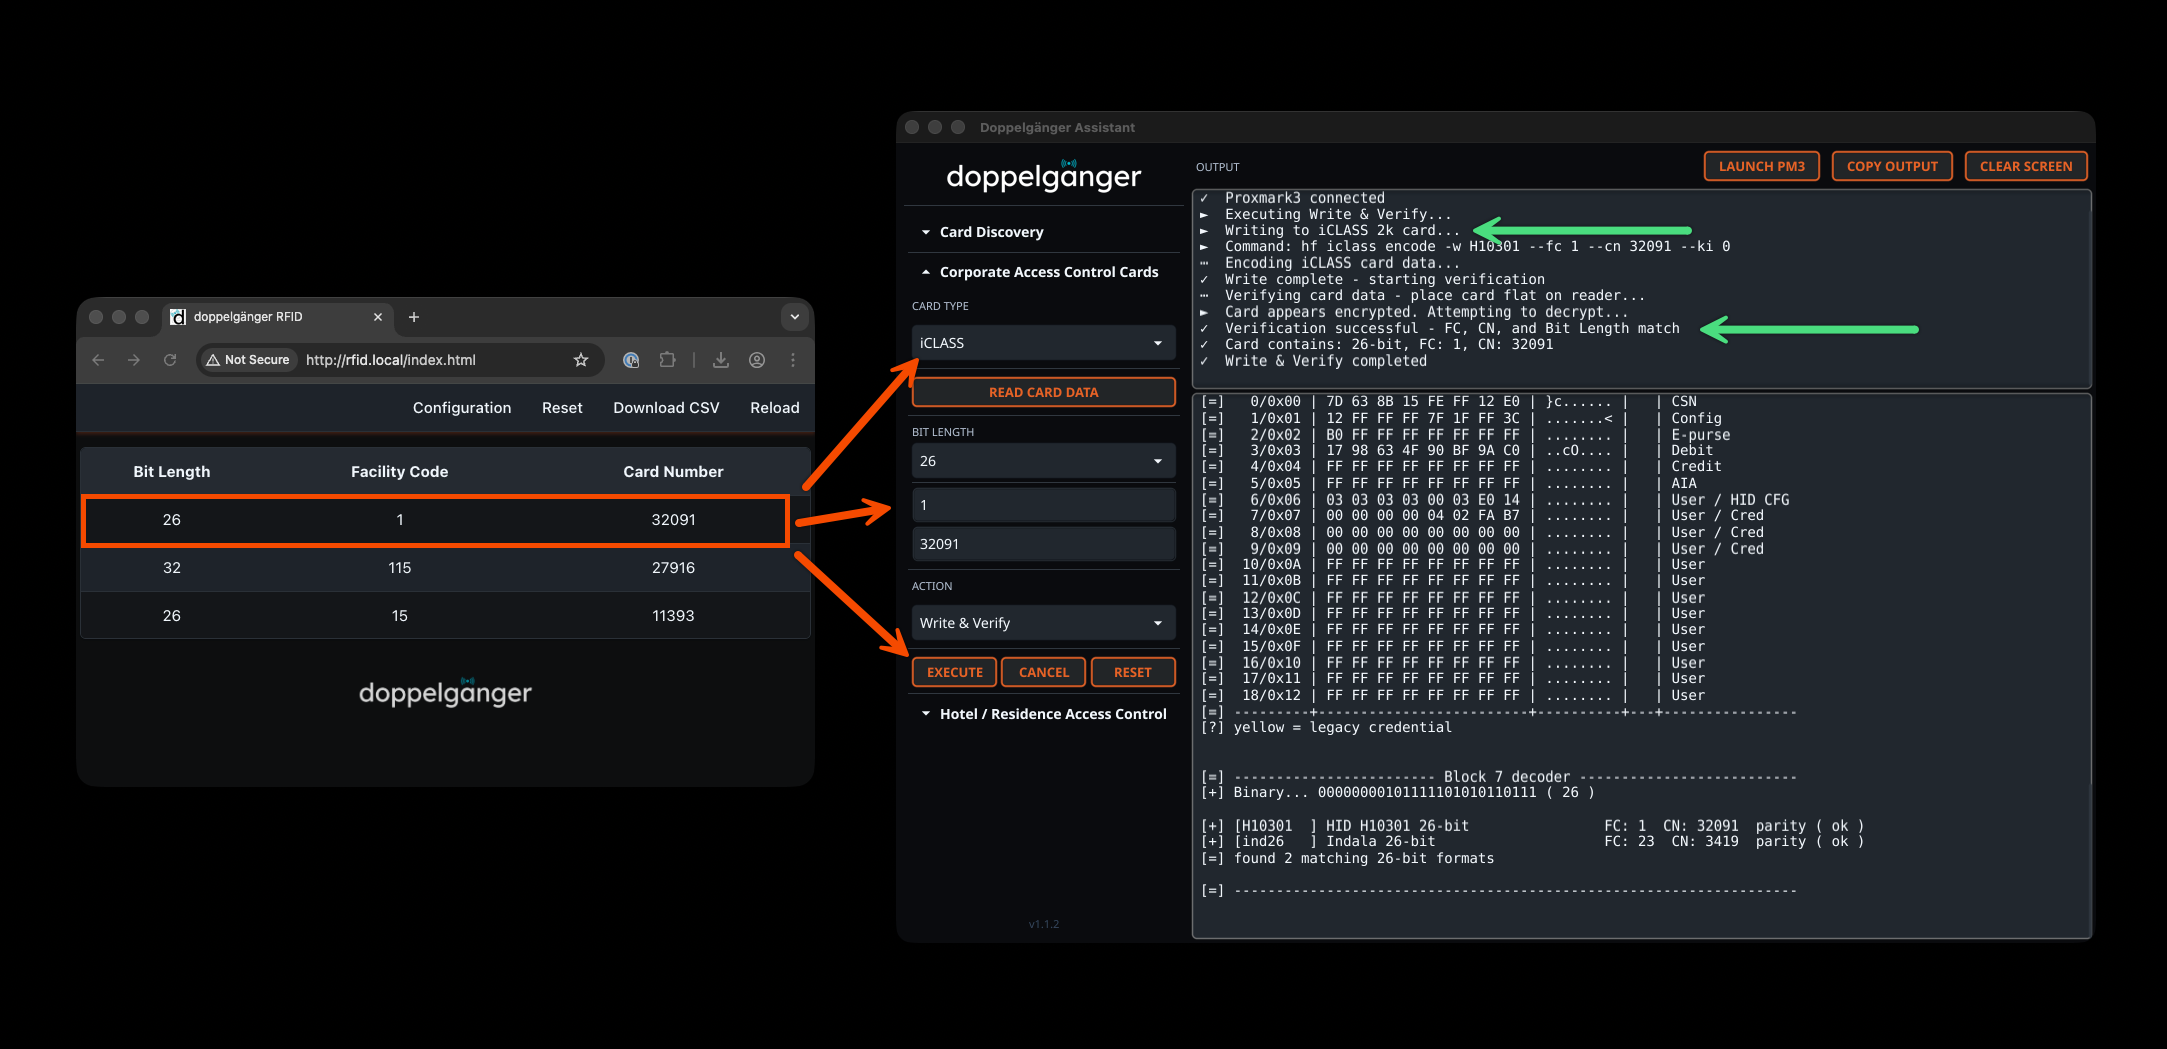
doppelganger_assistant preview

doppelganger_assistant

GitHubtweathers-sec/doppelganger_assistant

Card calculator and Proxmark3 Plugin for writing and/or simulating every card type that Doppelgänger Community, Pro, Stealth, and MFAS support.

embedded-systems-securityencryption-decryption-toolshardware-hacking+5
349 months ago
CVE-2017-16778-Intercom-DTMF-Injection preview

CVE-2017-16778-Intercom-DTMF-Injection

GitHubbreaktoprotect/cve-2017-16778-intercom-dtmf-injection

A coordinated disclosure and security advisory on Fermax Intercom DTML Injection vulneraiblity. Special thanks to Fermax International for prompt…

embedded-systems-securityexploitationhardware-hacking+6
226 years ago
watchTowr-vs-SonicWall-PreAuth-RCE-Chain preview

watchTowr-vs-SonicWall-PreAuth-RCE-Chain

GitHubwatchtowrlabs/watchtowr-vs-sonicwall-preauth-rce-chain

PoC exploit chain for pre-authentication remote code execution on SonicWall SMA 100 appliances exploiting CVE-2023-44221 and CVE-2024-38475.

embedded-systems-securityexploitationpenetration-testing+3
191 year ago
CVE-2025-2620-poc preview

CVE-2025-2620-poc

GitHubotsmane-ahmed/cve-2025-2620-poc

Proof-of-concept exploit for CVE-2025-2620, a critical stack-based buffer overflow in D-Link DAP-1620 routers enabling unauthenticated remote code…

binary-exploitationembedded-systems-securityexploitation+8
161 year ago
CVE-2023-22906 preview

CVE-2023-22906

GitHubnonamecoder/cve-2023-22906

Proof of Concept for CVE-2023-22906

embedded-systems-securityexploitationhardware-iot-security+3
83 years ago
CVE-2026-38577 preview

CVE-2026-38577

GitHubpoxsky/cve-2026-38577

Proof-of-concept demonstrating hardcoded root credentials (admin/system) in Tenda HG21 XPON modem firmware, enabling unauthorized root access via…

embedded-systems-securityexploitationfirmware-analysis+5
24 days ago
misfortune-cookie preview

misfortune-cookie

GitHubluel-4013/misfortune-cookie

Interactive PoC suite for CVE-2014-9222 (Misfortune Cookie) and related router exploits, featuring detection, auth bypass, DoS, and RCE modules with…

binary-exploitationembedded-systems-securityexploitation+6
19 days ago
CVE-2025-9961 preview

CVE-2025-9961

GitHubyt2w/cve-2025-9961

Exploit for TP-Link AX10/AX1500 stack buffer overflow in CWMP (TR-069) enabling remote code execution via ret2libc with ASLR bypass. Includes…

binary-exploitationembedded-systems-securityexploitation+5
69 months ago
CVE-2026-6837-zyxel-export-cgi-command-injection preview

CVE-2026-6837-zyxel-export-cgi-command-injection

GitHubminanagehsalalma/cve-2026-6837-zyxel-export-cgi-command-injection

Public writeup, PoC, and emulation materials for CVE-2026-6837 affecting Zyxel export-cgi PKCS#12 export handling.

embedded-systems-securityexploitationfirmware-analysis+3
31 month ago
ledger-app-monero-1.42-vuln preview

ledger-app-monero-1.42-vuln

GitHubph4r05/ledger-app-monero-1.42-vuln

PoC repository for CVE-2020-6861: Ledger Monero App Spend key Extraction

cryptographyembedded-systems-securityexploitation+3
46 years ago
cve-2021-21735-zte-zxhn-h168n-admin-compromise preview

cve-2021-21735-zte-zxhn-h168n-admin-compromise

GitHubminanagehsalalma/cve-2021-21735-zte-zxhn-h168n-admin-compromise

CVE-2021-21735 write-up: ZTE ZXHN H168N V3.5 wizard-page information leak, firmware routing flaw, and the path from exposed PPPoE/WLAN data to full…

embedded-systems-securityexploitationfirmware-analysis+3
44 months ago
CVE-2021-44827 preview

CVE-2021-44827

GitHubfull-disclosure/cve-2021-44827

Proof-of-concept exploit for authenticated remote code execution (CVE-2021-44827) targeting TP-Link Archer C20i routers. Provides post-exploitation…

embedded-systems-securityexploitationhardware-iot-security+4
44 years ago
CVE-2024-48705 preview

CVE-2024-48705

GitHubl41kaa/cve-2024-48705

Wavlink AC1200 with firmware versions M32A3_V1410_230602 and M32A3_V1410_240222 are vulnerable to a post-authentication command injection while…

binary-analysiscommand-and-controlembedded-systems-security+7
21 year ago
PX4-Military-UAV-Autopilot-1.12.3-Stack-Buffer-Overflow-Exploit-CVE-2025-5640- preview

PX4-Military-UAV-Autopilot-1.12.3-Stack-Buffer-Overflow-Exploit-CVE-2025-5640-

GitHubmbanyamer/px4-military-uav-autopilot-1.12.3-stack-buffer-overflow-exploit-cve-2025-5640-

Proof-of-concept exploit for CVE-2025-5640, a stack buffer overflow in PX4 Military UAV Autopilot <=1.12.3. Sends crafted MAVLink packets to trigger…

binary-exploitationembedded-systems-securityexploitation+3
41 year ago
CVE-2023-33781 preview

CVE-2023-33781

GitHubs0tr/cve-2023-33781

Proof-of-concept exploit for CVE-2023-33781 enabling arbitrary binary execution on D-Link DIR-842V2 routers via telnet and backup/restore…

binary-exploitationembedded-systems-securityexploitation+3
16 months ago
Previous1…456…17Next