

CVE-2023-38646
 yxl2001/cve-2023-38646
PoC exploit for CVE-2023-38646, a pre-authentication RCE in Metabase. Includes a reverse shell payload generator with base64 encoding fix for…
exploitationpayload-generationpenetration-testing+3
yxl2001/cve-2023-38646PoC exploit for CVE-2023-38646, a pre-authentication RCE in Metabase. Includes a reverse shell payload generator with base64 encoding fix for…
 muhammad-ali007/log4j_cve-2021-44228
Hands-on lab exercise for exploiting Log4Shell (CVE-2021-44228) with JNDI injection, LDAP referral servers, and reverse shell payloads. Includes…
 hungdnvp/poc-cve-2020-0796
Proof-of-concept exploit for CVE-2020-0796 (SMBGhost) targeting Windows 10/Server SMBv3.1.1. Includes Nmap reconnaissance, vulnerability scanning,…
 h3x0v3rl0rd/cve-2019-5736
Go-based exploit for CVE-2019-5736 (Runc container escape) with a customizable reverse shell payload, designed for penetration testing and red team…
 giovannipajeu1/cve-2024-23741
Automated exploit for CVE-2024-23741 targeting Hyper on macOS. Validates vulnerability and injects code to spawn a remote shell via RunAsNode and…
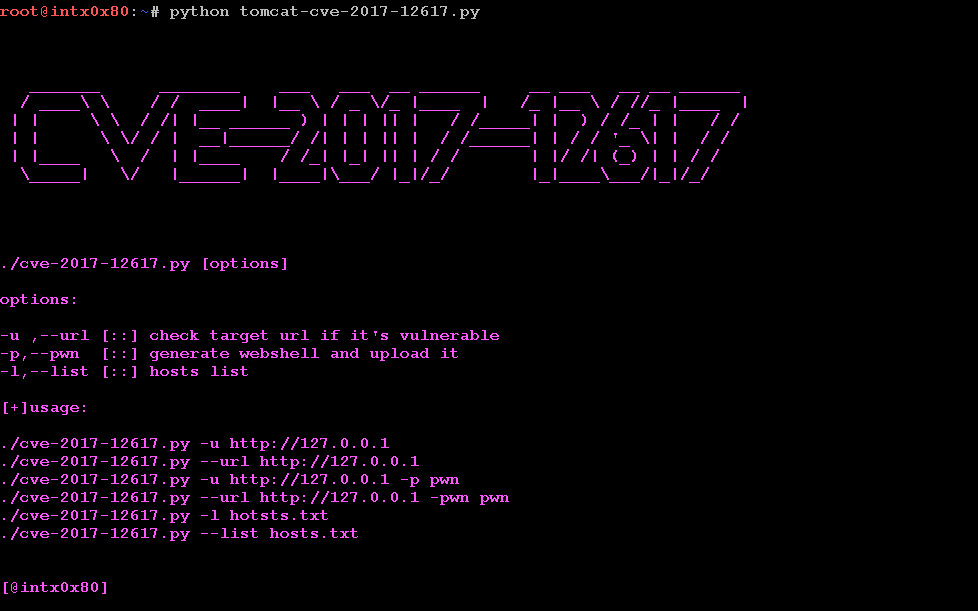 scirusvulgaris/cve-2017-12617
Python exploit for Apache Tomcat CVE-2017-12617 RCE vulnerability. Checks targets, generates webshells, and provides remote shell access on systems…
 z50913/cve-2020-27955
Proof-of-concept exploit for CVE-2020-27955 in Git-LFS, demonstrating remote code execution via a crafted git clone operation to obtain a reverse…
 finn79426/cve-2020-10199
Proof-of-concept and technical walkthrough demonstrating remote code execution in Sonatype Nexus, including EL injection debugging, BCEL payload…
 dnr6419/cve-2018-16167
Proof-of-concept exploit for LogonTracer v1.2.0 remote code execution vulnerability, providing a reverse shell via Python and netcat.
 hopsypopsy8/cve-2024-53677-exploitation
Step-by-step walkthrough for exploiting Apache Struts CVE-2024-53677 RCE via file upload manipulation, including OGNL injection, payload embedding,…
 monjheta/cve-2020-0796
Proof-of-concept remote code execution exploit for CVE-2020-0796 (SMBGhost) targeting unpatched Windows 10 1903/1909. Delivers a reverse shell via…
 nxploited/cve-2024-2667-poc
PoC exploit for CVE-2024-2667: automated arbitrary file upload and shell access via insufficient file validation in InstaWP Connect WordPress plugin…
 wtn-arny/cve-2024-37085
Python exploit for CVE-2024-37085, an authentication bypass in domain-joined ESXi hypervisors, enabling unauthenticated shell upload and full…
 assassinukg/cve-2020-8165
Python exploit shell for CVE-2020-8165, providing a reverse shell payload for remote code execution on vulnerable Rails applications.
 tannlh/cve-2018-20250
Exploit for CVE-2018-20250 (WinRAR ACE path traversal) with automated payload generation and Metasploit reverse shell integration for penetration…
 khaidtraivch/cve-2021-41773-apache-2.4.49-
Exploit scripts for CVE-2021-41773 (Apache 2.4.49) enabling path traversal and remote code execution via CGI, including a reverse shell payload.
 wytchwulf/cve-2015-1397-magento-shoplift
Exploit scripts for CVE-2015-1397 in Magento CMS, including a pre-auth exploit to gain admin credentials and a post-auth RCE module for reverse shell…
 cotherm/cve-2025-25706
Detailed CVE-2025-25706 proof-of-concept demonstrating authenticated remote code execution via command injection in ProApps ping functionality,…