
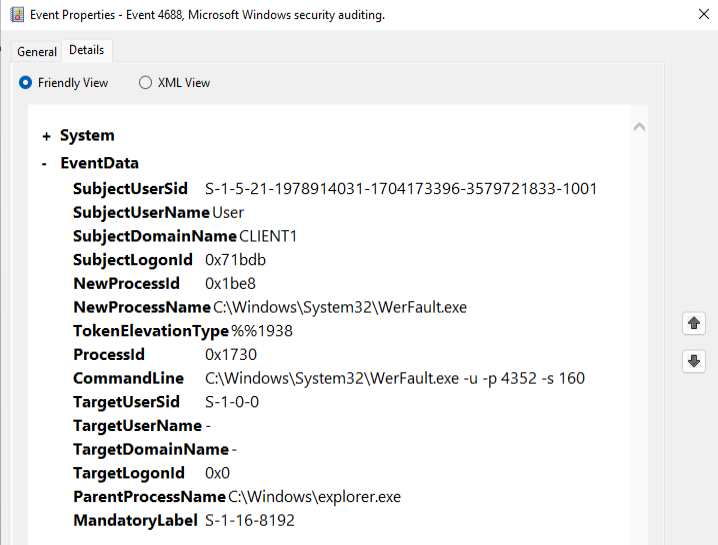
CS-DropSpawn_BOF
 gmh5225/cs-dropspawn_bof
CobaltStrike BOF to spawn Beacons using DLL Application Directory Hijacking
exploitationpayload-developmentpenetration-testing+2
gmh5225/cs-dropspawn_bofCobaltStrike BOF to spawn Beacons using DLL Application Directory Hijacking
 kasturixbm5/staged-dll-injection-smb-
Staged DLL injection proof-of-concept built in C using Win32 APIs — developed in an isolated lab environment for red team certification study (CRTO).
 r41n3rzuf477/cve-2023-41772
Windows privilege escalation exploit for CVE-2023-41772 (UIFuckUp) that elevates non-admin users to SYSTEM on Windows 10 (1809+) and 11 via a crafted…
 bhassani/eternalbluec
EternalBlue suite remade in C/C++ which includes: MS17-010 Exploit, EternalBlue vulnerability detector, DoublePulsar detector and DoublePulsar…
 3gstudent/cve-2017-8464-exp
Support x86 and x64
 telefonica/uac-a-mola
Modular framework for Windows UAC bypass attacks and mitigation, featuring DLL hijacking, fileless execution, and real-time monitoring to detect and…
 cylancevulnresearch/reflectivedllrefresher
Reflective DLL that scans process memory and unhooks loaded libraries to evade security software, with UPX, TLS injector, and Meterpreter integration.
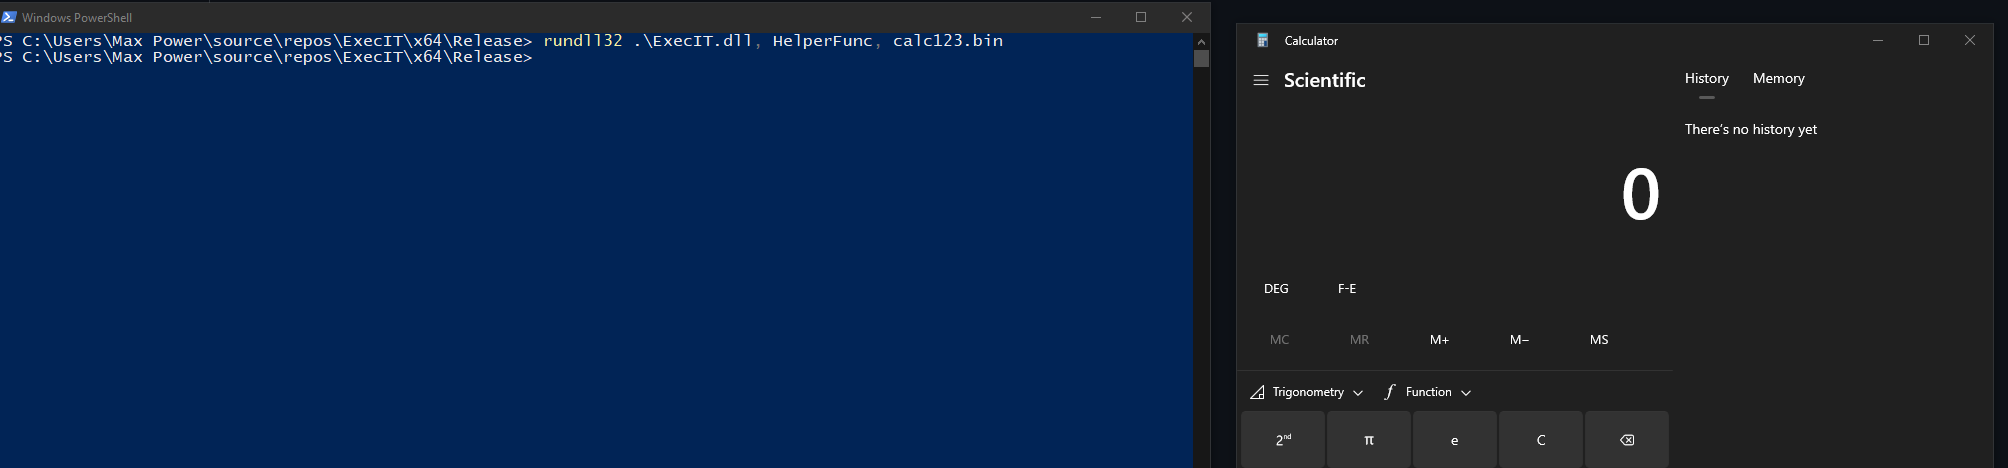 florylsk/execit
Execute shellcode files with rundll32
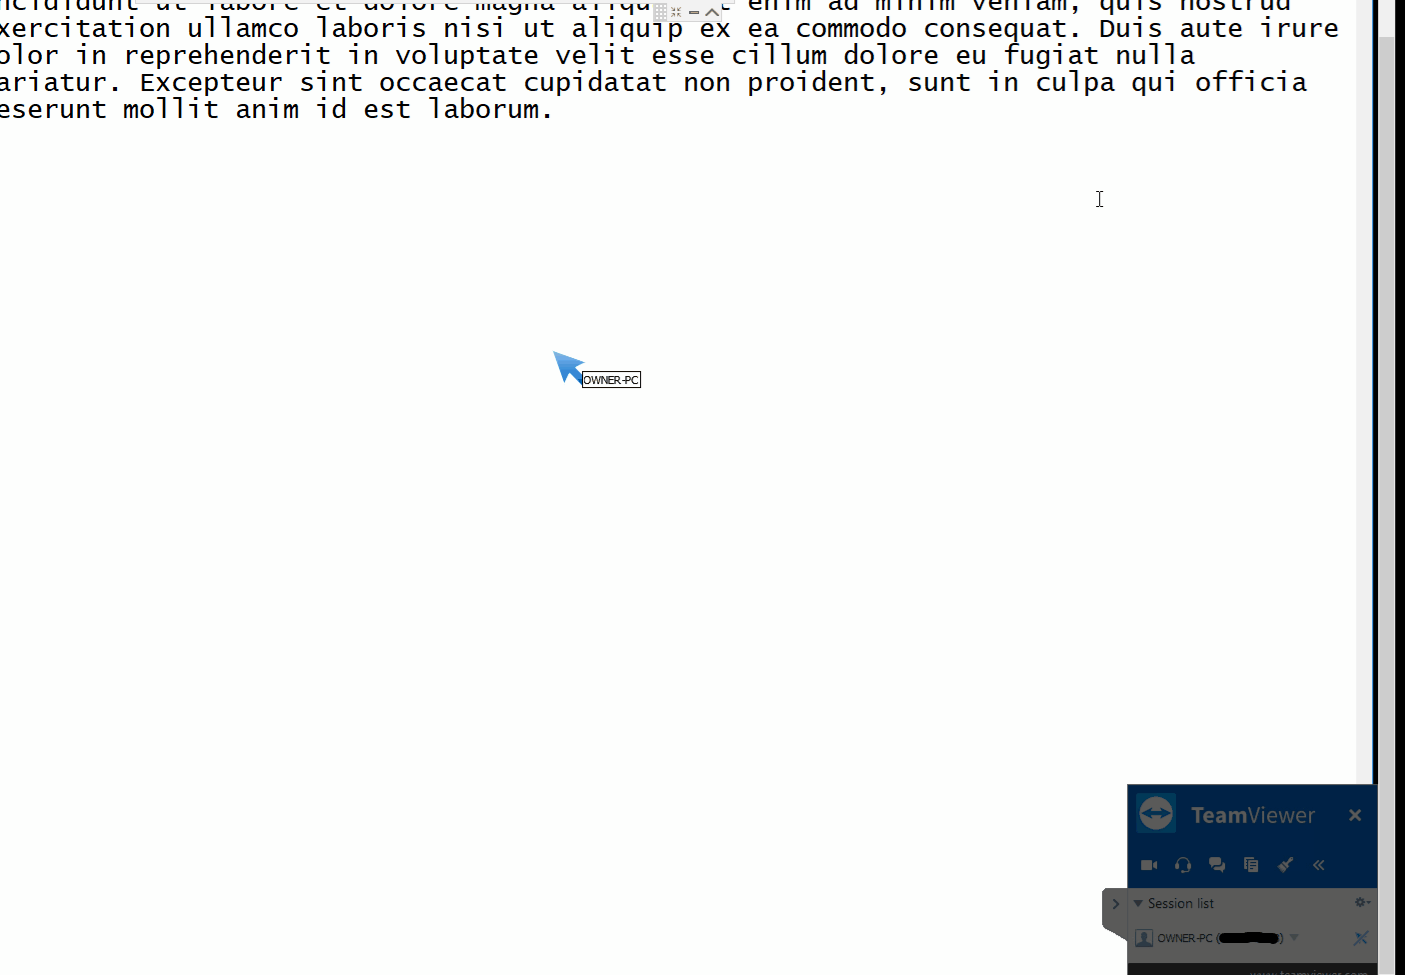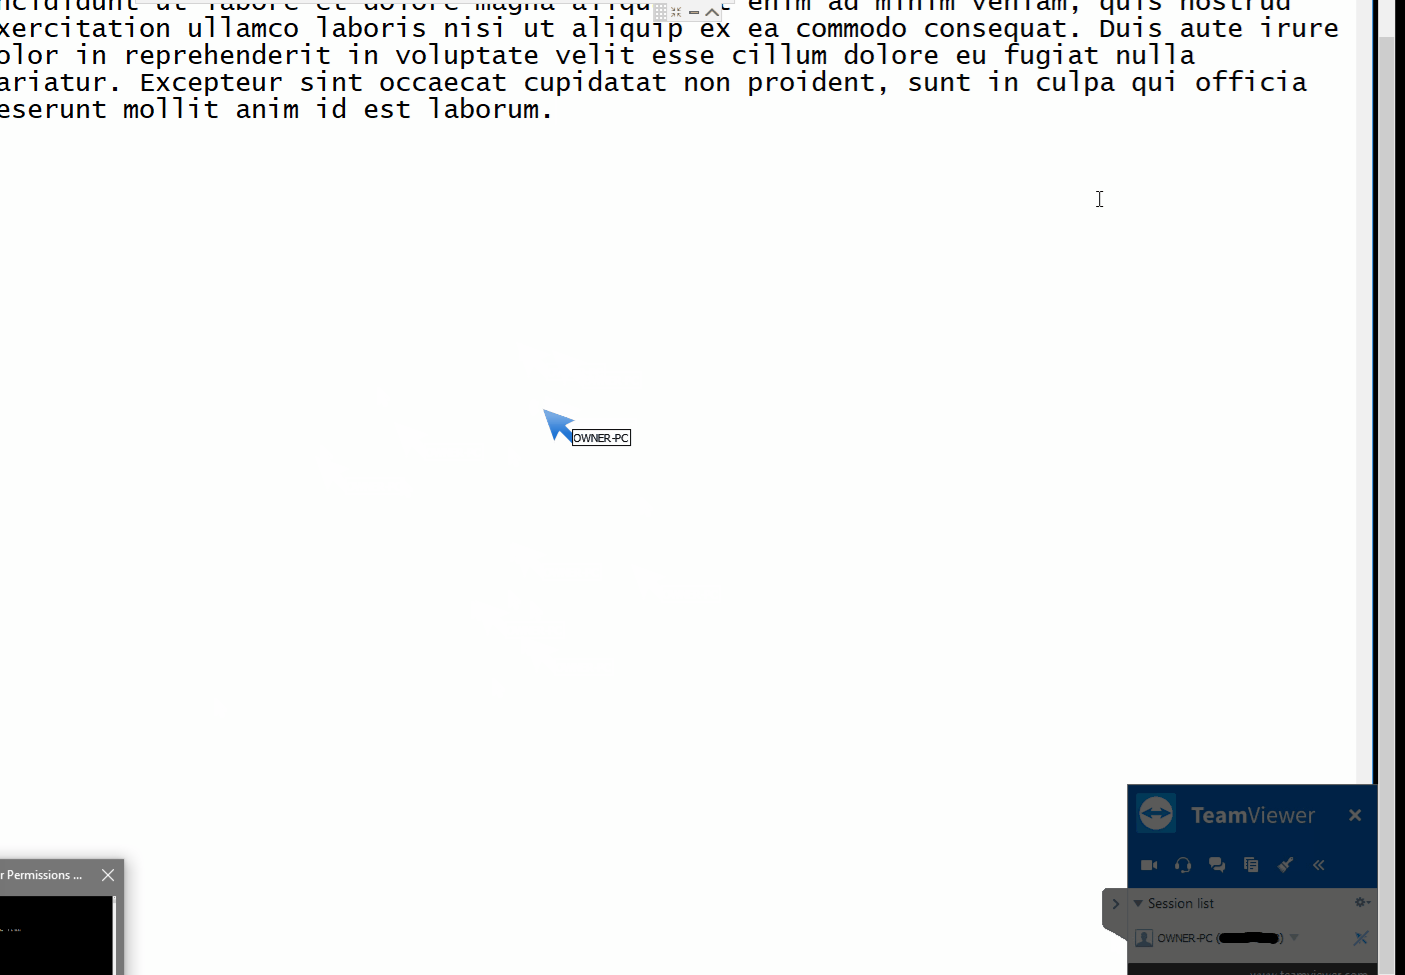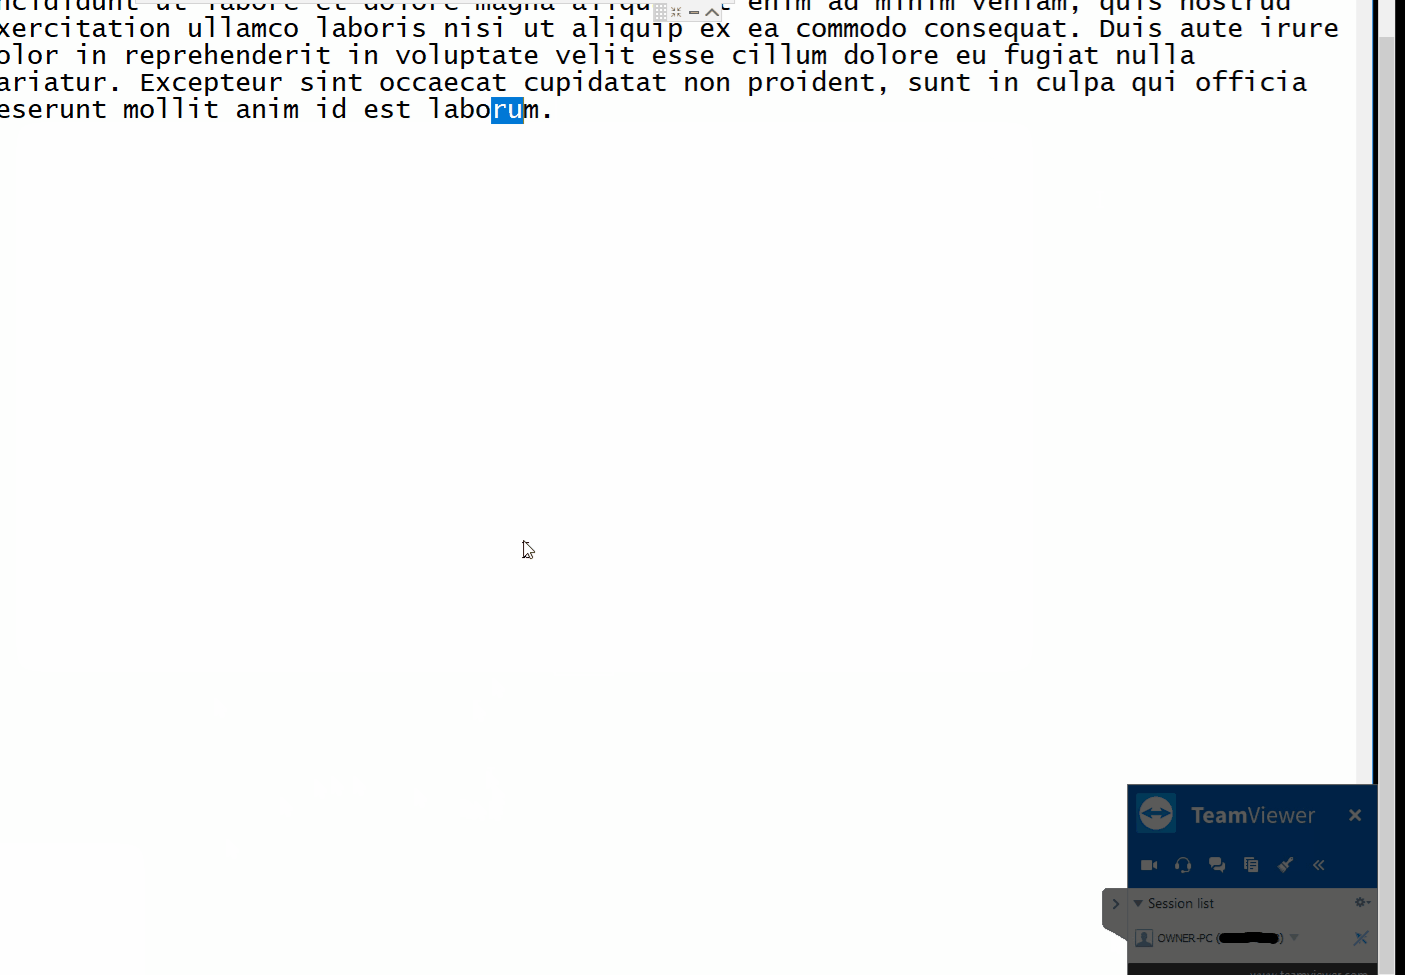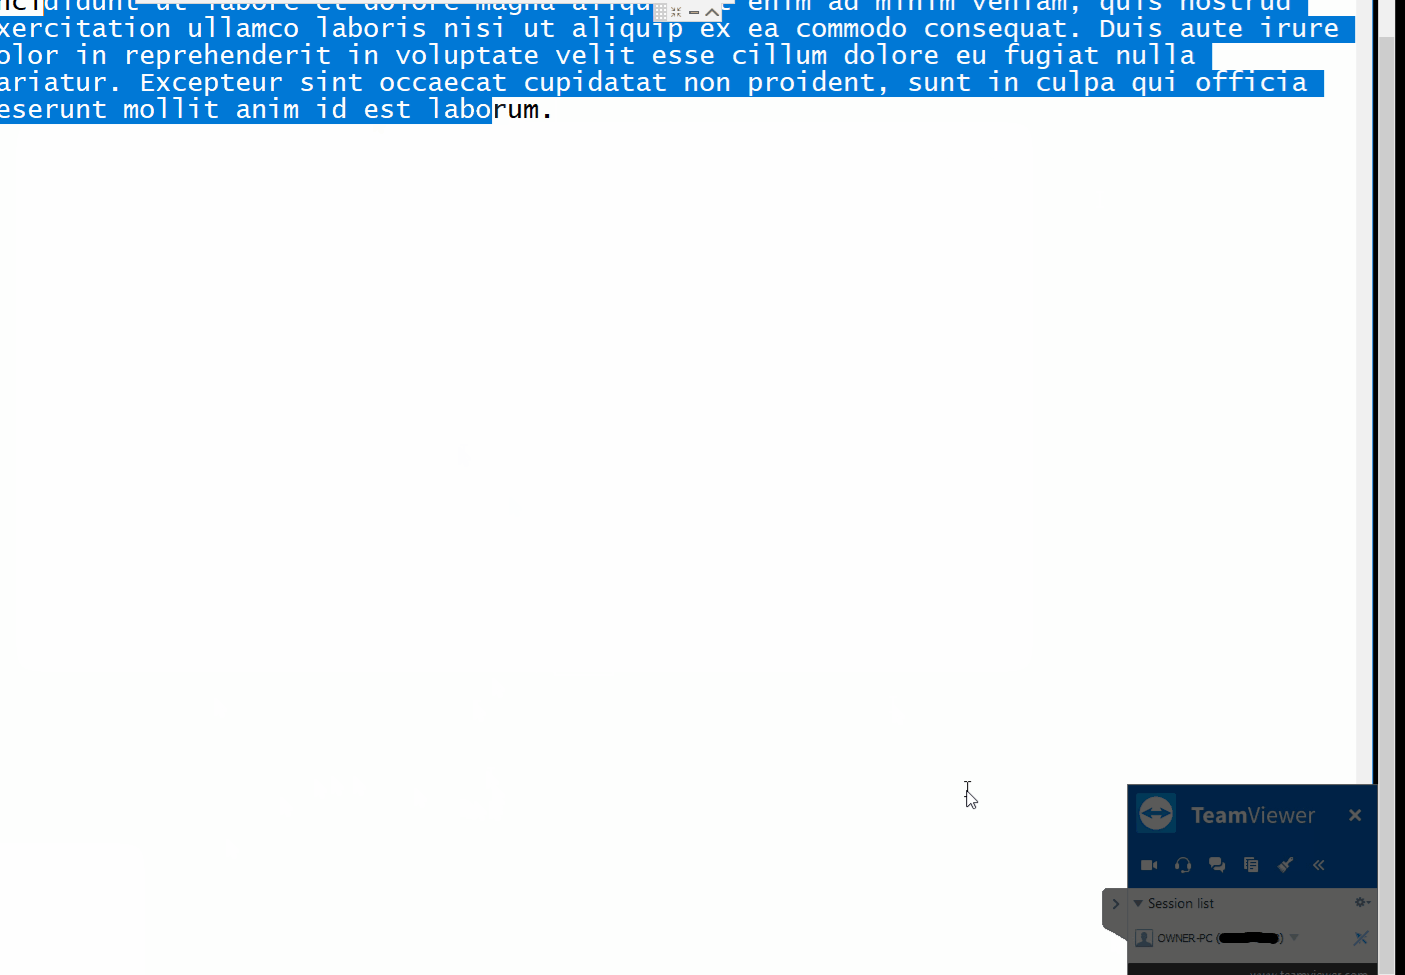 gellin/teamviewer_permissions_hook_v1
A proof of concept injectable C++ dll, that uses naked inline hooking and direct memory modification to change your TeamViewer permissions.
 tiagob0b/cve-2021-40444
Malicious DOCX generator exploiting CVE-2021-40444 (Microsoft Office Word RCE) with CAB-based DLL side-loading and CAB-less RAR/WSF attack chains for…
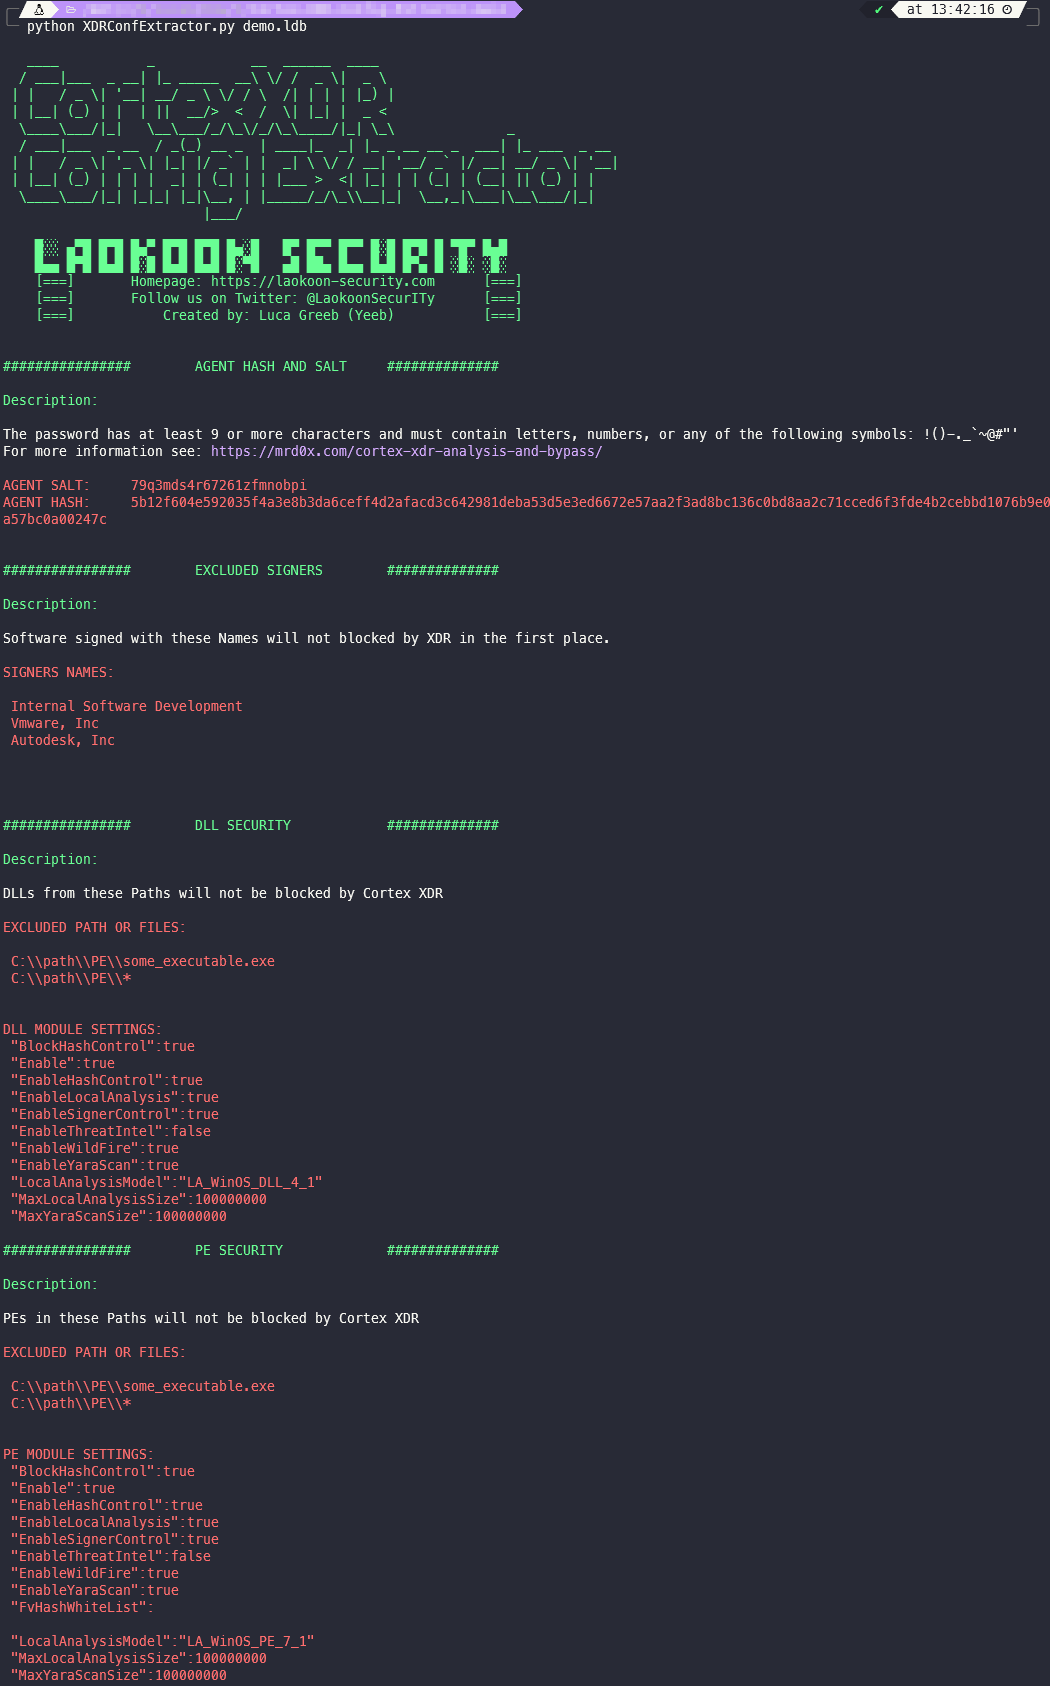 laokoon-security/cortex-xdr-config-extractor
Parses Cortex XDR agent database lock files to extract agent settings, uninstall password hash/salt, and security exclusions for red team assessments…
 breenmachine/rottenpotatong
New version of RottenPotato as a C++ DLL and standalone C++ binary - no need for meterpreter or other tools.
 ghostvectoracademy/dllhijackhunter
Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.
 0xrootpls/fritter
Polymorphic shellcode generator for in-memory execution of EXE, DLL, .NET, VBScript, and JScript with per-output and per-build randomization for…
 sailay1996/cdpsvclpe
Windows Local Privilege Escalation via CdpSvc service (Writeable SYSTEM path Dll Hijacking)
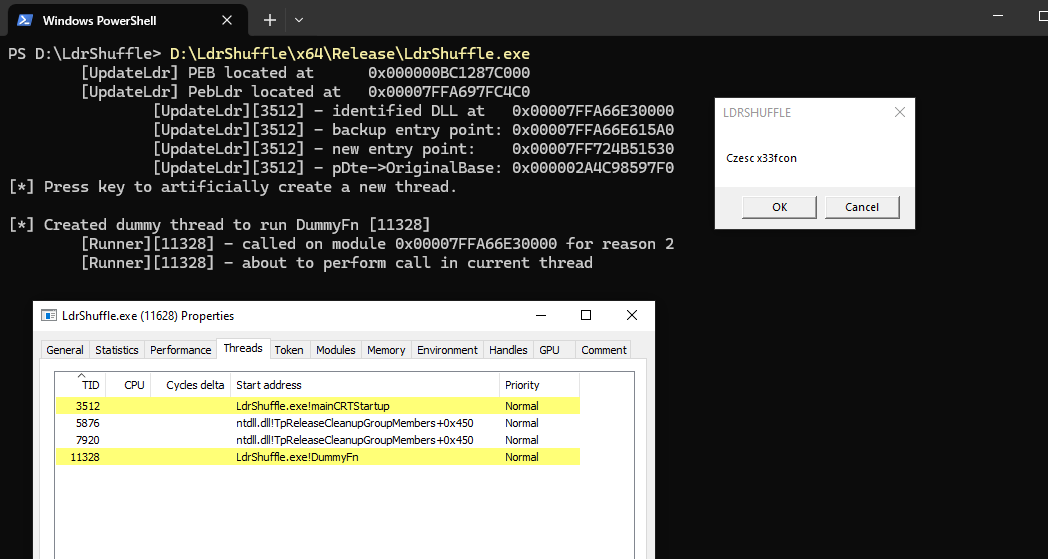 rwxstoned/ldrshuffle
Code execution/injection technique using DLL PEB module structure manipulation
 k8gege/cve-2021-40444
Exploit toolkit for CVE-2021-40444 MSHTML remote code execution, featuring DLL payload generation, Office document crafting, and lateral movement…
 dust-life/cve-2019-18935-memshell
C++ memshell DLL generator for CVE-2019-18935, enabling in-memory web shell deployment via Telerik UI deserialization with Assembly.Load and IJW…