
CVE-2024-48990-PoC-Testing
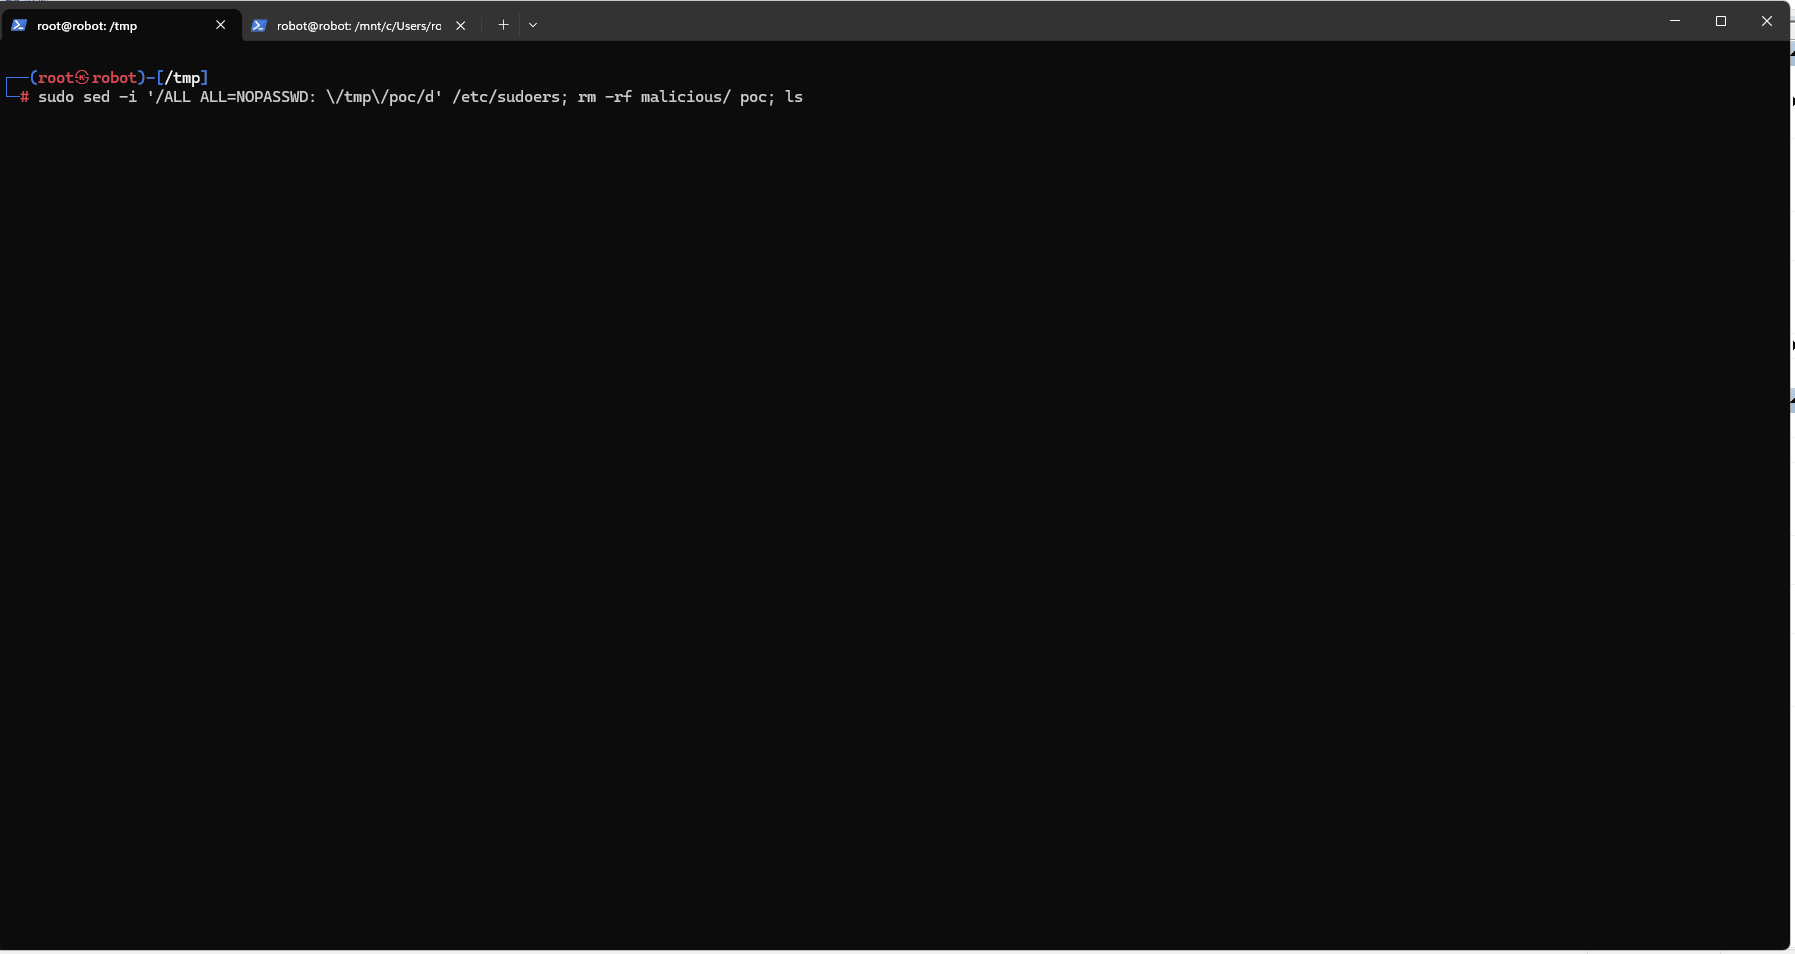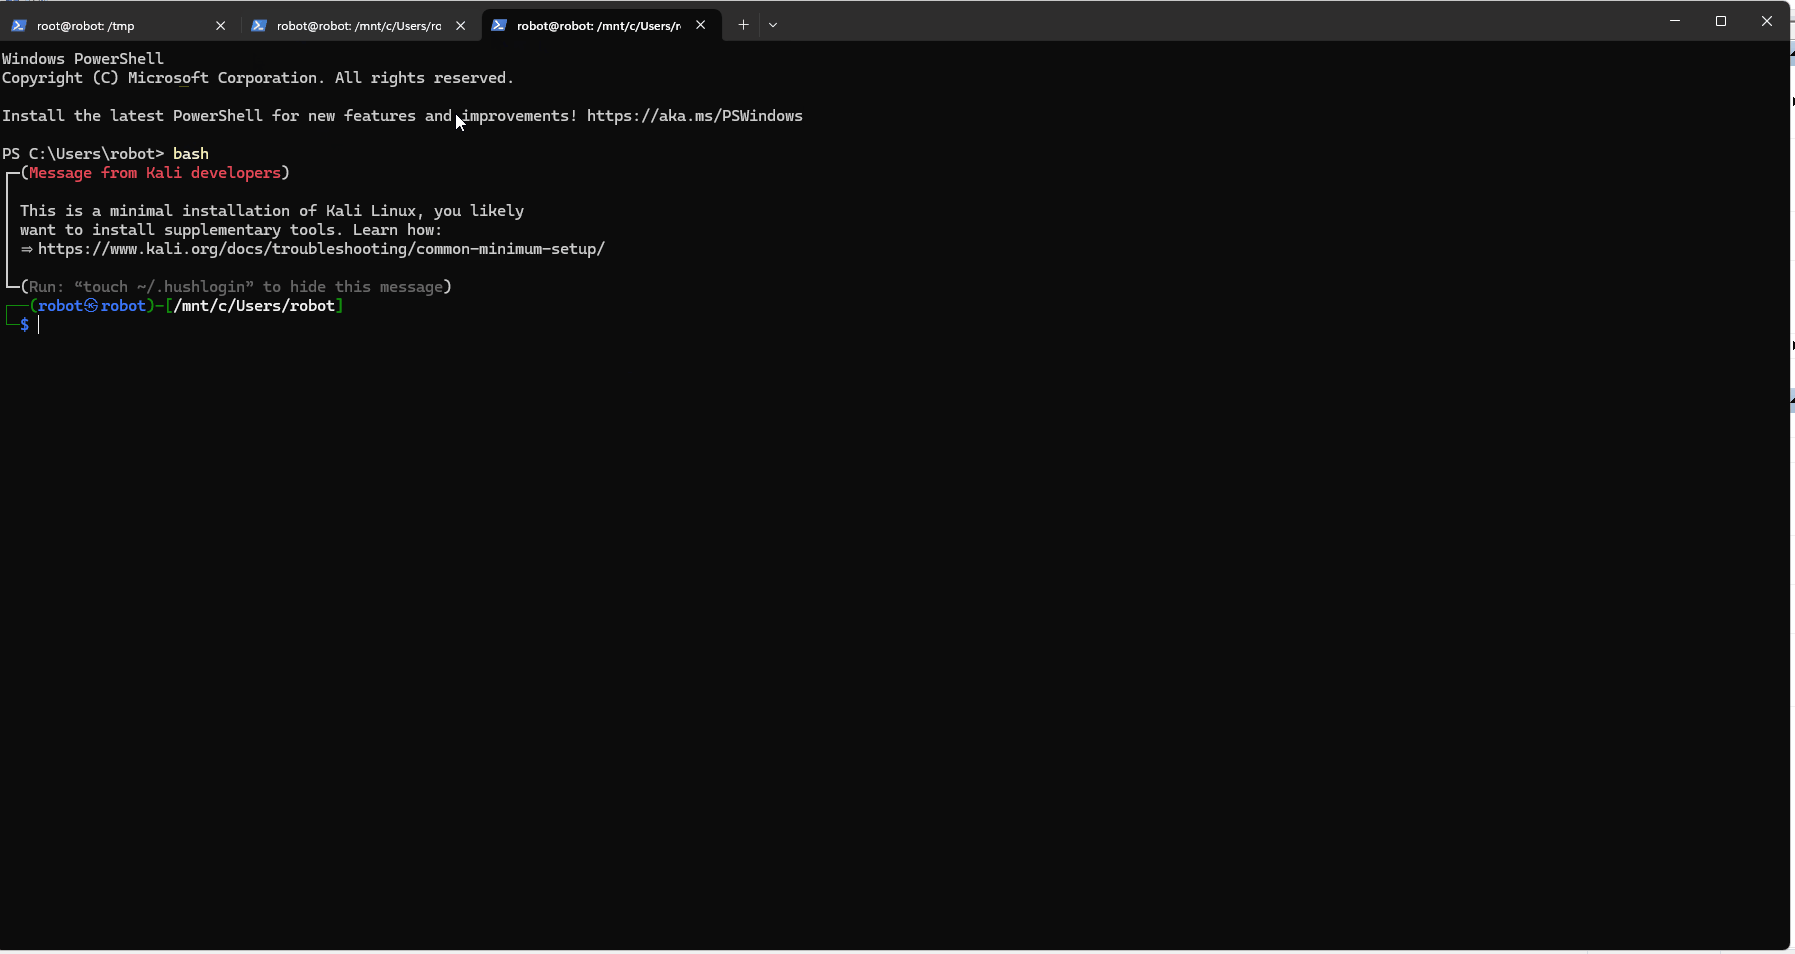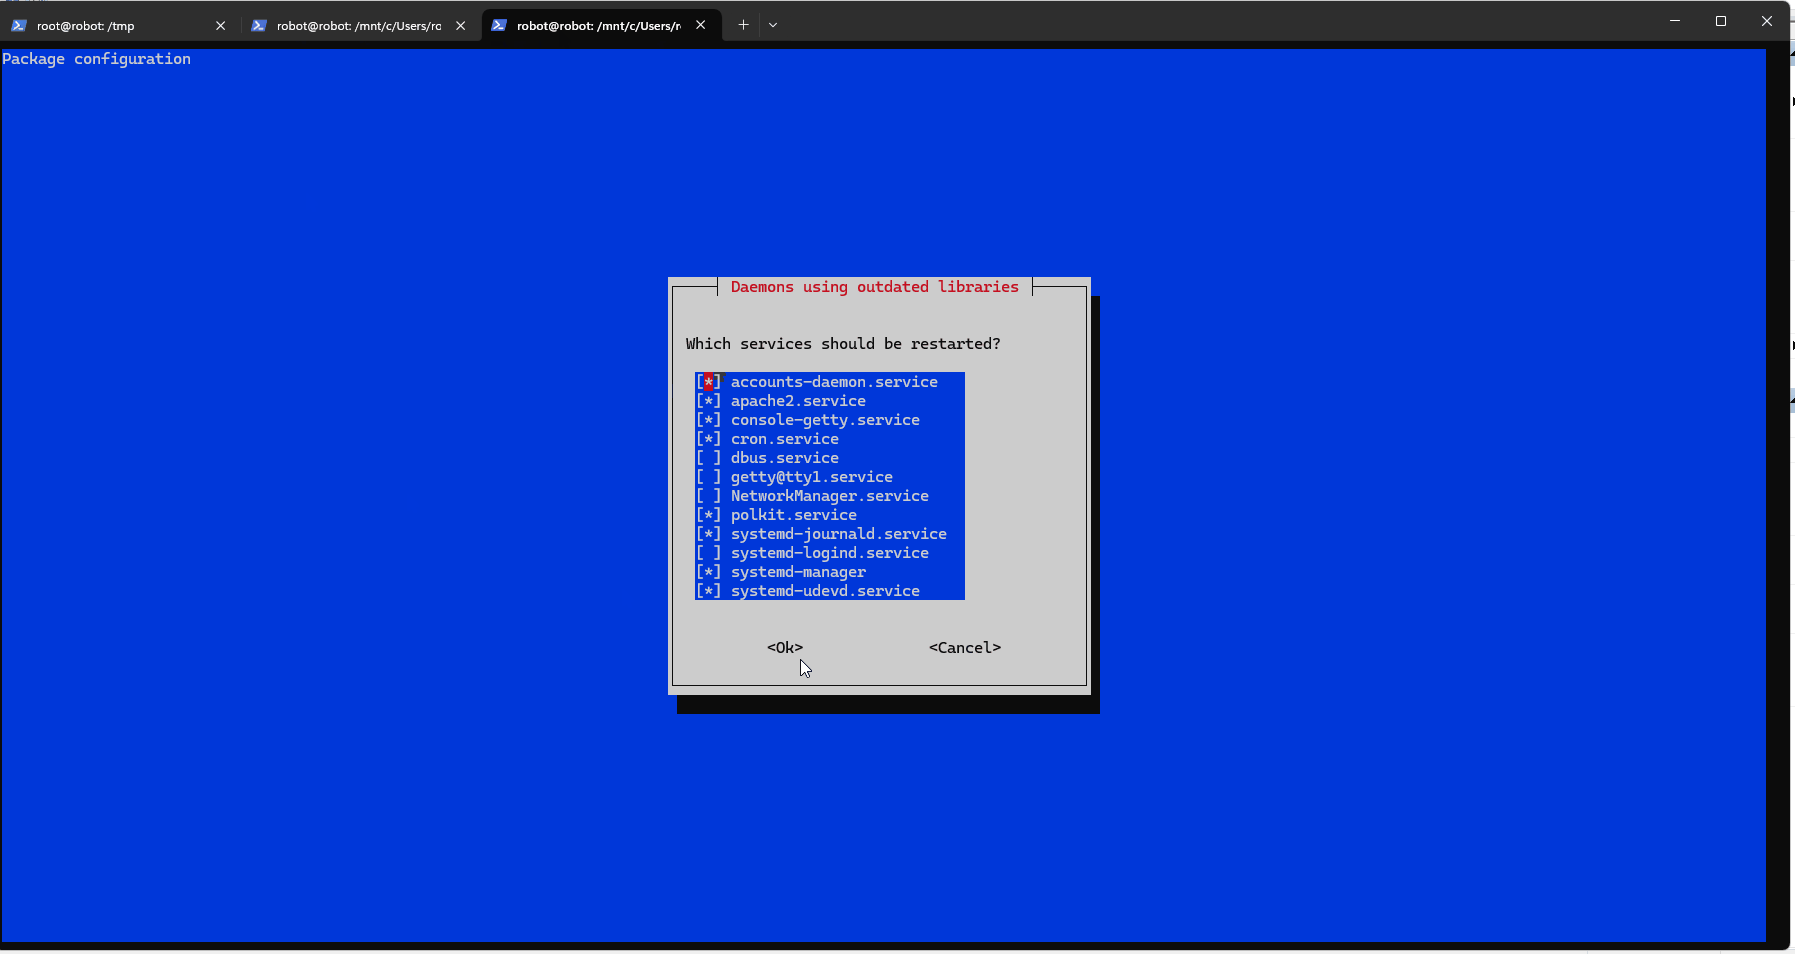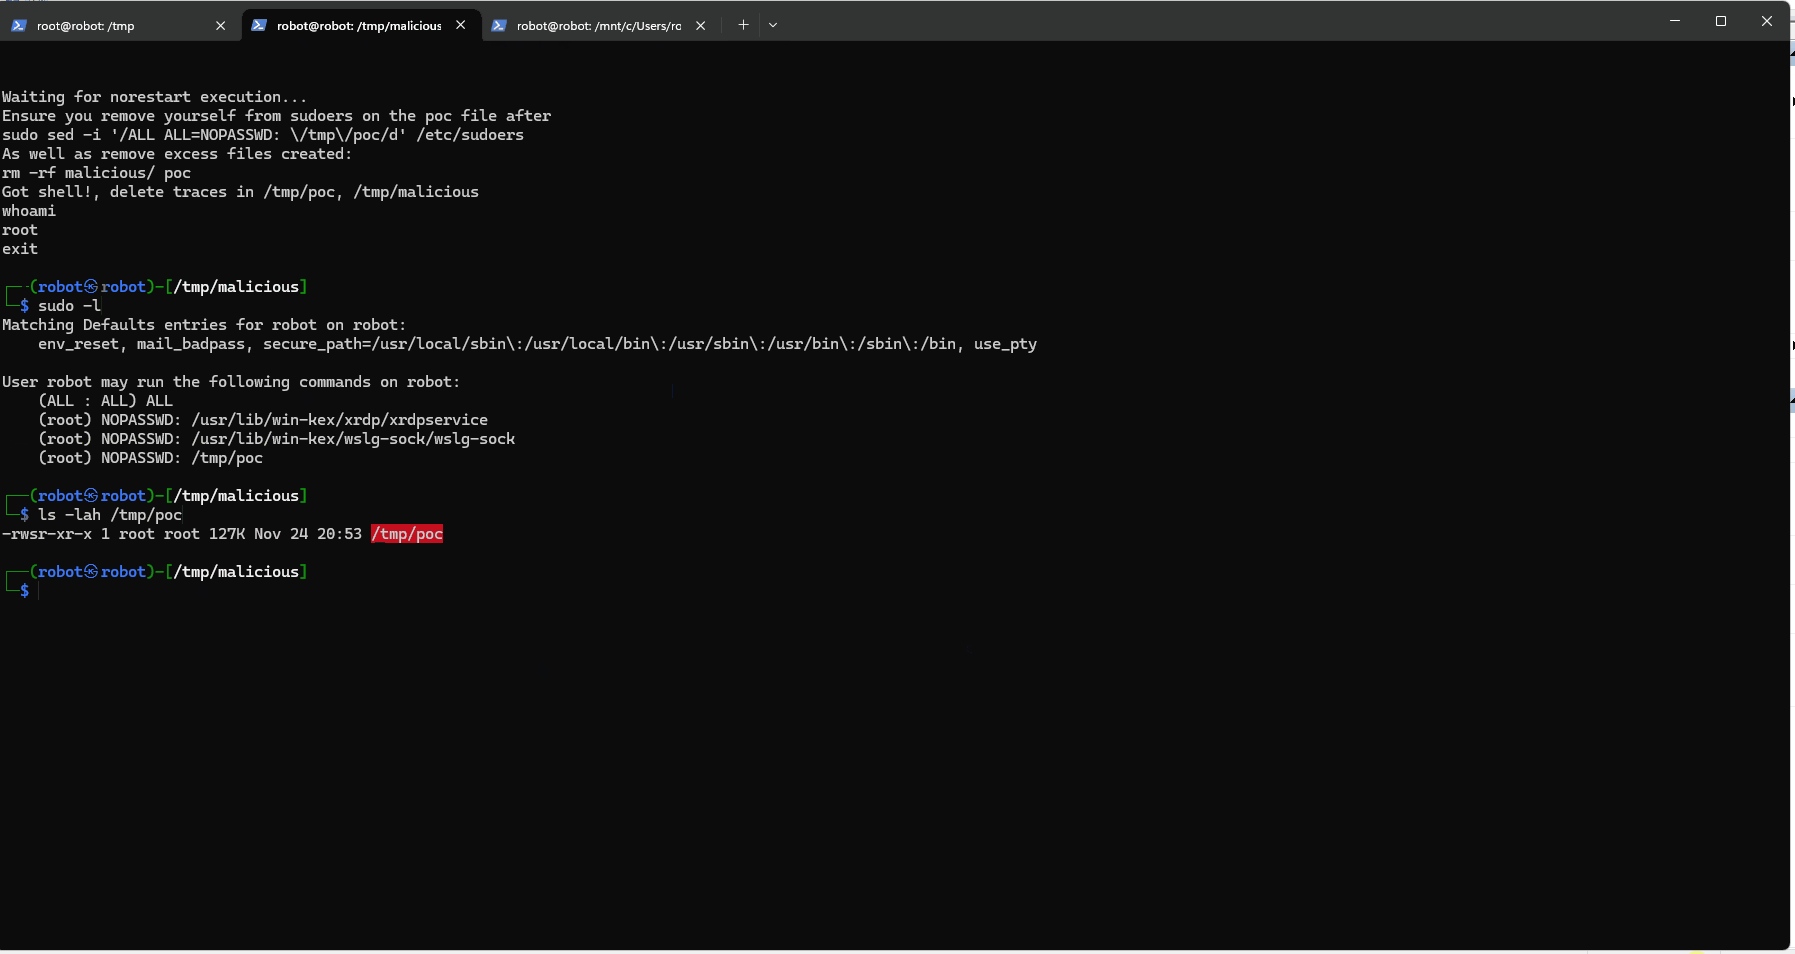
 pentestfunctions/cve-2024-48990-poc-testing
Testing POC for use cases
educationexploitationlabs-practice+3
26
pentestfunctions/cve-2024-48990-poc-testingTesting POC for use cases
 404-src/cve-2026-34486
Exploit for Apache Tomcat EncryptInterceptor bypass leading to unauthenticated RCE via Java deserialization on port 4000. Includes lab setup,…
 george0papasotiriou/cve-2025-15556-notepad-wingup-updater-rce
Proof-of-concept exploit for CVE-2025-15556, demonstrating update integrity bypass in Notepad++ WinGUp updater via MITM proxy or DNS spoofing,…
 sparrowhawk1113/exploit-for-cve-2024-46987
Exploit for CVE-2024-46987
 bytereaper77/cve-2025-7840
Proof‑of‑concept exploit for CVE‑2025‑7840 that injects malicious payloads into the Firstname parameter of a reservation form to trigger XSS
 puben/cve-2025-24011-poc
Umbraco User Enum - CVE-2025-24011 PoC
 pentestgeek/phishing-frenzy
Ruby on Rails Phishing Framework
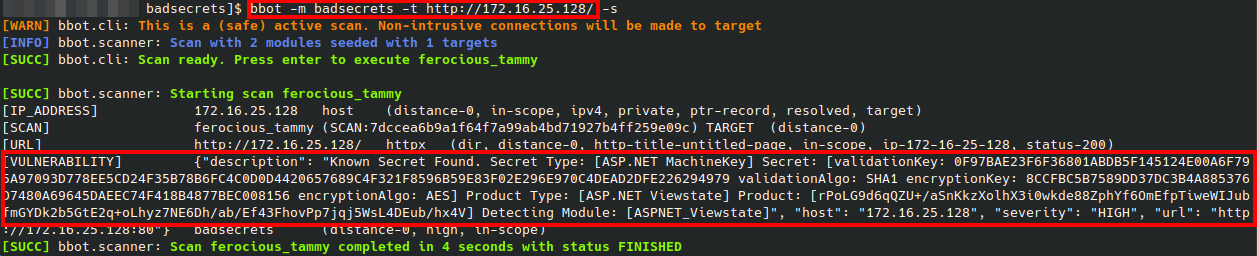 blacklanternsecurity/badsecrets
A library for detecting known secrets across many web frameworks
 mpgn/rails-doubletap-rce
RCE on Rails 5.2.2 using a path traversal (CVE-2019-5418) and a deserialization of Ruby objects (CVE-2019-5420)
 0x00-0x00/cve-2016-2098
Exploits Ruby on Rails Action Pack remote code execution (CVE-2016-2098) by abusing unrestricted render() to run arbitrary shell commands through a…
 0x00-0x00/cve-2015-3224
Modification of Metasploit module for RCE in Ruby-On-Rails Console CVE-2015-3224
 cyberdefenseinstitute/poc_cve-2016-2098_rails42
A PoC of CVE-2016-2098 (rails4.2.5.1 / view render)
 shinthink/cve-2026-66066
CVE-2026-66066 — KindaRails2Shell: Rails Active Storage/libvips Arbitrary File Read → RCE. MATLAB/HDF5 dual-identity file → SECRET_KEY_BASE theft →…
 omarkurt/cve-2014-0130
cve-2014-0130 rails directory traversal vuln
 mpgn/cve-2018-3760
Rails Asset Pipeline Directory Traversal Vulnerability
 0xeval/cve-2015-3224
Ruby on Rails Web Console (v2) Whitelist Bypass Code Execution implementation in Python
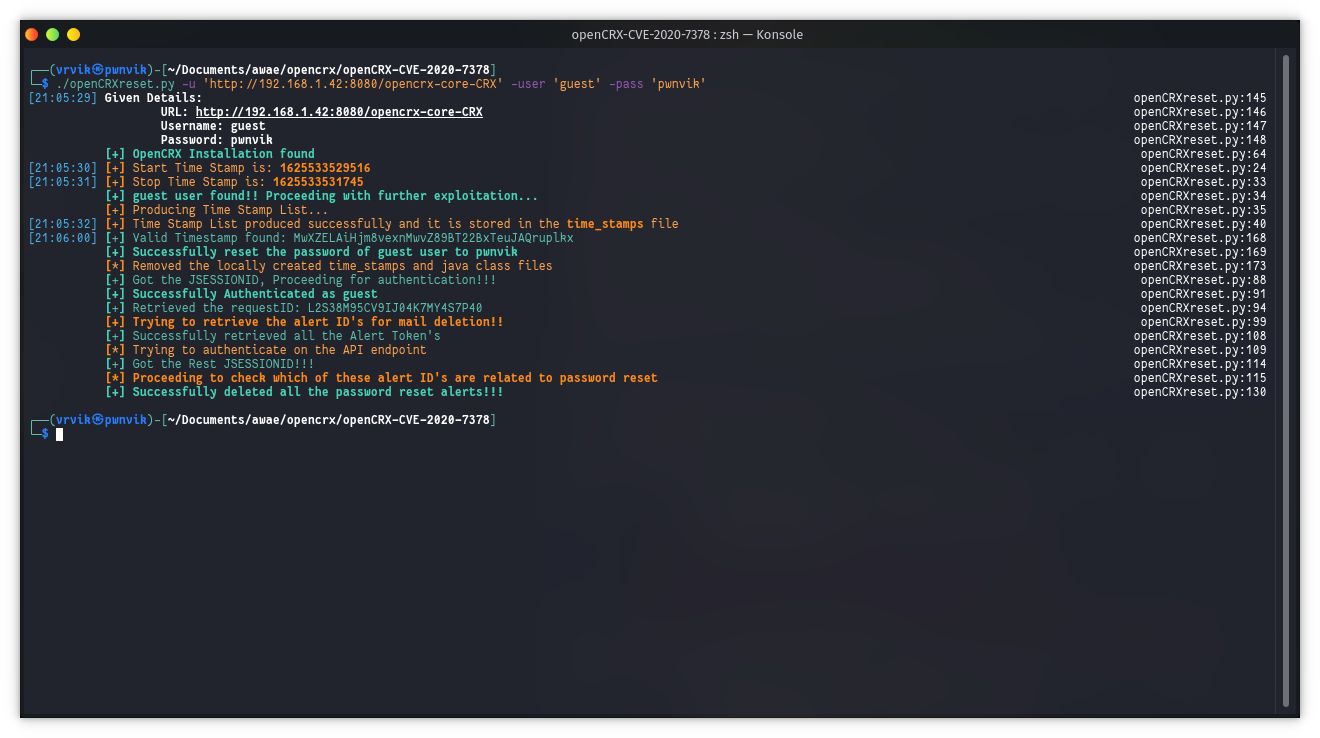 ruthvikvegunta/opencrx-cve-2020-7378
Exploits Password Reset Vulnerability in OpenCRX, CVE-2020-7378. Also maintains Stealth by deleting all the password reset mails created by the script
 omaratallahh/cve-2023-23138
short view of ruby on rails properties misconfiguration