
Burp_CVE-2025-31324
 blueowl-overlord/burp_cve-2025-31324
Python-based Burp Suite extension is designed to detect the presence of CVE-2025-31324
api-security-testingexploitationpenetration-testing+3
blueowl-overlord/burp_cve-2025-31324Python-based Burp Suite extension is designed to detect the presence of CVE-2025-31324
 aureum01/cve-2023-23752
A bash automation that exploits the vulnerable endpoints for the Joomla! API 4.0 - 4.2.7
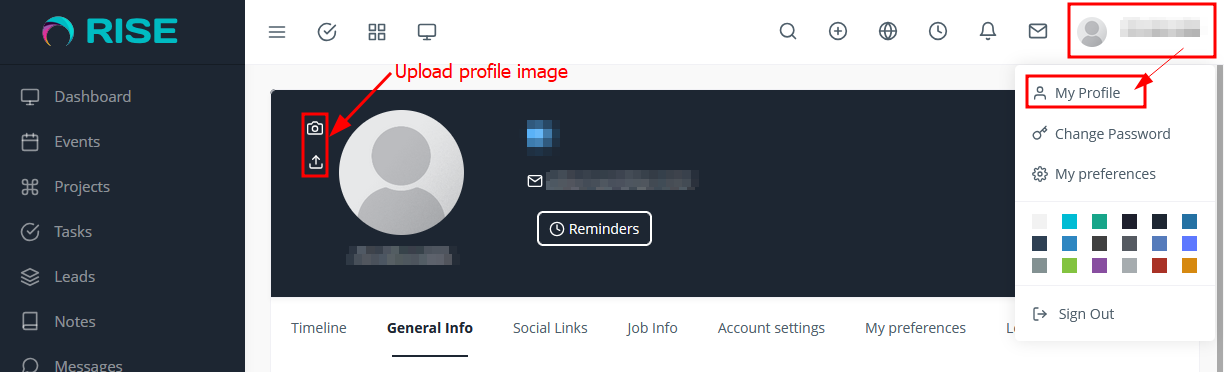 l4zyfox/rise-ultimate_project_manager_e_crm
CVE-2025-3855 - RISE Ultimate Project Manager - IDOR
 shoucheng3/perwendel__spark_cve-2018-9159_2-7-1
Lightweight Java 8 web framework with routing, filters, and static file serving. Includes security advisory for older versions and CRUD API examples.
 shoucheng3/perwendel__spark_cve-2018-9159_2_7_2_fixed
Lightweight Java 8 web framework for building REST APIs and web applications, with built-in routing, static file serving, and template engine support.
 palmtreeforest/codepath_week_7-8
CodePath Assignment for Weeks 7 & 8: CVE-2017-14719, CVE-2019-9787 & Unauthenticated Page/Post Content Modification via REST API
 t0xodile-swig/http3-adapter
Burp Suite extension that intercepts requests and sends them over HTTP/3, converting responses back for Burp, with support for kettled requests and…
 kamalx06/xxeripper
Black-box XXE scanner detecting in-band, error-based, and blind out-of-band injection via statistical baselining, parser fingerprinting, and OOB…
 wkeeling/selenium-wire
Extends Selenium's Python bindings to give you the ability to inspect requests made by the browser.
 themalwareguardian/brokeclaudia
CVE-2025-41090 (brokeCLAUDIA): Broken access control in microCLAUDIA, the anti-ransomware platform by CCN-CERT.
 google/martian
Martian is a library for building custom HTTP/S proxies
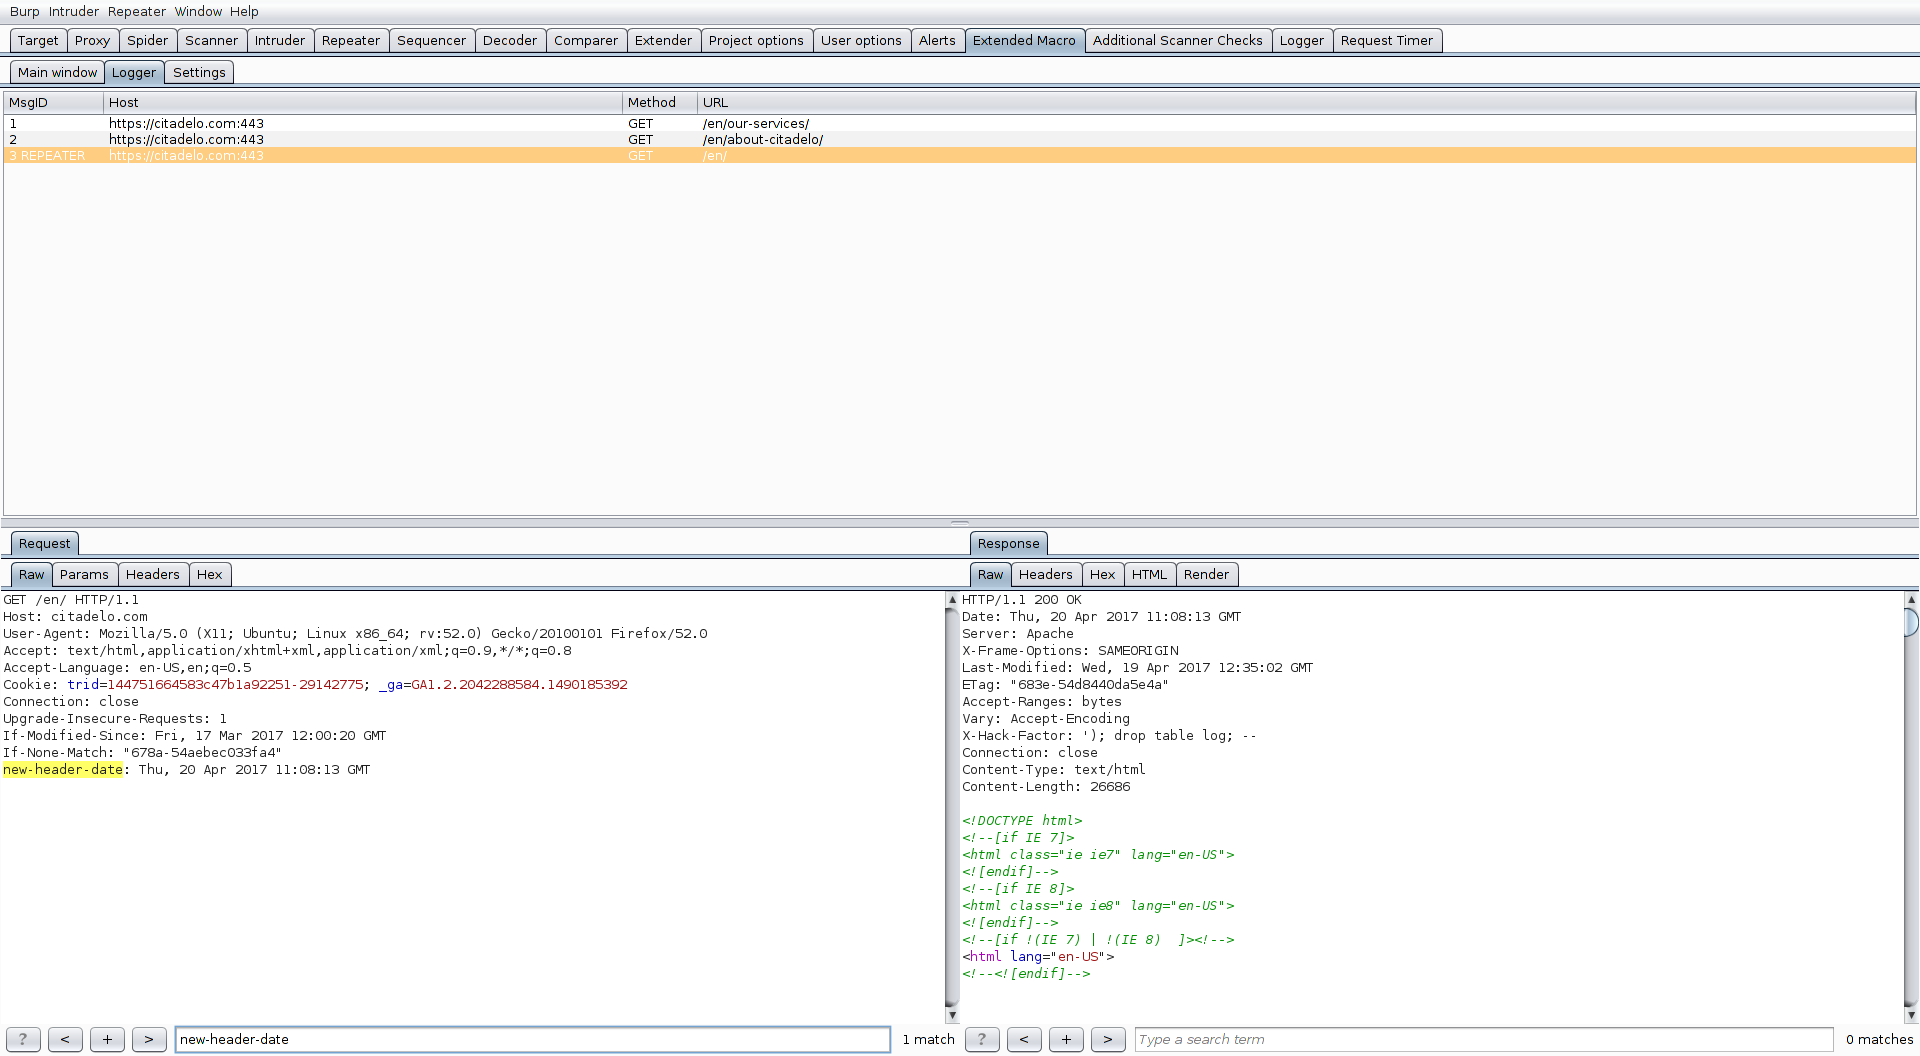 fruh/extendedmacro
ExtendedMacro - BurpSuite plugin providing extended macro functionality
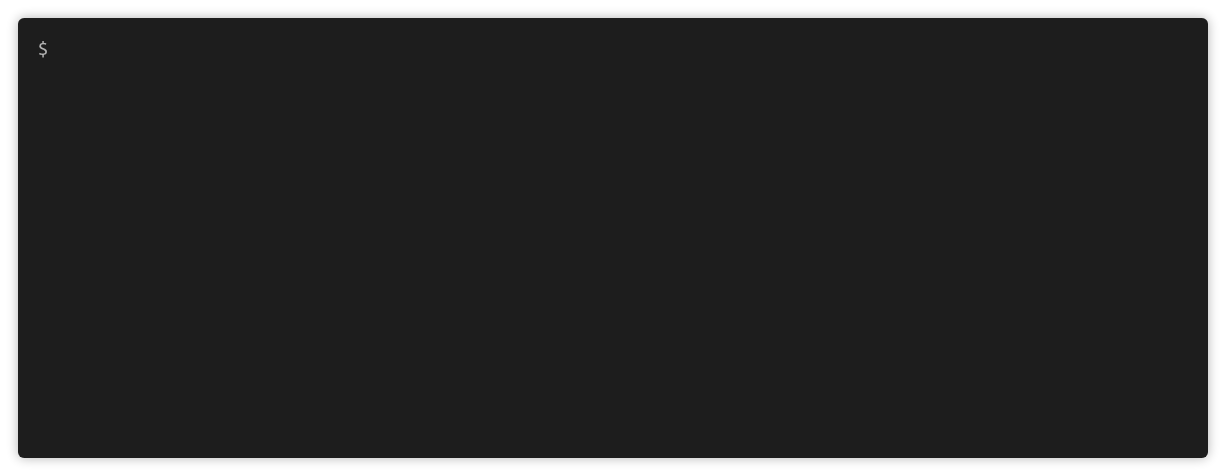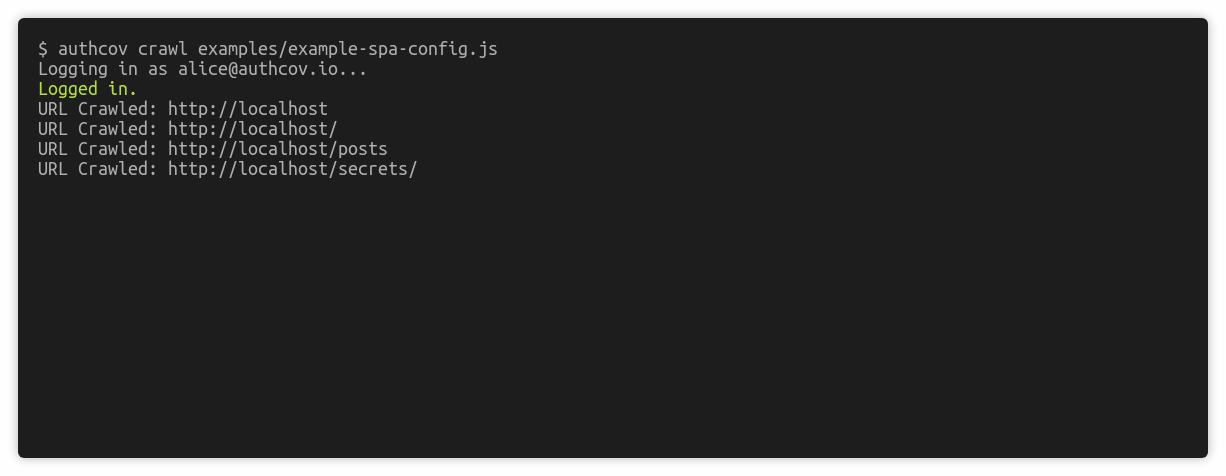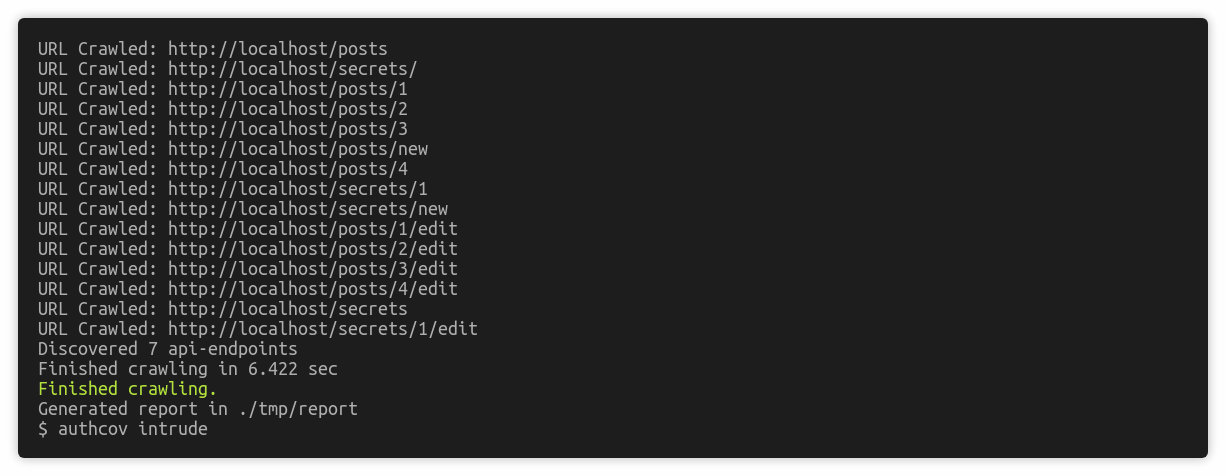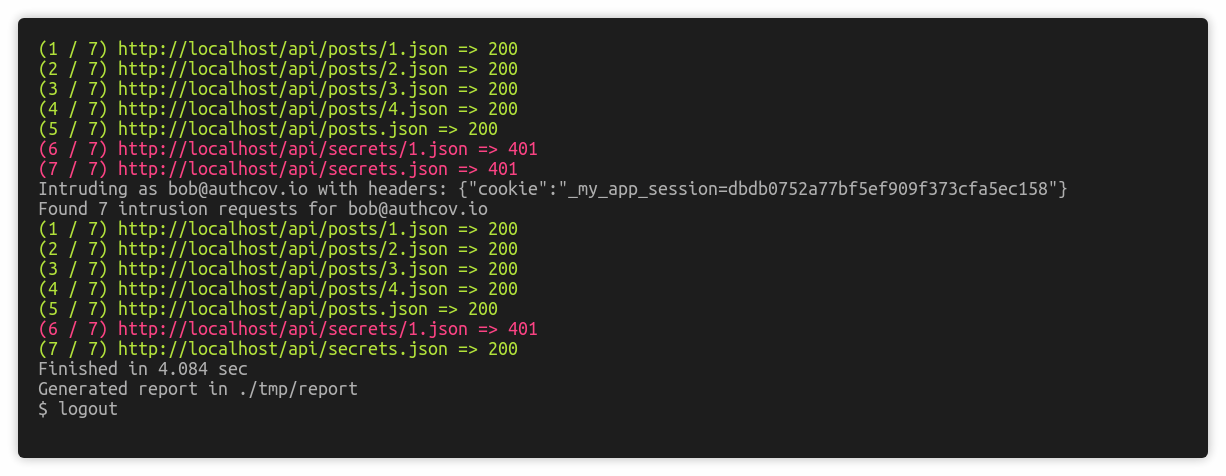 authcov/authcov
Web app authorisation coverage scanning
 sh1yo/request_smuggler
Http request smuggling vulnerability scanner
 h2non/toxy
Hackable HTTP proxy for resiliency testing and simulated network conditions
 rapid7/hackazon
A modern vulnerable web app
 openstack-archive/syntribos
Python API security testing tool from OpenStack Security Group
 vmware-archive/burp-rest-api
REST/JSON API to the Burp Suite security tool.