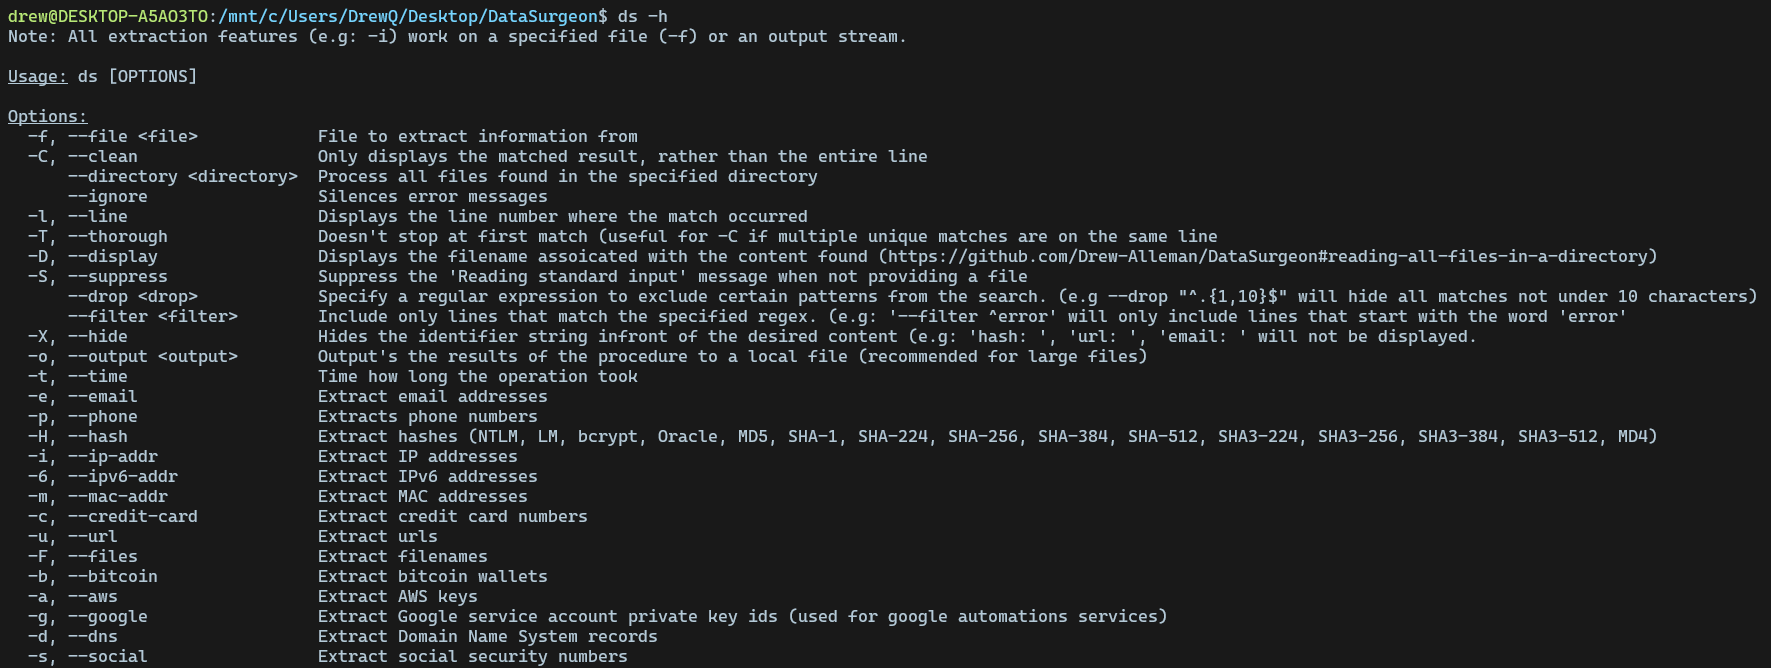
DataSurgeon
 drew-alleman/datasurgeon
Quickly Extracts IP's, Email Addresses, Hashes, Files, Credit Cards, Social Security Numbers and a lot More From Text
ctfdata-exfiltrationforensics+6
900
drew-alleman/datasurgeonQuickly Extracts IP's, Email Addresses, Hashes, Files, Credit Cards, Social Security Numbers and a lot More From Text
 viralmaniar/passhunt
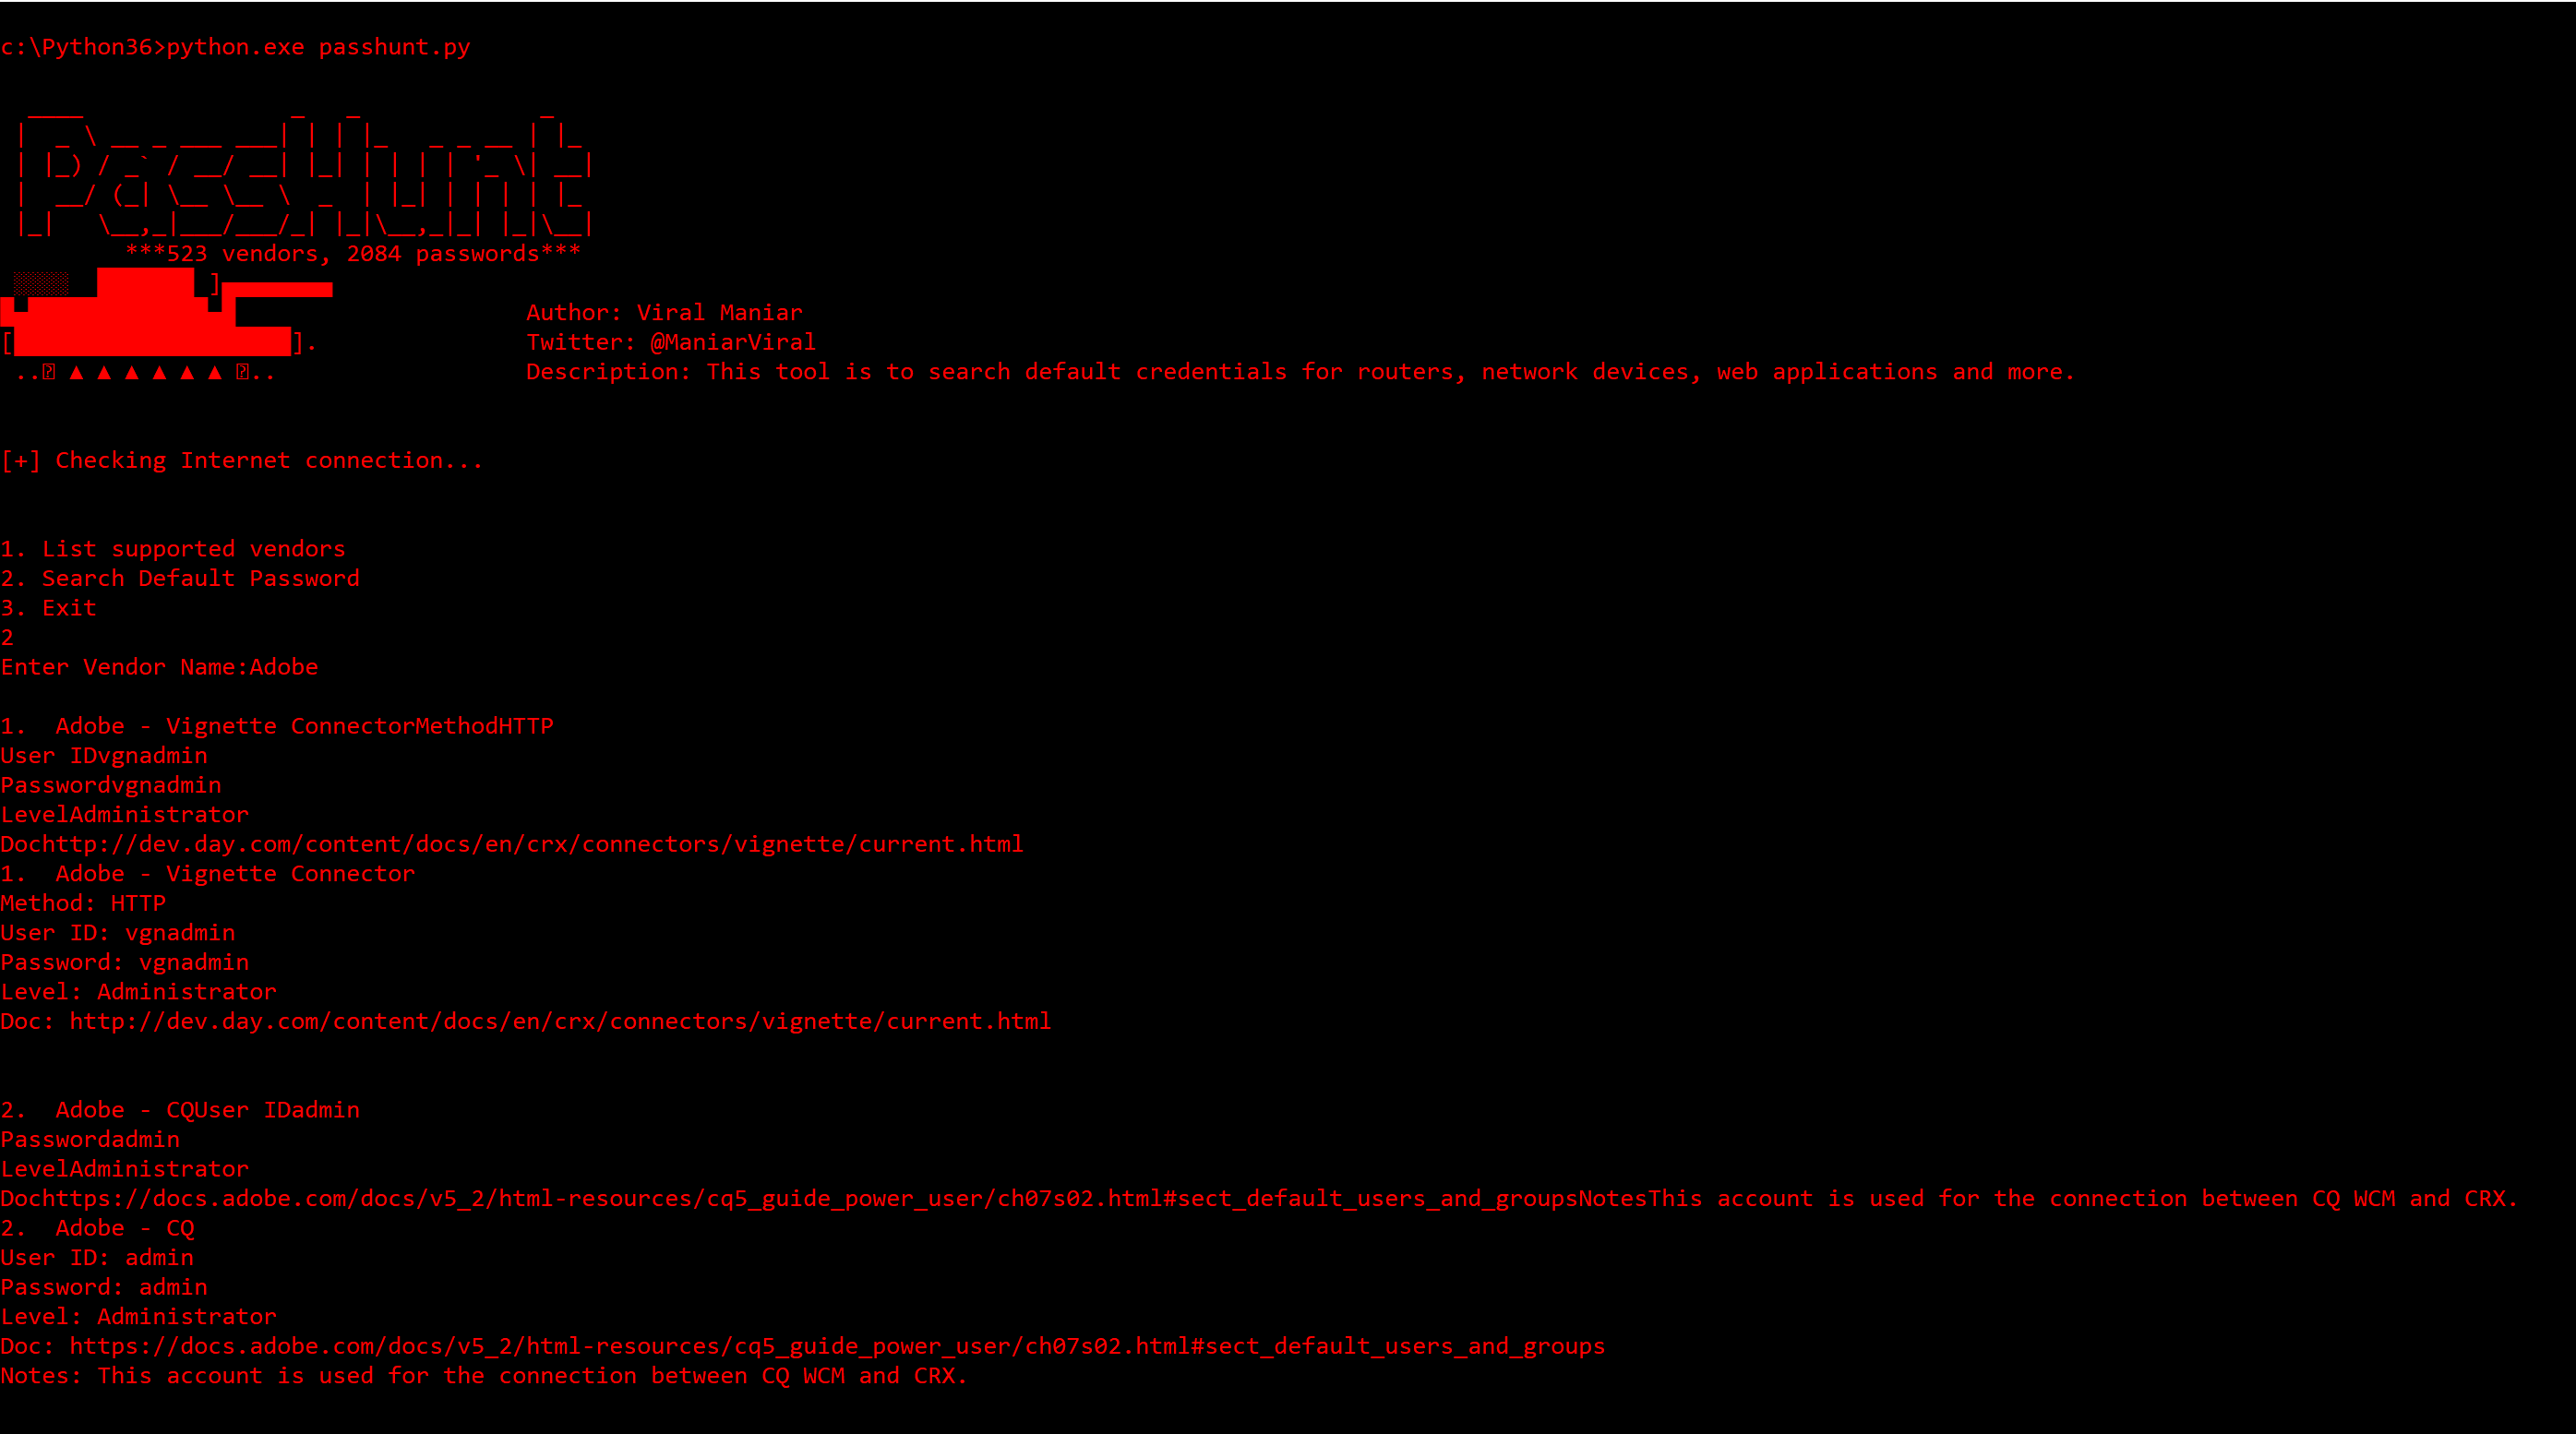
Passhunt is a simple tool for searching of default credentials for network devices, web applications and more. Search through 523 vendors and their…

 puppetm4ster/koyane-framework
Modular wordlist generation, editing, analysis, and discovery toolkit for password cracking, fuzzing, and ethical security testing. Supports…
 edoardottt/awesome-hacker-search-engines
A curated list of awesome search engines useful during Penetration testing, Vulnerability assessments, Red/Blue Team operations, Bug Bounty and more
 oritera/cairn
LLM-driven state-space search engine for autonomous penetration testing, CTF solving, and vulnerability research. Uses blackboard architecture with…
 j3r1ch0123/cve-2024-40422
Found this on exploit-db, decided to make my own for practice. This exploit will search out the passwd file and print the contents on a vulnerable…
 ensimag-security/cve-2018-10933
Academic exploit implementation for CVE-2018-10933, a libssh authentication bypass vulnerability, with a detailed report and Shodan search…
 ihebski/a-red-teamer-diaries
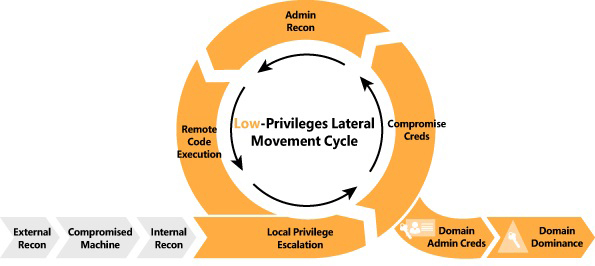
RedTeam/Pentest notes and experiments tested on several infrastructures related to professional engagements.
 masterking32/masterhttprelayvpn
Domain-fronted HTTP/SOCKS5 proxy tunneling traffic through Google Apps Script with MITM TLS interception, HTTP/1-2 multiplexing, and DPI evasion.
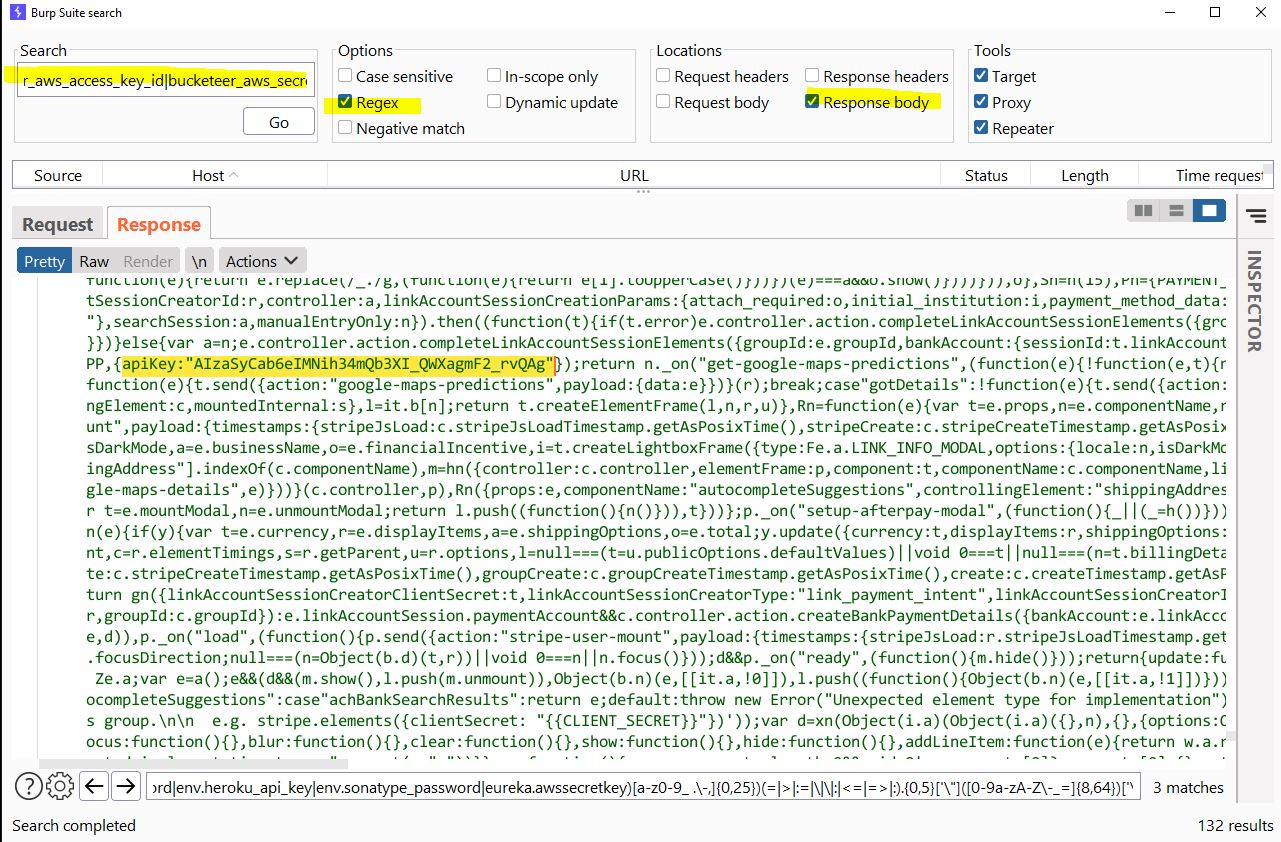 h4x0r-dz/leaked-credentials
how to look for Leaked Credentials !
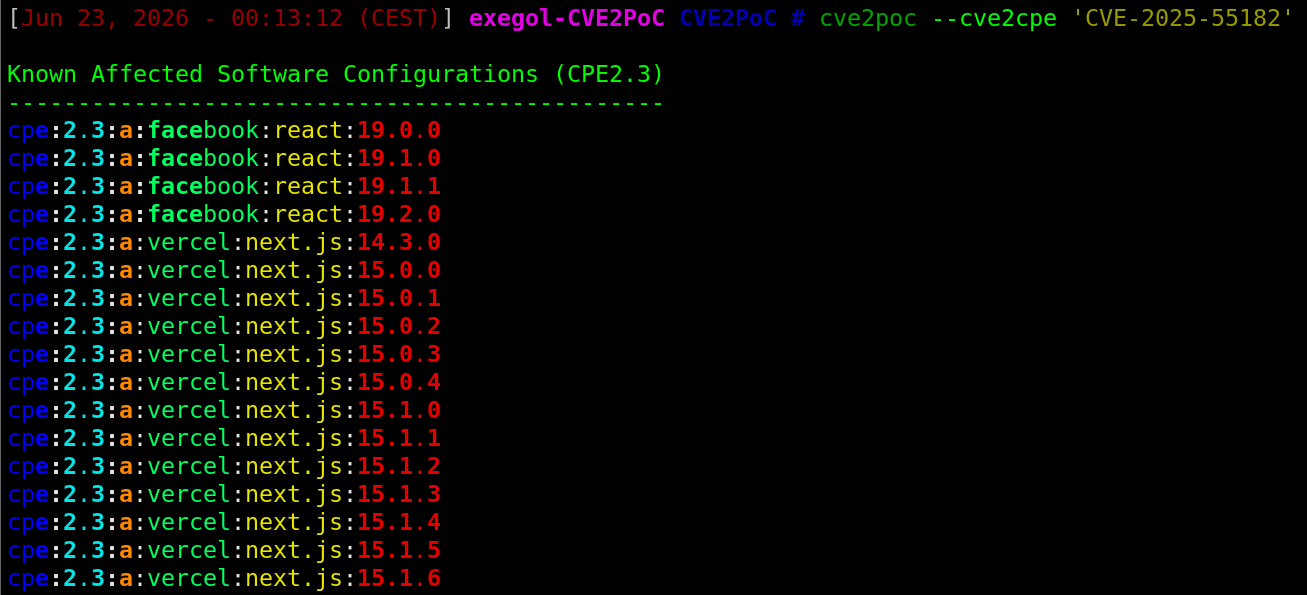 0liverflow/cve2poc
CVE2PoC is a tool that helps penetration testers, bug hunters, and security researchers quickly find public exploits or PoCs related to a CVE ID
 t0kx/exploit-cve-2015-1427
Elasticsearch 1.4.0 < 1.4.2 Remote Code Execution exploit and vulnerable container
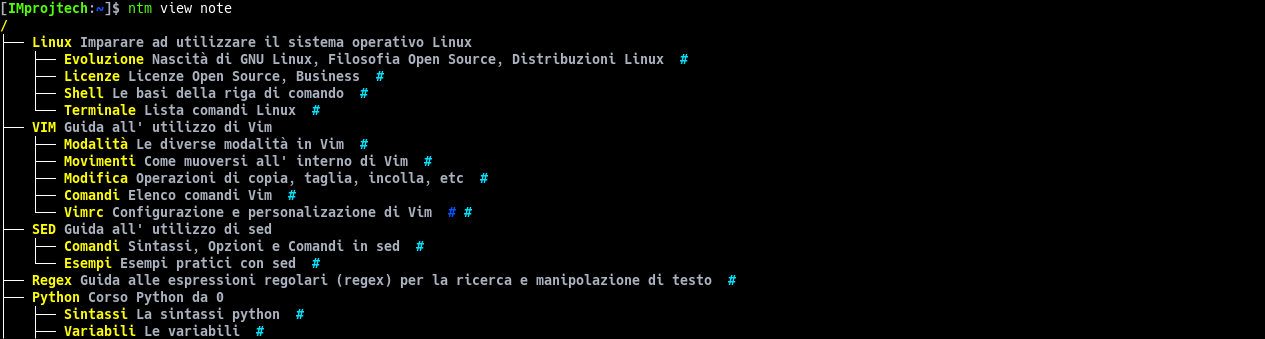 improjtech/notamy
Terminal-based note manager with hierarchical tagging and file linking
 yup-ivan/cve-2024-9796
POC (SQLi) -> CVE-2024-9796
 80ottanta80/cve-2024-32019-poc
Bash script for Privilege Escalation via "ndsudo" (Netdata Local Exploit)
 w2xim3/cve-2023-6933
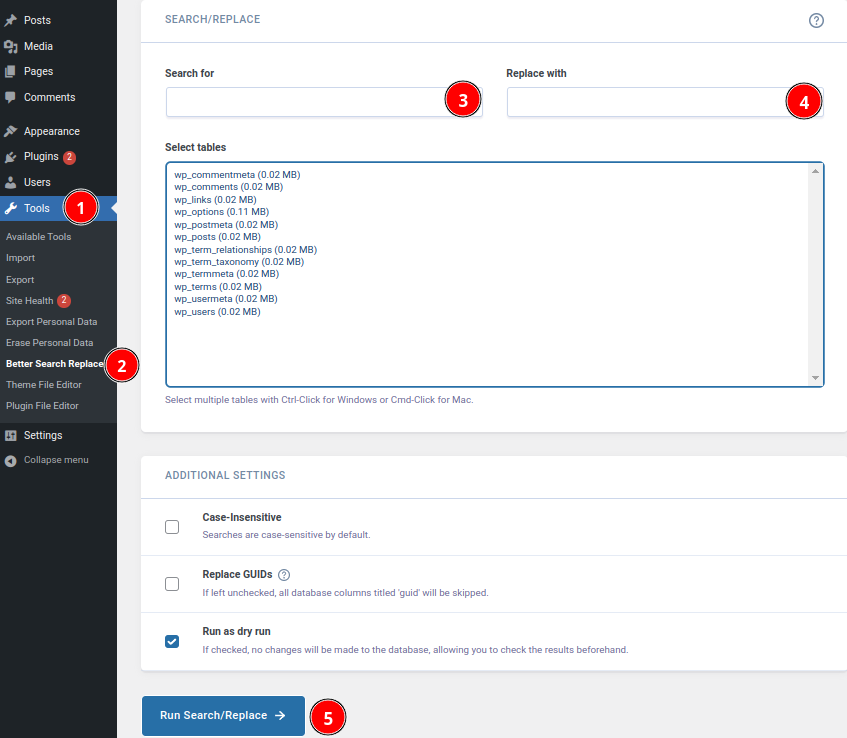
Introduction to CVE-2023-6933 Vulnerability