
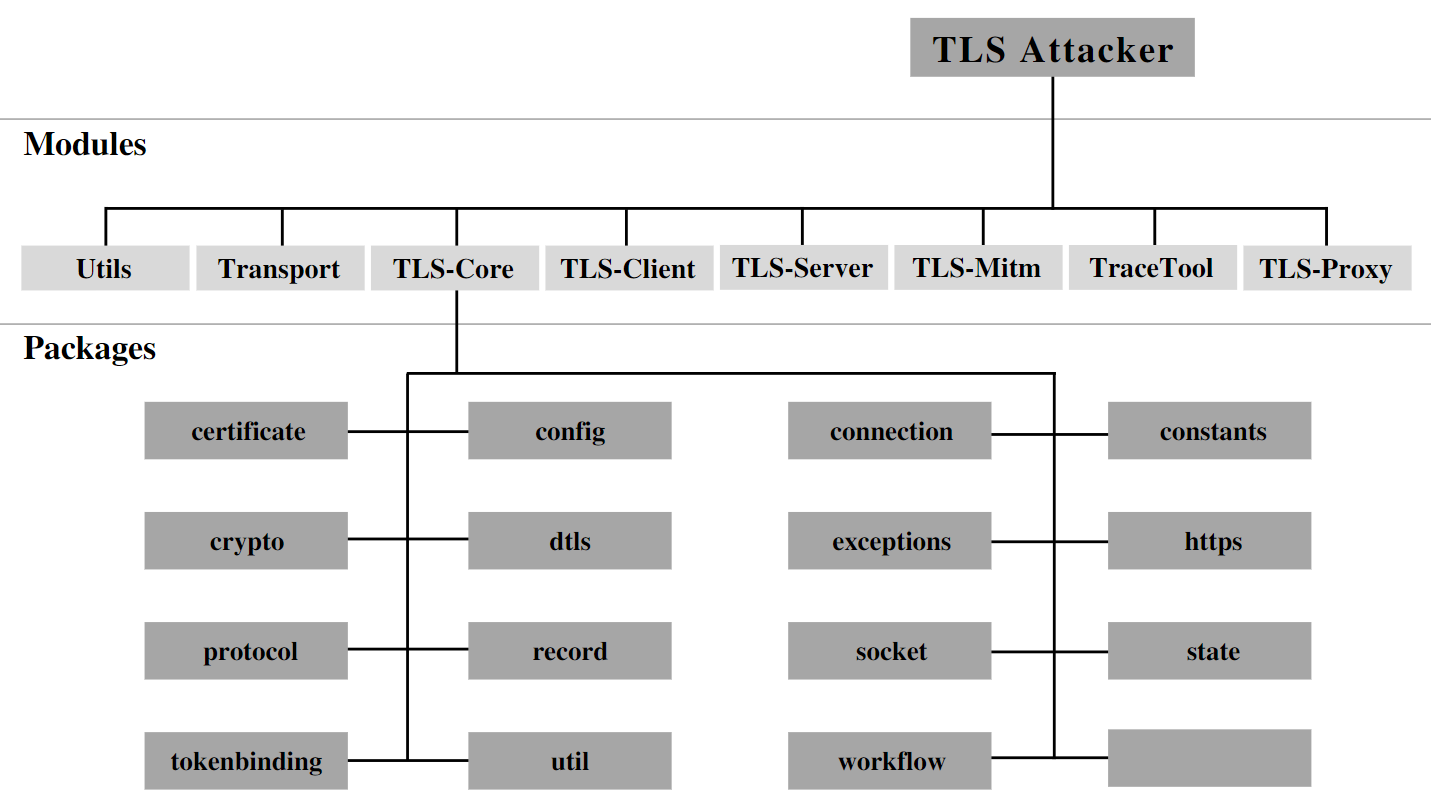
TLS-Attacker
 tls-attacker/tls-attacker
Java-based framework for systematic fuzzing and analysis of TLS libraries. Enables arbitrary protocol message crafting, modification, and testing of…
cryptographyfuzzingnetwork-security+2
876
tls-attacker/tls-attackerJava-based framework for systematic fuzzing and analysis of TLS libraries. Enables arbitrary protocol message crafting, modification, and testing of…
 galkan/crowbar
Crowbar is brute forcing tool that can be used during penetration tests. It is developed to support protocols that are not currently supported by…
 lukechilds/reverse-shell
On-demand reverse shell service that auto-detects target environment and executes appropriate payload for remote access during penetration tests.
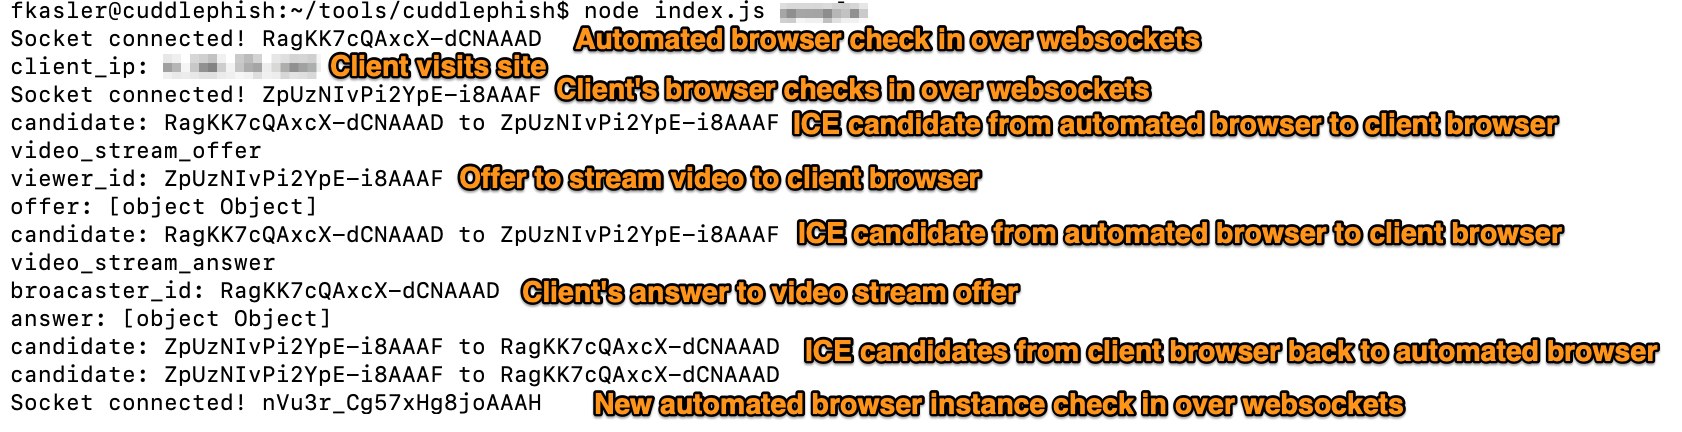 fkasler/cuddlephish
Weaponized Browser-in-the-Middle (BitM) for Penetration Testers
 trustedsec/coffloader
Run Beacon Object Files (BOFs) outside Cobalt Strike by parsing 64-bit COFF object files, with Beacon-compatible argument generation and helper…
 vanhoefm/fragattacks
Automated vulnerability tester for Wi-Fi clients and access points, detecting FragAttacks fragmentation/aggregation flaws through frame injection,…
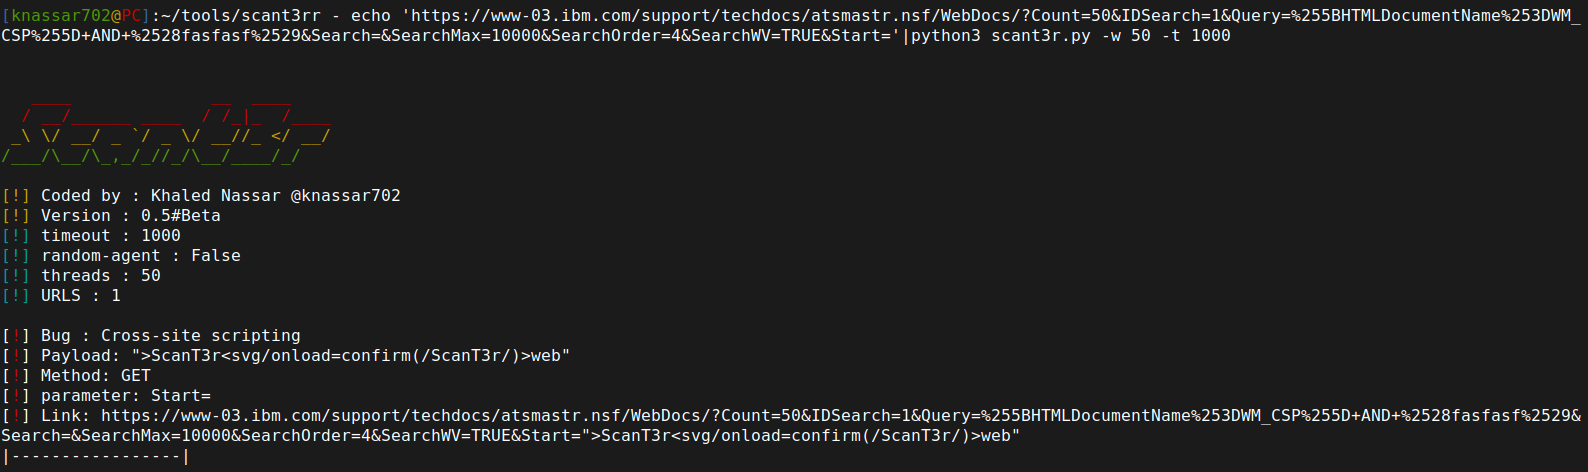 mindpatch/scant3r
Module-based web vulnerability scanner and bug bounty automation framework with built-in XSS, SSTI, SSRF, and Firebase detection engines. Designed to…
 flock4h/freeway
WiFi Penetration Testing & Auditing Tool
 hackmanit/web-cache-vulnerability-scanner
Go-based CLI scanner for web cache poisoning and deception. Supports 10 poisoning techniques, multiple deception methods, built-in crawler, JSON…
 edoardottt/missing-cve-nuclei-templates
Weekly updated list of missing CVEs in nuclei templates official repository. Mainly built for bug bounty, but useful for penetration tests and…
 rub-nds/ws-attacker
WS-Attacker is a modular framework for web services penetration testing. It is developed by the Chair of Network and Data Security, Ruhr University…
 dzonerzy/gowapt
Go Web Application Penetration Test
 datadog/threatest
CLI and Go framework for end-to-end testing of threat detection rules. Detonates attack techniques and verifies alerts in security platforms like…
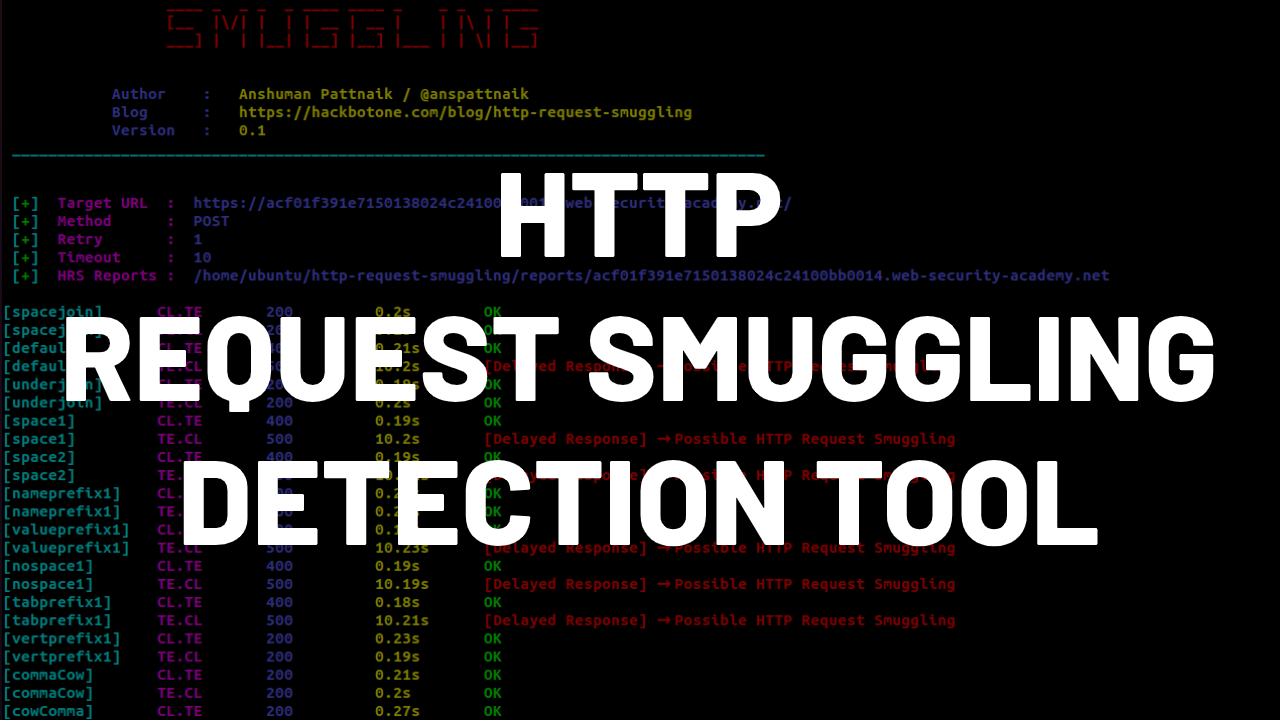 anshumanpattnaik/http-request-smuggling
CLI tool to detect HTTP Request Smuggling vulnerabilities using time-delay analysis with built-in CL.TE and TE.CL payloads for automated security…
 sapt01/hbsqli
Automated Tool for Testing Header Based Blind SQL Injection
 jas502n/cve-2020-14882
Weblogic CVE-2020-14882 unauthorized RCE exploit with patch bypass, command execution, and webshell deployment for penetration testing.
 nu11secur1ty/windows11exploits
Collection of Windows 11 exploit proof-of-concepts and vulnerability demonstrations for security research and penetration testing.
 jewel591/xssmap
Python-based XSS vulnerability scanner with support for POST/GET requests, parameter injection in cookies/referer/user-agent, and multiple encoding…