MCP-Inspector-CVE-2025-49596

MCP-Inspector-vulncheck is a Python script that checks if an MCP Inspector server is vulnerable to CVE-2025-49596. It tests whether the /sse endpoint…

MCP-Inspector-vulncheck is a Python script that checks if an MCP Inspector server is vulnerable to CVE-2025-49596. It tests whether the /sse endpoint…

Deliberately vulnerable C# API application for practicing web application exploitation and security testing. Includes Docker setup and documentation…

RumbleTalk Live Group Chat <= 6.1.9 - Missing Authorization via handleRequest

Proof-of-concept exploit for CVE-2024-50633, a Broken Object Level Authorization (BOLA) vulnerability in Indico v3.2.9–v3.3.2, enabling unauthorized…

Proof-of-concept exploit for CVE-2023-31719, demonstrating SQL injection in the FUXA web application's /api/signin endpoint via a crafted JSON…

Zita Site Builder <= 1.0.2 - Missing Authorization to Arbitrary Plugin Installation

he Hunk Companion Plugin for WordPress: Vulnerable to Unauthorized Plugin Installation/Activation (Versions Up to and Including 1.8.4)

Proof-of-concept exploit for CVE-2024-26026: unauthenticated SQL injection in F5 BIG-IP Next Central Manager API, enabling remote data extraction and…

Lightweight Java 8 web framework with routing, filters, and static file serving. Includes security advisory for older versions and CRUD API examples.

Python-based Burp Suite extension is designed to detect the presence of CVE-2025-31324

A bash automation that exploits the vulnerable endpoints for the Joomla! API 4.0 - 4.2.7

Lightweight Java 8 web framework for building REST APIs and web applications, with built-in routing, static file serving, and template engine support.

CodePath Assignment for Weeks 7 & 8: CVE-2017-14719, CVE-2019-9787 & Unauthenticated Page/Post Content Modification via REST API

The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…

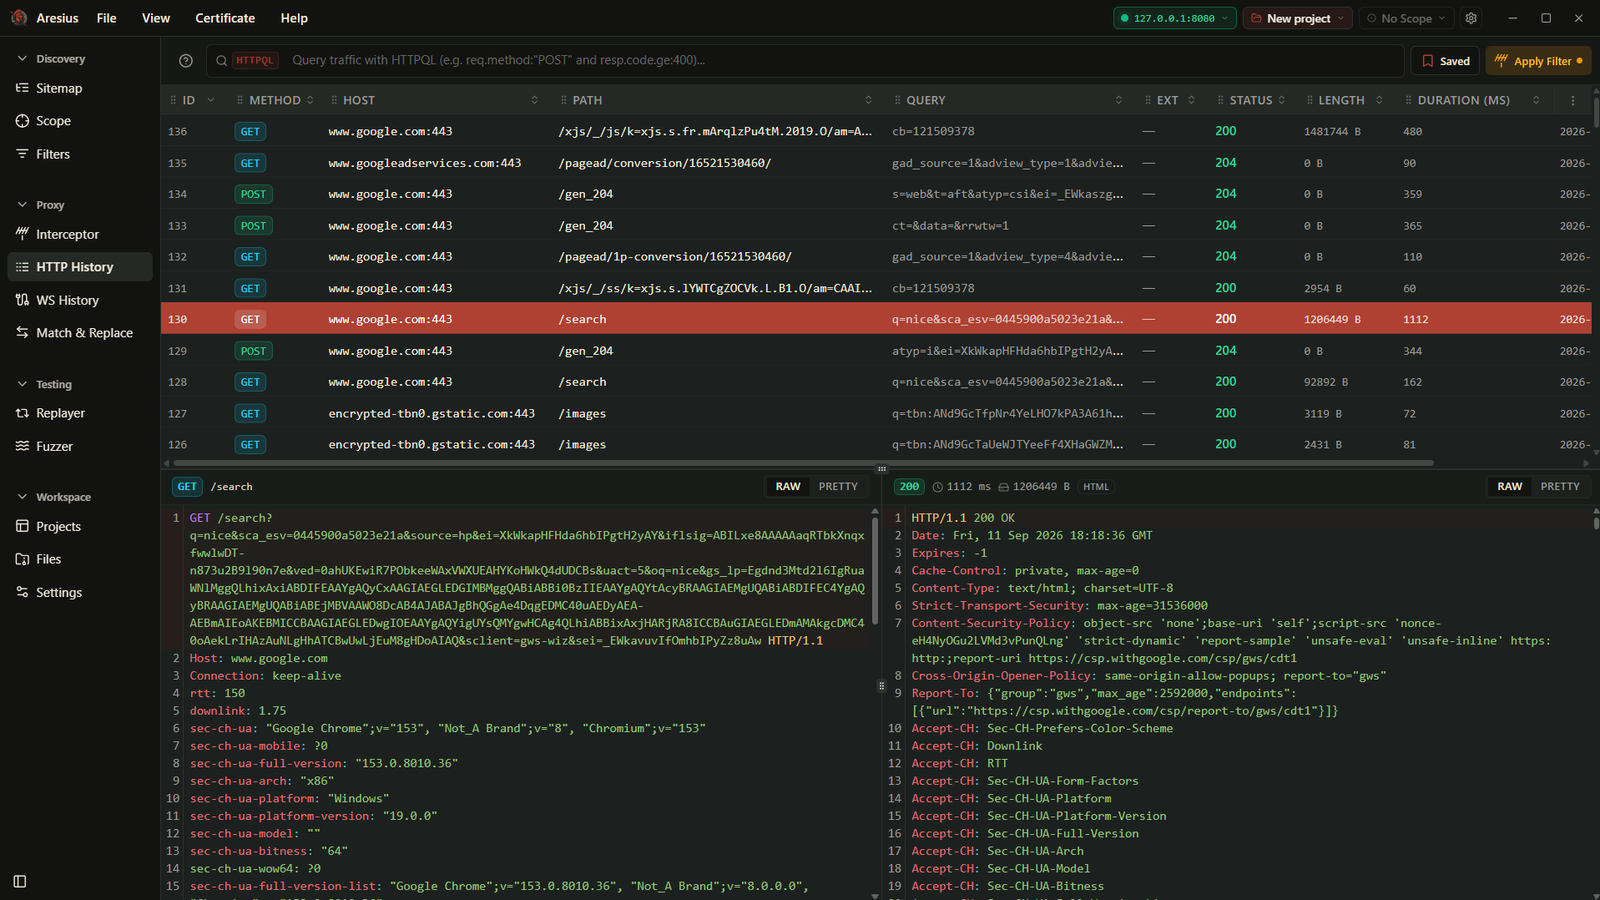
A fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.

Terminal-based HTTP intercepting proxy with TUI for capturing, inspecting, and modifying requests in real time, plus a Repeater for resending and…

Native HTTP/HTTPS interception proxy for penetration testers and bug bounty hunters with live request tampering, request replay, high-speed fuzzing,…

Extends Selenium's Python bindings to give you the ability to inspect requests made by the browser.