
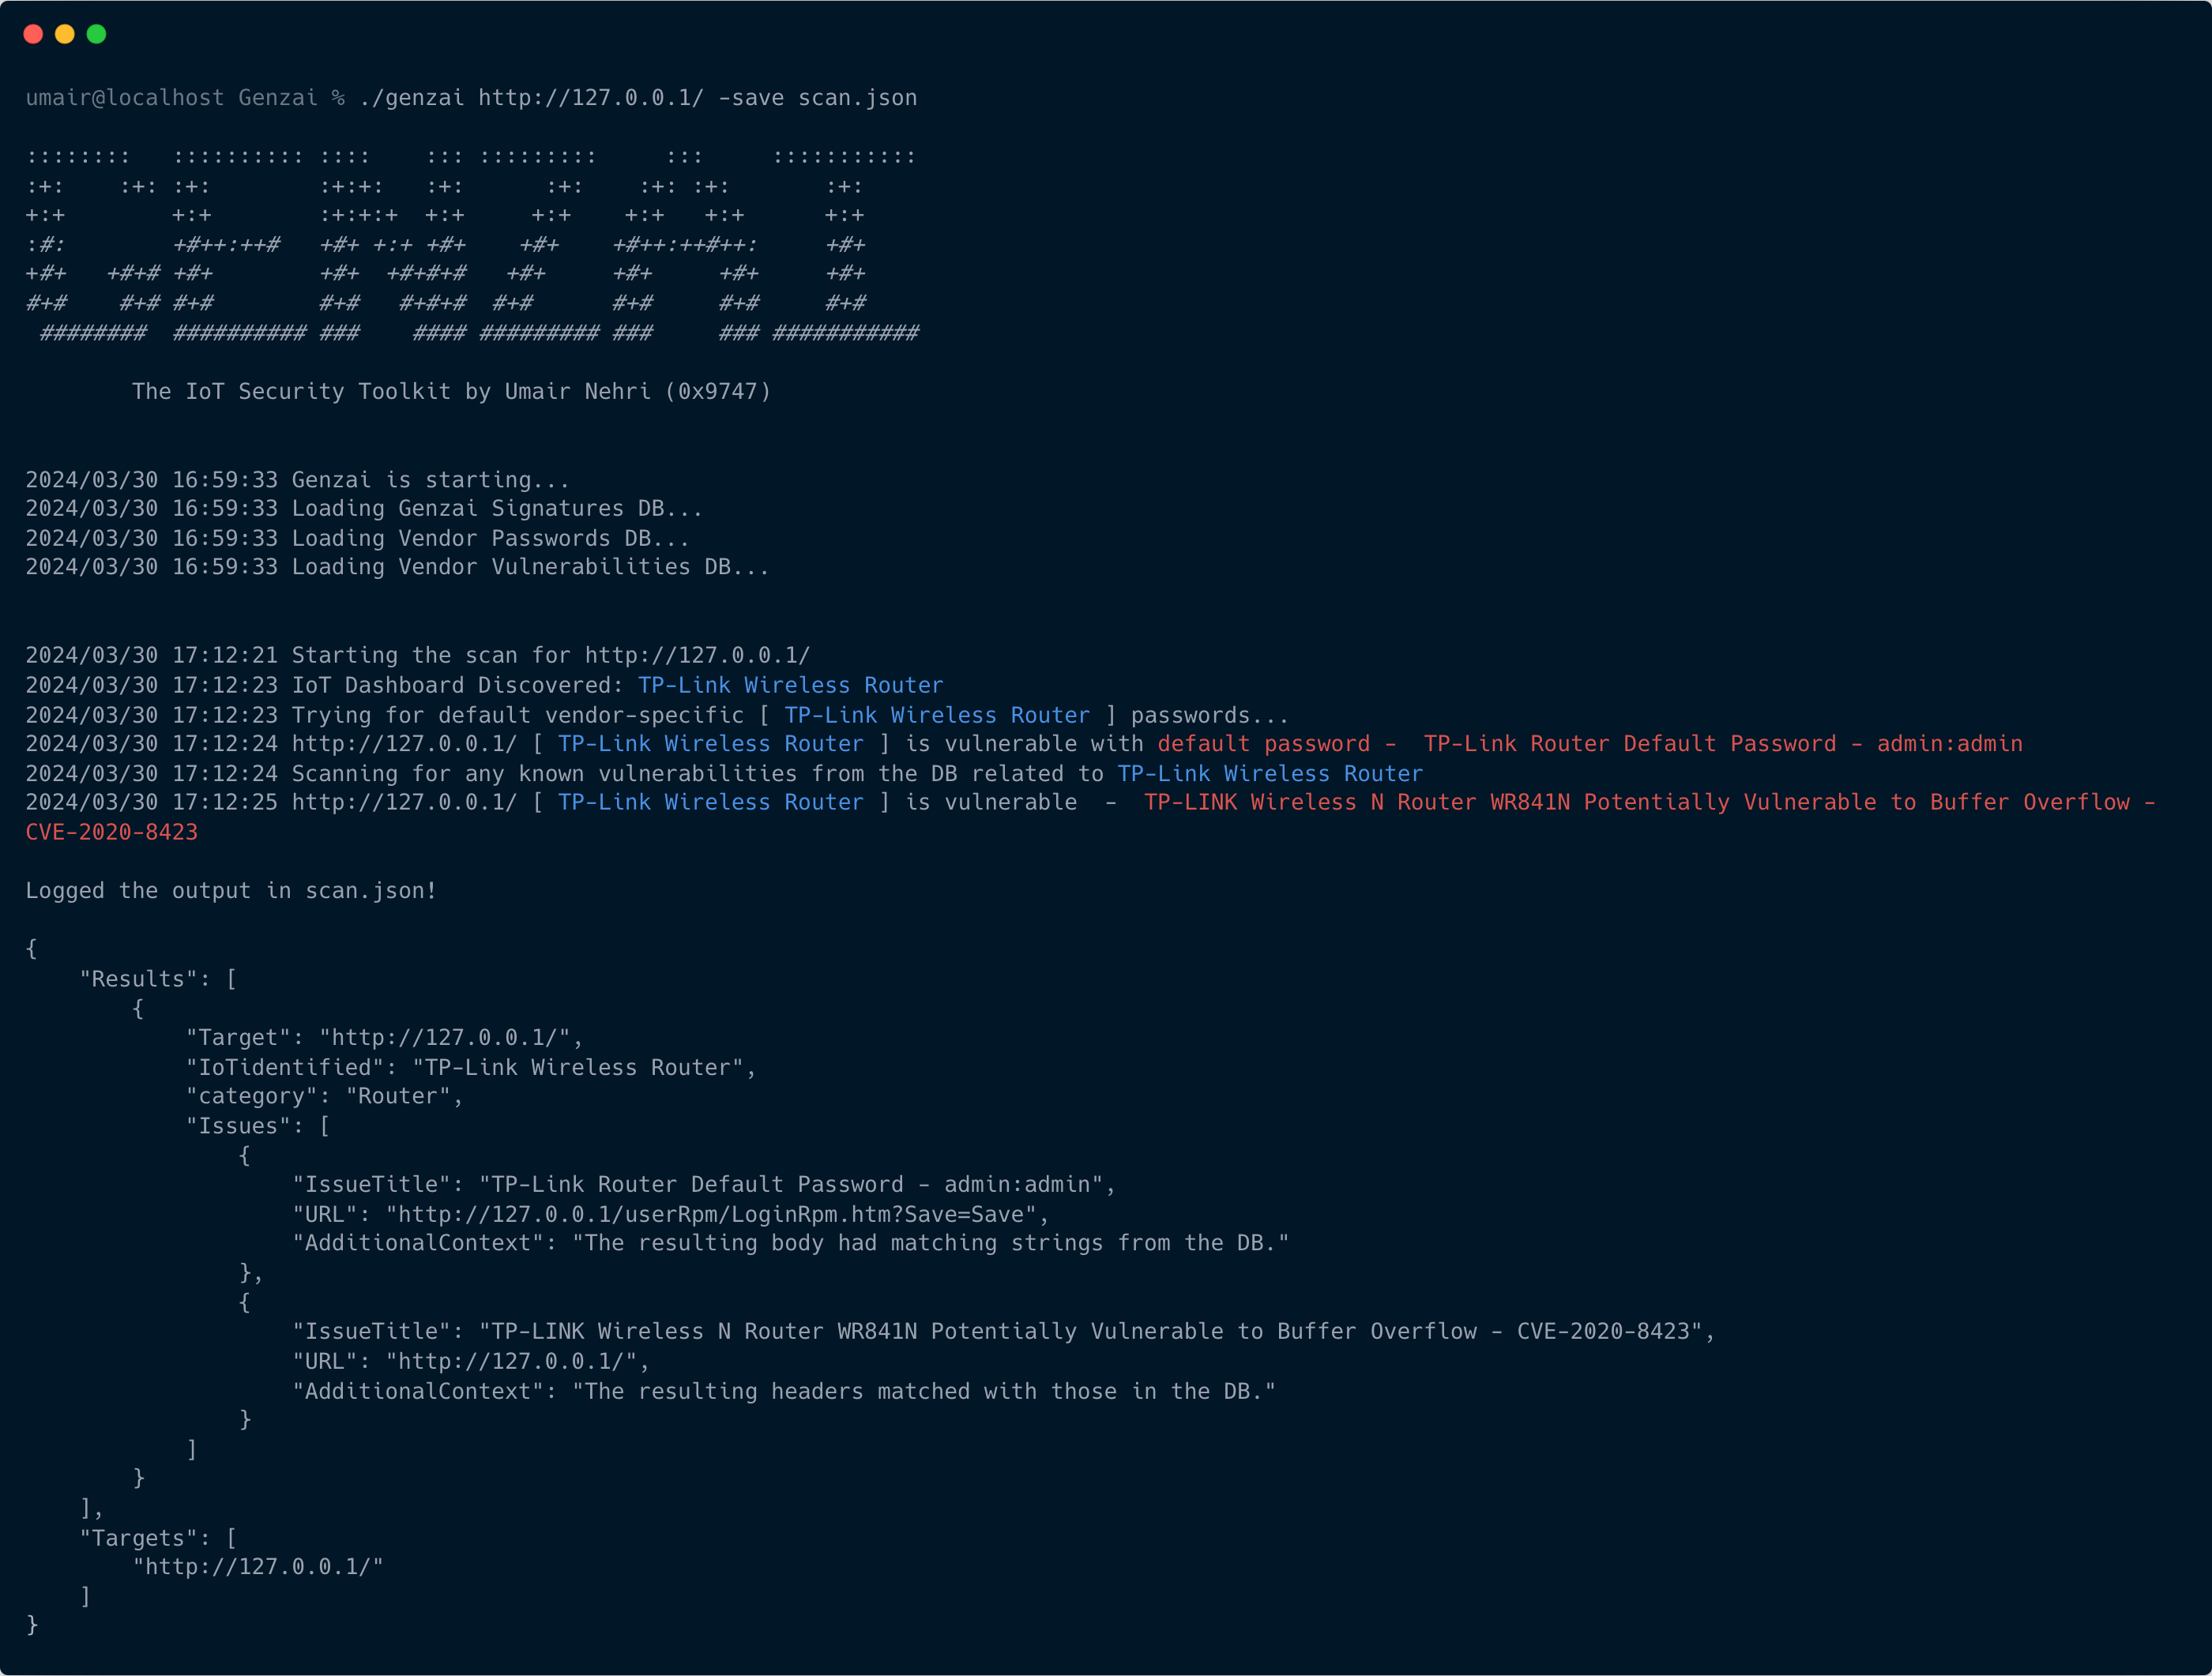
Genzai
 umair9747/genzai
The IoT security toolkit to help identify IoT related dashboards and scan them for default passwords and vulnerabilities.
iot-securitypassword-attackspenetration-testing+3
212
umair9747/genzaiThe IoT security toolkit to help identify IoT related dashboards and scan them for default passwords and vulnerabilities.
 lachlan2k/cve-2023-35803
PoC exploit for CVE-2023-35803 unauthenticated buffer overflow in Aerohive HiveOS/Extreme Networks IQ Engine, enabling remote code execution on…
 kemrec/cve-2025-11142-axis-mediaclip-rce
Proof-of-concept and technical analysis for CVE-2025-11142, an authenticated OS command injection in AXIS VAPIX mediaclip.cgi, with time-based and…
 christophe.duvernois/usb-spy
Intercepts and analyzes USB Mass Storage traffic at the block and file level, emulates USB devices, and supports custom Python stubs for security…
 ebrasha/cve-2024-7029
PoC exploit for CVE-2024-7029 in AVTech devices. Enables authentication bypass, remote code execution, vulnerability scanning, and interactive shell…
 interceptsuite/interceptsuite
MITM proxy for TCP/TLS/DTLS/UDP traffic, with STARTTLS, IoT, Thick Client and more.
 vakzz/tplink-cve-2017-11519
POC for TP-Link Archer C9 - Admin Password Reset and RCE (CVE-2017-11519)
 fj016/cve-2024-41992-poc
PoC for the CVE-2024-41992 (RCE on devices running WiFi-TestSuite-DUT)
 tony102741/cve-2026-15469
Advisory and technical analysis of CVE-2026-15469, a hard-coded RSA-512 mesh group private key in TP-Link Deco routers, including root cause, impact,…
 c0ld1/gpon_rce
Exploit for Remote Code Execution on GPON home routers (CVE-2018-10562) written in Python.
 badboycxcc/xss-cve-2022-30489
Proof-of-concept exploit for CVE-2022-30489, a stored XSS vulnerability in WAVLINK WN535G3 routers, demonstrating a POST-based attack via the…
 yilin1203/cve-2022-40881
Proof-of-concept exploit for CVE-2022-40881 targeting SolarView Compact devices. Uses fofa query for reconnaissance and payload delivery for…
 iwallplace/cve-2026-26898-xiaomi-ssrf-hostheaderinjection
Unauthenticated SSRF in Xiaomi Mi Router 4A Gigabit Edition (firmware 3.0.24) via Host Header Injection — CVE-2026-26898
 krypton612/hikivision
Exploit for CVE-2017-7921 targeting Hikvision IP cameras, enabling remote credential extraction and device takeover via unauthenticated access.
 varangamin/cve-2017-6206
The DGS-1510 Websmart switch series firmware has been found to have security vulneratiblies. The vulnerabilities include unauthenticated command…
 wanlichangchengwanlichang/cve-2024-29972
Exploit script for CVE-2024-29972 Zyxel NAS backdoor account, combining with CVE-2024-29973 for unauthorized root access via NsaRescueAngel.
 huzaifahussain98/cve-2019-17525
D-LINK ROUTER "MODEL NO: DIR-615" with "FIRMWARE VERSION:20.10" & "HARDWARE VERSION:T1
 killsystema/scan-cve-2026-24061
Scans for CVE-2026-24061 telnetd auth bypass, generating payloads and verifying root access on vulnerable GNU inetutils telnetd devices.