

dinkleberry
 aliask/dinkleberry
Patch your D-Link device affected by CVE-2024-3272
binary-analysisembedded-systems-securityexploitation+4
aliask/dinkleberryPatch your D-Link device affected by CVE-2024-3272
 amiraliuks/ip-camera-research
Security research on a consumer IP camera built on the Fullhan FH8626V100 SoC (model AJL30PG0803).
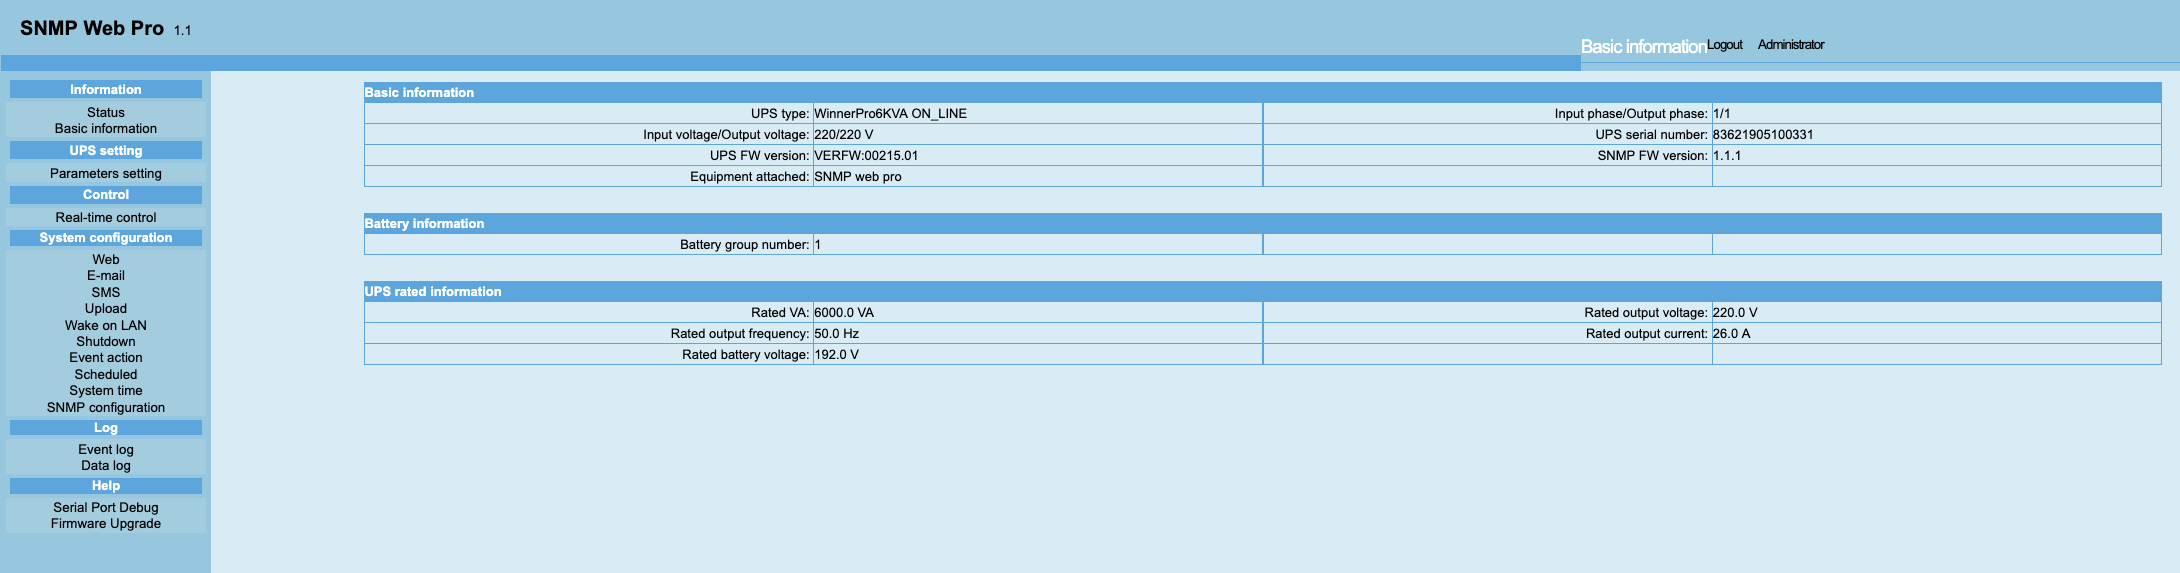 virgula0/cve-2026-44402
Pre-Authenticated Full Root Remote Command Execution in Voltronic Power SNMP Web Pro 1.1
 ide0x90/cve-2016-1555
Metasploit module exploiting unauthenticated command injection in multiple Netgear router models to achieve remote code execution with root…
 jdbonfils/poc_cve-2025-48507
Proof of Concept of CVE-2025-48507. The security flaw can be leveraged by Non-Secure software (e.g., Linux) to break Trust Zone and gain access to…
 safelock-d2e/quiksand-cve-2023-24012
Proof-of-concept demonstrating a permission bypass in ROS 2 SROS2 security framework, allowing unauthorized topic subscription via modified…
 pwnonu/t3-technology-cpe-advisories
CVE-2026-35904 / CVE-2026-35905 / CVE-2026-35906 — Unauth RCE, Hardcoded Root Creds & Telnet Enable in T3 Technology CPE
 murrez/asus-aicloud-rce
SETROOTCERTIFICATE (write /etc/cert.pem.1) + APPLYAPP (RC_SERVICE execution). Refs: CVE-2025-2492, CVE-2024-12912, CVE-2025-59366; runZero;…
 sermikr0/cve-2026-38422
CVE-2026-38422 — Remote Code Execution via Combined Buffer Overflows in Tasmota fetch_jpg() (Tasmota <= 15.3.0.3)
 vital-information-resource-under-siege/cve-2026-38698-and-cve-2026-38699
Technical details and publication about CVE-2026-38698 and CVE-2026-38699
 sermikr0/cve-2026-38427
CVE-2026-38427 — Integer Wraparound → Heap Buffer Overflow in Tasmota fetch_jpg() uint16_t (Tasmota <= 15.3.0.3)
 yanissec/cve-2018-7845
CVE-2018-7845
 yanissec/cve-2018-7849
CVE-2018-7849
 bertoldvdb/pcanexploit
CVE-2024-44610: Authenticated remote root exploit in Peak PCAN-Ethernet CAN-(FD) gateways
 bu0ucat/d-link-nas-cve-2024-10914-
这是一个D-Link rce漏洞 检测程序
 laskdjlaskdj12/cve-2024-29671-poc
This is POC of CVE-2024-29671
 0xqrx/cve-2024-6333
Authenticated Remote Code Execution vulnerability in Xerox WorkCentre printers via the Network Troubleshooting Log feature.
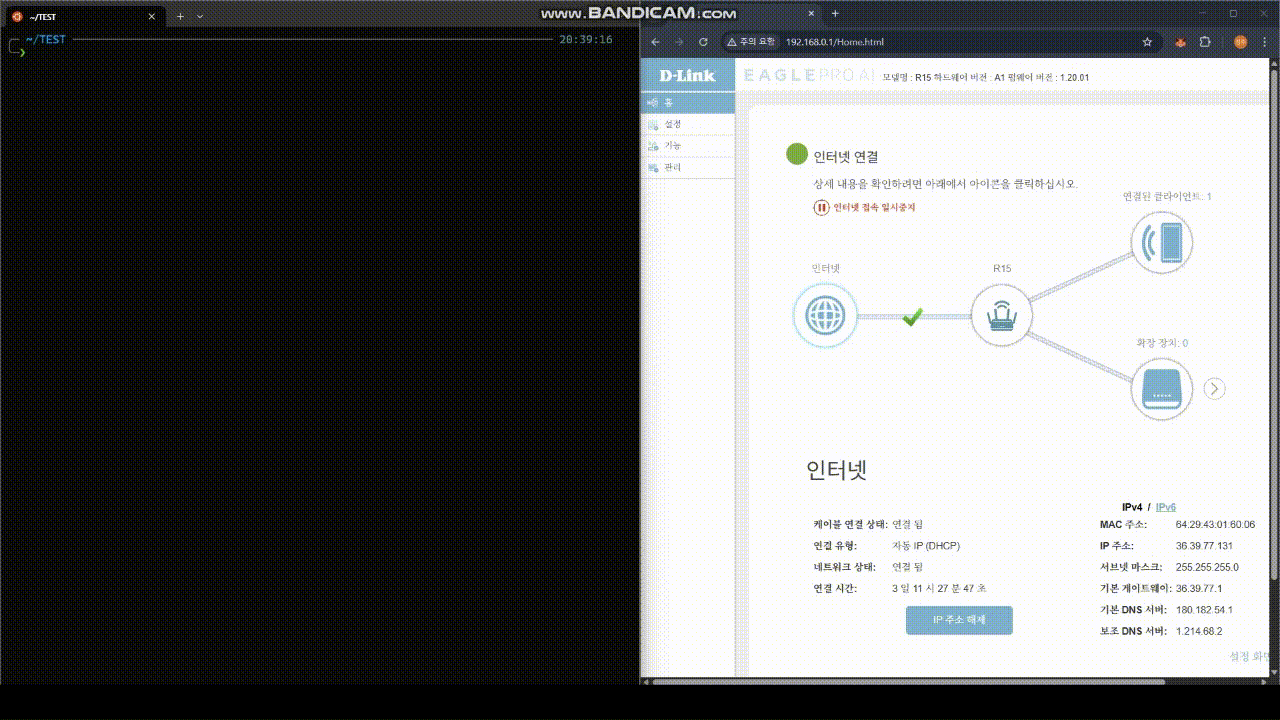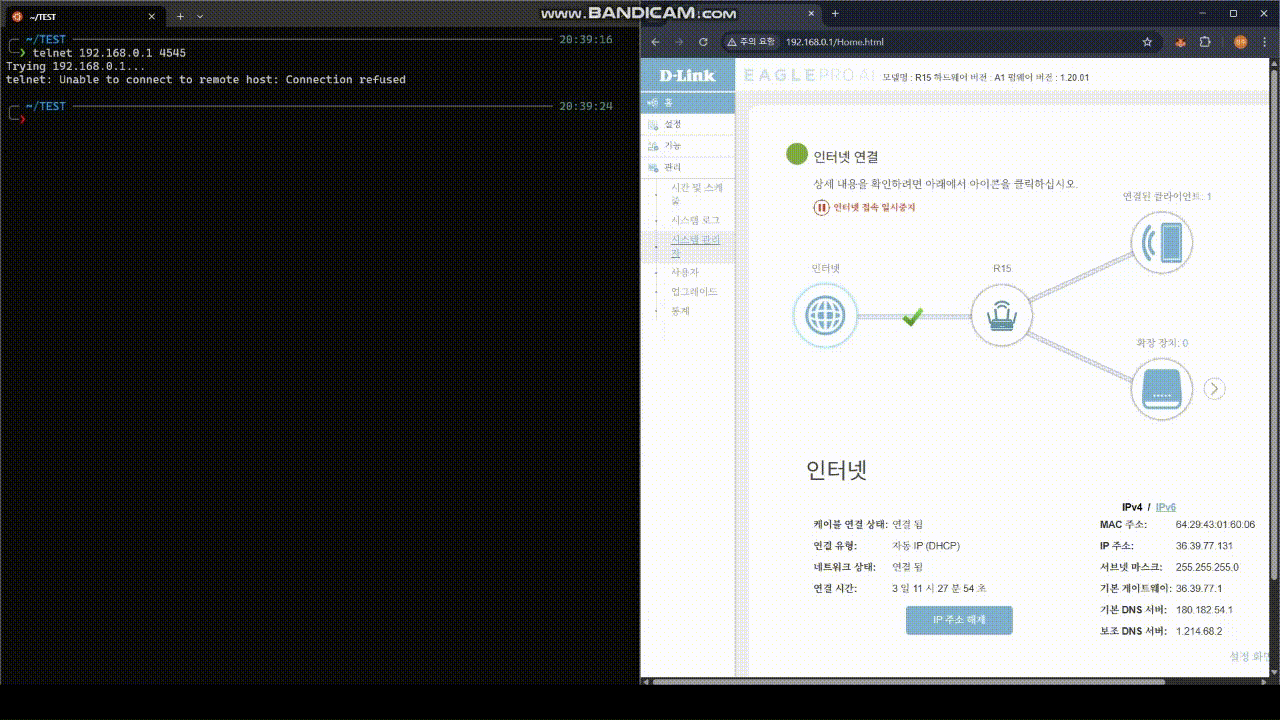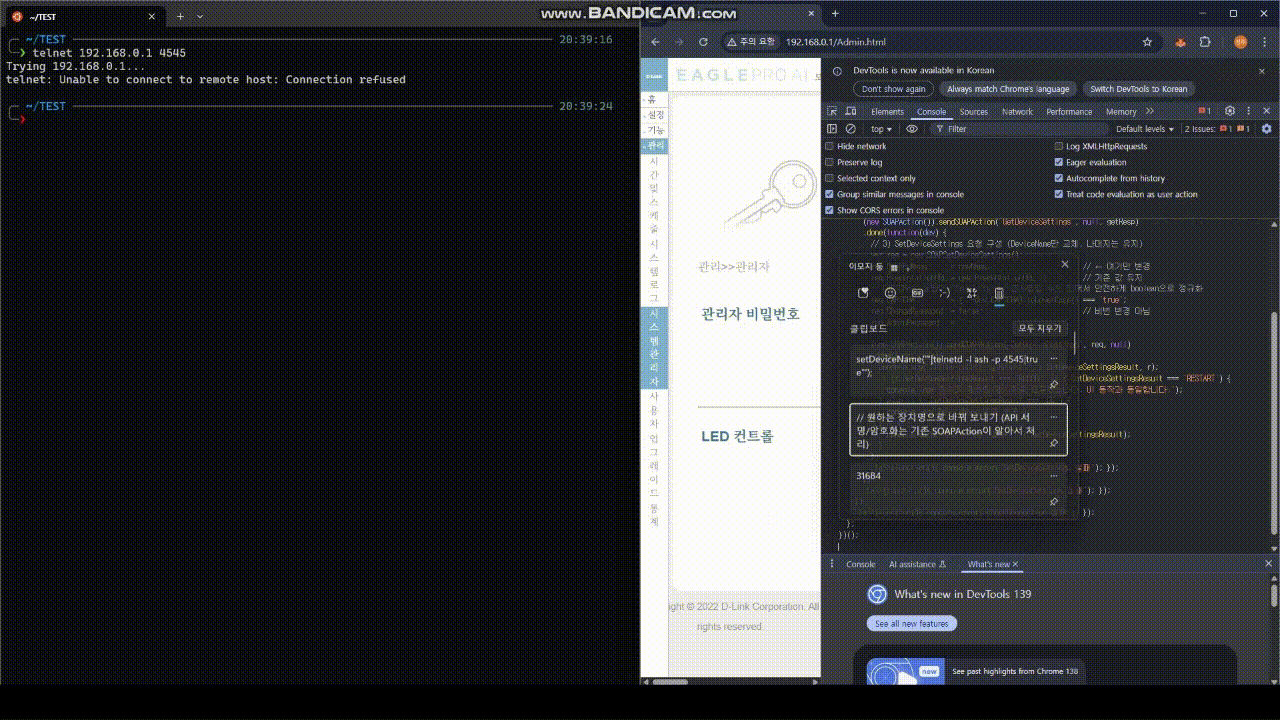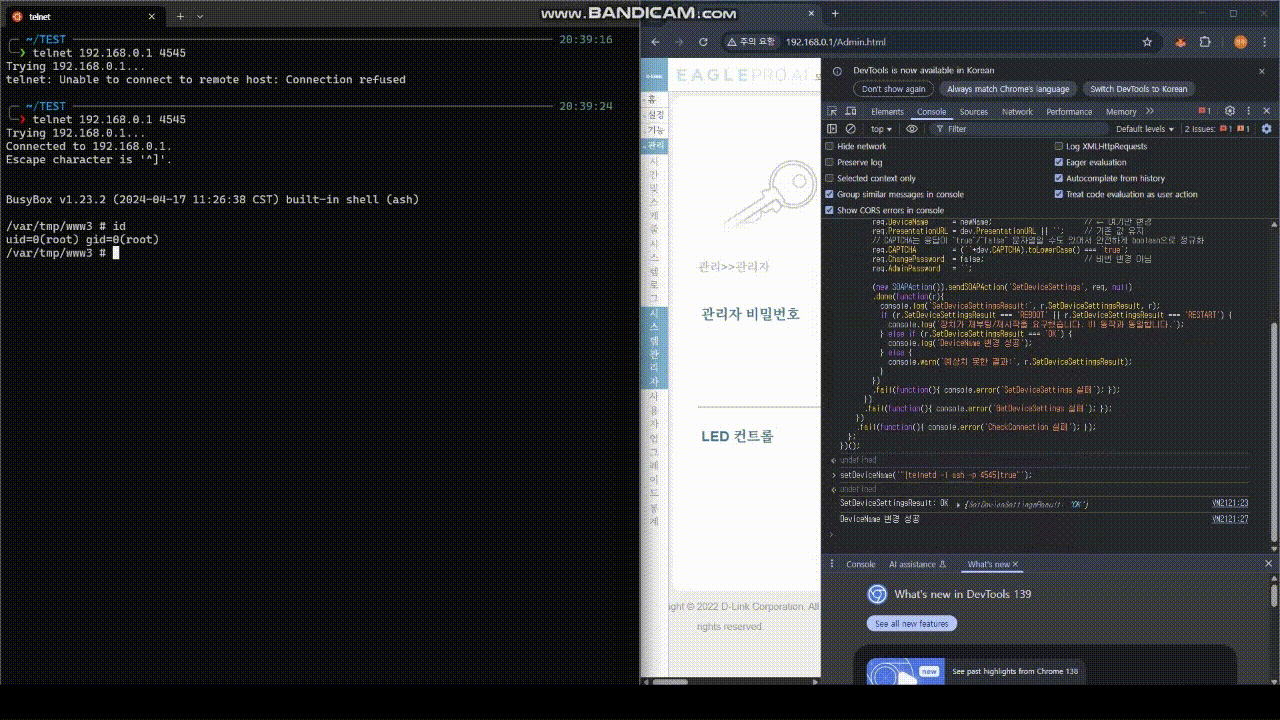 k0n9-log/cve-2025-60854
D-link AX1500 Vulnerability