

MSSQLand
 n3rada/mssqland
In-target C# post-exploitation and exploitation tool for Microsoft SQL Server (MS SQL / MSSQL) traversing linked-server chains of any depth with…
configuration-auditingdatabase-securityimpersonation-tools+6
75
n3rada/mssqlandIn-target C# post-exploitation and exploitation tool for Microsoft SQL Server (MS SQL / MSSQL) traversing linked-server chains of any depth with…
 abraxas/signal-server-dropwizard-admin
Signal-Server v20261007.0.0 - High - Remote - Privilege leftover - unauth Dropwizard admin :8081
 jtesta/ssh-audit
SSH server & client security auditing (banner, key exchange, encryption, mac, compression, compatibility, security, etc)
 tls-attacker/tls-scanner
Automated TLS server and client configuration scanner for pentesters and researchers. Evaluates cipher suites, protocol versions, and security…
 nimaarek/cve-2026-8932-poc
Proof-of-concept reproducing CVE-2026-8932, an incomplete mTLS configuration matching flaw in libcurl connection reuse, with a local lab server and C…
 baba01hacker666/cve-2026-33032
Python proof-of-concept for CVE-2026-33032 that inspects nginx status and configs, then demonstrates unauthorized config write with reload to deploy…
 george0papasotiriou/cve-2026-22007-ntp-monlist-amplification-over-ipv6
Python PoC for CVE-2026-22007: NTP monlist amplification over IPv6, including a simulated vulnerable server and spoofed UDP reflection attack.
 oscerd/cve-2026-40022
Reproducer for CVE-2026-40022: Apache Camel camel-platform-http-main authentication bypass on non-root context paths
 jfs-jfs/cve-2026-37073
Proof-of-concept exploit for CVE-2026-37073: unauthenticated SMTP email abuse via incorrect access control in Veno File Manager 4.4.9.
 dahalsamir/cve-2026-23744-mcpjam-rce-exploit
This Python proof-of-concept targets a vulnerable MCP (Model Context Protocol) service exposed by the target application. The vulnerability allows an…
 alisster00/cve-2026-23744-rce
This utility was created during research involving MCPJam v1.4.2. The application exposes an API endpoint that accepts a server configuration object.…
 deepsecurityresearch/cve-2026-2586
Authenticated EL injection exploit for GlassFish/Payara admin console enabling remote command execution via crafted parameters in the virtual server…
 dungsocool/cve-2017-12635_36
Step-by-step lab demonstrating exploitation of CVE-2017-12635 (privilege escalation) and CVE-2017-12636 (remote code execution) against Apache…
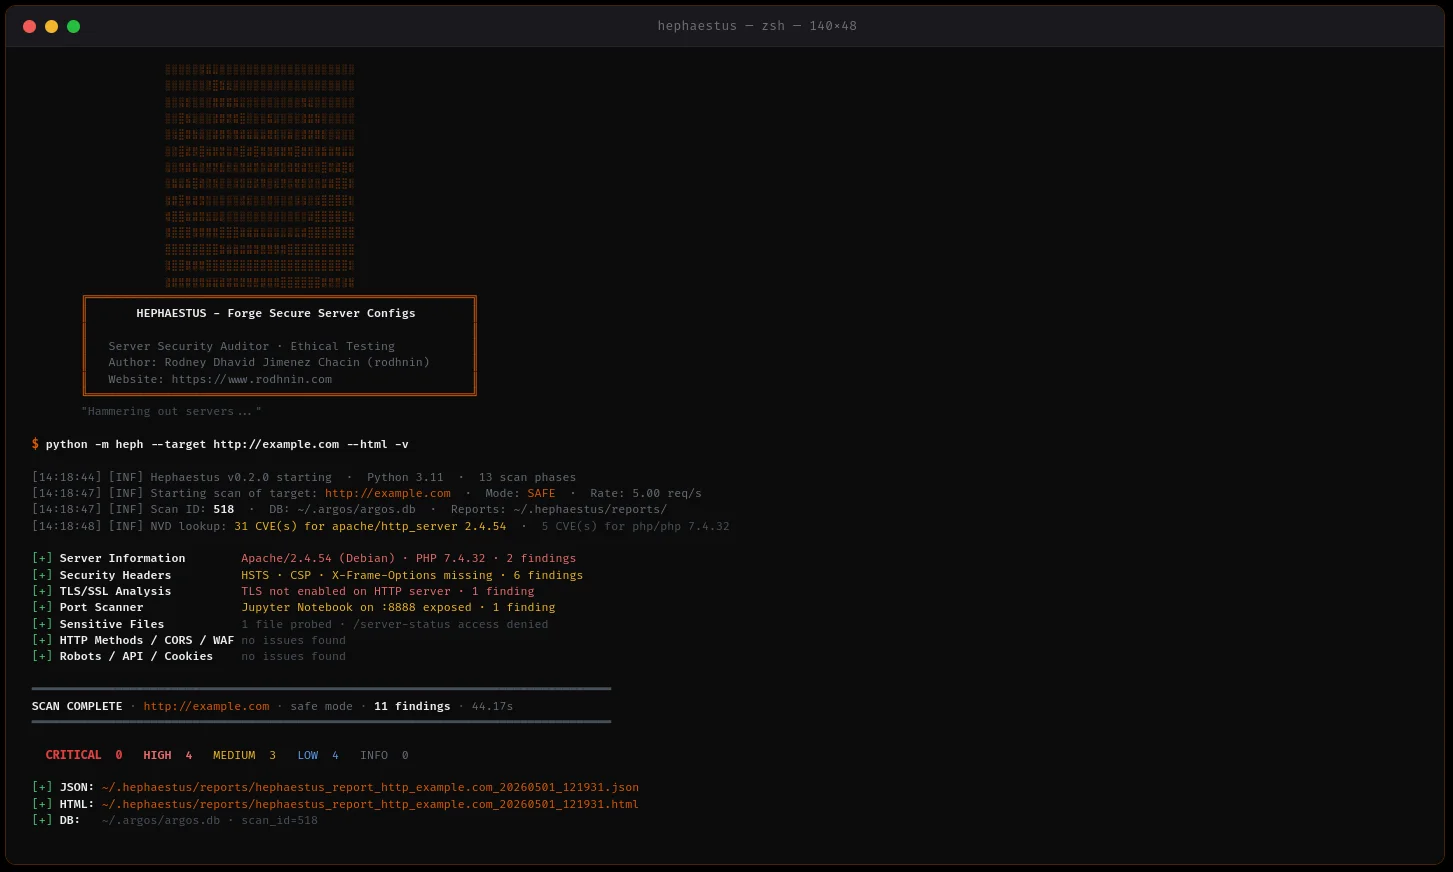 rodhnin/hephaestus-server-forger
server security auditor scanning Apache, Nginx, and IIS configurations with AI-powered hardening guides and professional reporting.
 jdormannn/secureops-lab
Performed a live cybersecurity assessment on a university Linux server. During analysis, active attack activity was identified, including brute-force…
 typicalsmc/cve-2025-49132-poc
Proof-of-concept exploit for CVE-2025-49132, a path traversal vulnerability in Pterodactyl panel. Forges session cookies using exposed Redis server…
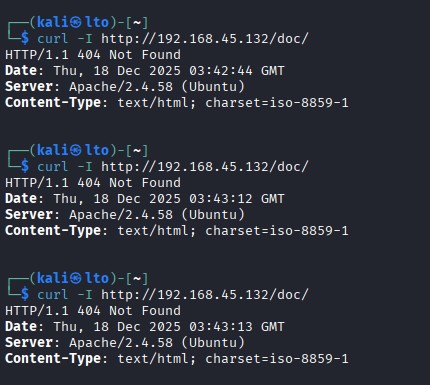 lto7777777/cve-1999-0678
CVE-1999-0678- /doc directory browsable
 d0n601/cve-2025-12721
g-FFL Cockpit <= 1.7.1 - Missing Authorization to Unauthenticated Information Exposure