
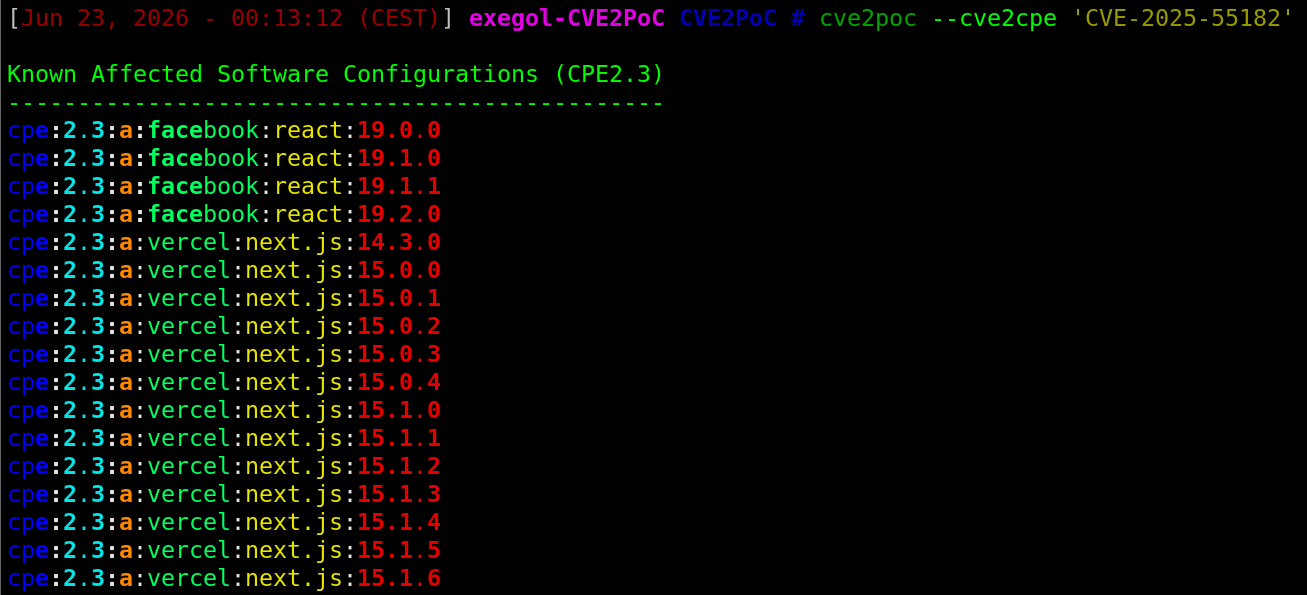
CVE2PoC
 0liverflow/cve2poc
CVE2PoC is a tool that helps penetration testers, bug hunters, and security researchers quickly find public exploits or PoCs related to a CVE ID
educationexploitationinformation-gathering+5
0liverflow/cve2pocCVE2PoC is a tool that helps penetration testers, bug hunters, and security researchers quickly find public exploits or PoCs related to a CVE ID
 edoardottt/awesome-hacker-search-engines
A curated list of awesome search engines useful during Penetration testing, Vulnerability assessments, Red/Blue Team operations, Bug Bounty and more
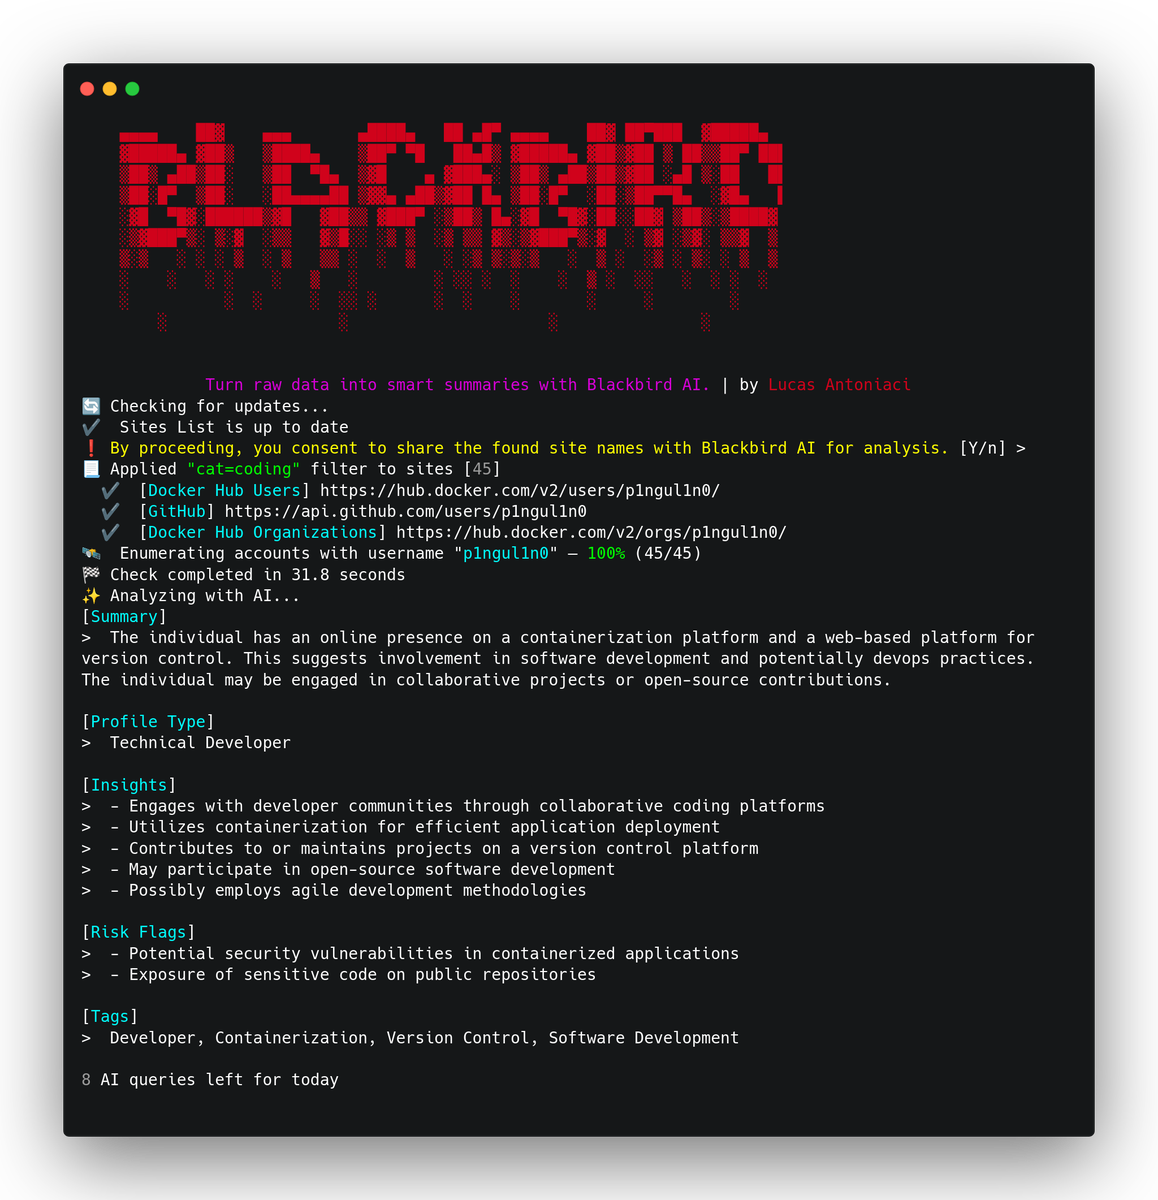 antoniaci/blackbird
An OSINT tool to search for accounts by username and email in social networks.
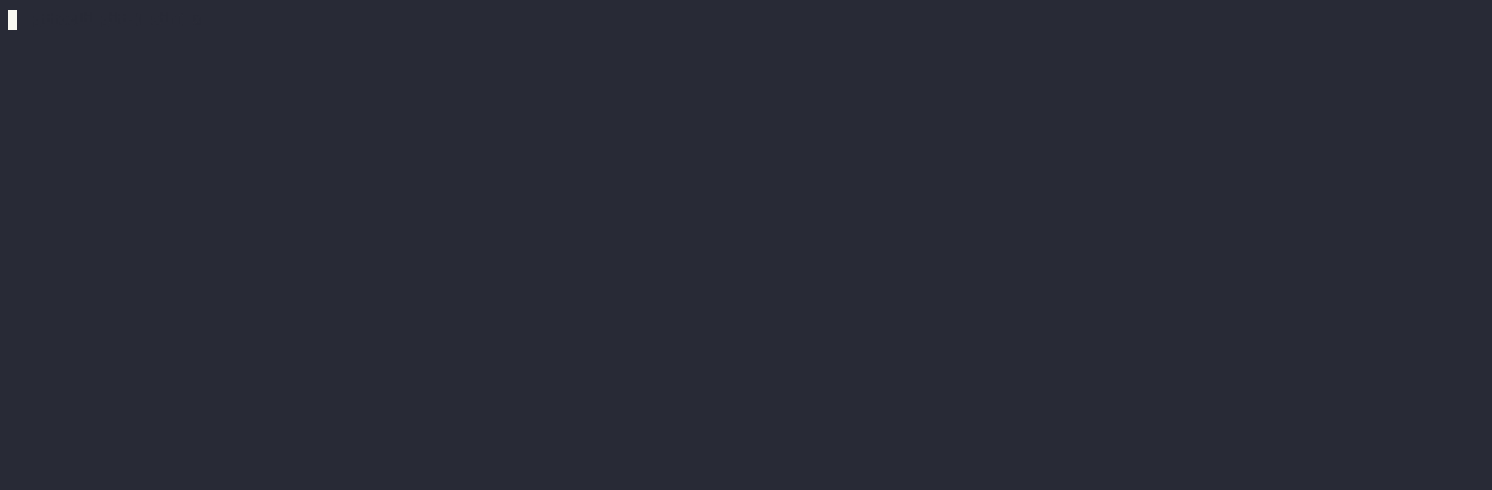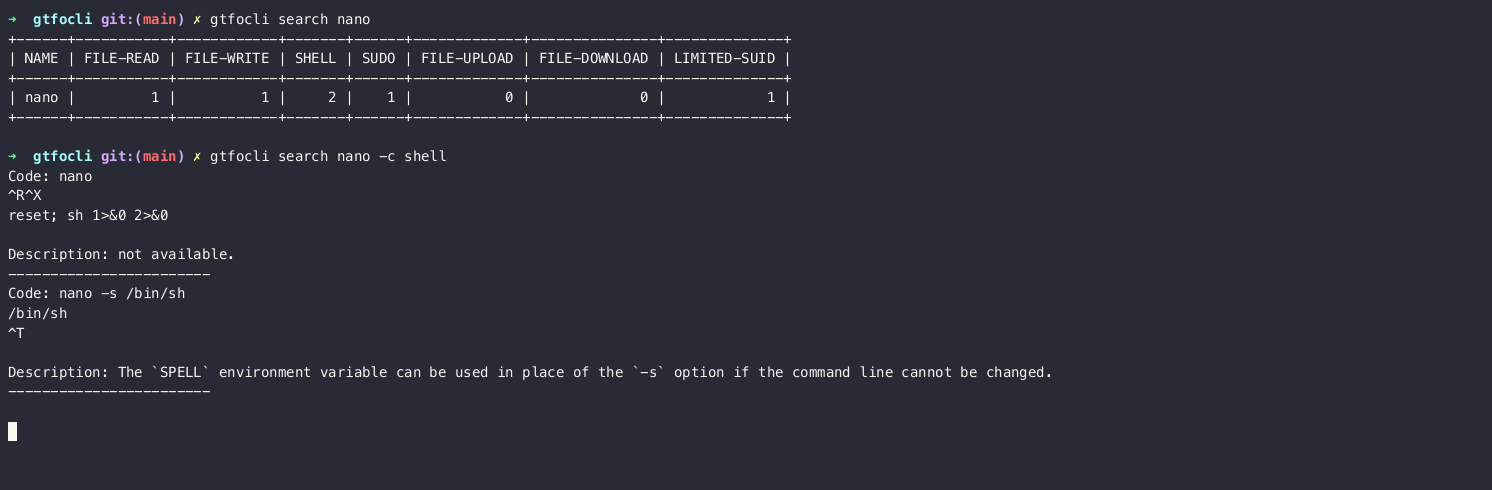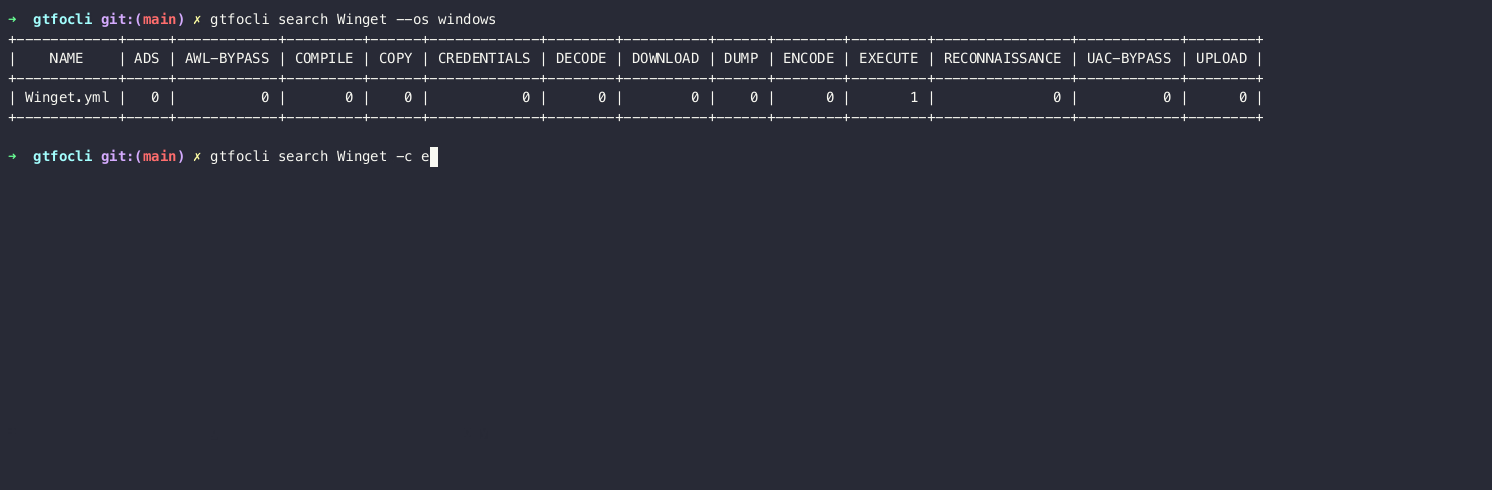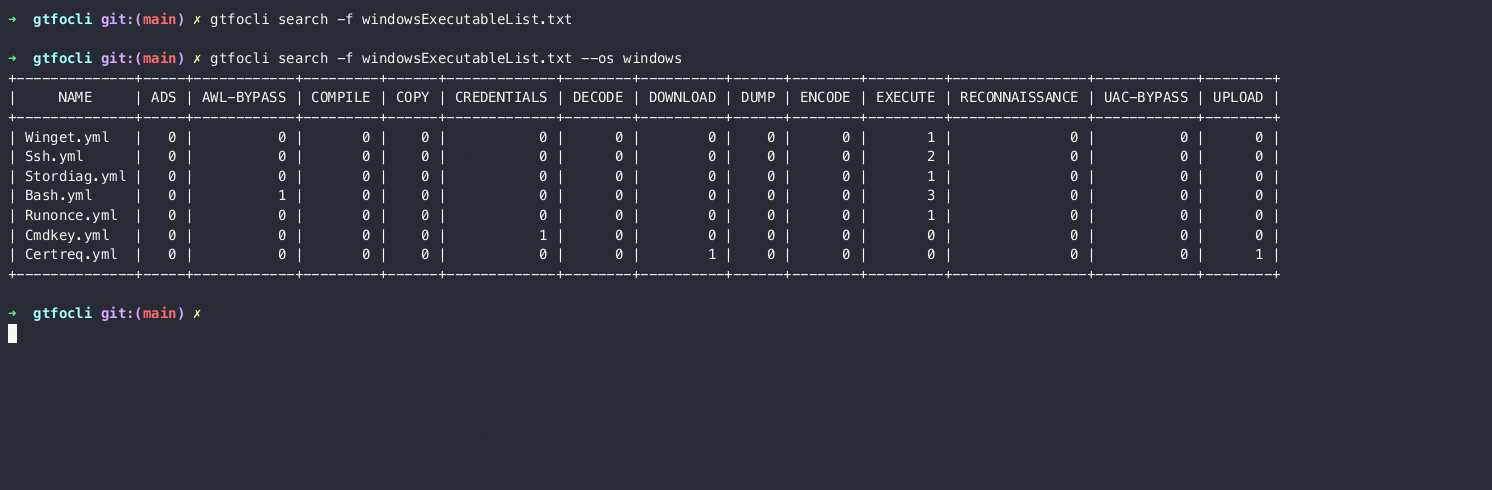 cmd-tools/gtfocli
GTFO Command Line Interface for easy binaries search commands that can be used to bypass local security restrictions in misconfigured systems.
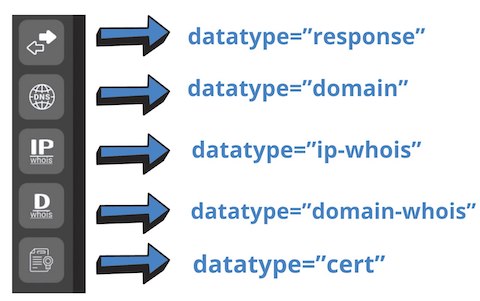 netlas-io/netlas-cookbook
The goal of this guide is very simple - to teach anyone interested in cyber security, regardless of their knowledge level, how to make the most of…
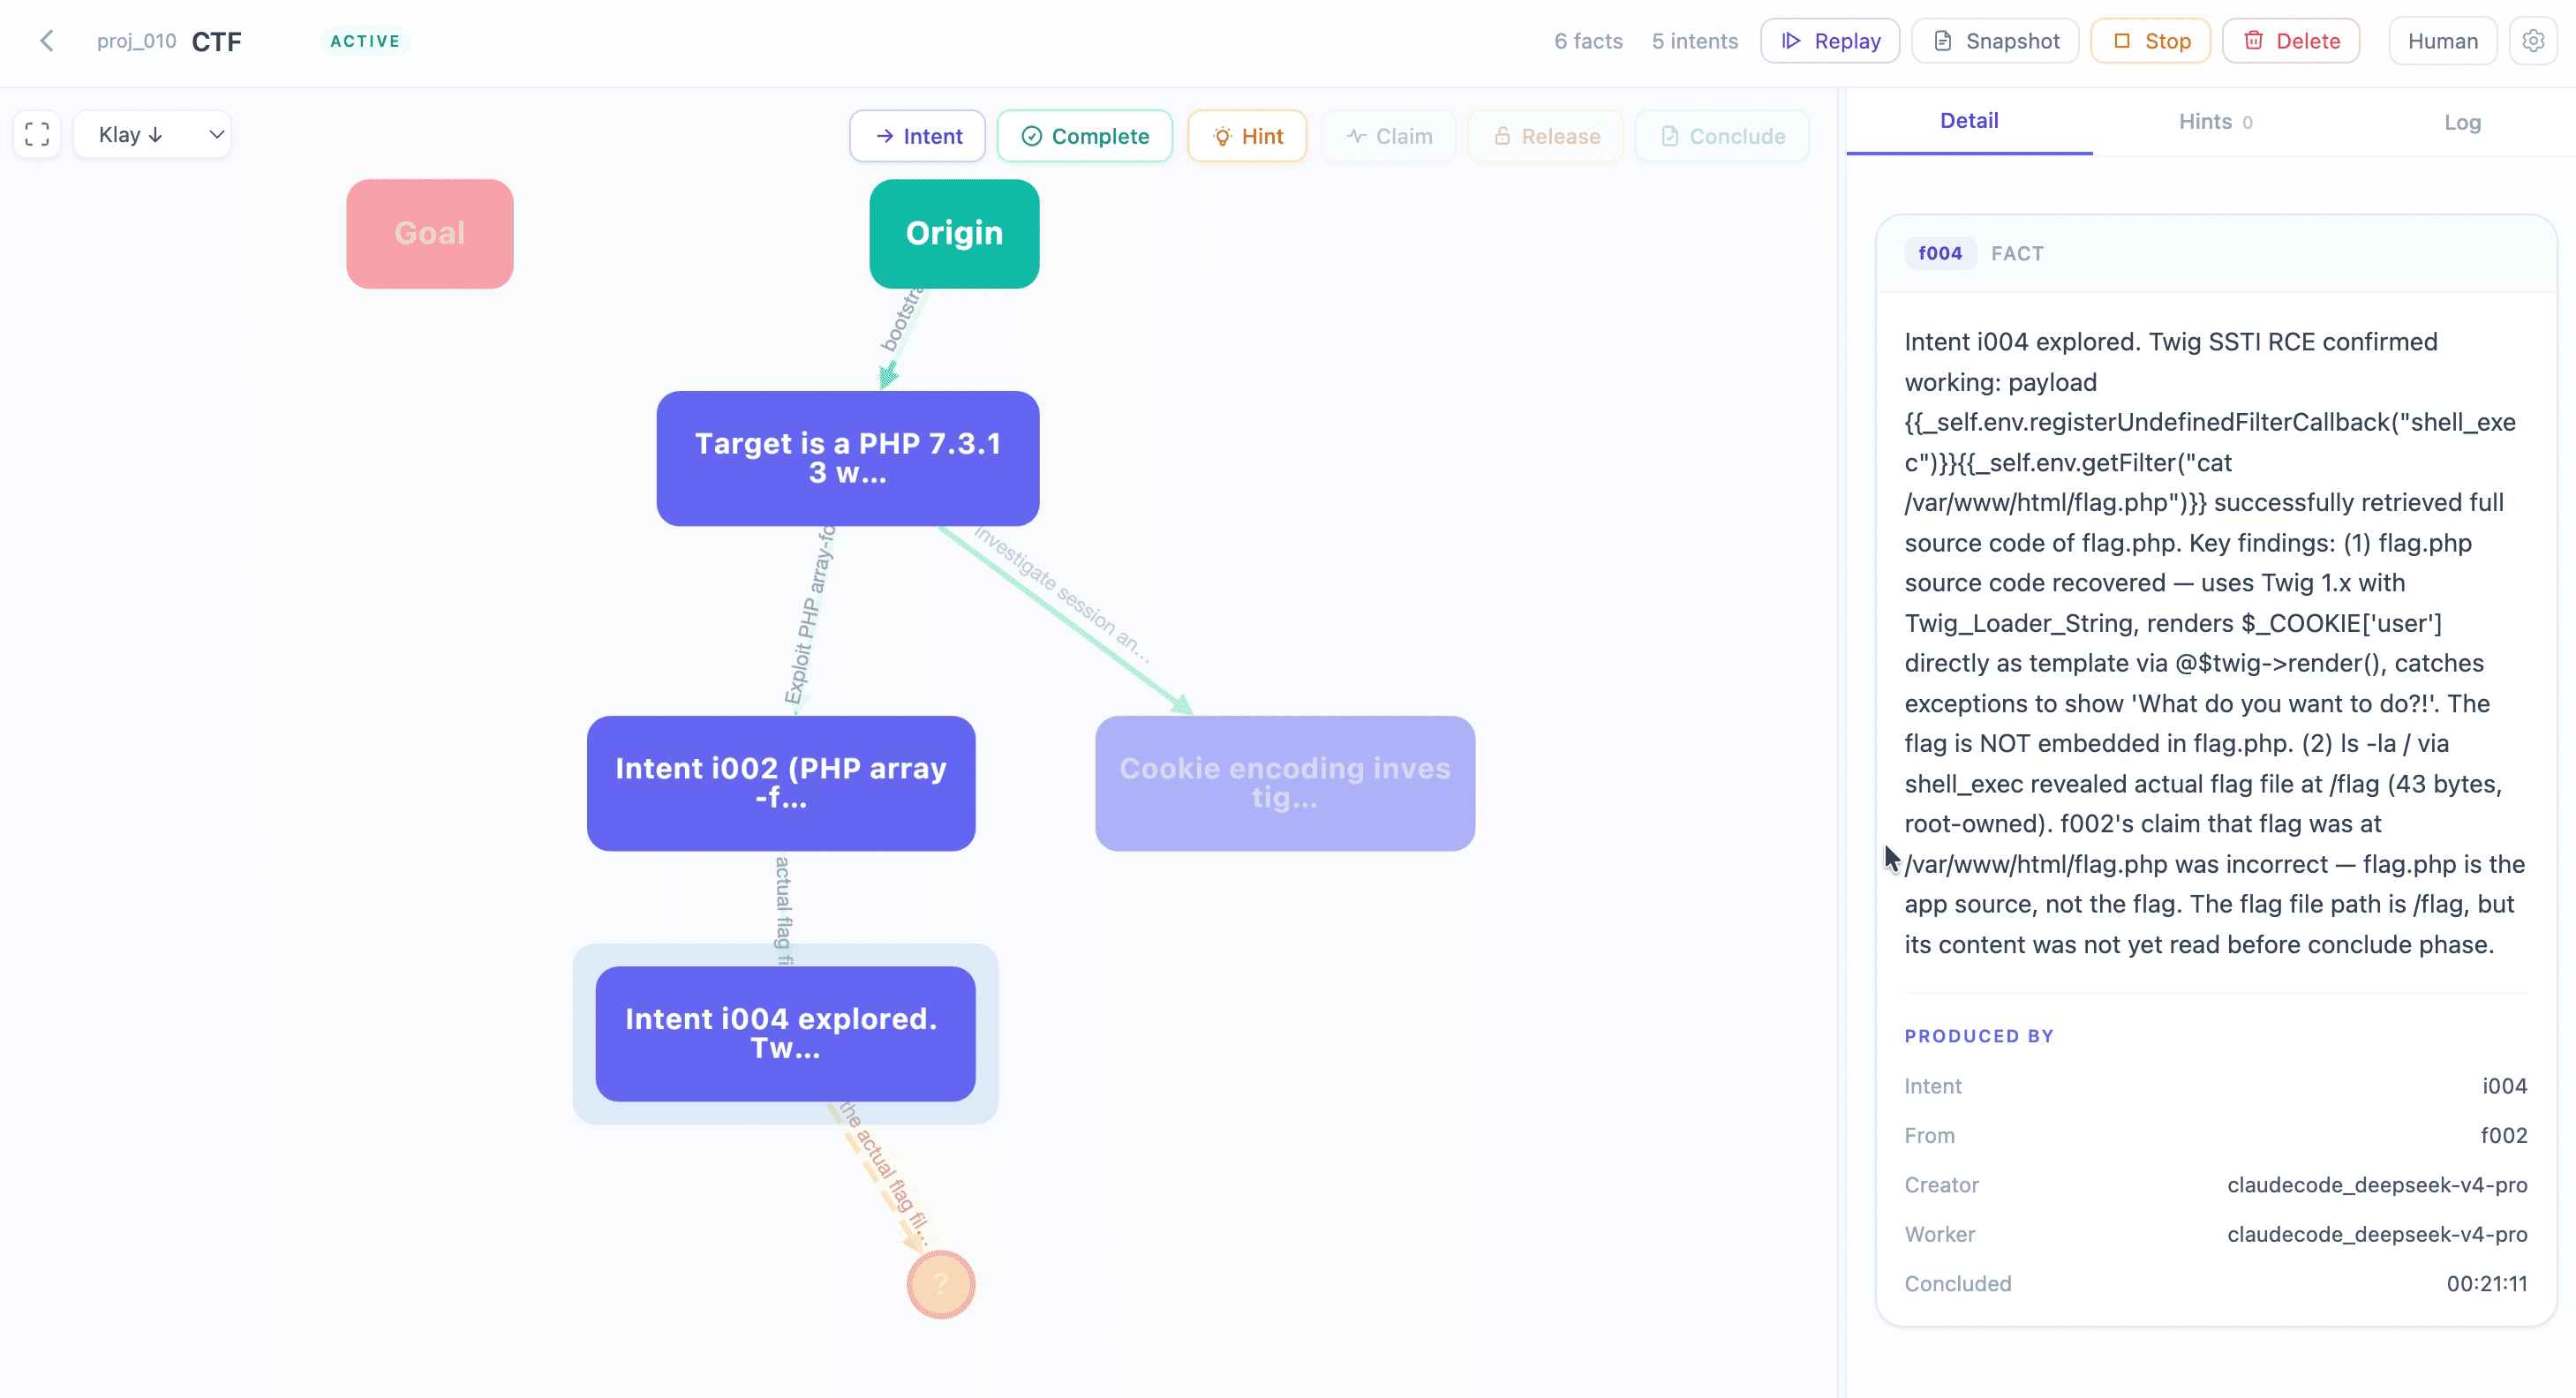 oritera/cairn
LLM-driven state-space search engine for autonomous penetration testing, CTF solving, and vulnerability research. Uses blackboard architecture with…
 hamed233/cybersecurity-mastery-roadmap
A comprehensive, step-by-step guide to mastering cybersecurity from beginner to expert level with curated resources, tools, and career guidance
 puppetm4ster/koyane-framework
Modular wordlist generation, editing, analysis, and discovery toolkit for password cracking, fuzzing, and ethical security testing. Supports…
 0xmrma/cve-2026-33146
A public share looked clean in the page tree, but the search endpoint told a different story. In Docmost, restricted child pages hidden from public…
 inertfluid/sk-cve-2026-26030-lab
Ethical, network-isolated Docker lab reproducing CVE-2026-26030 — Semantic Kernel in-memory vector store filter eval() RCE (patched in 1.39.4)
 masterking32/masterhttprelayvpn
Domain-fronted HTTP/SOCKS5 proxy tunneling traffic through Google Apps Script with MITM TLS interception, HTTP/1-2 multiplexing, and DPI evasion.
 ex-cal1bur/cve-2026-42568
An LDAP injection vulnerability exists in org.yamcs.security.LdapAuthModule. The username parameter is inserted directly into LDAP search filters…
 mrtdlgc/goodoldsearch-oss
Local static query builder for precise search across web engines, Shodan, crt.sh, and Wayback Machine. Supports Google dorks, filetype filters, date…
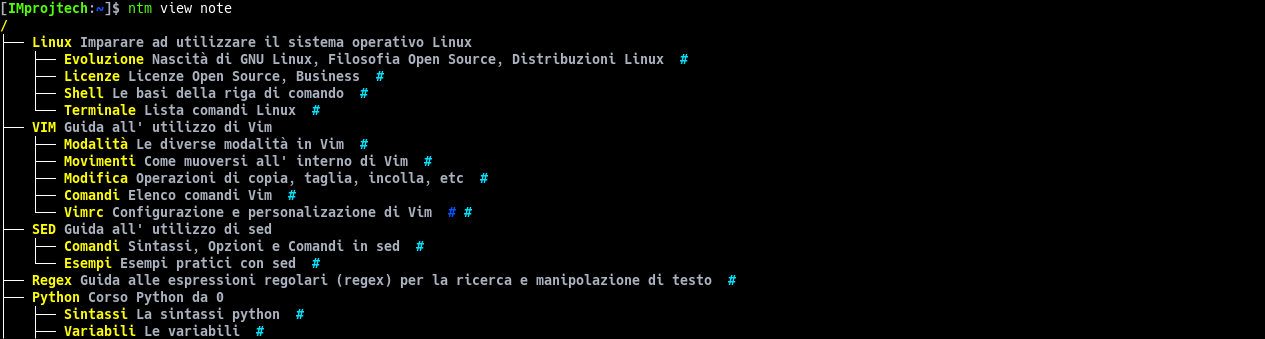 improjtech/notamy
Terminal-based note manager with hierarchical tagging and file linking
 mbanyamer/cve-2026-26988-librenms-sqli
Proof-of-concept exploit for unauthenticated SQL injection in LibreNMS ajax_table.php, demonstrating time-based and boolean-based blind injection…
 revshellxd/lfi-destruction
This program Prompts you for the Local File Inclusion information and will automatically search the /etc/passwd and using the users names found will…
 yup-ivan/cve-2024-9796
POC (SQLi) -> CVE-2024-9796