
CVE_2025_24257----NOT-MINE
 learningdisordercapital35/cve_2025_24257----not-mine
Demonstrate CVE-2025-24257 with a public PoC for IOGPUFamily kernel heap OOB read/write and panic analysis
binary-exploitationexploitationmemory-forensics+2
learningdisordercapital35/cve_2025_24257----not-mineDemonstrate CVE-2025-24257 with a public PoC for IOGPUFamily kernel heap OOB read/write and panic analysis
 k3ystr0k3r/cve-2026-29053
Python PoC and version scanner for CVE-2026-29053, an authenticated RCE in Ghost CMS below 6.19.1 via malicious Handlebars theme templates.
 cc1a2b/jshunter
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive…
 r3vpwnx/cve-2025-58434
Exploit chain for Flowise 3.0.5: unauthenticated account takeover via password-reset token disclosure (CVE-2025-58434) chained to CustomMCP…
 skraft9/cve-2025-29471
Stored XSS in Nagios Log Server 2024R1.3.1
 venablee/cve-2026-30251
Reflected XSS vulnerability disclosure for ZenShare Suite login_newpwd.php, allowing arbitrary JavaScript execution via crafted URL in codice_azienda…
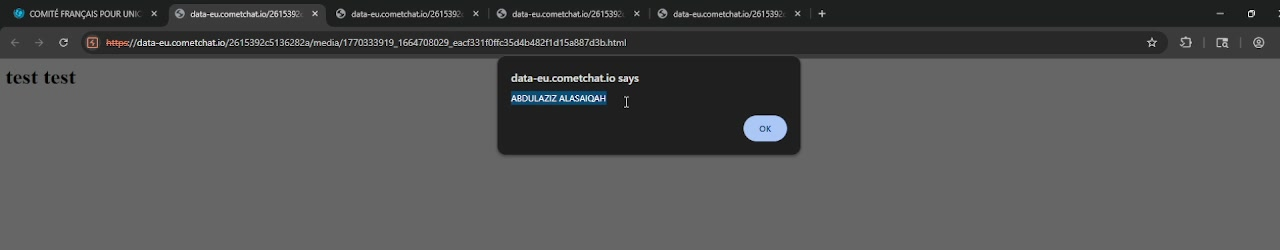 defineid/wildfire
CVE-2026-39154, Stored XSS in CometChat JS SDK
 alixploit22/cvex2shel
CVE-2026-64638 adalah kerentanan Pre-Auth Reflected Cross-Site Scripting (XSS) di WordPress yang ditemukan pada tahun 2026. Kerentanan ini…
 juice-shop/juice-shop
Intentionally vulnerable web application covering OWASP Top 10 vulnerabilities for security training, CTF competitions, and penetration testing…
 hakluke/hakrawler
Simple, fast web crawler designed for easy, quick discovery of endpoints and assets within a web application
 0xdak/cve-2026-67340_exploit
Post-auth RCE exploit for ArcadeDB via JavaScript trigger GraalVM sandbox escape, executing OS commands over HTTP API with reverse shell or blind…
 raphy76/wp2shell-poc-fulljs
full javascript reproduction of CVE-2026-63030 (author_exclude, author__not_in and misalignment between validations and matches)
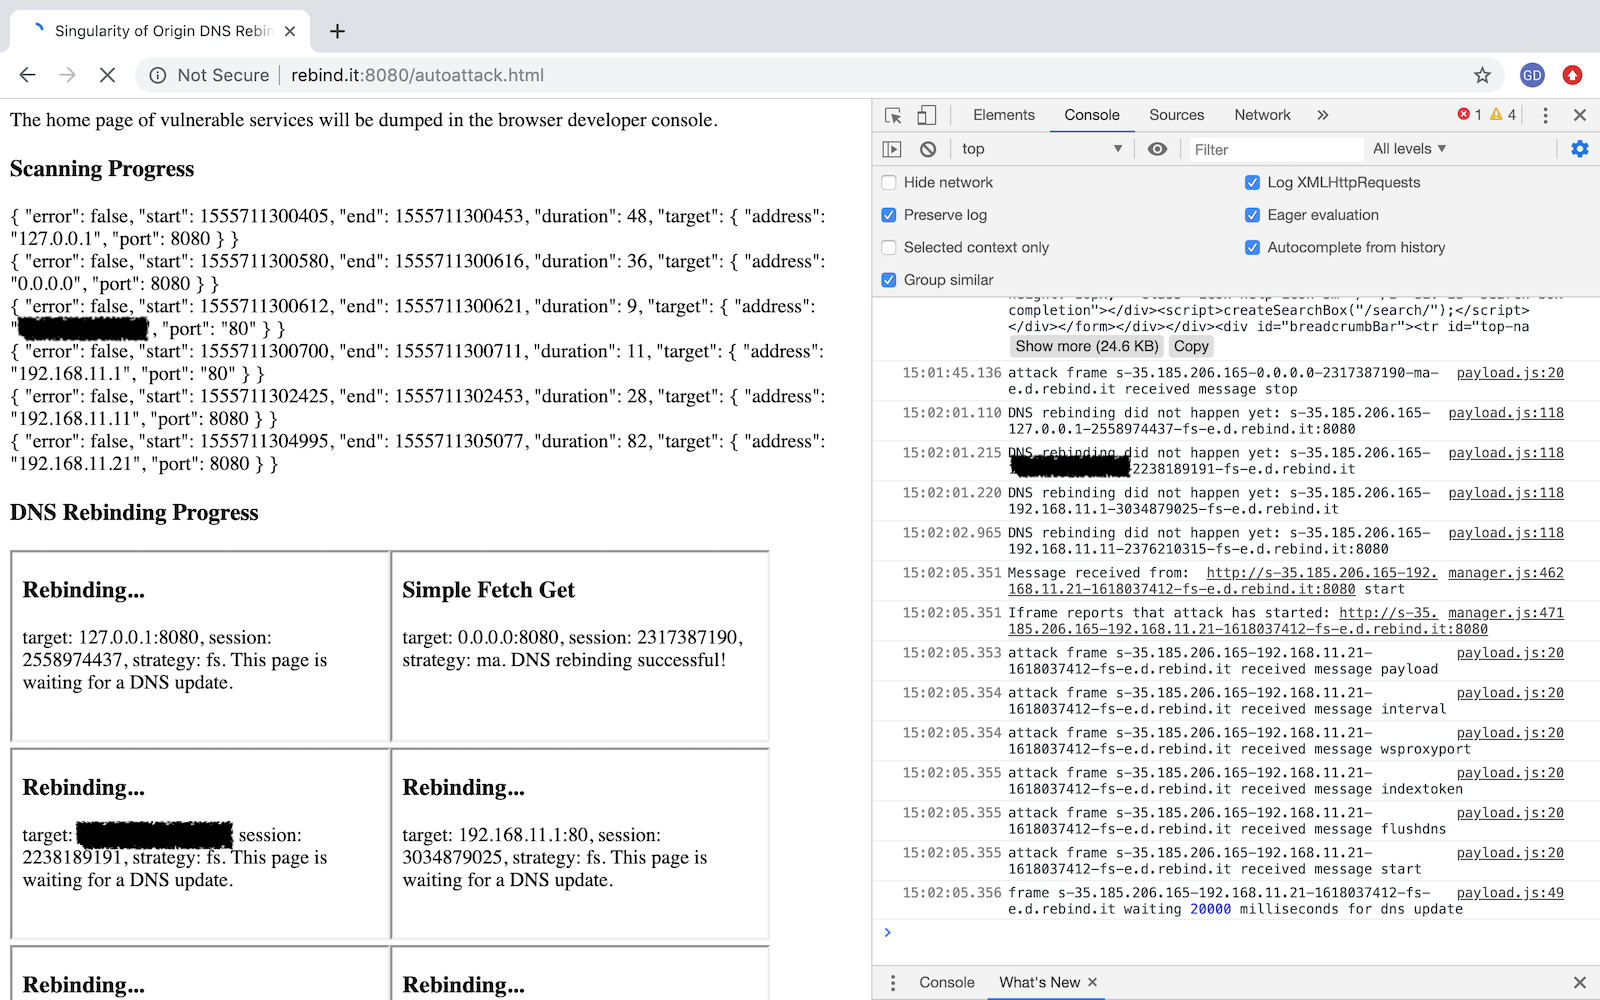 nccgroup/singularity
A DNS rebinding attack framework.
 se1zer/nextjs_exploit_tool
Next.js RSC RCE Exploit Tool (CVE-2025-55182)
 ibrahim-sartawi/cve-2026-26719
A stored Cross‑Site Scripting vulnerability exists in xxl-job-admin JobInfoController.java where the addressList parameter accepts unsanitized…
 nixon-h/cve-2025-68147-ospos-stored-xss
PoC repository for CVE-2025-68147: Stored Cross-Site Scripting (XSS) in OpenSourcePOS. Vulnerability allows privilege escalation via malicious…
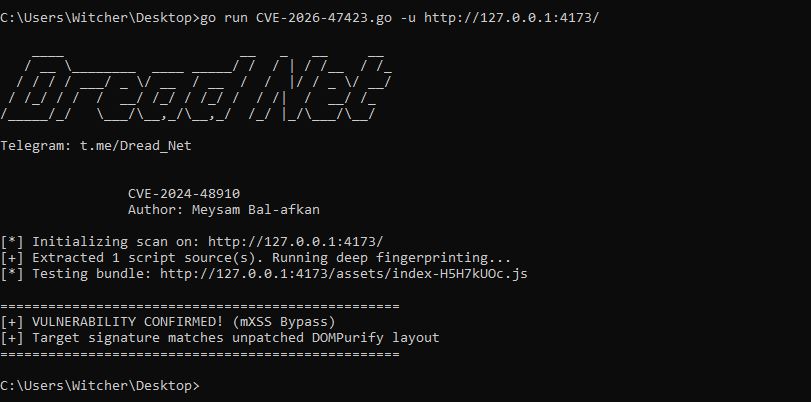 galaxy-sc/cve-2026-47423-dompurify-xss-detector
Go-based scanner that detects DOMPurify sanitizer bypass (CVE-2026-47423) via logic fingerprinting on minified production JavaScript bundles,…
 volkandindar/agartha
A Burp Suite extension for identifying injection flaws (LFI, RCE, SQLi), authentication/authorization issues, and HTTP 403 access violations. It…