
vphone-cli
 lakr233/vphone-cli
Boot and manage virtual iPhones on Apple Silicon with firmware patching, jailbreak variants, and security research features for iOS testing and…
exploitationfirmware-analysisios-security+3
16.2k
lakr233/vphone-cliBoot and manage virtual iPhones on Apple Silicon with firmware patching, jailbreak variants, and security research features for iOS testing and…
 cervantessec/cervantes
Open-source collaborative platform for pentesters and red teams to manage projects, clients, vulnerabilities, and generate OWASP-compliant reports…
 judgedbykira/cve-2026-20896-gitea-authentication-bypass
An explanation and PoC to exploit CVE-2026-20896 Authentication Bypass Vulnerability on Gitea. Being able to steal session tokens for valid users in…
 nccgroup/singularity
A DNS rebinding attack framework.
 sh4den/cve-2022-47966
The manage engine mass loader for CVE-2022-47966
 jf-gondim/mcp-pwn
PoC exploit for CVE-2026-23744 — unauthenticated RCE in MCPJam Inspector via unvalidated serverConfig command injection on /api/mcp/connect, enabling…
 nccgroup/http-mcp-bridge
HTTP proxy bridge for security testing of remote MCP servers, allowing standard HTTP tools to send JSON-RPC messages and manage sessions.
 synacktiv/mofos
Virtual machines manipulation framework
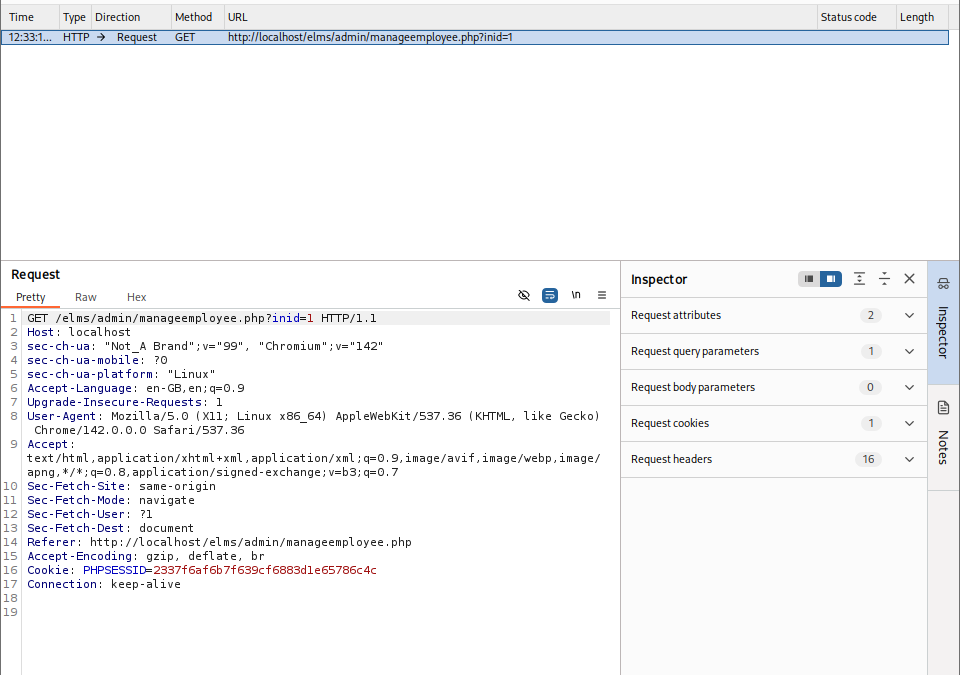 r-pradyun/cve-2025-67315
CSRF vulnerability PoC and remediation guide for employee deactivation in an admin panel. Includes CVSS scoring, attack reproduction steps, and…
 vighneshnair7/cve-2024-51031
Proof-of-concept for CVE-2024-51031: Stored Cross-Site Scripting (XSS) in Sourcecodester Cab Management System 1.0 via manage_account.php fields.…
 vighneshnair7/cve-2024-51030
Proof-of-concept exploit for SQL injection in Sourcecodester Cab Management System 1.0, demonstrating arbitrary SQL execution via the id parameter in…
 praison001/cve-2024-4879-servicenow
Exploit for CVE-2024-4879 affecting Vancouver, Washington DC Now and Utah Platform releases
 graysignal/cve-2024-4879-servicenow
Exploit for CVE-2024-4879 affecting Vancouver, Washington DC Now and Utah Platform releases
 epicosy/vul4j-23
Curated Java web framework vulnerability (CVE-2016-5394) for Apache Sling, designed for security testing, exploitation practice, and vulnerability…
 raikia/fiercephish
FiercePhish is a full-fledged phishing framework to manage all phishing engagements. It allows you to track separate phishing campaigns, schedule…
 pashayogi/cve-2023-2744
Mass CVE-2023-2744
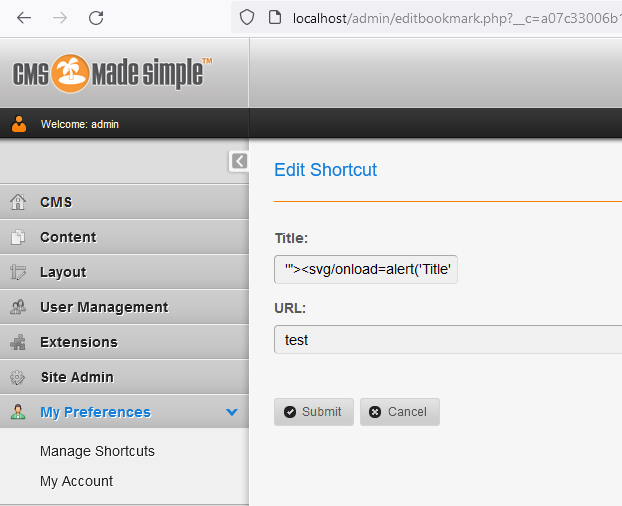 sromanhu/cve-2023-43357-cmsmadesimple-stored-xss---shortcut
Cross Site Scripting vulnerability in CMSmadesimple v.2.2.18 allows a local attacker to execute arbitrary code via a crafted script to the Title in…
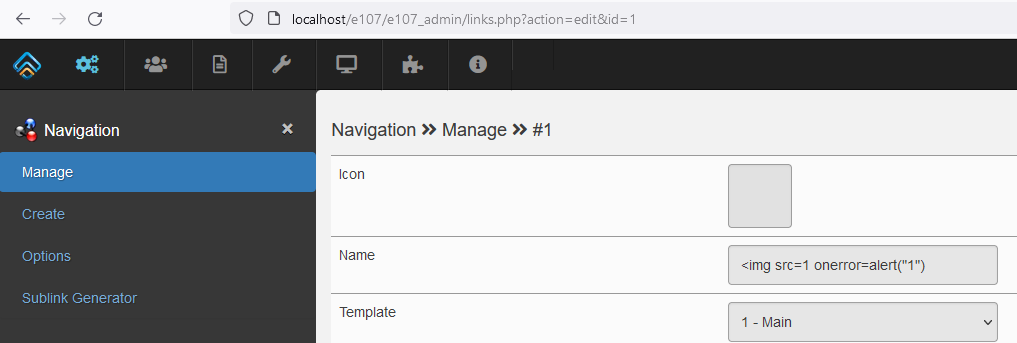 sromanhu/cve-2023-43873-e107-cms-stored-xss---manage
e107 2.3.2 is affected by a Cross-Site Scripting (XSS) vulnerability that allows attackers to execute arbitrary code via a crafted payload to the…