

Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
15 results
gori preview

gori

GitHubhahwul/gori

A fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.
api-security-testingfuzzinginformation-gathering+8
100
2 days ago
chisel preview

chisel

GitHubjpillora/chisel

Fast TCP/UDP tunnel over HTTP with SSH encryption, supporting reverse port forwarding, SOCKS5 proxy, and client authentication for secure network…
command-and-controldata-exfiltrationgeneral-purpose-utilities+8
16.6k19 days ago
slinger preview

slinger

GitHubemo-crab/slinger

An HTTP client specifically developed for security researchers
api-security-testingpenetration-testingvulnerability-analysis+2
2928 days ago
CVE-2026-66746-HTTP-Response-Splitting-via-Unvalidated-Response-Header-Values-rouille- preview

CVE-2026-66746-HTTP-Response-Splitting-via-Unvalidated-Response-Header-Values-rouille-

GitHubtheopaid/cve-2026-66746-http-response-splitting-via-unvalidated-response-header-values-rouille-

Security Advisory: HTTP Response Splitting via Unvalidated Response Header Values (rouille)
code-analysispenetration-testingvulnerability-analysis+2
1 month ago
CVE-2026-49365 preview

CVE-2026-49365

GitHuboscerd/cve-2026-49365

PoC reproducer for CVE-2026-49365 (Apache Camel camel-netty-http / camel-undertow): muteException defaults to false, so an uncaught exception's full…

educationexploitationinformation-gathering+3
1 month ago
Qlik-View-12.60-Including-SR-Stored-Cross-Site-Scripting-CVE-2022-42248 preview

Qlik-View-12.60-Including-SR-Stored-Cross-Site-Scripting-CVE-2022-42248

GitHubozozuz/qlik-view-12.60-including-sr-stored-cross-site-scripting-cve-2022-42248

Proof-of-concept exploit for CVE-2022-42248, a stored cross-site scripting vulnerability in QlikView Ajax Client allowing remote attackers to execute…
exploitationinformation-gatheringpenetration-testing+3
54 months ago
interactsh preview

interactsh

GitHubprojectdiscovery/interactsh

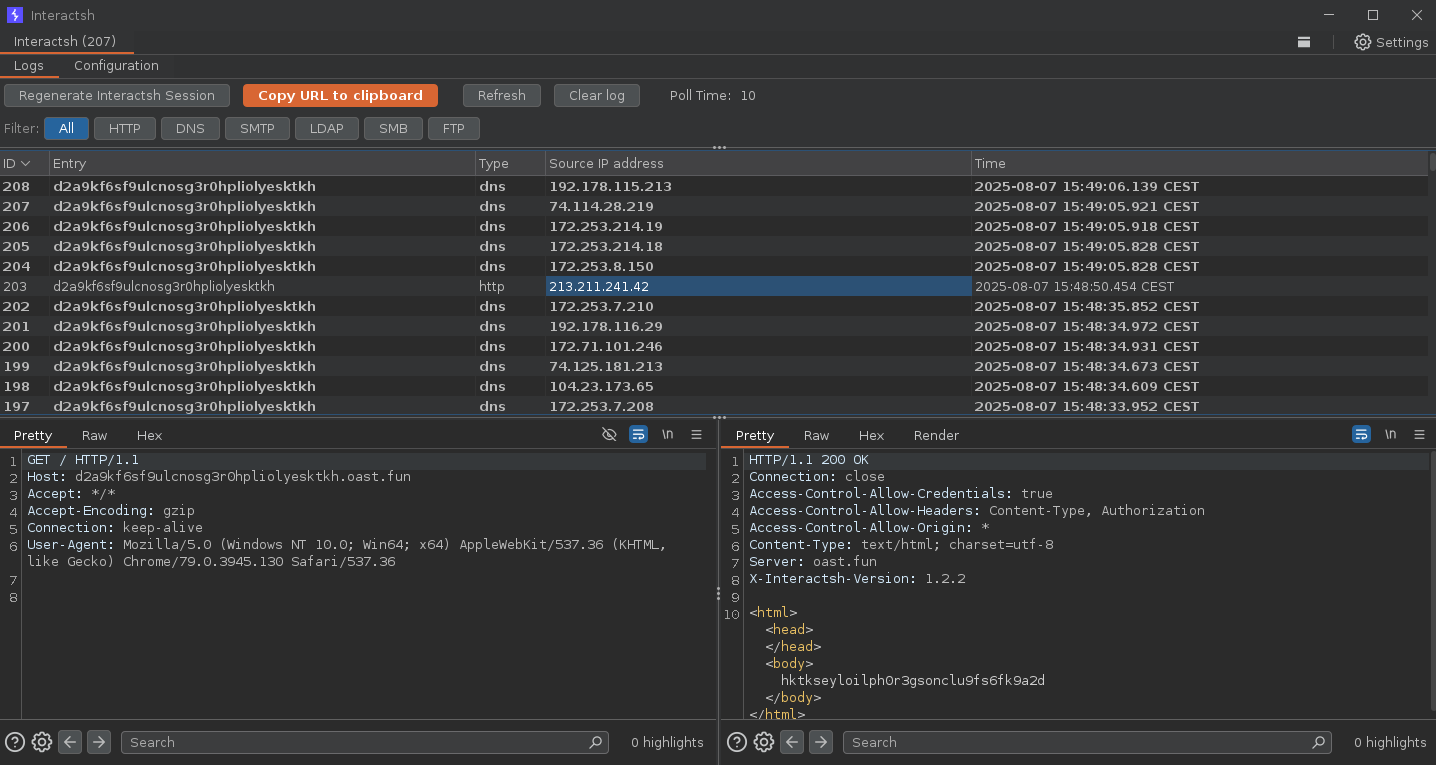
An OOB interaction gathering server and client library
dns-analysisinformation-gatheringpenetration-testing+2
4.5k6 months ago
RustTLSX preview

RustTLSX

GitHubd0rb/rusttlsx

🦀 Stealth HTTP client for Rust . mimics real browser TLS fingerprints for undetectable requests. Fast, type-safe, and built for precision networking.
anti-botcrawlerfingerprint-spoofing+5
10 months ago
CVE-2025-23048-POC preview

CVE-2025-23048-POC

GitHubabsholi7ly/cve-2025-23048-poc

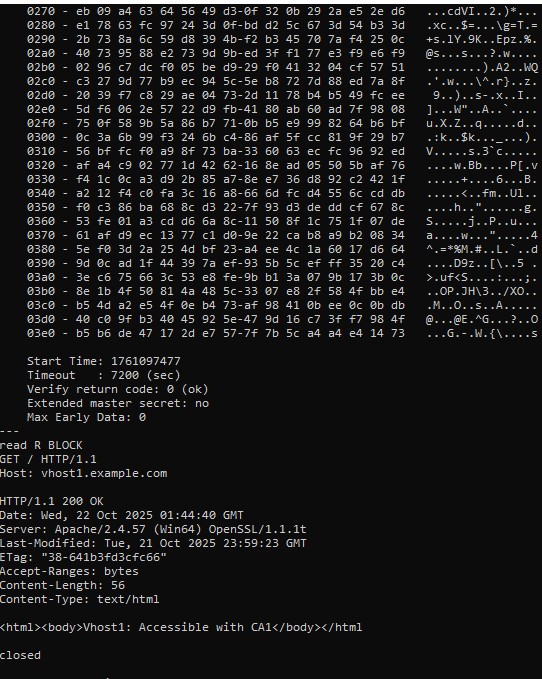
Apache HTTP Server versions 2.4.35 – 2.4.63 are vulnerable to a client certificate authentication bypass when TLS 1.3 session resumption is used…
authenticationexploitationpenetration-testing+3
411 months ago
forbidden preview

forbidden

GitHubivan-sincek/forbidden

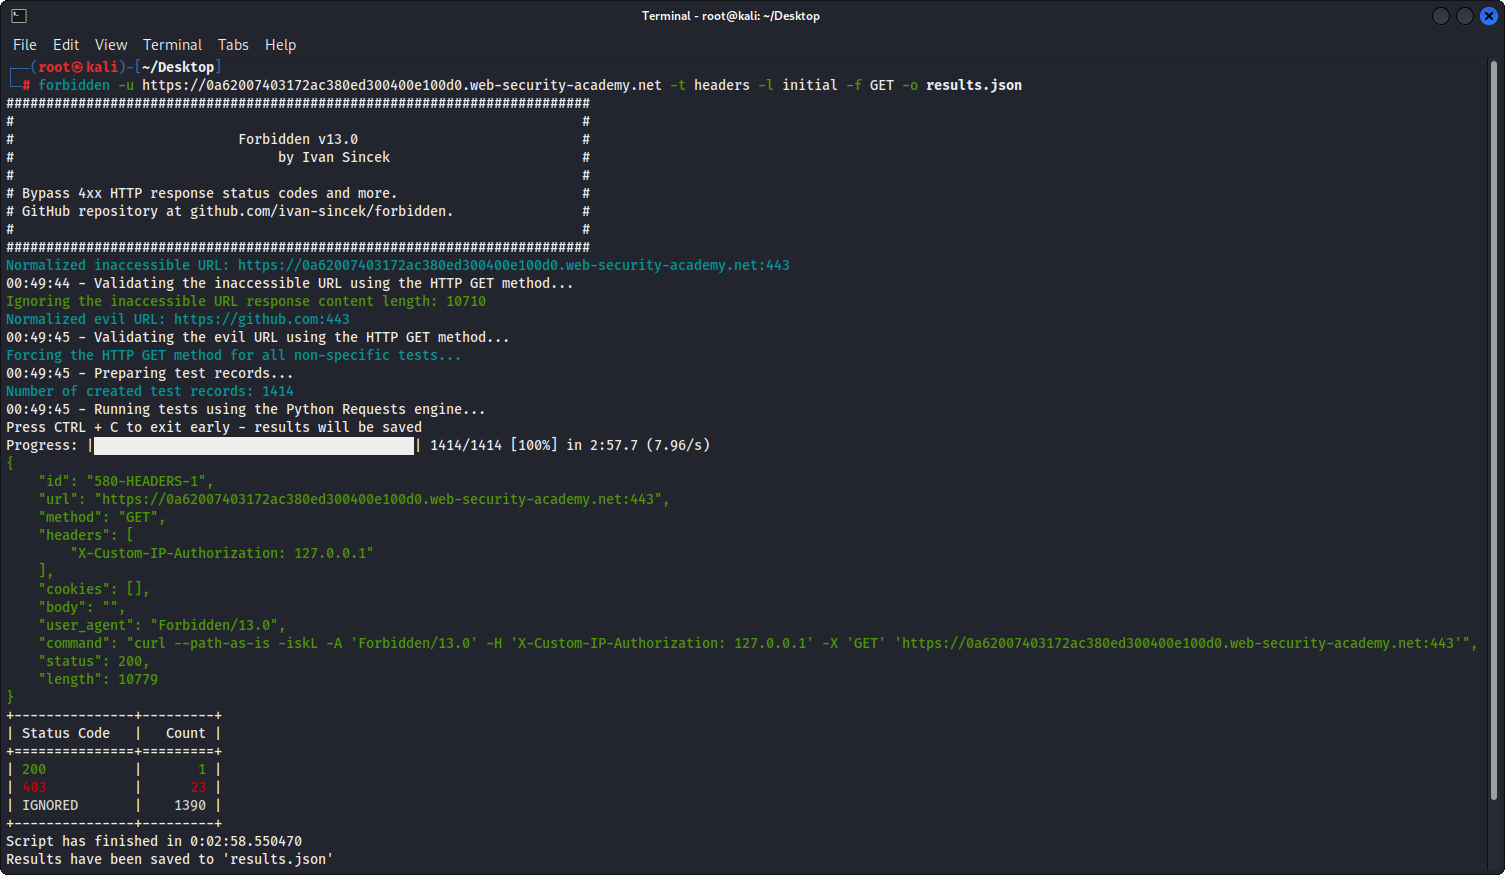
Bypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.

fuzzingids-ips-evasioninformation-gathering+5
2570 years ago
axios-CVE-2025-27152-PoC preview

axios-CVE-2025-27152-PoC

GitHubdavidblakecoe/axios-cve-2025-27152-poc

Proof-of-concept exploit for CVE-2025-27152 in Axios, demonstrating a server-side request forgery vulnerability in the popular HTTP client library.
exploitationpayload-developmentpenetration-testing+2
1 year ago
CVE-2022-0155-PoC preview

CVE-2022-0155-PoC

GitHubcoana-tech/cve-2022-0155-poc

Proof-of-concept demonstrating CVE-2022-0155 cookie theft via HTTP redirect in follow-redirects npm package, including Express server and client…
exploitationpayload-generationpenetration-testing+2
2 years ago
CVE-2019-17638-Jetty preview

CVE-2019-17638-Jetty

GitHubforse01/cve-2019-17638-jetty

Exploit for CVE-2019-17638 targeting Jetty Java HTTP server, enabling remote code execution via crafted HTTP requests for security testing and…
exploitationpenetration-testingvulnerability-analysis+2
15 years ago
wssip preview

wssip

GitHubnccgroup/wssip

Application for capturing, modifying and sending custom WebSocket data from client to server and vice versa.

fuzzingpenetration-testingweb-proxies-interception+1
4517 years ago
ABPTTS preview

ABPTTS

GitHubnccgroup/abptts

TCP tunneling over HTTP/HTTPS for web application servers

ids-ips-evasionpenetration-testingred-teaming+1
74410 years ago